Freedom251 › Network Traffic Analysis Software
nfdump
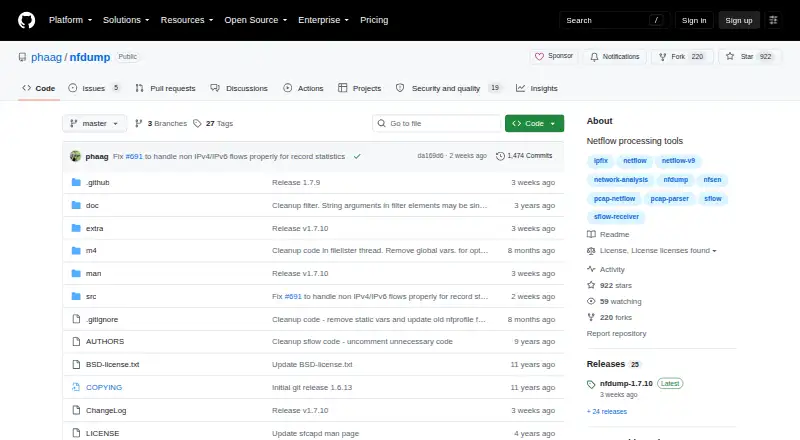
What nfdump is
nfdump is a free, BSD-licensed suite for collecting, processing, and analyzing network flow data. It works with NetFlow versions 1, 5, 7, and 9, IPFIX, and sFlow, and can also turn live or PCAP-file traffic into flow data. Its tools support tcpdump-like filtering, user-defined aggregation, flow statistics, conversation analysis, and bandwidth monitoring. Flow records can be enriched with geolocation, autonomous-system, and Tor exit-node information when optional databases are used. Results can be written as text, CSV, JSON, or user-defined formats. The suite includes collector and processing tools such as nfcapd, sfcapd, nfdump, nfanon, nfexpire, and nfreplay. Collected files can be compressed with LZO, LZ4, ZSTD, or bzip2; ZSTD and bzip2 need system libraries. For metrics, the project documents export through nfinflux for InfluxDB and nfexporter for Prometheus-compatible tools, and it is compatible with NfSen. nfdump runs on Linux in a self-hosted deployment. Root privileges are unnecessary unless binding to ports below 1024. The documentation notes that nfcapd has no built-in access control, so host-level security should filter source IP addresses. Version 1.7.x reads files created by 1.6.18 or newer; older 1.6.x files may need conversion.
Who it suits
nfdump suits network administrators who collect flow data from devices and want tools for filtering, aggregation, statistics, and export. It is a fit for Linux users who can operate a self-hosted suite and manage host-level access controls.
What it does well
- Collects NetFlow, IPFIX, and sFlow data.
- Converts live or PCAP traffic into flow data.
- Supports filtering, custom aggregation, and flow statistics.
- Exports text, CSV, JSON, and user-defined formats.
- BSD-licensed and free to use.
What to know first
- Linux and self-hosted deployment are the listed platform options.
- nfcapd has no built-in access control.
- Legacy nfdump 1.6.x files may need conversion for 1.7.x.
Limits
The project states no paid plans or usage limits. nfdump 1.7.x reads files created by 1.6.18 or newer; legacy 1.6.x files may need conversion.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free / BSD-licensed software | No paid plans or usage limits stated | Free |
As github.com lists them, read 8 Oct 2026. The maker's own page has the final word.
Getting started
- Open the project at https://github.com/phaag/nfdump.
- Install and run the suite on Linux in a self-hosted deployment.
- Use nfcapd or sfcapd to collect flow data.
- Use nfdump and the included processing tools to filter, analyze, or export data.
- Filter source IP addresses with host-level security when using nfcapd.
nfdump is a free, open-source Linux suite for teams that need direct control over network-flow collection and analysis. It fits administrators comfortable running self-hosted tooling and assembling their own operational workflow. Its broad protocol support and flexible exports are the main reasons to choose it, while the command-line, host-managed approach will not suit teams seeking a turnkey service.
Overview
nfdump combines collectors, processors, and utilities instead of presenting a single hosted dashboard. Components such as nfcapd, sfcapd, nfdump, nfanon, nfexpire, and nfreplay cover ingestion, processing, retention, anonymization, and replay. It accepts NetFlow versions 1, 5, 7, and 9, IPFIX, and sFlow v4 and v6, making it a practical fit for networks with mixed device generations.
The BSD license and zero purchase price remove licensing barriers for labs, small operations, and organizations that require on-premises deployment. You remain responsible for the Linux host, storage, upgrades, analyst access, and any dashboard or workflow built around the utilities. Root access is unnecessary unless a collector must bind to a port below 1024, which simplifies ordinary deployments.
Key features
Collection and conversion
Collectors receive flow records from supported network devices, while conversion can turn live traffic or PCAP files into flow data. That combination supports continuous telemetry and retrospective capture analysis in one toolchain. It is particularly useful when investigations need to compare routine flow records with packet-capture material.
Filtering, aggregation, and conversations
Tcpdump-like flow filters provide granular ways to isolate protocols, hosts, or conversations. User-defined aggregation and flow statistics turn large record sets into summaries suitable for bandwidth monitoring and conversation analysis. The approach rewards operators who are comfortable constructing precise queries; it is less approachable than a visual, guided investigation interface.
Enrichment and output
Optional databases can add geolocation, autonomous-system, and Tor exit-node context to records. Text, CSV, JSON, and user-defined output formats make the results usable in scripts, reports, and downstream systems. Enrichment depends on maintaining the relevant databases, so it adds operational value but also another maintenance task.
Compression and integrations
Collected files support LZO, LZ4, ZSTD, and bzip2 compression. ZSTD and bzip2 require system libraries, an important packaging consideration when standardizing hosts. Documented tools nfinflux and nfexporter export metrics to InfluxDB and Prometheus-compatible tooling, and compatibility with NfSen extends its usefulness in monitoring environments that already use that ecosystem.
Security and compatibility
nfcapd has no built-in access control, so host-level controls must restrict source IP addresses. That is a meaningful concern for deployments exposed beyond a tightly controlled network. nfdump 1.7.x reads files created by nfdump 1.6.18 or newer; legacy 1.6.x files may require conversion and can only be read directly by nfdump, which complicates migrations from older archives.
Pricing
| Plan | Price | Best for |
|---|---|---|
| Free / BSD-licensed software | free | Anyone needing the complete open-source suite without paid plans or stated usage limits |
There are no paid tiers or published quotas. The economic trade-off is infrastructure and administration: you supply the Linux deployment, storage, security controls, and any visualization or support process. Project support points to man pages, GitHub issues and pull requests, and the email address in AUTHORS rather than a commercial service-level package.
Platforms
nfdump runs on Linux and is designed for self-hosted, on-premises deployment. It is therefore a strong match for organizations that can operate Linux servers and a poor fit for readers seeking a browser-first hosted service or native desktop and mobile clients.
Who it's for
Choose nfdump for network administrators, security teams, home labs, and service providers that need protocol breadth, scriptable processing, and control over where flow data is stored. It is also a sensible foundation for teams already using InfluxDB, Prometheus-compatible tools, or NfSen. Look elsewhere if nontechnical users need guided dashboards, if multiple user roles require application-level access control, or if maintaining collectors and retention is outside your operating model.
Pros and cons
- Pros: Broad NetFlow, IPFIX, and sFlow coverage supports heterogeneous networks.
- Pros: PCAP and live-traffic conversion enables both ongoing monitoring and forensic workflows.
- Pros: Filters, aggregation, enrichment, and text/CSV/JSON/custom output suit automation and detailed investigations.
- Pros: BSD licensing provides a complete free suite with no stated usage caps.
- Cons: Linux self-hosting leaves infrastructure, storage, upgrades, and presentation to your team.
- Cons: nfcapd lacks built-in access control, requiring host-level source-IP filtering.
- Cons: Older 1.6.x archives may need conversion before a 1.7.x migration.
Alternatives
ManageEngine NetFlow Analyzer is the better choice when you want a freemium product with Android, iOS, Linux, web, and Windows access; its free edition covers two interfaces, while paid Standard and Professional editions are priced per month for 10 interfaces.
ntopng suits readers wanting a web-oriented, cross-platform option with an open-source community edition aimed at small networks and a suggested maximum of 256 live local hosts.
Caligare Flow Inspector is worth considering for a web-based Linux deployment with a free non-commercial edition limited to two devices, 24-hour history, and 250 flows per second, plus a trial.
FlowViewer is another free Linux/web option that requires a Unix server, with paid hourly custom support and router-configuration services.
Nagios XI fits teams seeking a broader self-hosted monitoring platform, with a free tier capped at seven nodes or 100 services and paid Standard licensing.
ElastiFlow is preferable when packaged dashboards and detections matter; its free Basic plan supports up to 4,000 records per second and 25 SNMP devices.
Riverbed Aternity is an enterprise digital-experience offering with custom pricing.
Akvorado is a free, self-hosted alternative developed by Free, described as a French ISP.
For more products in this category, see Network Traffic Analysis Software.
Verdict
Pick nfdump when you need a capable, no-cost Linux toolkit for collecting and investigating diverse flow protocols, with scriptable filtering, enrichment, compression, and metric exports. Its strongest advantage is control without license fees; its main drawback is that you must design and secure the surrounding self-hosted operation, including access control for nfcapd.
Verdict
Pick nfdump if you need a free Linux suite for collecting and analyzing network flow data, with several protocols and output formats. It also supports enrichment and metric export through documented tools. Look elsewhere if you need built-in access control for nfcapd or do not want to manage a self-hosted deployment.
Questions
How much does nfdump cost?
nfdump is free and distributed under a BSD license.
Which flow protocols does it support?
It collects NetFlow versions 1, 5, 7, and 9, IPFIX, and sFlow versions 4 and 6.
Which operating system and deployment does it use?
Linux is the listed platform, and deployment is self-hosted.
Can nfdump export metrics to other tools?
The project documents metric export through nfinflux for InfluxDB and nfexporter for Prometheus-compatible tools. It is also compatible with NfSen.
Does nfcapd include access control?
No. The documentation says nfcapd has no built-in access control and recommends filtering source IP addresses with host-level security.
How are older flow files handled?
nfdump 1.7.x reads files created by nfdump 1.6.18 or newer. Legacy 1.6.x files may need conversion and can only be read directly by nfdump.
Facts from nfdump's own pages
- Compatibility limit
- nfdump 1.7.x reads files created by nfdump 1.6.18 or newer, while legacy 1.6.x files may need conversion and only nfdump can read them directly. · github.com, 8 Oct 2026
- Compression
- Collected files can use LZO, LZ4, ZSTD, or bzip2 compression; ZSTD and bzip2 require system libraries. · github.com, 8 Oct 2026
- Enrichment
- Flow records can be enriched with geolocation, autonomous-system, and Tor exit-node information using optional databases. · github.com, 8 Oct 2026
- Filtering and aggregation
- It supports tcpdump-like flow filtering, user-defined aggregation, and flow statistics. · github.com, 8 Oct 2026
- Included tools
- The suite includes collector and processing tools such as nfcapd, sfcapd, nfdump, nfanon, nfexpire, and nfreplay. · github.com, 8 Oct 2026
- Integrations
- The project documents metric export through nfinflux for InfluxDB and nfexporter for Prometheus-compatible tools, and says it is compatible with NfSen. · github.com, 8 Oct 2026
- License
- The project is distributed under a BSD license. · github.com, 8 Oct 2026
- Output
- Supported output formats include text, CSV, JSON, and user-defined formats. · github.com, 8 Oct 2026
- Privileges
- Root privileges are not required unless binding to ports below 1024. · github.com, 8 Oct 2026
- Protocol support
- It collects NetFlow versions 1, 5, 7, 9, IPFIX, and sFlow data. · github.com, 8 Oct 2026
- Purpose
- nfdump is a suite of tools for collecting, processing, and analyzing NetFlow, IPFIX, and sFlow data from network devices. · github.com, 8 Oct 2026
- Security
- The documentation says nfcapd has no built-in access control, so host-level security should filter source IP addresses. · github.com, 8 Oct 2026
- Support
- The project points users to its man pages, GitHub issues and pull requests, and the email address in AUTHORS for questions. · github.com, 8 Oct 2026
- Traffic conversion
- It can convert live or PCAP-file traffic into flow data. · github.com, 8 Oct 2026