Freedom251 › Software Composition Analysis Software
Nancy
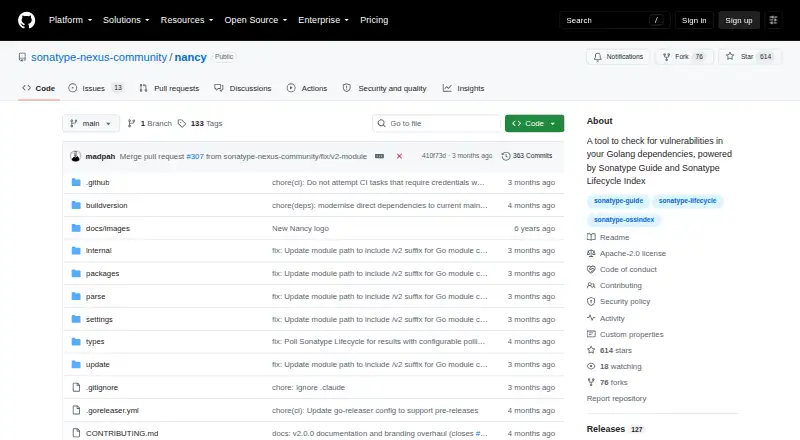
What Nancy is
Nancy is a free, open-source command-line tool for checking Go module dependencies for vulnerabilities. It uses Sonatype's vulnerability database and can also scan with Sonatype Lifecycle. Nancy can gather dependency data by running `go list -json -deps ./...` or read that output through a pipe. Using `go list -json -m all` can include dependencies that do not appear in the final binary. Results can be printed as text, JSON, pretty JSON, or CSV. Users can suppress findings by CVE or Sonatype vulnerability ID through flags or ignore files, with optional expiration dates for those exclusions. The tool supports Linux, macOS, and Windows, and can run as a Docker image or in a self-hosted setup. Installation options include building from source, downloading GitHub release binaries, and using Homebrew on macOS. The project documents GitHub Actions and CircleCI integrations. Nancy's repository lists the Apache-2.0 license. Its maintainers describe the project as community-maintained, not officially supported by Sonatype, and direct support questions to GitHub Issues.
Who it suits
Nancy suits developers and teams working with Go modules who want to inspect dependency vulnerability data from the command line or in CI workflows. It also fits users who prefer self-hosted tools and want control over output formats and vulnerability exclusions.
What it does well
- Free and licensed under Apache-2.0.
- Accepts Go dependency data directly or through a pipe.
- Offers text, JSON, pretty JSON, and CSV output.
- Exclusions can target CVEs or Sonatype vulnerability IDs.
- Documents GitHub Actions and CircleCI integrations.
What to know first
- Only Go module dependencies are supported.
- Dependencies resolved by commit hash rather than proper versions are unsupported.
- The default stdin input limit is 100 MB.
- Maintainers direct users to GitHub Issues rather than Sonatype support tickets.
Limits
Nancy supports Go modules, and dependencies resolved by commit hash rather than proper versions are not supported by its vulnerability lookup. By default, it accepts up to 100 MB of `go list` output from stdin; that limit can be adjusted.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Nancy | Open-source command-line tool; no Nancy price stated | Free |
As github.com lists them, read 11 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the Nancy GitHub repository.
- Install with a source build, a GitHub release binary, or Homebrew on macOS.
- Run `go list -json -deps ./...` through Nancy, or pipe its output into Nancy.
- Optionally use `go list -json -m all` to include dependencies outside the final binary.
- Use a free Sonatype Guide bearer token, as Nancy recommends.
- Connect Nancy to GitHub Actions or CircleCI if using those documented integrations.
Verdict
Choose Nancy if you need a free command-line vulnerability scan for Go module dependencies and want to use it in documented CI workflows. Look elsewhere if your dependency set relies on commit-hash-only resolutions or you require official Sonatype product support.
Questions
Does Nancy cost anything?
Nancy is free, and its plan is listed as free.
What operating systems does Nancy support?
The listed platforms are Linux, macOS, Windows, and self-hosted deployment.
Is Nancy open source?
Yes. Its repository lists the Apache-2.0 license.
What dependency ecosystem does Nancy scan?
Nancy works with Go modules (`go.mod`). Dependencies resolved by commit hash rather than proper versions are unsupported.
How can I install Nancy?
The project offers source builds, downloadable GitHub release binaries, and Homebrew on macOS. It can also run as a Docker image.
Who provides support for Nancy?
The maintainers describe Nancy as a community project, not officially supported by Sonatype, and direct users to GitHub Issues.
Facts from Nancy's own pages
- Authentication
- Nancy recommends a free Sonatype Guide bearer token; OSS Index username and token credentials remain supported but are deprecated for removal in v3.x.y. · github.com, 11 Oct 2026
- CI integrations
- The README links a Nancy GitHub Action and CircleCI Orb and includes a GitHub Actions scanning example. · github.com, 11 Oct 2026
- Compatibility limit
- Dependencies resolved by commit hash instead of proper versions are not supported by Nancy's vulnerability lookup. · github.com, 11 Oct 2026
- Container use
- Nancy can run as a Docker image, and the README describes latest, full-version, major-version, and major/minor tags. · github.com, 11 Oct 2026
- Dependency input
- Nancy works with projects using Go modules and can run `go list -json -deps ./...` itself or accept that output through a pipe. · github.com, 11 Oct 2026
- Dependency limitation
- The README says dependencies resolved by commit hash rather than proper versions are not supported by Nancy. · github.com, 11 Oct 2026
- Ignore rules
- Users can exclude vulnerabilities by CVE or Sonatype vulnerability ID using flags or files, including ignores with expiration dates. · github.com, 11 Oct 2026
- Input
- Nancy works with projects using Go modules and can run `go list -json -deps ./...` itself or read piped `go list` output. · github.com, 11 Oct 2026
- Input limit
- Nancy accepts up to 100 MB of `go list` output from stdin by default, and the limit can be adjusted. · github.com, 11 Oct 2026
- Installation
- The project offers source builds, downloadable GitHub release binaries, and Homebrew installation on macOS. · github.com, 11 Oct 2026
- Integrations
- The project documents GitHub Actions, CircleCI, Docker, and Sonatype Lifecycle integrations. · github.com, 11 Oct 2026
- License
- The Nancy repository lists the Apache-2.0 license. · github.com, 11 Oct 2026
- Output formats
- Nancy supports text, JSON, pretty JSON, and CSV output. · github.com, 11 Oct 2026
- Purpose
- Nancy checks Go dependencies for vulnerabilities using Sonatype Guide and can also scan with Sonatype Lifecycle. · github.com, 11 Oct 2026
- Scan scope
- The README says `go list -json -m all` can be used to scan all dependencies, including dependencies that do not end up in the final binary. · github.com, 11 Oct 2026
- Security and license
- The GitHub repository identifies the project as Apache-2.0 licensed and links a security policy. · github.com, 11 Oct 2026
- Support
- The maintainers say Nancy is a community project not officially supported by Sonatype, and direct users to GitHub Issues rather than Sonatype support tickets. · github.com, 11 Oct 2026
- Vulnerability database
- Nancy uses Sonatype's vulnerability database to inspect dependency files for potentially vulnerable library usage. · github.com, 11 Oct 2026
- Vulnerability exclusions
- Users can exclude vulnerabilities by CVE or Sonatype vulnerability ID, including with dated expiring ignores. · github.com, 11 Oct 2026