Freedom251 › Ruby Static Analysis Tools
bundler-audit
What bundler-audit is
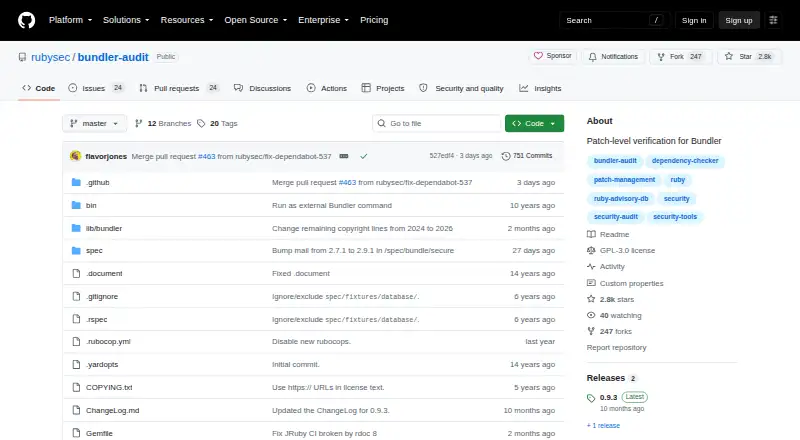
bundler-audit is a free, open-source tool for checking Ruby gems and Bundler projects. It scans Gemfile.lock for vulnerable gem versions and flags gem sources that use http:// or git://. The tool prints advisory details and allows users to ignore advisories they have manually worked around.
It can run without a network connection. Users can update the ruby-advisory-db database separately, or check a lockfile with or without an update. Rake tasks are available for auditing a bundle and updating the database; output can be JSON, and a per-project configuration file can store advisory IDs to ignore. Installation is documented with `gem install bundler-audit`. Listed requirements include Git, Ruby 2.0.0 or newer, RubyGems 1.8 or newer, Thor ~> 1.0 and Bundler 1.2.0 or newer. It is distributed as a Ruby gem under GPL version 3 or later, supports Linux and macOS, and directs users to GitHub Issues for support.
Who it suits
bundler-audit may suit Ruby and Bundler project maintainers who want to check lockfiles for vulnerable gems and insecure sources. It is also relevant to users who need offline checks or JSON output.
What it does well
- Checks Gemfile.lock for vulnerable gem versions.
- Flags http:// and git:// gem sources.
- Can run without a network connection.
- Supports JSON output and per-project ignored-advisory settings.
- Free software under GPL version 3 or later.
What to know first
- Requires Ruby 2.0.0 or newer and listed dependencies.
- Listed platforms are Linux and macOS.
- The project does not state a support service.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| bundler-audit | GPL-3.0-or-later · Ruby gem | Free |
As github.com lists them, read 5 Oct 2026. The maker's own page has the final word.
Verdict
bundler-audit focuses on lockfile checks for Ruby and Bundler projects, with offline use, advisory controls and Rake tasks. Users should check the listed runtime requirements and platform coverage before adopting it.
Facts from bundler-audit's own pages
- Advisory database
- The tool can update the ruby-advisory-db database and check a lockfile with or without updating it. · github.com, 5 Oct 2026
- Advisory handling
- It prints advisory information and allows users to ignore advisories that have been manually worked around. · github.com, 5 Oct 2026
- Founded
- 2013 · github.com, 28 Sept 2026
- Insecure sources
- It checks for insecure gem sources using http:// and git://. · github.com, 5 Oct 2026
- Installation and requirements
- The project documents installation with gem install bundler-audit and lists Git, Ruby 2.0.0 or newer, RubyGems 1.8 or newer, Thor ~> 1.0, and Bundler 1.2.0 or newer as requirements. · github.com, 5 Oct 2026
- Integration
- Rake tasks are available for auditing a bundle and updating the vulnerability database. · github.com, 5 Oct 2026
- License
- The project is free software under GPL version 3 or later. · github.com, 5 Oct 2026
- Maintainer and support
- The README identifies Hal Brodigan in its copyright notice and directs users to GitHub Issues; it does not state a support service. · github.com, 5 Oct 2026
- Offline use
- The project says it does not require a network connection to run. · github.com, 5 Oct 2026
- Output and configuration
- It supports JSON output and a per-project configuration file for ignored advisory IDs. · github.com, 5 Oct 2026
- Purpose
- bundler-audit provides patch-level verification for Bundler projects. · github.com, 5 Oct 2026
- Release details
- RubyGems lists version 0.9.3, published November 28, 2025, with MFA used for publishing. · rubygems.org, 5 Oct 2026
- Vulnerable gems
- It checks Gemfile.lock for vulnerable gem versions. · github.com, 5 Oct 2026
Where bundler-audit stands on Freedom251
- Ruby Static Analysis Tools#3 of 21
- Software Composition Analysis Software#10 of 65