Freedom251 › Fuzz Testing Software
Jazzer
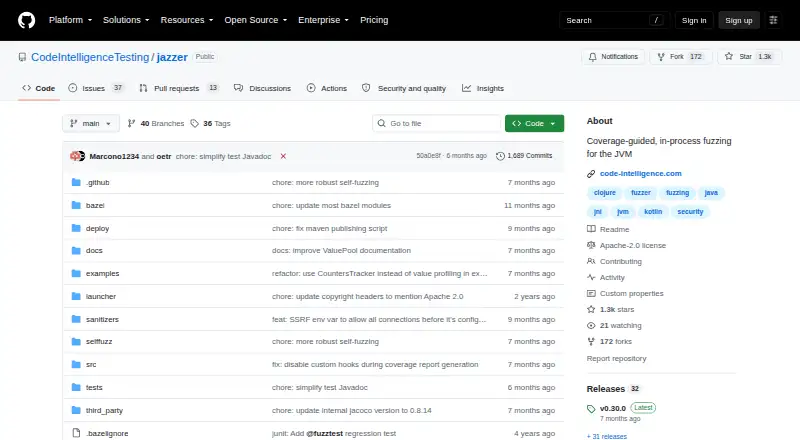
What Jazzer is
Jazzer is a free, coverage-guided in-process fuzzer for JVM applications, based on libFuzzer. It supports Java, Kotlin, Scala, and Clojure targets, along with JNI and native libraries. With JUnit 5.9.0 or newer, fuzz tests can be included alongside regular unit tests. The @FuzzTest annotation lets it generate and mutate method inputs, including primitives, strings, arrays, and standard library classes. Tests can run against saved crashing inputs in regression mode or fuzz for new coverage. Built-in sanitizers detect security issues such as SSRF, file path traversal, and OS command injection, and feed signals back into fuzzing. Jazzer works with Maven, Gradle, and Bazel, or can run as a standalone binary or through its Java main class. Supported systems are Linux x86_64 and arm64, macOS 12 or later on x86_64 and arm64, and Windows x86_64. The jazzer-junit package is available on Maven Central, and the repository uses the Apache-2.0 license.
Who it suits
Jazzer suits developers testing JVM applications and libraries, including Java, Kotlin, Scala, or Clojure projects. Its JUnit integration and build-tool support can fit teams that want fuzz tests alongside their regular test workflows.
What it does well
- JUnit integration supports fuzz tests alongside unit tests.
- Built-in sanitizers flag several Java security issues.
- Works with Maven, Gradle, and Bazel.
- Supports Linux, macOS, and Windows.
- Free under Apache-2.0.
What to know first
- JUnit integration requires JUnit 5.9.0 or newer.
- Windows support is limited to x86_64.
- macOS support requires version 12 or later.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Jazzer | Coverage-guided, in-process fuzzing for the JVM · Linux x86_64 and arm64, macOS 12+ x86_64 and arm64, Windows x86_64 | Free |
| Jazzer open-source | JVM fuzzing · local execution · Apache-2.0 licensed | Free |
As github.com lists them, read 29 Sept 2026. The maker's own page has the final word.
Getting started
- Visit the Jazzer GitHub website.
- Choose the standalone binary from a GitHub release archive or use the Java main class.
- For a JUnit project, use JUnit 5.9.0 or newer and the jazzer-junit package from Maven Central.
- Integrate it with Maven, Gradle, or Bazel as appropriate for your project.
- Add fuzz tests with the @FuzzTest annotation and select regression or fuzzing mode.
Verdict
Jazzer combines coverage-guided fuzzing with JUnit integration and security-focused sanitizers for JVM targets. Its listed platform support and JUnit version requirement are worth checking against a project’s setup.
Questions
How much does Jazzer cost?
Jazzer is free. Its listed plan costs nothing.
Which platforms does Jazzer support?
It supports Linux x86_64 and arm64, macOS 12 or newer on x86_64 and arm64, and Windows x86_64.
Which languages and targets can it fuzz?
Supported languages are Java, Kotlin, Scala, and Clojure. It can also target JVM applications and JNI or native libraries.
Does Jazzer work with JUnit?
Yes. It integrates with JUnit 5.9.0 or newer, with regression mode for saved crashing inputs and fuzzing mode for generating inputs.
Is Jazzer open source?
The GitHub repository identifies Jazzer as licensed under Apache-2.0.
Which build tools does it support?
Its README documents Maven, Gradle, and Bazel, including Bazel support through rules_fuzzing.
Facts from Jazzer's own pages
- Bug detectors
- Built-in sanitizers detect Java security issues including SSRF, file path traversal, and OS command injection, and provide feedback to guide fuzzing. · github.com, 29 Sept 2026
- BugDetectors API
- The public BugDetectors API lets code configure selected detectors, including SSRF and path-traversal checks. · codeintelligencetesting.github.io, 15 Oct 2026
- Build integrations
- Supported build workflows include Maven, Gradle and Bazel, with official rules_fuzzing support for Bazel. · github.com, 15 Oct 2026
- Build tools
- The README documents use with Maven, Gradle, and Bazel, including support through rules_fuzzing. · github.com, 29 Sept 2026
- Company founding
- LinkedIn lists Code Intelligence as founded in 2017. · linkedin.com, 15 Oct 2026
- Company funding record
- Crunchbase shows Code Intelligence with four funding rounds and a Series A led by Tola Capital, while amounts are withheld. · crunchbase.com, 15 Oct 2026
- Company headquarters
- LinkedIn lists Code Intelligence's headquarters in Bonn, North Rhine-Westphalia, Germany. · linkedin.com, 15 Oct 2026
- Company legal name
- Crunchbase identifies the maker as Code Intelligence GmbH. · crunchbase.com, 15 Oct 2026
- Company size
- LinkedIn places Code Intelligence in the 51-200 employee range. · linkedin.com, 15 Oct 2026
- Configuration
- Settings can be supplied through defaults, manifest attributes, environment variables, system properties, JUnit properties or CLI flags. · github.com, 15 Oct 2026
- Corpus handling
- New-coverage inputs are stored in generated corpus directories and failures are stored in inputs directories. · github.com, 15 Oct 2026
- Coverage feedback
- The tool instruments JVM bytecode and uses coverage feedback to guide input mutations. · google.github.io, 15 Oct 2026
- Crash minimization
- The standalone tool includes an option to minimize a crashing input to a smaller reproducer. · github.com, 15 Oct 2026
- Distribution
- The jazzer-junit package is available on Maven Central and the README says it is signed with a published key. · github.com, 29 Sept 2026
- Fuzzing mode
- Setting JAZZER_FUZZ to a non-empty value enables active fuzzing and input mutation. · codeintelligencetesting.github.io, 15 Oct 2026
- FuzzTest annotation
- Developers mark fuzz methods with @FuzzTest, which supports generated parameters and JUnit execution. · codeintelligencetesting.github.io, 15 Oct 2026
- Headquarters
- Bonn, Germany · github.com, 28 Sept 2026
- Independent research limitation
- A 2026 paper reports that its GONDAR system found four times as many vulnerabilities as Jazzer on evaluated Java benchmarks. · arxiv.org, 15 Oct 2026
- Independent research result
- A 2026 study reports that its generated harnesses achieved a median 26% coverage improvement over OSS-Fuzz baselines and exceeded Jazzer AutoFuzz by 5% in package-scope coverage. · arxiv.org, 15 Oct 2026
- Input generation
- The @FuzzTest annotation lets Jazzer automatically generate and mutate method parameter inputs, including primitives, strings, arrays, and standard library classes. · github.com, 29 Sept 2026
- JUnit integration
- Jazzer integrates with JUnit 5.9.0 or newer through the jazzer-junit dependency. · github.com, 15 Oct 2026
- License
- The repository identifies Jazzer as Apache-2.0 licensed. · github.com, 15 Oct 2026
- Limit: open issues
- The public issue tracker includes reports about Android builds, JDK 25 segmentation faults, BigInteger generation stalls and offline instrumentation failures. · github.com, 15 Oct 2026
- Maven artifact
- Maven Central lists com.code-intelligence:jazzer version 0.30.0 and identifies it as Apache-2.0 software. · central.sonatype.com, 15 Oct 2026
Where Jazzer stands on Freedom251
- Fuzz Testing Software#1 of 26