Freedom251 › Fuzz Testing Software
Fuzzilli
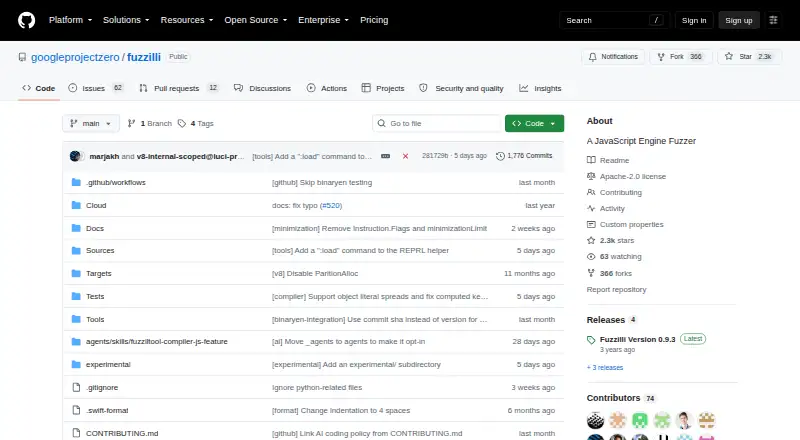
What Fuzzilli is
Fuzzilli is a free, open-source tool for coverage-guided fuzzing of dynamic-language interpreters. It creates test programs in FuzzIL, its own intermediate language, then mutates them and translates them to JavaScript. Mutations can change data flow or operation parameters, generate or splice code, and combine programs from a corpus. The system includes a mutation fuzzer, script runner, corpus, runtime environment, minimizer, evaluator, and lifter. It sends repeated cases to a target engine in a read-eval-print-reset loop: the engine runs a script, resets, and waits for another. Instances can coordinate inside one process or over TCP across machines. Listed target directories include JavaScriptCore, JerryScript, QuickJS, QtJS, Serenity, SpiderMonkey, V8, XS, Duktape, and njs. Setup requires a supported JavaScript engine compiled with coverage instrumentation using clang 4.0 or later, then a Fuzzilli build with Swift Package Manager. Docker and Google Compute Engine tools are available. The project uses Apache-2.0 licensing and says it is not an officially supported Google product.
Who it suits
Fuzzilli suits people fuzzing dynamic-language interpreters, particularly JavaScript engine developers and researchers able to build an instrumented target. The project invites contributions, which require a Contributor License Agreement and GitHub pull-request review.
What it does well
- Coverage-guided input generation, mutation, and hybrid methods.
- Supports multiple listed JavaScript engine targets.
- Instances can coordinate across machines over TCP.
- Docker and Google Compute Engine tooling is available.
What to know first
- Requires building an instrumented supported JavaScript engine.
- Requires Swift Package Manager to build Fuzzilli.
- Not an officially supported Google product.
Limits
Fuzzilli is free, with no trial. The source code requires building both the fuzzer and a supported JavaScript engine with coverage instrumentation.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Fuzzilli | Apache-2.0 licensed source code · requires building the fuzzer and a supported, instrumented JavaScript engine | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Fuzzilli repository on GitHub.
- Choose a supported JavaScript engine and compile it with coverage instrumentation using clang 4.0 or later.
- Build Fuzzilli with Swift Package Manager.
- Run Fuzzilli with the supported target engine; Docker and Google Compute Engine tooling are available for deployment.
Verdict
Fuzzilli offers a configurable fuzzing setup with multiple target engines and coordination options. Building it requires a compatible instrumented engine and the specified toolchain.
Questions
How much does Fuzzilli cost?
The listed plan is free. Fuzzilli is Apache-2.0 licensed open-source software.
Is there a free plan or trial?
Fuzzilli is free. No free trial is offered.
Which platforms does Fuzzilli support?
The listed platforms are Linux, macOS, and self-hosted use.
Which JavaScript engines are listed as targets?
Target directories include JavaScriptCore, JerryScript, QuickJS, QtJS, Serenity, SpiderMonkey, V8, XS, Duktape, and njs.
What is required to build Fuzzilli?
Build a supported JavaScript engine with coverage instrumentation using clang 4.0 or later, then build Fuzzilli with Swift Package Manager.
Is Fuzzilli an officially supported Google product?
No. The project states that it is not an officially supported Google product.
Facts from Fuzzilli's own pages
- Build requirements
- The documented workflow requires compiling a supported engine with coverage instrumentation and building Fuzzilli with Swift. · github.com, 4 Oct 2026
- Cloud deployment
- The project provides Docker scripts and files for local or distributed fuzzing and scripts for setting up and tearing down distributed fuzzing on Google Compute Engine. · github.com, 4 Oct 2026
- Cloud tooling
- Its Cloud directory contains Docker scripts and files, Google Compute Engine setup and teardown scripts, and rudimentary crash triaging. · github.com, 3 Oct 2026
- Contributions
- Project contributions require a Contributor License Agreement and are reviewed through GitHub pull requests. · github.com, 4 Oct 2026
- Core components
- The fuzzer includes a mutation fuzzer, script runner, corpus, runtime environment, minimizer, evaluator, and lifter. · github.com, 4 Oct 2026
- Deployment
- The project says Fuzzilli and supported engines can be built and run inside Docker and on Google Compute Engine. · github.com, 3 Oct 2026
- Distributed fuzzing
- Multiple instances can synchronize over a TCP-based protocol across machines or through dispatch queues within one process. · github.com, 4 Oct 2026
- Execution
- Fuzzilli uses a read-eval-print-reset-loop mode in which a modified target engine accepts scripts over pipes or shared memory, executes them, resets, and waits for the next script. · github.com, 3 Oct 2026
- Execution mode
- Fuzzilli uses a Read-Eval-Print-Reset-Loop to run repeated test cases in a target process and reduce process startup overhead. · github.com, 4 Oct 2026
- Fuzzer components
- The listed components include a mutation fuzzer, script runner, corpus, environment, minimizer, evaluator, and lifter. · github.com, 3 Oct 2026
- Google support
- The repository states that Fuzzilli is not an officially supported Google product. · github.com, 4 Oct 2026
- Intended users
- The project describes Fuzzilli as a tool for fuzzing dynamic language interpreters and invites patches and other contributions. · github.com, 3 Oct 2026
- License
- The repository identifies its license as Apache-2.0. · github.com, 4 Oct 2026
- Mutation
- Its mutators change program data flow, generate or splice code, combine corpus programs, and alter operation parameters. · github.com, 4 Oct 2026
- Mutations
- Its documented mutators can change data flow, generate or splice code, combine corpus programs, and modify operation parameters. · github.com, 3 Oct 2026
- Purpose
- Fuzzilli is a coverage-guided fuzzer for dynamic language interpreters that mutates programs in FuzzIL and translates them to JavaScript. · github.com, 4 Oct 2026
- Scaling
- Multiple instances can synchronize within one process or over a TCP-based protocol, allowing scaling across cores and machines. · github.com, 3 Oct 2026
- Security disclosure
- The project asks users to send a short note, possibly with a CVE number, or open a pull request to have a vulnerability found with Fuzzilli considered for the bug showcase. · github.com, 3 Oct 2026
- Security findings
- The repository’s bug showcase lists security-impacting bugs found with Fuzzilli in JavaScript engines including WebKit, SpiderMonkey, V8, Duktape, JerryScript, and Hermes. · github.com, 4 Oct 2026
- Security results
- The repository’s bug showcase lists security issues found with Fuzzilli across engines including WebKit/JavaScriptCore, SpiderMonkey, V8, Duktape, JerryScript, and Hermes. · github.com, 3 Oct 2026
- Supported targets
- The target directory lists JavaScriptCore, JerryScript, QuickJS, QtJS, Serenity, SpiderMonkey, V8, XS, Duktape, and njs. · github.com, 4 Oct 2026
- Support status
- The repository states that Fuzzilli is not an officially supported Google product. · github.com, 3 Oct 2026
- What it does
- Fuzzilli is a coverage-guided fuzzer for dynamic language interpreters, built around a custom intermediate language called FuzzIL that can be mutated and translated to JavaScript. · github.com, 3 Oct 2026
Where Fuzzilli stands on Freedom251
- Fuzz Testing Software#10 of 26