Freedom251 › SaaS Security Posture Management Software
FailSafe
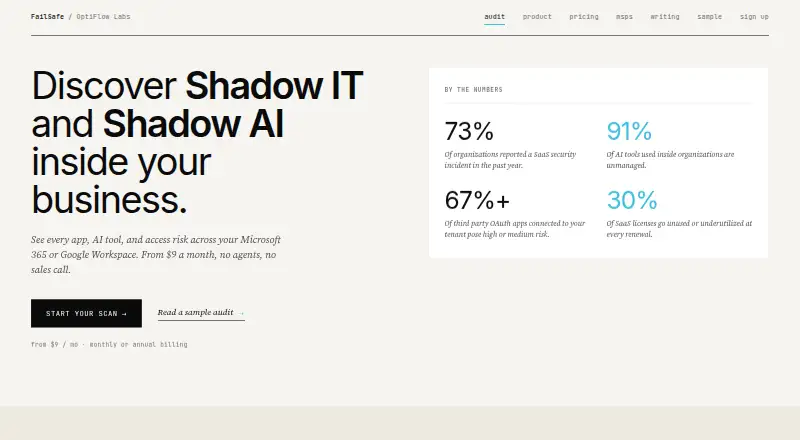
What FailSafe is
FailSafe is an agentless SaaS Security Posture Management platform for small and midsize businesses and managed service providers. It discovers SaaS and AI applications, OAuth permissions, shadow IT, and shadow AI across connected tenants. Connections to Microsoft 365 and Google Workspace use read-only API access, with no device agents to install. FailSafe includes SaaS inventory, AI tool discovery, OAuth grant visibility, license waste detection, stale access review, and drift detection.
The platform scores security posture from A to F and produces PDF reports mapped to NIST CSF, CIS v8, SOC 2, and ISO 27001. Financial transaction cross-reference and endpoint inventory are additional discovery layers; endpoint posture is included in Shadow IT Complete. The MSP offering includes a portfolio dashboard, white-labeled PDF reports, role-based isolation across client engagements, API keys, PSA webhooks, and SIEM export. Customer data is encrypted in transit and at rest, production infrastructure is in the United States, and customer data is not used to train AI models. The maker says FailSafe is not currently SOC 2 attested and has not had a third-party penetration test. The free plan covers up to 80 users in one organization; paid plans start at $9/mo.
Who it suits
FailSafe suits small and midsize businesses or MSPs that want read-only visibility into SaaS applications, AI tools, permissions, and security posture. Its MSP features may fit providers managing multiple client engagements who need portfolio reporting and integrations.
What it does well
- Connects to Microsoft 365 and Google Workspace through read-only API access.
- Discovers SaaS and AI applications, OAuth permissions, shadow IT, and shadow AI.
- Scores posture from A to F and maps PDF reports to four frameworks.
- Includes license waste detection, stale access review, and drift detection.
- MSP plans include portfolio reporting and role-based client isolation.
What to know first
- Automated remediation is not included.
- FailSafe is not currently SOC 2 attested.
- The maker says it has not yet had a third-party penetration test.
- The Shadow IT, Shadow IT Plus, and Shadow IT Complete plans have a 12 month term.
Limits
The free plan supports up to 80 users in one organization. The cheapest paid plan, Shadow IT, costs $9 a month on a 12 month term and also covers up to 80 users in one organization.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | Up to 80 users · one organization · no card required | Free |
| Shadow IT Complete | $189/mo or $2,079/yr (one free month); 12 month term · Unlimited users · flat rate | $189 a month |
| Shadow IT Plus | $29/mo or $319/yr (one free month); 12 month term · Up to 80 users · one organization | $29 a month |
| Shadow IT | $9/mo or $99/yr (one free month); 12 month term · Up to 80 users · one organization | $9 a month |
| FailSafe for MSPs | Custom quoted per seat across portfolio · Pricing varies by portfolio size, platform mix, and integration scope | On request |
| Enterprise | Quote based · Dedicated security engineer · included remediation hours · SSO · MSA and DPA · SLA | On request |
As optiflowlabs.ai lists them, read 7 Oct 2026. The maker's own page has the final word.
Getting started
- Visit https://optiflowlabs.ai/.
- Start with the free plan, which requires no card, or choose a paid plan.
- Connect Microsoft 365 or Google Workspace through read-only API access.
- Review discovered applications, permissions, and security posture in the web platform.
- For the MSP offering, request partner information; partner inquiries receive a response within one business day and include a 15 minute scoping call.
Overview
FailSafe is a read-only SaaS security posture management platform for small and midsize businesses and managed service providers. It suits teams that need to find SaaS and AI app exposure across Microsoft 365 or Google Workspace without installing device agents. Its discovery and compliance reporting are useful, but findings still require manual follow-up.
Key features
FailSafe discovers SaaS and AI applications, OAuth permissions, shadow IT, and shadow AI across connected tenants. Its A-to-F posture scores give teams a simple way to prioritize what to review, while inventory, OAuth grant visibility, license-waste detection, stale-access review, and drift detection address distinct sources of exposure and sprawl. Read-only API access limits the platform to observation: it does not offer automated remediation.
PDF reports map security posture to NIST CSF, CIS v8, SOC 2, and ISO 27001, making them useful for organizing compliance reviews. Financial transaction cross-reference and endpoint inventory are additional discovery layers; endpoint posture is included in Shadow IT Complete. The added layers can broaden visibility, but buyers should distinguish those options from the core discovery scope.
For MSPs, FailSafe offers a centralized portfolio dashboard, white-labeled PDF reports, and role-based isolation across client engagements. The offering lists API keys, PSA webhooks for ConnectWise, Autotask, and Halo, plus SIEM export in CEF, Splunk HEC, Datadog, and JSON formats. These integrations and portfolio controls make it more suitable for managing multiple clients than a single-organization plan. Partner inquiries receive a response within one business day and include a 15-minute scoping call.
Customer data is encrypted in transit and at rest, production infrastructure is in the United States, and customer data is not used to train AI models. Email Intelligence, when enabled, reads transactional SaaS signals, does not retain raw message bodies after processing, and can be disabled at any time. A significant qualification for security-conscious buyers is that FailSafe is not currently SOC 2 attested and has not yet had a third-party penetration test; SOC 2 Type 1 is targeted for 2027.
Pricing
The Free plan costs nothing and covers up to 80 users in one organization, with no card required. It is a practical way to start with a small team, but the 80-user and single-organization caps rule it out for larger deployments or multi-client MSP use. There is no free trial; the free plan is the entry point instead.
Shadow IT costs $9 a month, billed $9/mo or $99/yr (one free month), on a 12 month term. It keeps the same limit of up to 80 users and one organization, so the main step up from Free is a paid plan rather than added scale. Shadow IT Plus costs $29 a month, billed $29/mo or $319/yr (one free month), also on a 12 month term and with the same user and organization limits. The available plan details do not distinguish its added capabilities, so buyers should confirm the differences before choosing between the two paid tiers.
Shadow IT Complete costs $189 a month, billed $189/mo or $2,079/yr (one free month), on a 12 month term. Its unlimited-user flat rate and included endpoint posture make it the clearest fit for organizations that need broader discovery or have more than 80 users. FailSafe for MSPs has custom pricing, quoted per seat across the portfolio; pricing varies by portfolio size, platform mix, and integration scope. Enterprise is quote based and includes a dedicated security engineer, remediation hours, SSO, an MSA and DPA, and an SLA. These custom tiers suit buyers needing portfolio-level services or enterprise terms, but do not provide a published price for budgeting.
Platforms
FailSafe is available through API and web access. Its supported SaaS connections are Microsoft 365 and Google Workspace, using read-only API access with no device agents to install. It is not a device-agent deployment, and its discovery scope depends on connected tenants.
Who it's for
FailSafe fits SMB security teams and MSPs that want a consolidated view of SaaS and AI use, OAuth permissions, access drift, and compliance posture without granting write access. Shadow IT Complete is the stronger fit when endpoint posture or more than 80 users matter; MSPs should consider the portfolio offering for centralized client management. Organizations that require automated fixes, current SOC 2 attestation, or a completed third-party penetration test should look elsewhere.
Pros and cons
- Pro: Read-only connections to Microsoft 365 and Google Workspace enable SaaS and AI discovery without installing device agents.
- Pro: A-to-F scoring and reports mapped to four named frameworks give teams a way to prioritize and organize compliance work.
- Pro: MSP portfolio controls, white-labeled reports, and multiple PSA and SIEM integrations support multi-client operations.
- Con: No automated remediation means teams must act on findings through other tools or processes.
- Con: Free and the two lower paid plans cap coverage at 80 users and one organization.
- Con: FailSafe is not SOC 2 attested and has not yet completed a third-party penetration test, a material limitation for buyers with assurance requirements.
Alternatives
For a broader set of published platform options, browse SaaS Security Posture Management Software.
- Cloudflare Access is worth comparing if its free plan for under 50 users or its broader listed platform coverage better fits your needs.
- Qualys External Attack Surface Management may suit buyers who want a 30-day no-cost CSAM with EASM period to evaluate instead.
- Obsidian Security is an alternative with a free plan for up to 1K users and discovery of app sprawl, unsanctioned AI, and shadow SaaS.
- Onam Security API Security is a better candidate when API security is the priority, with a free plan covering one cloud account and up to 500 resources.
- Skyhigh Private Access is another paid option for teams seeking private access software.
- ClosedSSPM is a free alternative for buyers comparing SaaS security posture management options.
- Aperio is a free alternative to consider.
- AppOmni may fit buyers prepared for a $7,500 a year, 12-month contract for 100 users per SaaS application.
Verdict
Choose FailSafe if you are an SMB or MSP that needs agentless, read-only discovery of SaaS and AI exposure, posture scoring, and compliance-oriented reports. Its strongest case is combining that visibility with MSP portfolio controls and integrations. Look elsewhere if you need automated remediation or require a provider that is already SOC 2 attested or has completed a third-party penetration test.
Verdict
Choose FailSafe if your organization or MSP needs read-only SaaS discovery, posture scoring, and compliance reporting. Look elsewhere if you need automated remediation or require a provider that is already SOC 2 attested or has completed a third-party penetration test.
Questions
Does FailSafe have a free plan or trial?
Yes, its Free plan costs 0.00 USD and requires no card. There is no free trial.
What does the cheapest paid plan cost?
Shadow IT costs $9 a month, or $99 per year with one free month, on a 12 month term.
Which services can FailSafe connect to?
It connects to Microsoft 365 and Google Workspace using read-only API access. No device agents need to be installed.
Does FailSafe support automated remediation?
No. Its access model is read-only, and automated remediation is not included.
What does FailSafe for MSPs include?
The MSP offering lists API keys, PSA webhooks for ConnectWise, Autotask, and Halo, and SIEM export in CEF, Splunk HEC, Datadog, and JSON formats. It also includes a centralized portfolio dashboard, white-labeled PDF reports, and role-based isolation across client engagements.
Is FailSafe SOC 2 attested?
The maker says FailSafe is not currently SOC 2 attested and has not yet had a third-party penetration test. SOC 2 Type 1 is targeted for 2027.
Facts from FailSafe's own pages
- Discovery
- It discovers SaaS and AI applications, OAuth permissions, shadow IT, and shadow AI across connected tenants. · optiflowlabs.ai, 7 Oct 2026
- Email privacy
- Email Intelligence reads transactional SaaS signals when enabled, does not retain raw message bodies after processing, and can be disabled at any time. · optiflowlabs.ai, 7 Oct 2026
- Features
- Features include SaaS inventory, AI tool discovery, OAuth grant visibility, license waste detection, stale access review, and drift detection. · optiflowlabs.ai, 7 Oct 2026
- Headquarters
- San Diego, California, United States · optiflowlabs.ai, 28 Sept 2026
- MSP capabilities
- The MSP platform includes a centralized portfolio dashboard, white labeled PDF reports, and role based isolation across client engagements. · optiflowlabs.ai, 7 Oct 2026
- MSP integrations
- The MSP offering lists API keys, PSA webhooks for ConnectWise, Autotask, and Halo, and SIEM export in CEF, Splunk HEC, Datadog, and JSON formats. · optiflowlabs.ai, 7 Oct 2026
- Optional discovery layers
- Financial transaction cross reference and endpoint inventory are additional discovery layers, with endpoint posture included in Shadow IT Complete. · optiflowlabs.ai, 7 Oct 2026
- Product
- FailSafe is an agentless SaaS Security Posture Management platform for small and midsize businesses and MSPs. · optiflowlabs.ai, 7 Oct 2026
- Reporting
- It scores security posture from A to F and produces PDF reports mapped to NIST CSF, CIS v8, SOC 2, and ISO 27001. · optiflowlabs.ai, 7 Oct 2026
- Security
- The security overview states that customer data is encrypted in transit and at rest, production infrastructure is in the United States, and no customer data is used to train AI models. · optiflowlabs.ai, 7 Oct 2026
- Security limits
- The maker says FailSafe is not currently SOC 2 attested and has not yet had a third party penetration test; SOC 2 Type 1 is targeted for 2027. · optiflowlabs.ai, 7 Oct 2026
- Support
- The MSP page says partner inquiries receive a response within one business day and include a 15 minute scoping call. · optiflowlabs.ai, 7 Oct 2026
- Supported platforms
- FailSafe connects to Microsoft 365 and Google Workspace using read only API access, with no device agents to install. · optiflowlabs.ai, 7 Oct 2026