Freedom251 › SaaS Security Posture Management Software
ClosedSSPM
What ClosedSSPM is
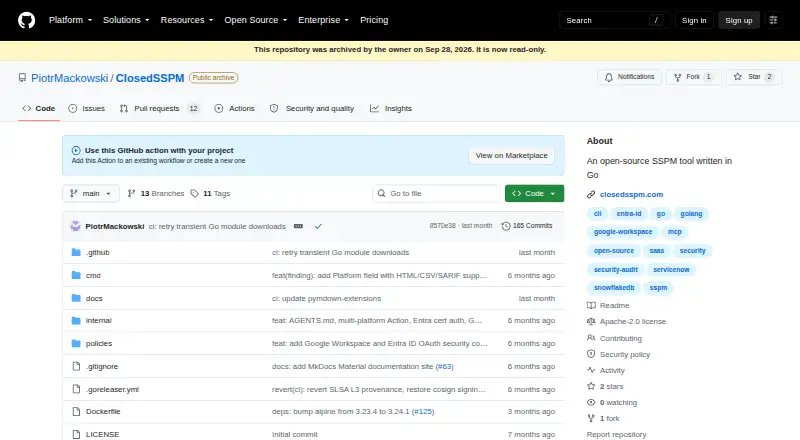
ClosedSSPM is a free, open-source tool that audits SaaS platforms for security misconfigurations and provides remediation guidance. It checks ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID, with 166 checks across the four services. A customizable YAML policy engine defines the checks, and the tool operates read-only without changing audited platforms. Results can be exported as HTML, JSON, CSV, or SARIF. Users can save platform snapshots for analysis without live access, and SARIF reports can be imported into DefectDojo. An MCP server lets AI agents analyze scan results and suggest fixes; a GitHub Action and a failure threshold support automated security gates in CI/CD. The project says credentials are read from environment variables and are not saved to disk or configuration files. Snapshots may contain sensitive SaaS configuration data and should be treated as confidential. Installation options include Homebrew, downloadable binaries, Debian and RPM packages, Docker, or building from source. ClosedSSPM is Apache 2.0 licensed. Its GitHub repository was archived on September 28, 2026 and is read-only.
Who it suits
It suits security teams that need read-only checks across the listed SaaS platforms and want report exports or CI/CD gating. Users should account for the archived, read-only repository and handle saved snapshots as confidential data.
What it does well
- 166 checks across four SaaS platforms
- Read-only operation does not write to audited services
- Exports HTML, JSON, CSV, and SARIF reports
- Supports offline snapshot analysis and DefectDojo import
- Credentials are not persisted to disk or config files
What to know first
- GitHub repository is archived and read-only
- Snapshots may contain sensitive configuration data
Limits
ClosedSSPM is free, with no free-trial period. Its checks cover ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID; the repository is archived and read-only.
Getting started
- Visit the GitHub project page.
- Choose an installation route: Homebrew, platform binary, Debian or RPM package, Docker, or source build.
- Provide credentials through environment variables.
- Run an audit against a supported service, or analyze a saved platform snapshot offline.
- Review results in HTML, JSON, CSV, or SARIF format.
ClosedSSPM is a free, open-source scanner for SaaS security misconfigurations and remediation guidance. It is most suitable for teams managing ServiceNow, Snowflake, Google Workspace, or Microsoft Entra ID that want repeatable, customizable audits without write access. Its strongest case is focused, automation-friendly coverage; its archived repository is the main reason to consider another product.
Overview
ClosedSSPM concentrates on four enterprise services rather than attempting broad SaaS discovery. It performs permission and configuration analysis, supports compliance monitoring, and keeps every audit read-only, so scans cannot alter the systems being assessed. That makes it a sensible fit for cautious security reviews and scheduled control checks, but not for teams seeking automatic remediation.
The project is licensed under Apache 2.0. Credentials are read from environment variables and are not persisted to disk or configuration files, reducing exposure from local configuration storage. Saved snapshots can include sensitive SaaS configuration data, however, and should be handled as confidential records. The GitHub repository was archived on September 28, 2026 and is read-only, a material maintenance risk for organizations that need an actively evolving security tool.
Key features
Platform-specific coverage
The project lists 166 checks: 86 for ServiceNow, 55 for Snowflake, 15 for Microsoft Entra ID, and 10 for Google Workspace. ServiceNow coverage spans ACLs, roles, scripts, integrations, configuration, users, and static analysis, making it the best-supported target. Google Workspace coverage is much narrower, so organizations relying heavily on that service should not mistake the platform list for equal depth.
Custom policies and reporting
A YAML policy engine lets security teams tailor checks to internal requirements. Reports can be exported as HTML, JSON, CSV, or SARIF, covering both human review and machine-readable workflows. SARIF import into DefectDojo gives teams a route to centralized vulnerability management rather than leaving findings in isolated scan files.
Automation and offline work
A GitHub Action and the --fail-on threshold support CI/CD gates that can stop a pipeline when findings exceed a chosen level. Users can save platform snapshots and analyze them later without live access, useful for controlled or intermittent-access environments. An MCP server allows AI agents to inspect scan results and suggest fixes; suggestions still require human implementation because ClosedSSPM remains read-only.
Pricing
ClosedSSPM is free, with no paid tiers and no free trial. There is no seat charge or usage quota stated, so its cost advantage is clearest for teams able to operate an open-source, self-managed scanner. The trade-off is that the archived repository provides no active development path, which can matter more than license cost for long-lived compliance programs.
Platforms
It is available through an API and runs on Linux, macOS, Windows, and self-hosted deployments. Installation options include Homebrew, downloadable platform binaries, Debian and RPM packages, Docker, and source builds. This range suits engineering-led deployments, while teams wanting a vendor-hosted web service will need another approach.
Who it's for
Choose ClosedSSPM when your security program centers on the four supported SaaS platforms, requires read-only assurance, and benefits from policy-as-code, CI/CD enforcement, or offline snapshots. It is particularly attractive to ServiceNow and Snowflake owners because those services account for most of the checks. Look elsewhere if you need broader SaaS coverage, active repository maintenance, or remediation that changes cloud settings automatically.
Pros and cons
- Pros: 166 checks across four named SaaS platforms provide concrete, service-specific coverage.
- Pros: YAML policies, multiple report formats, GitHub Actions, and a failure threshold support repeatable security operations.
- Pros: Read-only scans and non-persisted credentials limit operational and credential-storage risk.
- Pros: Offline snapshot analysis and DefectDojo SARIF import extend use beyond a single live scan.
- Cons: Coverage is uneven, with only 10 Google Workspace checks.
- Cons: Snapshots may contain sensitive configuration data and require confidential handling.
- Cons: The repository was archived and is read-only, creating uncertainty around future fixes and platform changes.
Alternatives
Cloudflare Access is a freemium, multi-platform access product with a free plan for under 50 users and a $7-per-month pay-as-you-go plan; pick it when access control is the priority rather than read-only posture auditing.
FailSafe offers a free tier for up to 80 users and one organization, with paid Shadow IT coverage; choose it when user and shadow-IT limits matter more than ClosedSSPM's four-service checks.
Qualys External Attack Surface Management provides a 30-day no-cost CSAM with EASM trial; it is the better fit for a time-limited evaluation of external attack-surface management.
Obsidian Security has a free plan for up to 1,000 users and a paid Advanced tier; consider it when SaaS discovery and spear-phishing detection are the goal.
Onam Security API Security has a free tier covering one cloud account, 500 resources, and 30 days of finding history, with a $22-per-month Pro plan; choose it for cloud and API-focused resource monitoring.
Skyhigh Private Access is a paid access product with pricing not listed.
Aperio is a free, self-hosted option for teams wanting another open-source deployment.
AppOmni is a paid SaaS security platform with a $7,500-per-year plan for 100 users per SaaS application; select it when vendor-backed, contract-based SaaS security is preferable.
Verdict
ClosedSSPM is a strong fit for technically capable teams auditing ServiceNow or Snowflake that want free, customizable, read-only checks and automation-friendly outputs. Its focused coverage, offline analysis, and CI/CD integration are practical strengths. Choose another product if ongoing maintenance, wider service coverage, or active vendor development is more important than a no-cost Apache-licensed scanner.
Verdict
ClosedSSPM offers broad checks and several reporting and automation options, while keeping audits read-only. Its archived repository is an important limitation for teams evaluating ongoing maintenance.
Questions
Is ClosedSSPM free?
Yes. It is free, and the project lists no free trial.
Which platforms does ClosedSSPM audit?
It audits ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID.
Is ClosedSSPM open source, and what is its license?
Yes. It is open source and licensed under Apache 2.0.
What reports can ClosedSSPM produce?
It generates HTML, JSON, CSV, and SARIF reports. SARIF reports can be imported into DefectDojo.
Is the repository maintained as an active project?
The GitHub repository was archived on September 28, 2026 and is read-only.
How can I install ClosedSSPM?
Installation options include Homebrew, platform binaries, Debian and RPM packages, Docker, and building from source.
Facts from ClosedSSPM's own pages
- AI analysis
- An MCP server lets AI agents analyze scan results and suggest fixes. · closedsspm.com, 7 Oct 2026
- CI/CD integration
- The project provides a GitHub Action and a --fail-on threshold for automated security gates. · closedsspm.com, 7 Oct 2026
- Credential handling
- The security policy says credentials are read from environment variables and are not persisted to disk or config files. · github.com, 7 Oct 2026
- DefectDojo integration
- SARIF reports can be imported into DefectDojo for centralized vulnerability management. · github.com, 7 Oct 2026
- Downloads
- Installation options include Homebrew, platform binaries, Debian and RPM packages, Docker, and building from source. · github.com, 7 Oct 2026
- Installation
- The README lists Homebrew, downloadable binaries, Debian/Ubuntu packages, Red Hat/Fedora packages, Docker, and source builds. · github.com, 7 Oct 2026
- License and maintainer
- The project is licensed under Apache 2.0 and its documentation credits Piotr Mackowski. · closedsspm.com, 7 Oct 2026
- Offline analysis
- Users can save platform snapshots and analyze them later without live access. · closedsspm.com, 7 Oct 2026
- Policy engine
- Security checks use a YAML policy engine that users can customize. · closedsspm.com, 7 Oct 2026
- Project status
- The GitHub repository was archived on September 28, 2026 and is read-only. · github.com, 7 Oct 2026
- Purpose
- ClosedSSPM is an open source tool that audits SaaS platforms for security misconfigurations and provides remediation guidance. · closedsspm.com, 7 Oct 2026
- Read-only operation
- The tool is read-only and does not write to audited SaaS platforms. · github.com, 7 Oct 2026
- Reports
- It generates reports in HTML, JSON, CSV, and SARIF formats. · closedsspm.com, 7 Oct 2026
- Security checks
- The project lists 166 checks across four platforms: 86 for ServiceNow, 55 for Snowflake, 15 for Entra ID, and 10 for Google Workspace. · closedsspm.com, 7 Oct 2026
- Security design
- The security policy says the tool is read-only, does not persist credentials, and uses stdio-only transport for its MCP server. · github.com, 7 Oct 2026
- ServiceNow checks
- ServiceNow audits include 86 checks covering ACLs, roles, scripts, integrations, configuration, users, and static analysis. · closedsspm.com, 7 Oct 2026
- Snapshot handling
- The project warns that collected snapshots may contain sensitive configuration data and should be treated as confidential. · github.com, 7 Oct 2026
- Snapshot sensitivity
- Snapshots may contain sensitive SaaS configuration data and should be treated as confidential. · github.com, 7 Oct 2026
- Supported platforms
- It audits ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID. · closedsspm.com, 7 Oct 2026
- Supported services
- It audits ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID. · closedsspm.com, 7 Oct 2026