Freedom251 › SaaS Security Posture Management Software
Aperio
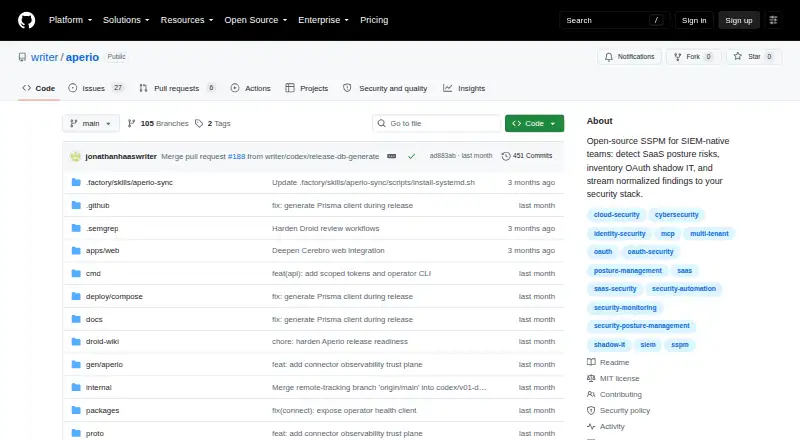
What Aperio is
Aperio is an open-source SaaS Detection & Response platform for identifying SaaS posture risks, tracking OAuth shadow IT, and sending findings to security systems. Its connectors cover GitHub, Slack, Google Workspace, Okta, 1Password, Microsoft 365, and Atlassian Jira and Confluence. Detection rules include public GitHub repositories, Slack workspace 2FA enforcement, and Google Workspace sharing, admin, Gmail, delegation, and OAuth risks. Okta, 1Password, Microsoft 365, and Atlassian are connection-only, with their rule packs pending. Findings can retain evidence, receive severity scores, be deduplicated, and resolve automatically if a later sync no longer detects the signal. A Google Workspace token scan inventories third-party OAuth apps and rates risk by scope sensitivity. Findings can be sent to Splunk HEC, Panther, Panopticon, Elasticsearch, Datadog Logs, webhooks, or JSON Lines files. Listed working remediation handlers can suspend Okta users, reset Okta MFA, and revoke Slack OAuth apps. Provider-side changes require human approval, with response actions using two-person approval. Aperio is MIT licensed and supports self-hosted Compose deployment; documented local setup requires PostgreSQL 15 or later.
Who it suits
Aperio suits security teams that need SaaS posture checks, OAuth app inventory, and findings routed into security systems. Its self-hosted deployment and human-gated response controls may fit organizations managing provider-side actions.
What it does well
- Findings retain evidence and support deduplication.
- Google Workspace scan inventories OAuth apps by risk.
- SIEM delivery supports retries and deduplication.
- Working remediation handlers cover Okta and Slack.
What to know first
- Four connector groups are connection-only, with rules pending.
- Local setup requires PostgreSQL 15 or later.
- Provider-side writes require human approval.
- Some remediation handlers are stubbed.
Limits
Aperio is free and open source. Okta, 1Password, Microsoft 365, and Atlassian connectors are connection-only, with rule packs pending; the documented local setup requires PostgreSQL 15 or later.
Getting started
- Visit the Aperio GitHub repository.
- Prepare PostgreSQL 15 or later for the documented local setup.
- Deploy Aperio with the self-hosted Compose option.
- Connect the SaaS services you want to monitor.
- Configure a listed SIEM destination, webhook, or JSON Lines delivery target.
Verdict
Aperio brings SaaS detection, OAuth inventory, incident handling, and SIEM delivery into an open-source platform. Its connector rule coverage is uneven, and listed response actions include both working handlers and stubs.
Questions
How much does Aperio cost?
It is listed as free and open source.
What license does Aperio use?
The repository identifies Aperio as MIT licensed.
Which services can Aperio connect to?
Its built-in connectors cover GitHub, Slack, Google Workspace, Okta, 1Password, Microsoft 365, and Atlassian Jira and Confluence.
Which platforms are listed?
Listed platforms include API, Linux, self-hosted, and web.
What does the local deployment require?
The documented local setup uses self-hosted Compose and requires PostgreSQL 15 or later.
Can Aperio make changes in connected services automatically?
Provider-side writes require human approval. Response actions use two-person approval; listed working handlers can suspend Okta users, reset Okta MFA, and revoke Slack OAuth apps.
Facts from Aperio's own pages
- Approval controls
- Agent proposals require human approval before provider-side writes, and response actions use two-person approval. · github.com, 9 Oct 2026
- Connector limits
- Okta, 1Password, Microsoft 365, and Atlassian are listed as connection-only, with their rule packs pending. · github.com, 9 Oct 2026
- Deployment
- Aperio can be run with a self-hosted Compose deployment and requires PostgreSQL 15 or later for the documented local setup. · github.com, 9 Oct 2026
- Detection coverage
- The repository lists detections for public GitHub repositories, Slack workspace 2FA enforcement, and several Google Workspace sharing, admin, Gmail, delegation, and OAuth risks. · github.com, 9 Oct 2026
- Findings
- Findings support evidence persistence, severity scoring, deduplication, risk exceptions, and automatic resolution when a signal disappears on a later sync. · github.com, 9 Oct 2026
- Founded
- 2020 · github.com, 28 Sept 2026
- Headquarters
- San Francisco, California, United States · github.com, 28 Sept 2026
- Human approval
- Agent proposals require human approval before provider-side writes, and response actions are described as human-gated with separation of duties. · github.com, 9 Oct 2026
- Incident handling
- It opens and deduplicates incidents with evidence and a replayable timeline, and can auto-resolve findings after a later sync no longer detects the signal. · github.com, 9 Oct 2026
- License
- The repository identifies Aperio as MIT licensed. · github.com, 9 Oct 2026
- Maker
- The GitHub repository is published under the writer organization. · github.com, 9 Oct 2026
- OAuth inventory
- A per-user Google Workspace token scan catalogs third-party OAuth apps and assigns CRITICAL, HIGH, MEDIUM, or LOW risk levels based on scope sensitivity. · github.com, 9 Oct 2026
- Purpose
- Aperio is an open-source SaaS Detection & Response platform for detecting SaaS posture risks, inventorying OAuth shadow IT, and streaming findings to security systems. · github.com, 9 Oct 2026
- Remediation
- The repository lists working remediation handlers for suspending Okta users, resetting Okta MFA, and revoking Slack OAuth apps; other handlers are described as stubbed and pluggable. · github.com, 9 Oct 2026
- SaaS connectors
- Built-in connectors cover GitHub, Slack, Google Workspace, Okta, 1Password, Microsoft 365, and Atlassian Jira and Confluence. · github.com, 9 Oct 2026
- Security
- Connector credentials are encrypted at rest with AES-256-GCM; the stack also lists cookie sessions, TOTP MFA, and role-based access control. · github.com, 9 Oct 2026
- Security controls
- The repository describes AES-256-GCM encryption for credentials, cookie sessions, TOTP MFA, role-based access control, and organization-scoped tenant isolation. · github.com, 9 Oct 2026
- SIEM delivery
- SIEM deliveries use a durable outbox with retries and deduplication by finding and destination. · github.com, 9 Oct 2026
- SIEM integrations
- SIEM destinations include Splunk HEC, Panther, Panopticon, Elasticsearch, Datadog Logs, generic webhooks, and JSON Lines files. · github.com, 9 Oct 2026
- Tenant isolation
- The repository describes Aperio as multi-tenant, with organization scoping and tenant isolation enforced at route, repository, and integration layers. · github.com, 9 Oct 2026