Freedom251 › Container Engines
Enroot
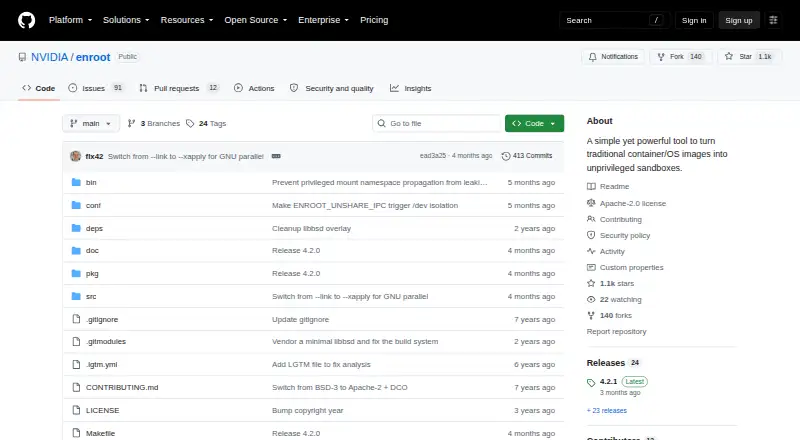
What Enroot is
Enroot is a free, open-source Linux command-line utility that turns container and operating system images into unprivileged sandboxes. Its project describes it as suited to high-performance computing and virtualized environments where portability and reproducibility matter and extra isolation is not warranted. Enroot uses Linux user and mount namespaces to preserve filesystem separation, while providing little to no isolation.
The utility runs without a daemon and supports multi-user use without a setuid binary. Its commands cover batch, bundle, create, exec, export, import, list, remove, and start operations. It imports known container image formats, including Docker images; the README reports a 3x to 5x speedup for importing large Docker images.
Built-in GPU support uses libnvidia-container. Standard hooks can provide NVIDIA GPU support or inject Mellanox host MOFED for InfiniBand HCA support. Optional GPU requirements include NVIDIA drivers version 361.93 or later and libnvidia-container-tools version 1.0 or later. Runtime configuration can be set in enroot.conf or with environment variables, which take precedence. Enroot offers standard and hardened package flavors; the hardened flavor is described as slightly more secure but with greater overhead. It is released under Apache License 2.0 and requires Linux kernel 3.10 or later with support for namespaces, user namespaces, and seccomp filters.
Who it suits
Enroot suits Linux users in high-performance computing or virtualized environments who need portable, reproducible container sandboxes and can work with little to no isolation. It is also a fit for multi-user setups that need rootless operation without a daemon or setuid binary.
What it does well
- Free utility released under Apache License 2.0.
- Runs without a daemon or setuid binary.
- Supports unprivileged multi-user use.
- Imports Docker images and other known image formats.
- Includes GPU support and hooks for NVIDIA and Mellanox capabilities.
- Offers standard and hardened package flavors.
What to know first
- Provides little to no isolation.
- Requires Linux kernel 3.10 or later and specified kernel features.
- GPU support has additional driver and tool requirements.
- The hardened package flavor has greater overhead.
Limits
Enroot provides little to no isolation. It requires Linux kernel 3.10 or later with support for namespaces, user namespaces, and seccomp filters; optional GPU support also requires NVIDIA drivers version 361.93 or later and libnvidia-container-tools version 1.0 or later.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Enroot (Apache-2.0) | Open-source command-line utility · Linux kernel >= 3.10 · standard and hardened package flavors | Free |
As github.com lists them, read 8 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Enroot project on GitHub.
- Check that the host runs Linux kernel 3.10 or later with namespace, user namespace, and seccomp filter support.
- Install a package for a Debian-based or RHEL-based distribution, or build from source using the instructions for Debian, RHEL, or Arch.
- Choose the standard or hardened package flavor.
- Import a supported image, then use the command line to create and start a sandbox.
- For optional GPU support, meet the listed NVIDIA driver and libnvidia-container-tools requirements.
Verdict
Pick Enroot for Linux container workflows where rootless operation, portability, and reproducibility matter more than strong isolation. Look elsewhere if your use case requires substantial isolation; Enroot is explicitly described as providing little to none.
Questions
Is Enroot free?
Yes. The listed plan is $0.00 per free, and the project is released under Apache License 2.0.
Which systems does Enroot support?
Enroot is for Linux and self-hosted use. Installation instructions provide packages for Debian-based and RHEL-based distributions and source build instructions for Debian, RHEL, and Arch-based distributions.
Does Enroot support Docker images?
Yes. It can import known container image formats, including Docker images.
Does Enroot support GPUs?
Built-in GPU support uses libnvidia-container. Optional requirements include NVIDIA drivers version 361.93 or later and libnvidia-container-tools version 1.0 or later.
How isolated are Enroot sandboxes?
Enroot uses Linux user and mount namespaces to maintain filesystem separation, but the project describes its isolation as little to none.
Who makes Enroot?
Enroot is the NVIDIA project hosted at github.com/NVIDIA/enroot.
Facts from Enroot's own pages
- Configuration
- Runtime configuration can be set in enroot.conf or through environment variables, which take precedence over the file. · github.com, 8 Oct 2026
- GPU support
- Built-in GPU support uses libnvidia-container, and the optional GPU requirements include NVIDIA drivers version 361.93 or later and libnvidia-container-tools version 1.0 or later. · github.com, 8 Oct 2026
- HPC use
- The project describes Enroot as suited to high-performance or virtualized environments where portability and reproducibility matter and extra isolation is not warranted. · github.com, 8 Oct 2026
- Image imports
- Enroot can import known container image formats, including Docker images, and the README reports a 3x to 5x speedup for importing large Docker images. · github.com, 8 Oct 2026
- Install platforms
- Installation instructions provide packages for Debian-based and RHEL-based distributions and source build instructions for Debian-, RHEL-, and Arch-based distributions. · github.com, 8 Oct 2026
- Integrations
- Standard hooks can provide NVIDIA GPU support and inject Mellanox host MOFED for InfiniBand HCA support into containers. · github.com, 8 Oct 2026
- Isolation
- Enroot uses Linux user and mount namespaces and provides little to no isolation while preserving filesystem separation. · github.com, 8 Oct 2026
- License
- The project is released under the Apache License 2.0. · github.com, 8 Oct 2026
- Linux requirements
- Enroot requires Linux kernel 3.10 or later and kernel support for namespaces, user namespaces, and seccomp filters. · github.com, 8 Oct 2026
- Package options
- The project offers standard and hardened package flavors, and says the hardened flavor is slightly more secure but has greater overhead. · github.com, 8 Oct 2026
- Purpose
- Enroot turns traditional container and OS images into unprivileged sandboxes. · github.com, 8 Oct 2026
- Security reporting
- The security policy asks reporters to disclose vulnerabilities by emailing [email protected] instead of opening an issue or pull request. · github.com, 8 Oct 2026
- Unprivileged
- Enroot is standalone, requires no daemon, and supports unprivileged multi-user use without a setuid binary. · github.com, 8 Oct 2026
- Workflow features
- The command line supports batch, bundle, create, exec, export, import, list, remove, and start operations on container sandboxes. · github.com, 8 Oct 2026
Where Enroot stands on Freedom251
- Container Engines#10 of 31