Freedom251 › Cloud Governance Software
Cloud Custodian
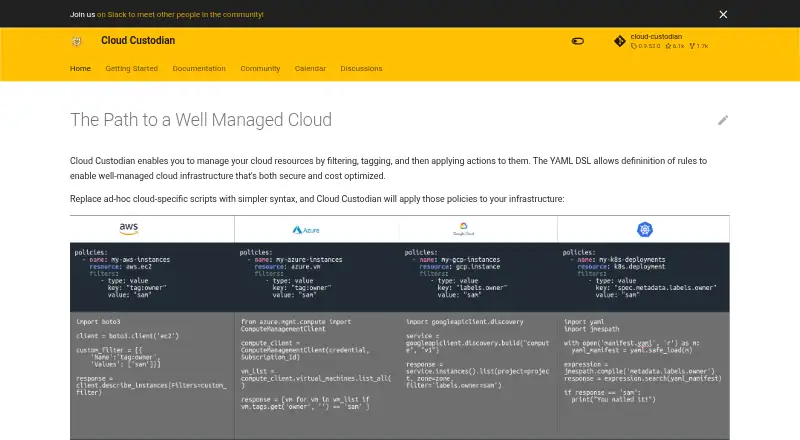
What Cloud Custodian is
Cloud Custodian manages cloud resources through policies written in YAML. Each policy names a resource type, narrows the target with filters, and specifies actions for matching resources. Teams can use it to enforce security and compliance rules, apply tags, clean up unused resources, and manage costs across AWS, Azure, and Google Cloud Platform. Policies can run in response to provider events through serverless features or on a cron schedule; users can validate policies and preview matches in dry-run mode before actions execute. A run can produce policy metrics, structured resource records, and logs for cloud metrics, storage, and logging services. Documented event integrations include AWS CloudWatch Events and Config Rules, Azure EventGrid, and GCP AuditLog and Pub/Sub. The project documents Linux, macOS, and Windows installation, plus Docker and Kubernetes operation. Kubernetes, Tencent Cloud, and OpenStack support is in beta, while Terraform integration is in alpha. The software is free and open source under the Apache 2.0 license.
Who it suits
It suits teams that want policy-based controls for cloud security, compliance, tagging, resource cleanup, or cost management. It is relevant to users working with AWS, Azure, or Google Cloud Platform resources.
What it does well
- Free and open source under Apache 2.0.
- Dry-run previews show matching resources before actions.
- Supports security, compliance, tagging, cleanup, and cost policies.
- Policies can run on events or cron schedules.
What to know first
- Kubernetes, Tencent Cloud, and OpenStack support is beta.
- Terraform integration is in alpha.
- AWS event-triggered policies are limited to the same region and account.
Limits
Kubernetes, Tencent Cloud, and OpenStack support are in beta, and Terraform integration is in alpha. For AWS, event-triggered policies can run only in the same region and account; periodic policies may run in another region and account.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Cloud Custodian | Free for everyone to use · Open source · Apache 2.0 license | Free |
As cloudcustodian.io lists them, read 29 Sept 2026. The maker's own page has the final word.
Getting started
- Visit https://cloudcustodian.io/.
- Choose an installation route for Linux, macOS, or Windows, or use Docker or Kubernetes.
- Write a policy in YAML with a resource type, filters, and actions.
- Validate the policy and use dry-run mode to review matching resources.
- Run policies through provider event features or as a cron job on a server.
Overview
Cloud Custodian is a policy engine for filtering and acting on cloud resources, with policies written in YAML. It suits cloud teams that want to define their own security, compliance, tagging, cleanup, and cost controls. Its appeal is policy flexibility across major cloud providers; the trade-off is that teams need to write and run those policies themselves.
Each policy names a resource type, filters for matching resources, and specifies actions. That gives teams a consistent way to handle different governance tasks, but it is a better fit for people comfortable with YAML and cloud operations than for those seeking a turnkey management interface.
The community project uses the Apache 2.0 license and was accepted to CNCF on June 25, 2020.
Key features
Policy definition and preview
Validation and dry-run mode let teams inspect matching resources before actions execute. That is a useful safeguard for policies that could change or clean up resources. Policy testing, admission control, runtime enforcement, CI/CD integration, and policy reporting are also supported capabilities.
Event and scheduled enforcement
Policies can run in response to cloud-provider events through serverless integrations, or periodically as a cron job on a server. Documented examples include AWS CloudWatch Events and Config Rules, Azure EventGrid, and GCP AuditLog and Pub/Sub. The AWS constraint matters for teams planning event-driven deployments: those policies can run only in the same region and account, while periodic policies can run in a different region and account.
Metrics and records
Policy runs can produce metrics, structured resource records, and logs for cloud-provider metrics, storage, and logging services. These outputs can support operational review, though teams still need to choose and manage the services where they are sent.
Pricing
Cloud Custodian costs nothing, billed Free for everyone to use. The plan is open source under the Apache 2.0 license, and there is no free trial because the software is free. That makes it accessible for teams willing to operate their own policies; it does not remove the work of authoring and deploying them.
Platforms
Installation is documented for Linux, macOS, and Windows, with Docker and Kubernetes as additional ways to run it. The project also describes local, instance, and AWS Lambda execution. Policy support covers AWS, Azure, and Google Cloud Platform. Kubernetes, Tencent Cloud, and OpenStack support is in beta, while Terraform integration is in alpha, so teams depending on those integrations should account for their maturity.
Who it's for
Cloud Custodian is a strong fit for cloud and security teams that want policy-based controls for compliance, tags, cost, or unused-resource cleanup, and can manage YAML policies and execution environments. Its preview mode and reporting outputs help teams check policy impact and review runs. It is less suited to buyers who want a managed interface or mature support for the beta and alpha integrations.
Community support includes Slack, a mailing list, GitHub discussions, and community meetings open to users and developers of all skill levels. Security vulnerabilities can be reported to [email protected]; the project says it acknowledges reports by email.
Pros and cons
- Pros: One YAML policy model covers resource filtering and actions across AWS, Azure, and Google Cloud Platform.
- Pros: Validation and dry runs expose matching resources before actions execute, reducing avoidable policy mistakes.
- Pros: Free use under Apache 2.0 avoids a software license charge.
- Cons: Teams must define and operate policies and execution themselves, rather than relying on a turnkey service.
- Cons: Kubernetes, Tencent Cloud, and OpenStack support is beta, and Terraform integration is alpha.
- Cons: AWS event-triggered policies are restricted to the same region and account.
Alternatives
For broader comparisons, see Cloud Governance Software and Infrastructure Policy as Code Tools.
- Kyverno is another free, open-source choice for teams looking for policy enforcement across its listed API, Linux, macOS, self-hosted, and Windows platforms.
- AWS Control Tower is worth considering when a team wants AWS's governance service; it adds no Control Tower charge, though underlying AWS services are billed by usage.
- CGPulse may suit teams that prefer a freemium service with a free trial, two cloud accounts, ten scans a month, and five auto-fixes a month on its free plan.
- OmniGCloud may fit teams seeking a freemium tool with a free plan for one connector, one SaaS workspace, basic CSV export, and a basic audit trail.
- Kubewarden is another free option.
- AWS Config is a paid, usage-based alternative for teams seeking an AWS service, with monthly charges based on recorded configuration items and active rules.
- CoreStack Cloud Governance is a paid option for buyers considering individual products, bundles, or unlimited assessments with custom pricing.
- Jamcracker is a paid cloud management platform aimed at MSPs, system integrators, enterprises, and cloud teams.
Verdict
Choose Cloud Custodian if your team wants free, policy-driven controls across AWS, Azure, and Google Cloud Platform and is prepared to own the YAML policies and their execution. Its preview and reporting capabilities make it a considered choice for teams automating governance. Look elsewhere if you need a turnkey management experience or depend on integrations still in beta or alpha.
Verdict
Cloud Custodian offers policy-driven resource management across three major cloud providers, with preview and reporting options. Note the beta and alpha status of some integrations and the AWS constraint on event-triggered runs.
Questions
How much does Cloud Custodian cost?
The listed plan is free, and the project is open source under the Apache 2.0 license.
Is there a free plan or trial?
Cloud Custodian is free to use. There is no free trial.
Which cloud providers does it support?
The documentation describes policy support for AWS, Azure, and Google Cloud Platform resources. Kubernetes, Tencent Cloud, and OpenStack support are in beta.
Which platforms can I use?
Installation is documented for Linux, macOS, and Windows. The project also documents Docker and Kubernetes operation, as well as local, instance, and AWS Lambda execution.
Can I preview a policy before it acts?
Yes. Policies can be validated and run in dry-run mode to show matching resources without executing actions.
Who makes Cloud Custodian?
The site identifies it as a community project and states that it was accepted to CNCF on June 25, 2020.
Facts from Cloud Custodian's own pages
- Beta and alpha support
- The homepage says Kubernetes, Tencent Cloud, and OpenStack support is in beta, while Terraform integration is currently in alpha. · cloudcustodian.io, 29 Sept 2026
- Cloud providers
- The documentation describes policy support for AWS, Azure, and Google Cloud Platform resources. · cloudcustodian.io, 29 Sept 2026
- Community support
- The project points users to Slack, a mailing list, GitHub discussions, and community meetings that are open to users and developers of every skill level. · cloudcustodian.io, 29 Sept 2026
- Deployment options
- The project documents installation on Linux, macOS, and Windows, and running through Docker or Kubernetes; its homepage also describes local, instance, and AWS Lambda execution. · cloudcustodian.io, 29 Sept 2026
- Enforcement
- Cloud Custodian integrates with provider serverless features to enforce policies in response to events, and can also run as a cron job on a server. · cloudcustodian.io, 29 Sept 2026
- Integration examples
- Documented event integrations include AWS CloudWatch Events and Config Rules, Azure EventGrid, and GCP AuditLog and Pub/Sub. · cloudcustodian.io, 29 Sept 2026
- Maker and history
- The site identifies the project as a community project and states that it was accepted to CNCF on June 25, 2020; it does not state a headquarters or founding date. · cncf.io, 29 Sept 2026
- Metrics and records
- Runs can produce policy metrics, structured resource records, and logs for cloud provider metrics, storage, and logging services. · cloudcustodian.io, 29 Sept 2026
- Notable execution limit
- The AWS documentation says event-triggered policies can run only in the same region and account, while periodic policies may run in a different region and account. · cloudcustodian.io, 29 Sept 2026
- Policy controls
- Policies specify a resource type, filters to narrow resources, and actions to apply to matching resources. · cloudcustodian.io, 29 Sept 2026
- Policy preview
- Users can validate policies and run them in dry-run mode to see matching resources without executing actions. · cloudcustodian.io, 29 Sept 2026
- Purpose
- Cloud Custodian manages cloud resources by filtering and tagging them, then applying actions through policies written in a YAML domain specific language. · cloudcustodian.io, 29 Sept 2026
- Security and cost
- It supports security policy enforcement, compliance, tag policies, cleanup of unused resources, and cost management. · cloudcustodian.io, 29 Sept 2026
- Security reporting
- The project asks people to report security vulnerabilities to its security team at [email protected] and says it will acknowledge reports by email. · github.com, 29 Sept 2026
Where Cloud Custodian stands on Freedom251
- Cloud Governance Software#3 of 26
- Infrastructure Policy as Code Tools#4 of 25