Freedom251 › Threat Modeling Software
AWS Threat Composer
What AWS Threat Composer is
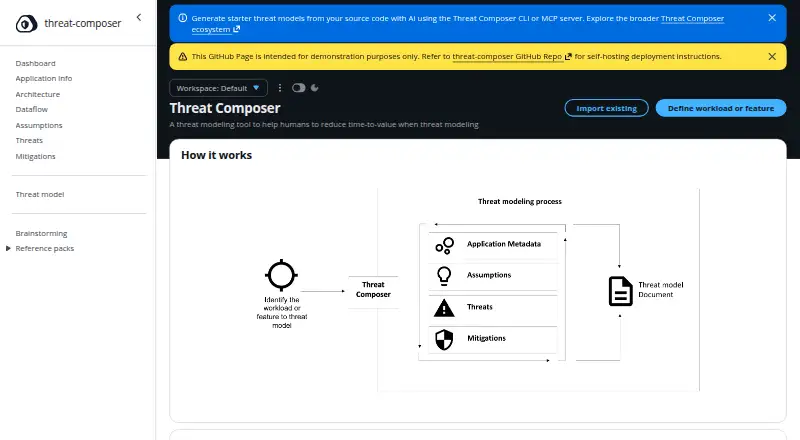
AWS Threat Composer helps teams identify security issues and plan responses through iterative threat modeling. It provides structured threat grammar and adaptive prompts for writing threat statements, alongside architecture and data-flow diagrams, assumption tracking, threat-to-mitigation links, and an insights dashboard with quality metrics and improvement suggestions. Users can manage multiple models and export them as JSON, Markdown, DOCX, or PDF. The web app stores work in the browser, supports importing and exporting, and can be used as a hosted demo or deployed as a customizable static site in an AWS account. A VS Code extension in AWS Toolkit edits .tc.json files and stores them locally, including for offline work; this supports keeping models with code in version control. The browser extension displays files from GitHub, GitLab, Bitbucket, and Amazon CodeCatalyst, including configured self-hosted URLs. An experimental AI-assisted CLI and MCP server can analyze source code for starter models, with AWS Bedrock inference costs applying.
Who it suits
It suits people modeling system threats who want diagrams, assumptions, mitigations, and model exports in one workflow. Teams keeping threat models alongside code may find the VS Code integration relevant.
What it does well
- Adaptive suggestions help compose threat statements.
- Includes architecture and data-flow diagrams.
- Tracks assumptions and links threats to mitigations.
- Exports models in four formats.
- VS Code integration supports offline local-file editing.
What to know first
- AI CLI and MCP server are experimental.
- AI tools incur AWS Bedrock inference costs.
- Browser extension is read-only and requires internet access.
- Browser extension store publication is not yet available.
Limits
The AI-assisted CLI and MCP server are experimental, and AWS Bedrock inference costs apply. The browser extension only provides read-only viewing, requires internet access for web-hosted files, and may take time to load large models.
Getting started
- Open the hosted web application or deploy its static website to an AWS account.
- Use browser storage, or import an existing model.
- Use the VS Code extension included in AWS Toolkit to edit .tc.json files locally.
- Export a model as JSON, Markdown, DOCX, or PDF when needed.
- For AI-assisted starter models, use the CLI or MCP server and account for AWS Bedrock inference costs.
Overview
AWS Threat Composer is a threat-modeling tool for teams and individuals who want to document security risks alongside system design or code. Its strongest fit is a workflow that benefits from structured threat statements, linked diagrams and mitigations, and portable model files. The free offering is broad, but the experimental AI tools carry Bedrock costs and should not be mistaken for a settled part of the workflow.
Models combine architecture and data-flow diagrams with tracked assumptions, threats, and mitigations. An insights dashboard adds quality metrics and suggestions, making the tool useful not only for recording risks but also for reviewing model quality. Multiple models and four export formats give users room to manage separate projects and move their work between tools.
The web app stores work in the browser and supports import and export; it can be used as a hosted demo or deployed as a customizable static site in an AWS account. That choice lets users decide between a hosted experience and self-hosting, while browser storage makes the web workflow distinct from the VS Code extension’s local-file approach.
For more options in this category, see our Threat Modeling Software list.
Key features
Structured threat writing and model review
A structured grammar and adaptive suggestions help users compose consistent threat statements during iterative modeling. This is a practical advantage for teams that want a repeatable way to express risks rather than a blank-page exercise. The insights dashboard’s quality metrics and improvement suggestions provide another review aid, though they do not replace security judgment.
Diagrams, assumptions, and mitigation links
Architecture and data-flow diagrams give a model a visual account of the system, while assumption tracking and links between assumptions, threats, and mitigations help keep the reasoning connected. Users can manage multiple models, which suits work spanning more than one system or project.
File formats and integrations
JSON, Markdown, DOCX, and PDF exports make models usable in both structured and document-oriented workflows. The VS Code extension, included in AWS Toolkit, edits .tc.json files, works offline, and stores data in local files. That is the better fit for people who want threat models alongside code in version control.
The browser extension is for viewing, not editing, threat model files on GitHub, GitLab, Bitbucket, and Amazon CodeCatalyst. It requires internet access to load web-hosted files, may take time with large models, and its documentation says publication through Chrome Web Store and Firefox Add-ons is not yet available. Its privacy posture is comparatively clear: it does not collect or transmit data, use analytics or tracking, or make external API calls.
AI-assisted modeling
The experimental CLI and MCP server analyze source code to generate starter threat models. They may help users get an initial model underway, but experimental status makes them a weaker choice for a dependable core process. AWS Bedrock inference costs also apply, so the free pricing model does not make AI usage cost-free.
Pricing
AWS Threat Composer is free, with a free plan. The web app, VS Code extension, browser extension, and self-hosting option make that a substantial starting point without a paid tier to weigh against it. The main cost qualification is the AI-assisted CLI and MCP server, which incur AWS Bedrock inference costs; users can avoid those costs by not using the AI tools.
Support and feedback go through GitHub Issues and GitHub Discussions. Security vulnerabilities should be reported through AWS’s Vulnerability Disclosure Program or [email protected].
Platforms
AWS Threat Composer is available as a web app and can be self-hosted in an AWS account. It also supports Linux, macOS, and Windows, with API and extension integrations. The VS Code extension supports offline, local-file work, whereas the browser extension needs internet access to show web-hosted files.
Who it's for
Threat modeling practitioners, developers, and security teams are the natural audience, particularly those who want to keep models close to code or review them through source-control platforms. The structured writing, diagrams, risk prioritization, and collaborative-review support suit iterative team work. It is less suitable for anyone who needs a fully mature AI workflow or an editable browser-extension experience.
Pros and cons
Pros
- Structured threat statements: Adaptive grammar helps give risk descriptions a consistent form.
- Connected models: Diagrams, assumptions, threats, and mitigations can be tied together, with dashboard feedback for model improvement.
- Portable outputs: Four export formats support both structured reuse and document sharing.
- Flexible working modes: Users can choose browser storage, local VS Code files, or a customizable self-hosted web deployment.
- Clear browser-extension privacy limits: The extension makes no external API calls and does not track or transmit data.
Cons
- AI is experimental and metered by AWS usage: Bedrock inference costs apply, so the AI tools add both maturity and cost considerations.
- Browser extension is view-only: Editing must happen elsewhere, and loading hosted files requires internet access.
- Browser-extension distribution is not yet through the major stores: Chrome Web Store and Firefox Add-ons publication is not yet available.
Alternatives
CAIRIS is another free option for teams seeking a tool available on web, Linux, macOS, Windows, and self-hosted environments. OWASP Threat Dragon is also free, runs on web and desktop platforms, and has no paid plans or usage limits stated.
IriusRisk is worth considering for a freemium workflow with a Community Edition capped at three active threat models and one user with limited collaboration; its stated features include templates, libraries, and XML diagram export. ThreatForge is a free option available on web, Windows, macOS, and Linux.
ThreatModeler Nexus offers a free Community Edition aimed at practitioners, students, developers, architects, and security teams exploring threat modeling before scaling. ThreatOpus may suit teams looking for a paid monthly Starter plan with 15 users, 10 team workspaces, 50 threat-modeling generations per month, and 10 repositories; it costs £129.99 a month.
ThreatTree gives free users up to three forests, three DFDs per forest, and five attack trees per DFD, while its Pro plan costs $29 a month per user. Microsoft Threat Modeling Tool is a free option for Windows users.
Verdict
Choose AWS Threat Composer if you want a free, structured threat-modeling workflow that connects written risks to diagrams, assumptions, mitigations, and code-adjacent files. Its export range and offline VS Code integration are persuasive strengths for teams that want models to remain portable and close to development work. Look elsewhere if you need an established AI workflow, editable browser-based viewing, or a browser extension distributed through Chrome Web Store or Firefox Add-ons.
Verdict
AWS Threat Composer combines structured threat writing, visual modeling, and multiple export options. Consider the experimental status and Bedrock costs before relying on its AI tools.
Questions
How much does AWS Threat Composer cost?
The project is free. AWS Bedrock inference costs apply when using its AI-assisted CLI or MCP server.
Where can I use it?
The listed platforms are API, extension, Linux, macOS, self-hosted, web, and Windows. The web application can be used as a hosted demo or deployed as a static website in an AWS account.
Can I use it offline?
The VS Code extension included in AWS Toolkit works offline and stores data in local files. The browser extension requires internet access to load web-hosted files.
What file formats can models use?
Threat models can be exported as JSON, Markdown, DOCX, or PDF. The VS Code extension edits .tc.json files.
Does it include AI features?
Its AI-assisted CLI and MCP server analyze source code to generate starter threat models. Those tools are experimental and AWS Bedrock inference costs apply.
How does the browser extension work?
It can display threat-model files from GitHub, GitLab, Bitbucket, and Amazon CodeCatalyst, including configured self-hosted URLs. It is read-only, and publication through the Chrome Web Store and Firefox Add-ons is not yet available.
Facts from AWS Threat Composer's own pages
- AI cost
- The project page says AWS Bedrock inference costs apply to the AI-powered CLI and MCP server. · github.com, 2 Oct 2026
- AI tools
- The AI-assisted CLI analyzes codebases to generate starter threat models, and the MCP server supports workflow management and schema validation for AI assistants. · github.com, 3 Oct 2026
- AI usage costs
- The AI CLI and MCP server use AWS Bedrock, and Bedrock inference costs apply. · github.com, 3 Oct 2026
- Audience and workflow
- The project is designed for people threat modeling systems, and its VS Code integration supports keeping threat models alongside code in version control. · github.com, 2 Oct 2026
- Browser extension integrations
- The browser extension supports GitHub, GitLab, Bitbucket, and Amazon CodeCatalyst, including configurable URL patterns for self-hosted instances. · github.com, 2 Oct 2026
- Browser extension limitation
- The browser extension provides read-only viewing, requires internet access to load web-hosted files, and may take time to load large models. · github.com, 3 Oct 2026
- Browser extension limits
- The browser extension is read-only, requires internet access to load web files, and its documentation says Chrome Web Store and Firefox Add-ons publication is not yet available. · github.com, 2 Oct 2026
- Browser extension privacy
- The browser extension documentation says it does not collect or transmit data, uses no analytics or tracking, and handles viewing locally in the browser. · github.com, 3 Oct 2026
- Browser integrations
- The browser extension supports viewing threat model files on GitHub, GitLab, Bitbucket, and Amazon CodeCatalyst; its documentation says Chrome Web Store and Firefox Add-ons publication is not yet available. · github.com, 3 Oct 2026
- Diagrams and insights
- Features include architecture and data flow diagrams, plus an insights dashboard with quality metrics and improvement suggestions. · github.com, 3 Oct 2026
- Exports
- Threat models can be exported in JSON, Markdown, DOCX, and PDF formats. · github.com, 2 Oct 2026
- Modeling features
- It supports architecture and data flow diagrams, assumptions tracking, threat and mitigation links, and an insights dashboard. · github.com, 2 Oct 2026
- Model management
- Users can track assumptions, link them to threats and mitigations, manage multiple models, and export models as JSON, Markdown, DOCX, or PDF. · github.com, 3 Oct 2026
- Purpose
- Threat Composer is a threat modeling ecosystem for identifying security issues and developing strategies to address them in the context of a system. · github.com, 3 Oct 2026
- Self-hosting
- The web application can be deployed to an AWS account with customization. · github.com, 2 Oct 2026
- Support
- The project directs users to GitHub Issues and GitHub Discussions for bug reports, feature requests, and questions. · github.com, 2 Oct 2026
- Support and security reports
- The project directs users to GitHub Issues and Discussions for feedback and support, and asks that security vulnerabilities be reported through AWS's Vulnerability Disclosure Program or [email protected]. · github.com, 3 Oct 2026
- Threat statements
- It uses structured threat grammar with adaptive suggestions to help users compose threat statements. · github.com, 3 Oct 2026
- Threat writing
- It uses structured threat grammar with adaptive suggestions to help compose threat statements. · github.com, 2 Oct 2026
- VS Code
- The AWS Toolkit for Visual Studio Code includes Threat Composer support for creating, viewing, and editing .tc.json files; the extension documentation lists Windows, macOS, and Linux compatibility. · github.com, 3 Oct 2026
- Web app
- The web application is available as a hosted demo or as a static website users can self-host in their AWS account; it supports browser-based storage and import/export. · github.com, 3 Oct 2026
- Web app storage
- The web application uses browser-based storage and supports import and export. · github.com, 2 Oct 2026
Where AWS Threat Composer stands on Freedom251
- Threat Modeling Software#3 of 23