Freedom251 › API Security Software
APISec Platform
What APISec Platform is
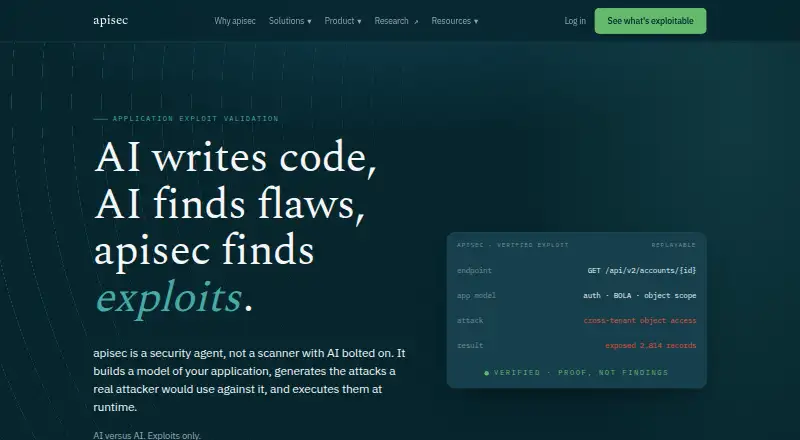
APISec Platform is an AI-based application security platform for validating exploits against APIs and applications. It discovers applications, builds a dynamic model of how they work, and runs attacker-like tests at runtime. The model can capture endpoints, parameters, authentication flows, roles, permissions, object ownership, and business logic without requiring documentation or developer interviews. Testing covers business logic, data access, roles and permissions, configuration, infrastructure, and controls such as injection and token handling. For validated exploits, APISec returns a request sequence, data reached, blast radius, replay, and a suggested resolution. It says it discovers APIs across infrastructure, source, gateways, ingress and authentication paths, web apps, Postman, SwaggerHub, Insomnia, and CI/CD, including agents, MCP servers, and LLM call sites. Public APIs run against APISec's public cloud; private and on-premises APIs can use a Kubernetes or Docker container, and cloud deployments can run in a customer's GCP, Azure, or AWS environment. The free plan covers public API testing and basic simulations. Standard costs $690 a month per 100 endpoints; Pro costs $2,750 a month per 100 endpoints.
Who it suits
APISec Platform suits teams seeking runtime exploit validation across APIs and applications, including tests of business logic, permissions, and authentication. The free plan is limited to public API testing and basic simulations.
What it does well
- Models application roles, permissions, and business logic
- Returns validated exploit details and a suggested resolution
- Tests business logic, access, configuration, and security controls
- Supports private and on-premises API testing deployments
- Free plan includes public API testing and basic simulations
What to know first
- Standard costs $690 a month per 100 endpoints
- Pricing is per 100 endpoints in increments
- Private and on-premises testing has custom pricing
Limits
The Free plan covers public API testing and basic test simulations. Standard and Pro pricing is per 100 endpoints in increments; private and on-premises API testing uses custom pricing.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | $0 forever · Public API testing · Basic test simulations · Community support · Dashboard access | Free |
| Pro | $2,750/mo · per 100 endpoints or $33,075/yr · Standard features · CI/CD and ticketing integrations · Custom attack simulations · Advanced reporting and SLAs · White-glove onboarding · Premium support | $2,750 a month |
| Standard | $690/mo · per 100 endpoints or $8,275/yr · Continuous automated validation · Business-logic attacks · Continuous API testing · Team collaboration · Dedicated support | $690 a month |
| Bug Bounty | Custom pricing · Certified expert reports · Manual and ad-hoc deep dives · Private and public API testing · Authentication support | On request |
As apisec.ai lists them, read 15 Oct 2026. The maker's own page has the final word.
Getting started
- Open the APISec website
- Choose the Free plan for public API testing or review Standard and Pro pricing
- Use public API testing through APISec’s public cloud
- For private or on-premises APIs, use an APISec Kubernetes or Docker container
- For cloud deployment, run it in your GCP, Azure, or AWS environment
Overview
APISec Platform is a runtime application-security service that maps API behavior and runs attacker-like tests against it. It is best suited to teams that need to validate complex access rules and investigate what a successful exploit could reach. For teams seeking that evidence, its broad discovery and replayable findings are compelling; endpoint-based pricing and deployment choices need careful consideration.
Key features
Rather than depending on documentation or developer interviews, APISec dynamically captures endpoints, parameters, authentication flows, roles, permissions, object ownership, and business logic. That can help teams work with APIs whose behavior is not fully documented. It is a broader approach than schema checks alone, so it may be more than a team needs if its priority is limited to validating API specifications.
Testing spans business logic, data access, roles and permissions, configuration, infrastructure, and controls such as injection and token handling. A validated exploit comes with its request sequence, the data it reached, its blast radius, replay, and a suggested resolution. That evidence can help security and engineering teams reproduce a finding and judge its impact, rather than relying on an alert without a clear attack path.
APISec can discover APIs across infrastructure, source, gateways, ingress and authentication paths, web apps, Postman, SwaggerHub, Insomnia, and CI/CD. Its discovery also covers agents, MCP servers, and LLM call sites; supported API formats include OpenAPI Specification, Swagger, Postman, and RAML. Nearly every aspect of the platform is exposed through an API for custom automations and integrations, a useful fit for teams that want to connect testing to existing workflows.
Public APIs run against APISec’s public cloud. Private and on-premises APIs can use an APISec Kubernetes or Docker container, while cloud deployments can run in the customer’s GCP, Azure, or AWS environment. Hosted agents can also validate private APIs. The deployment range is a strength for teams with different hosting needs, but private and on-premises testing carries custom pricing.
The free, open-source APISec Surface discovery tool runs locally and states that nothing leaves the machine. Surface includes local discovery tools, GitHub Actions, and a browser extension; AI Surface and MCP audit use MIT licenses, and the Bolt Browser Extension uses Apache 2.0. These tools offer a distinct, locally run discovery option, but do not replace the platform’s paid continuous validation plans.
Pricing
APISec uses a freemium model, with paid plans priced per 100 endpoints in increments. That makes the endpoint count central to budgeting as coverage grows. The published monthly prices are per 100 endpoints; annual equivalents are also provided for the Standard and Pro plans.
| Plan | Price | What it includes |
|---|---|---|
| Free | free; billed $0 forever | Public API testing, basic test simulations, community support, and dashboard access. No credit card is required. |
| Standard | $690 a month; billed $690/mo per 100 endpoints or $8,275/yr | Continuous automated validation and API testing, business-logic attacks including BOLA and RBAC, team collaboration, and dedicated support. |
| Pro | $2,750 a month; billed $2,750/mo per 100 endpoints or $33,075/yr | Everything in Standard, plus full CI/CD and ticketing integrations, custom attack simulations, advanced reporting and SLAs, white-glove onboarding, and premium support. |
| Bug Bounty | Custom pricing | Certified expert reports, manual and ad-hoc deep dives, private and public API testing, and authentication support for periodic assurance. |
Free is a way to explore basic simulations against public APIs, not a substitute for continuous validation. Standard is the entry point for teams that want ongoing testing and business-logic coverage; its per-100-endpoint price makes it important to size the scope before choosing it. Pro suits teams that need the added integrations, custom simulations, reporting, and SLA support. Bug Bounty is aimed at periodic expert review rather than continuous testing. Private and on-premises API testing uses custom pricing, so the Standard and Pro prices do not establish those deployment costs. APISec offers a free trial, but no trial length is stated.
Platforms
APISec supports API, extension, Linux, self-hosted, and web environments. Public APIs use APISec’s cloud, while private and on-premises options include customer-environment cloud deployments and Kubernetes or Docker containers. This range accommodates teams that cannot send private API testing through a public-cloud deployment, though they should account for custom pricing.
Who it's for
APISec is a strong fit for security and engineering teams responsible for APIs with complex permissions, business logic, or private deployment requirements. Its application model and exploit evidence are especially relevant when teams need to understand the path and reach of an attack. It is less suited to buyers who only need schema-driven tests or who want to budget without accounting for endpoint-based increments.
Pros and cons
Pros
- Findings include attack evidence. Request sequence, reached data, blast radius, replay, and a suggested resolution help teams assess and reproduce validated exploits.
- Discovery spans varied sources. Coverage across infrastructure, gateways, web apps, development tools, CI/CD, agents, and LLM call sites can help teams map APIs across different parts of their environment.
- Multiple deployment paths. Public cloud, customer-cloud, Kubernetes, and Docker options give teams choices for public, private, and on-premises API testing.
- A local discovery tool is available. APISec Surface runs in the user’s environment and states that nothing leaves the machine.
Cons
- Paid pricing scales in endpoint increments. Standard and Pro are priced per 100 endpoints, so the listed entry prices are not a universal total for larger API estates.
- Private and on-premises testing requires custom pricing. Buyers cannot use the published Standard or Pro figures to determine the cost of those deployments.
- Free testing is limited to public APIs and basic simulations. Teams seeking ongoing automated validation and business-logic attacks need a paid plan.
Alternatives
Consider 42Crunch API Security Platform if you want a free plan centered on an AI coding plugin, OpenAPI audit, vulnerability scans, and automatic fixes. Pynt is worth considering if you want a free starter plan capped at 10 API endpoints, with a business plan also available.
Schemathesis is an open-source option that generates tests from OpenAPI and GraphQL schemas. VulnAPI is a free MIT-licensed option for educational and testing purposes. AquilaX API Security Scanner may suit teams prioritizing secrets scanning, PII detection, compliance auditing, unlimited scans, and CI/CD and IDE integrations on its free plan.
Beagle Security offers a free plan with one lite test per month, monthly surface scan reports, and SSL and domain expiry monitoring. ZeroThreat starts with five free scan credits valid for 15 days, followed by one scan credit per month and one target per account. Bright Security DAST is another option.
For broader directories, see API Security Testing Software and API Security Software.
Verdict
Choose APISec Platform if your team needs continuous, evidence-backed testing of APIs with complex access rules, and can plan around per-endpoint pricing and its deployment requirements. Its strongest reason to buy is the combination of broad application discovery and validated, replayable exploit evidence. Look elsewhere if you need only schema-based testing or require a predictable published price for private or on-premises coverage.
Verdict
APISec Platform combines application discovery and runtime testing with detailed evidence for validated exploits. Review the per-endpoint pricing and deployment options, especially for private or on-premises testing.
Questions
Is there a free plan?
Yes. Free costs nothing, billed $0 forever, requires no credit card, and includes public API testing, basic test simulations, and community support.
What do the paid plans cost?
Standard is $690 a month per 100 endpoints, or $8,275/yr. Pro is $2,750 a month per 100 endpoints, or $33,075/yr.
Can it test private APIs?
Yes. Private and on-premises APIs can use an APISec Kubernetes or Docker container. The pricing information gives custom pricing for private API testing.
Which deployment options are available?
Public APIs run against APISec’s public cloud. Cloud deployments can run in a customer’s GCP, Azure, or AWS environment.
Does it test authentication and authorization?
Yes. Its application model captures authentication flows, roles, permissions, and object ownership, and its testing covers roles and permissions.
Who makes APISec Platform?
The company identifies itself as APIsec, Inc. and says it was created in 2018.
Facts from APISec Platform's own pages
- API-first
- The FAQ says nearly every aspect of the product is exposed as an API for custom automations and integrations. · apisec.ai, 29 Sept 2026
- API formats
- API registration accepts OpenAPI, Swagger, Postman, and RAML documents from a URL or uploaded file. · docs.apisec.ai, 15 Oct 2026
- Application model
- Its application model captures endpoints, parameters, authentication flows, roles, permissions, object ownership, and business logic dynamically without requiring documentation or developer interviews. · apisec.ai, 29 Sept 2026
- Attack coverage
- The platform tests business logic, data access, roles and permissions, application configuration, infrastructure, and security controls such as injection and token handling. · apisec.ai, 29 Sept 2026
- Automated attack generation
- The documentation says APISec generates thousands of test cases tailored to each API architecture. · docs.apisec.ai, 15 Oct 2026
- Behavioral learning
- APISec learns roles, tokens, object ownership, and allowed or disallowed behavior to test business logic and authorization. · apisec.ai, 15 Oct 2026
- Browser extension
- APIsec BOLT passively captures browser API traffic locally, detects authentication details, generates OpenAPI specifications, and can onboard captured applications for scans. · chromewebstore.google.com, 15 Oct 2026
- Company
- APISec says it was created in 2018 and identifies the company as APIsec, Inc. · apisec.ai, 29 Sept 2026
- Company identity
- The legal entity is APIsec Inc., headquartered at One Sansome Street, Suite 3500, San Francisco, California. · apisec.ai, 15 Oct 2026
- Company profile
- LinkedIn lists APIsec as privately held, founded in 2018, headquartered in San Francisco, and employing 11–50 people. · linkedin.com, 15 Oct 2026
- Data-use terms
- The terms state that APISec will not sell, rent, or lease service data and reserve the company’s intellectual-property rights in the service. · apisec.ai, 15 Oct 2026
- Deployment
- Public APIs run against APISec’s public cloud; private and on-premises APIs can use an APISec Kubernetes or Docker container, and cloud deployments can run in the customer’s GCP, Azure, or AWS environment. · apisec.ai, 29 Sept 2026
- Developer examples
- The public examples repository provides Python and shell workflows to register applications, manage instances, trigger scans, and use personal-access-token authentication in CI/CD. · github.com, 15 Oct 2026
- Discovery
- The platform discovers APIs across source code, gateways, ingress, authentication paths, web applications, Postman, SwaggerHub, Insomnia, CI/CD, agents, MCP servers, and LLM call sites. · apisec.ai, 15 Oct 2026
- Documentation depth
- The documentation includes API registration, CLI endpoint addition, API calls, dashboards, categories, integrations, and configuration procedures with curl examples. · docs.apisec.ai, 15 Oct 2026
- Exploit proof
- The platform returns validated exploits with the request sequence, data reached, blast radius, replay, and suggested resolution. · apisec.ai, 29 Sept 2026
- Exploit validation
- Results include evidence of what was exploitable, replay information, and remediation context rather than only potential findings. · apisec.ai, 15 Oct 2026
- Founded
- 2018 · apisec.ai, 28 Sept 2026
- Funding
- Dealroom records a July 2018 $2.0 million seed investment from Canaan and describes the company as a San Francisco cloud API-security provider. · app.dealroom.co, 15 Oct 2026
- GitHub integration
- GitHub can receive vulnerability issues and can store or restore APISec playbooks through personal-access-token or SSH credentials. · docs.apisec.ai, 15 Oct 2026
- Integrations
- Configuration supports report, issue-tracker, notification, playbook-backup, and single-sign-on integrations. · docs.apisec.ai, 15 Oct 2026
- Integrations and discovery
- APISec says it discovers APIs across infrastructure, source, gateways, ingress and auth paths, web apps, Postman, SwaggerHub, Insomnia, and CI/CD, including agents, MCP servers, and LLM call sites. · apisec.ai, 29 Sept 2026
- Jira integration
- The Jira connector can create vulnerability tickets after APISec validates findings and can transition tickets when later scans confirm fixes. · docs.apisec.ai, 15 Oct 2026
- Limit: customization and complexity
- Gartner reviewers cite limited customization, clutter when many scan results appear, heavy setup for smaller teams, and remediation guidance that may lack step-by-step detail. · gartner.com, 15 Oct 2026
Where APISec Platform stands on Freedom251
- API Security Software#4 of 30
- API Security Testing Software#4 of 27