Freedom251 › AI Security Testing Tools
AIRTA Red Team
What AIRTA Red Team is
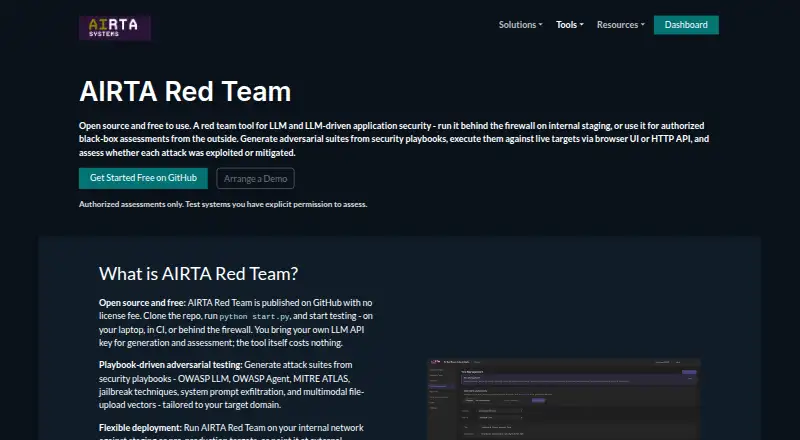
AIRTA Red Team runs authorized adversarial security assessments against LLMs and applications driven by them. It builds test suites from security playbooks, discovers target components and authentication, executes attacks, assesses outcomes, and exports reports. Listed coverage includes OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreaks, system prompt exfiltration, and custom playbooks. Strategies include zero-shot, multi-shot, few-shot, iterative, multimodal, jailbreak, and chain-of-thought testing. Targets can be reached through a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls. The tool can run locally in Docker, behind a firewall, in CI, or against external endpoints for authorized black-box testing. Run evidence includes prompts, uploads, responses, and tool calls in attack_log.json; pipeline_report.json provides category rollups and severity. Results can be exported to AIRTA Systems for review and regression tracking. The open-source tool has no license fee or subscription, but users must provide an LLM API key. Its repository says it is deprecated and no longer maintained.
Who it suits
It is aimed at red teams, whitehat testers, pentesters, and AppSec or MLsec teams assessing systems they have explicit permission to test. It focuses on observable runtime behavior rather than source-code static analysis.
What it does well
- Covers named LLM security playbooks
- Supports browser and direct HTTP API testing
- Can run locally, in CI, or behind a firewall
- Records attack evidence and report severity
What to know first
- Deprecated and no longer maintained
- Requires users' own LLM API key
- Does not perform source-code static analysis
- Testing requires explicit authorization
Limits
The free plan has no license fee or subscription, but test generation and assessment require your own LLM API key. Assessments cover observable runtime behavior rather than source-code static analysis.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| AIRTA Red Team | Open source; no license fee or subscription · Bring your own LLM API key | Free |
| Free | No license fee; bring your own LLM API key · Full pipeline, web UI, playbooks and CLI · self-hosted use | Free |
As airtasystems.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the AIRTA Red Team website.
- Choose a supported platform: API, Linux, macOS, web, or Windows.
- Run it locally in Docker, behind a firewall, in CI, or against an authorized external endpoint.
- Provide your own LLM API key for test generation and assessment.
- Select a browser runner or direct HTTP API transport and run an assessment.
AIRTA Red Team is a self-hosted tool for authorized runtime security assessments of LLMs and LLM-driven applications. It best suits red teams, pentesters, and AppSec or MLsec teams that want structured attack runs and evidence. Its unmaintained status makes it a poor choice for teams that need an actively supported tool.
Overview
AIRTA Red Team turns security playbooks into assessment suites, discovers target components and authentication, runs attacks, evaluates outcomes, and exports reports. Its runtime focus is useful for examining what an application exposes during interaction, but it does not perform source-code static analysis. The product calls for explicit permission before testing any system.
Deployment options include local Docker, environments behind a firewall, CI, and authorized black-box assessments of external endpoints. You can test through a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls. This range supports both browser-based applications and API targets, though users must bring their own LLM API key for test generation and assessment.
Key features
Playbooks and attack strategies
Coverage includes OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreak, system-prompt exfiltration, and custom playbooks. Strategies range from zero-shot and few-shot to multi-shot, iterative, multimodal, jailbreak, and chain-of-thought testing. That breadth helps teams assemble varied runtime checks, including prompt injection, jailbreak, data leakage, and custom cases; it does not replace static code review.
Evidence and workflow
Each run captures prompts, uploads, responses, and tool calls in attack_log.json. A separate pipeline_report.json summarizes categories and severity, giving reviewers a record of what the target received and returned. Results can also be exported through AIRTA Systems’ bulk import API for review and regression tracking.
The repository describes the project as deprecated and no longer maintained, and points users to Genbounty LLM Hunter instead. That is a substantial drawback for teams choosing a tool to anchor ongoing security work: its documented workflow may fit, but there is no active maintenance to rely on.
Pricing
AIRTA Red Team costs nothing. The open-source plan has no license fee or subscription, with no seat or quota cap stated in the plan. It does require users to provide their own LLM API key, so the software is free but test-generation and assessment access depends on that key.
There are no paid tiers to trade off against the free plan. This suits teams comfortable operating self-hosted open-source software and supplying their own API credentials; teams needing maintained support should look elsewhere.
Platforms
AIRTA Red Team supports API, Linux, macOS, web, and Windows, with self-hosted deployment. Docker and CI are among the described ways to run it, allowing teams to place assessments within their own environment or direct them at authorized external endpoints.
Who it's for
Red teams, whitehat testers, pentesters, and AppSec or MLsec teams are the clearest fit, particularly when they need runtime checks against LLM applications and evidence of prompts, uploads, responses, and tool calls. It is less suitable for teams seeking source-code analysis, an actively maintained project, or a workflow that does not depend on a user-supplied LLM API key.
Pros and cons
- Pro: Multiple playbooks and attack strategies give teams a broad basis for authorized runtime assessments.
- Pro: Browser and direct HTTP testing, including file uploads and tool calls, cover varied target interactions.
- Pro: Captured run logs and severity rollups provide concrete evidence for review and regression tracking.
- Pro: The open-source plan carries no license fee or subscription.
- Con: The project is deprecated and no longer maintained, making it a risky foundation for continuing security programs.
- Con: Users must supply an LLM API key, so the free license does not remove the need for API access.
- Con: Its assessment scope is runtime behavior, not source-code static analysis.
Alternatives
AI Security Testing Tools is the broader category to explore when comparing approaches. Consider OpenSecureAI Scanner if a freemium option with a published Pro tier is preferable: Pro costs $49 a month and includes 50,000 API requests monthly, 120 requests per minute per key, hosted AI remediation and LLM Gateway completions, and priority email.
Project Moonshot is another free option for teams comparing AI security tools. Promptfoo may suit teams wanting a published free Community plan with 10k red-team probes per month, LLM evaluation features, model providers and integrations, and local or self-hosted runs. For a scan-based alternative, PromptGuard has a free tier with 20,000 scans a month, one API key, one project, and 24-hour log retention.
PyRIT is a free open-source framework for teams prepared to use a Python environment and configure AI endpoints. Augustus is a free Apache 2.0 option for Linux, macOS, and Windows, with provider credentials potentially needed for API usage. Basilisk offers free AGPL-3.0 software distributed as CLI, desktop, Docker, or source, for authorized use. AgentScan may be a better fit for teams seeking a freemium scan service: its free plan allows five scans per month and includes 185 attack vectors, five categories, agent-format detection, and JSON results.
Verdict
AIRTA Red Team is a reasonable fit for security teams that need a no-license-fee, self-hosted way to run authorized LLM runtime assessments and retain structured evidence. Its varied attack coverage and browser/API workflows are useful strengths. Choose another tool if ongoing maintenance is a requirement: the project is deprecated, and every user must also bring an LLM API key.
Verdict
AIRTA Red Team offers broad runtime assessment workflows and report evidence without a license fee. Its deprecated, unmaintained status and required API key are important constraints.
Questions
How much does AIRTA Red Team cost?
The listed plan is free, with no license fee or subscription.
What do I need to use the free plan?
You must provide your own LLM API key for test generation and assessment.
Which platforms does it support?
The listed platforms are API, Linux, macOS, web, and Windows.
What kinds of security tests does it cover?
Listed areas include prompt injection, jailbreak, and data leakage tests, with custom test cases. Playbooks include OWASP LLM, OWASP Agent, MITRE ATLAS, system prompt exfiltration, and custom playbooks.
Is AIRTA Red Team still maintained?
The GitHub repository says it is deprecated and no longer maintained, and directs users to Genbounty LLM Hunter.
Who makes AIRTA Red Team?
It is presented on the AIRTA Systems website, and assessment results can be exported to AIRTA Systems through its bulk import API.
Facts from AIRTA Red Team's own pages
- Assessment models
- Playbook-specific expert models and a judge model classify attacks as exploited or mitigated and assign severity by category. · airtasystems.com, 15 Oct 2026
- Assessment scope
- The product page says assessments focus on observable runtime behavior rather than source-code static analysis. · airtasystems.com, 4 Oct 2026
- Attack coverage
- Listed playbooks include OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreak, system prompt exfiltration, and custom playbooks. · airtasystems.com, 4 Oct 2026
- Attack strategies
- The documented strategies include zero-shot, few-shot, multi-shot, jailbreak, multimodal, iterative and chain-of-thought testing. · airtasystems.com, 15 Oct 2026
- Authorization
- The product page says to test only systems for which the user has explicit permission. · airtasystems.com, 4 Oct 2026
- Authorized use
- The maker restricts use to systems for which the tester has explicit permission. · airtasystems.com, 15 Oct 2026
- Capterra pricing listing
- Capterra lists AIRTA Systems pricing as contact-vendor, with no free trial and no free version included in that listing. · capterra.com, 15 Oct 2026
- Company founders
- The about page says AIRTA Systems was founded in London by Cindy Ogidi and Bob Morel. · airtasystems.com, 15 Oct 2026
- Company founding year
- LinkedIn lists the company as founded in 2026. · linkedin.com, 15 Oct 2026
- Company legal name
- The product site footer identifies the maker as AIRTA Systems Ltd. · airtasystems.com, 15 Oct 2026
- Company size
- LinkedIn lists AIRTA Systems as having 11–50 employees. · linkedin.com, 15 Oct 2026
- Company type
- LinkedIn classifies AIRTA Systems as a public company in the technology, information and internet industry. · linkedin.com, 15 Oct 2026
- Deployment
- The maker documents local Docker deployment with python start.py, CLI operation with main.py, CI use, behind-firewall staging and authorized external black-box testing. · airtasystems.com, 15 Oct 2026
- Documentation
- The maker provides a support documentation page with article search and category filters, but the page currently shows a loading posts area rather than a visible Red Team manual. · airtasystems.com, 15 Oct 2026
- Editable suites
- Attack suites are JSON files containing playbooks, categories, prompts and optional multimodal payloads that can be edited in the web interface. · airtasystems.com, 15 Oct 2026
- Evidence
- Runs capture prompts, uploads, responses, and tool calls in attack_log.json and produce pipeline_report.json with category rollups and severity. · airtasystems.com, 4 Oct 2026
- Evidence files
- Runs capture prompts, uploads, responses and tool calls in attack_log.json and summarize results in pipeline_report.json. · airtasystems.com, 15 Oct 2026
- Execution
- Targets can be tested through a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls. · airtasystems.com, 4 Oct 2026
- Execution transports
- Targets can be exercised through a Playwright browser runner or direct HTTP transports named api_document and api_multipart. · airtasystems.com, 15 Oct 2026
- GetApp listing
- GetApp shows no user reviews and places AIRTA Systems in the Other Artificial Intelligence software category. · getapp.com, 15 Oct 2026
- Independent-review availability
- G2, Capterra, GetApp and Software Advice pages opened for AIRTA Systems each show zero or no user reviews, so there is no repeated reviewer praise or complaint pattern to report. · softwareadvice.com, 15 Oct 2026
- Integration
- The documented integration sends pipeline_report.json to AIRTA Systems through a bulk import API for review, regression tracking and compliance workflows. · airtasystems.com, 15 Oct 2026
- Integrations
- The tool can export assessment results to AIRTA Systems through its bulk import API for review and regression tracking. · airtasystems.com, 4 Oct 2026
- Intended users
- The product page identifies red teams, whitehat testers and pentesters, and AppSec and MLsec teams as intended users. · airtasystems.com, 4 Oct 2026
Where AIRTA Red Team stands on Freedom251
- AI Security Testing Tools#1 of 29