Recommended Free Tools
Mobile device management (MDM) needs a threat model of its own because it is a privileged control plane: it can enroll devices, distribute configuration and apps, collect device information, and trigger actions across a fleet. A threat model that covers only phones and tablets misses the people, services, trust relationships, and data flows that control them. MDM can enforce policy, but it is not a security technology by itself and does not eliminate risks from compromised identities, apps, networks, or devices.
What makes the MDM management plane a separate security concern?
NIST’s Mobile Threat Catalogue describes enterprise mobility management (EMM) systems as tools organizations commonly use to manage devices, deploy policies, and monitor device state. It also cautions that EMM is not itself a security technology. In practice, MDM is often one capability within an EMM service, but the distinction matters: policy enforcement is a control, not proof that the device or the wider environment is safe.
The service that manages devices has its own attack surface. An attacker who compromises an administrator account, misuses an enrollment path, or exploits a tenant boundary may be able to affect more than one endpoint. The actual reach depends on the platform, ownership and enrollment mode, policy, and service configuration; an MDM compromise does not automatically mean total control of every device.
NIST SP 800-124 Rev. 2, published in May 2023, states: “EMM technology can enforce enterprise security policies on a mobile device, which can configure or restrict the use of mobile functionality and security capabilities.” That authority is why the management plane should be modeled explicitly, alongside the endpoints it governs.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
What belongs inside the threat-model scope?
Start with the complete system that establishes trust and manages work on mobile devices, not just the server or a device-management agent. Include its human operators and the services connected to it.
- Management service and administration: cloud or on-premises components, administrator identities, roles, console access, and any provider components on which the service depends.
- Tenant and organizational boundaries: separation between customers, business units, environments, and delegated administrators.
- Enrollment and trust: user and device identity checks, enrollment invitations or tokens, certificates, certificate issuance and validation, and configuration profiles.
- Policy and software delivery: device configuration, application distribution, updates, and the path by which devices receive and apply changes.
- Devices, users, and data: managed endpoints, their owners, enterprise information, personal information on personally owned devices, and telemetry collected about device state.
- Connections and actions: device check-ins, synchronization, identity and enterprise-service integrations, network paths, and remote lock or wipe commands.
Mark trust boundaries on a diagram: administrator to console, organization to provider, tenant to tenant, enrollment service to device, certificate authority to device, and managed device to enterprise services. For each boundary, show what crosses it, who can initiate the exchange, and what happens if the information or identity is forged, exposed, changed, or delayed.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
Which MDM-specific threats should you consider?
NIST’s EMM threat category lists the examples below. Treat them as prompts for local analysis, not as an exhaustive checklist: NIST describes the Mobile Threat Catalogue as a living document and notes that threats may be missing. The catalogue identifies threat types; it does not establish their likelihood for a particular organization.
| Threat | What could go wrong | Question for the model |
|---|---|---|
| Unauthorized access to the administrator console | An attacker with console access may change policy, access management data, or issue commands within the authority of the compromised account. | Which roles can perform high-impact actions, and how are those identities protected and monitored? |
| Administrator misuse or privacy breach | An authorized operator may view information beyond their job need or misuse management capabilities against users. | What can each role see and do, and what evidence is retained for sensitive access and actions? |
| Improper tenant segmentation | A boundary failure could expose another tenant’s information or allow actions to cross organizational boundaries. | How are tenant isolation and delegated administration enforced and validated? |
| MDM impersonation | A device or user may trust a false management service or actor posing as one. | How does a device verify the identity of the management service it communicates with? |
| Improper certificate validation | A device may accept an untrusted certificate or fail to detect a certificate substitution in a management or enrollment flow. | Where are certificates issued, validated, renewed, and revoked, and what happens on validation failure? |
| Unauthorized enrollment | An unapproved device may become managed, or a device may be enrolled into an attacker-controlled service. | What identity and device checks must succeed before enrollment, and how can enrollment be revoked? |
| Improper data handling or unauthorized synchronization | Device or enterprise data may be collected, retained, or synchronized to an unintended destination or beyond its intended purpose. | Which data flows exist, who receives the data, and what retention and access limits apply? |
| Bypass of root or jailbreak checks | A device that fails an integrity check may still receive access or policy intended for devices meeting that check. | What decisions depend on the check, and what is the defined response when the check is absent, bypassed, or inconclusive? |
| Deletion of personal data | A remote action or mistaken policy may erase personal content as well as work data, depending on the device and management mode. | Which wipe actions are available in each enrollment mode, and have their effects been made clear to users and operators? |
The catalogue also describes mechanisms such as malicious apps abusing device-management features to block functions, and malicious configuration profiles carrying unwanted certificates or VPN settings or enrolling a device in a malicious management system. These examples illustrate why configuration and enrollment paths matter; they are not evidence that a particular historical scenario is a prevalent current exploit.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
How should you build and maintain the threat model?
- Set the business and lifecycle context. Record the information handled on mobile devices, enterprise services they can reach, user groups, device ownership, and whether a device is being deployed, used, transferred, or disposed of. NIST SP 800-124 Rev. 2 addresses organization-provided and personally owned devices across deployment, use, and disposal.
- Draw the system and its data flows. Map administrator sign-in, tenant boundaries, enrollment, certificate issuance and validation, policy and app delivery, device check-ins, telemetry, synchronization, remote lock or wipe, and connections to identity and enterprise services. Label trust boundaries and identify the party responsible for each component.
- Name actors and failure modes. Include external attackers, compromised or malicious users, insider administrators, compromised provider components, configuration mistakes, and policies that are mistaken or too broad. State assumptions about access and capability explicitly rather than treating every actor as all-powerful.
- Rate consequences in your own environment. Consider privilege, how many devices an action could reach, data sensitivity, recovery options, employee privacy, and disruption to business services. NIST’s catalogue supplies threat categories, not universal likelihood scores; do not substitute an unsupported generic rating for local evidence.
- Choose controls and verify them. Protect administrator credentials and console access, use multifactor authentication where supported, restrict roles, verify tenant separation, validate certificates and enrollment, limit collection and access to data, clarify wipe behavior for each ownership mode, monitor policy and management actions, and test changes before broad rollout. Consider mobile threat defense (MTD) where the organization’s risks justify it, and validate how any MTD alerts or remediation actions integrate with EMM.
- Revisit the model when the system changes. Reassess after changes to platform versions, enrollment modes, vendors, policies, identity integrations, or data flows, and through the device lifecycle. A change to one trust relationship can alter the impact of an existing threat.
How do ownership and enrollment choices change the trade-offs?
Ownership is not a cosmetic label: it affects the scope of management, what employees reasonably expect to remain private, and what a wipe or policy action can do. Android Enterprise documents work-profile and fully managed modes, while warning that available features vary by management solution and operating-system version. The table is a design comparison, not a promise that every product implements each behavior identically.
| Deployment pattern | Hardware owner | Typical management scope | Privacy and wipe questions |
|---|---|---|---|
| BYOD / personally owned | Employee | May use a work profile or management focused on work apps and data; exact scope depends on platform and enrollment. | What personal information is visible to administrators? Can work data be removed selectively, and what happens to personal data during a wipe? |
| Corporate-owned, personally enabled (COPE) | Organization | Organization controls the device, while personal use may be allowed; scope and separation depend on mode and configuration. | Which device information is collected, what personal use is permitted, and how are work and personal data handled during removal or reset? |
| Fully managed corporate device | Organization | Management can apply to the whole device under a fully managed mode, subject to platform, version, and solution capabilities. | What monitoring and controls are proportionate to the work use, and what data will a remote wipe remove? |
For each proposed mode, document hardware ownership, managed scope, administrator visibility, selective work-data removal, full remote-wipe behavior, supported operating systems and versions, and the security of certificates, enrollment, administrator access, and tenant separation. Also record how identity/access controls and any MTD capability fit into the deployment. Explain the resulting privacy and support expectations to users before enrollment.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
What MDM does not protect on its own
Even a well-configured management service cannot turn a vulnerable or compromised device into a trustworthy one. NIST’s enterprise mobile guidance also addresses loss and theft, phishing-based credential theft, malware, wireless attacks, device and operating-system vulnerabilities, and privacy implications. Those risks remain in scope for the wider mobile-security program.
Mobile threat defense can help address threats such as malicious apps, network attacks, phishing, misconfiguration, and known vulnerabilities. NIST describes MTD as something that may integrate with EMM for alerts and remediation. That relationship is complementary: MDM can apply or coordinate policy, while MTD supplies a different kind of detection and risk signal. Neither should be treated as a substitute for identity security, application controls, network protections, patching, or user-appropriate privacy limits.
Best Value
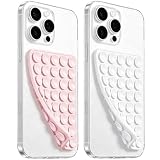
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
How to evaluate an MDM or EMM implementation
Product selection should follow the threat model, not replace it. Microsoft Intune is one example of a cloud endpoint-management service supporting MDM and MAM across mobile platforms. Android Enterprise documents a provider ecosystem. These are examples, not universal recommendations; compare each service’s current capabilities, configuration options, supported platform versions, privacy terms, and fit with your identity and incident-response processes. Vendor feature sets and platform support can change.
When evaluating a service, ask for evidence relevant to the boundaries in your model: how administrator roles and authentication work; how tenants are isolated; how enrollment and certificates are validated; what telemetry is collected and who can access it; how selective removal and full wipe differ by platform and mode; and how policy changes and remote actions are audited. Google’s Android Enterprise page stated “150+ Enterprise Mobility Management partners” when accessed on 2026-10-03. That is a Google-published ecosystem count, not an independent market measure or evidence of security effectiveness.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




