What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
NIST SP 800-53 control CM-3(2) asks organizations to test, validate, and document changes before they are finalized. Ben Link’s Season 6, Episode 4 of “How to Be Friends With Compliance” takes that enhancement as its subject and frames it around CI/CD pipelines, risk-based tiering, and documentation kept in Git. This article explains what the control’s label covers, which catalog version to cite, how the episode’s three implementation lenses fit together, and where the episode’s own claims stop.
What the episode is about
The episode description on DEV Community names the control directly: CM-3(2), which it labels “Testing, Validation, and Documenting Changes.” The page identifies the entry as Season 6, Episode 4 of a five-part series, credits Ben Link, and shows “Posted on Sep 24” without a year. It links an embedded YouTube video but does not provide a transcript, so this article relies on the written description for what the episode covers. (Ben Link’s episode page on DEV Community)
As an Amazon Associate I earn from qualifying purchases.
According to that description, the episode addresses a set of recurring objections: that compliance adds overhead, a few persistent myths, and how compliance relates to cost and security. Its practical focus is on three ideas, CI/CD pipelines, risk-based tiering, and Git-driven documentation as code. Those are the author’s framing. They are a useful way to organize the topic, but they are not NIST’s prescribed implementation.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsReading the control label correctly
The episode’s title uses the shorthand “CM(3),” while the description and this article use “CM-3(2).” The shorthand refers to the same subject, but the standard citation format is the family, control number, and enhancement in parentheses: CM for the Configuration Management family, 3 for control CM-3, and (2) for its second enhancement. Cite it as CM-3(2) in documentation, audit notes, and policy text so that it is not confused with the base control CM-3.
#1 Best Overall

- Outdoor 4 is our most affordable wireless smart security camera yet, offering up to two-year battery life for around-the-clock peace of mind. Local storage not included with Sync Module Core.
- See and speak from the Blink app — Experience 1080p HD live view, infrared night vision, and crisp two-way audio.
- Two-year battery life — Set up in minutes and get up to two years of power with the included AA Energizer lithium batteries and a Blink Sync Module Core.
- Enhanced motion detection — Be alerted to motion faster from your smartphone with dual-zone, enhanced motion detection.
- Person detection — Get alerts when a person is detected with embedded computer vision (CV) as part of an optional Blink Subscription Plan (sold separately).
Which version of SP 800-53 to cite
NIST’s publication page describes SP 800-53 Rev. 5 as a catalog of security and privacy controls for information systems and organizations. The controls are flexible and customizable, and NIST describes them as implemented through an organization-wide risk-management process rather than as a fixed checklist. The Rev. 5 publication date is listed as September 2020, with updates as of December 10, 2020. (NIST’s SP 800-53 Rev. 5 publication page)
The same page records release 5.2.0, issued August 27, 2025. That release adds specified new controls, revises SI-07(12), and updates selected control discussions and related controls. The page does not list CM-3(2) among the changes, so you should not describe CM-3(2) as altered in 5.2.0 unless you have checked the release materials yourself. When you cite the control, name the revision and, if you rely on the current text, the release you checked.
NIST also provides the publication’s DOI and supplemental materials, including OSCAL versions of the Rev. 5 controls. The NIST-linked OSCAL content repository includes a Rev. 5 directory, which is the place to look for machine-readable control data. The repository view available for this article did not display the CM-3(2) text itself, so confirm the wording in the NIST publication or the OSCAL files before you quote it.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Rank #2

- Our second-generation Video Doorbell and fourth-generation Outdoor 4 cameras offer up to two years of battery life and improved security features for more peace of mind, no matter where you are.
- Last longer with two-year battery life — Experience up to two years of smart security coverage on both devices with included AA Energizer lithium batteries and a Blink Sync Module (included with Outdoor 4).
- See and speak from the Blink app — Experience head-to-toe HD viewing from Video Doorbell and 1080p HD live view from Outdoor 4 as well as infrared night vision and crisp two-way audio.
- See more at your door with Blink Video Doorbell — Greet guests and watch packages get delivered, day and night, with head-to-toe HD view and infrared night vision. Use two-way talk to hear and speak through the Blink app.
- Enhanced motion detection with Outdoor 4 — With Outdoor 4, enjoy a wider field of view and be alerted to motion faster with dual-zone, enhanced motion detection.
(NIST-linked OSCAL content repository, SP800-53 Rev. 5 directory)
The three implementation lenses in the episode
The description organizes the discussion around three practical themes. Each one answers a different part of the question “how do we test and document this change?”
CI/CD pipelines as the place testing happens
A continuous integration and delivery pipeline is a sequence of automated stages that build, test, and deploy a change. Treating the pipeline as the testing point means test results are produced by the same process that moves the change forward, rather than in a separate review after the fact. The episode names CI/CD as an implementation theme. It does not, in the written description, say that any particular pipeline configuration satisfies CM-3(2).
Rank #3

- Outdoor 4 is our fourth-generation wireless smart security camera with up to two-year battery life for around-the-clock peace of mind.
- See and speak from the Blink app — Experience 1080p HD live view, infrared night vision, and crisp two-way audio.
- Two-year battery life — Set up in minutes and get up to two years of power with the included AA Energizer lithium batteries and a Blink Sync Module (sold separately).
- Enhanced motion detection — Be alerted to motion faster from your smartphone with dual-zone, enhanced motion detection.
- Person detection — Get alerts when a person is detected with embedded computer vision (CV) as part of an optional Blink Subscription Plan (sold separately).
Risk-based tiering to decide how much testing is enough
Risk-based tiering means classifying changes by impact and applying proportionate testing and approval to each tier. A routine configuration tweak and a change to an authentication service rarely need the same evidence. The description lists risk-based tiering as a theme, which fits the way SP 800-53 frames controls as tailored to an organization’s risk. The tiers themselves, and the testing each tier requires, are decisions your organization must document. The episode description does not define them.
Free tools Windows power users keep installed
One-click scans. No signup required.
Documentation as code kept in Git
Documentation as code means change records, test expectations, and configuration descriptions live in version-controlled files alongside the system they describe. The benefit is that the record of a change and the change itself share a history, so a reviewer can see what was tested and when it was altered. The description presents Git-driven documentation as a theme. Whether a Git history meets a particular assessor’s evidence expectations depends on what the record contains, which the description does not address.
| Lens | What it addresses in CM-3(2) | What the episode description says | What it does not establish |
|---|---|---|---|
| CI/CD pipelines | Where testing and validation are performed and recorded | Named as an implementation theme | Any specific pipeline design, tool, or configuration as compliant |
| Risk-based tiering | How much testing and approval a change needs | Named as an implementation theme | Specific tiers, thresholds, or required test types |
| Documentation as code in Git | How change documentation stays linked to the change | Named as an implementation theme | Whether a Git history alone satisfies documentation expectations |
Building a testing and documentation trail for a change
The episode’s themes suggest one practical sequence. The steps below are an analytical outline, not a list drawn from NIST or from the episode, and they should be adapted to your own system boundary and assessment requirements.
Rank #4
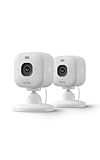
- Mini camera, max performance — Mini 2K+ is our third-generation compact plug-in camera, delivering sharper 2K video resolution and improved audio clarity, so you can see and hear more of what matters.
- See everything, miss nothing — With 2K video resolution, expansive coverage, and up to 4x zoom, you'll capture more detailed footage, even in challenging light conditions.
- Two-way talk that feels natural — Enjoy improved audio with noise cancellation for clearer conversations around your home, making it feel like you're there in person.
- Smarter protection — Receive smart detection like person and vehicle detection with an optional Blink Subscription Plan (sold separately).
- Plug in anywhere — Place or mount indoors, or take it outside with the Weather Resistant Power Adapter (sold separately). Installation takes just minutes.
- Classify the change by risk tier before it is proposed, and record the tier in the change request.
- Define the tests and validation checks that the tier requires, and write them down before implementation begins.
- Run those checks in the pipeline and retain the output, including the commit identifier and the environment tested.
- Record the approval decision and any deviations from the planned tests in the same versioned location as the change.
- After deployment, confirm that the documented configuration matches the deployed state, and note any difference as a finding.
Each step produces evidence an assessor can inspect. A common failure is documenting the change after deployment, which leaves a gap between what was tested and what was recorded. Keeping the record in the same repository as the change narrows that gap, though it does not close it on its own.
What the episode does not establish
- The written description does not show what the embedded video demonstrates, and the page provides no transcript.
- It does not present examples, quotations, measurements, or test results that can be verified from the page.
- It does not recommend a specific CI/CD platform, Git host, or compliance product.
- It does not establish that following its three themes will satisfy an assessment of CM-3(2) in any particular environment.
For a formal assessment, the control text in the NIST publication, your system’s documented configuration baseline, and your organization’s own risk decisions govern the outcome.
Recommended Free Tools
Verdict
CM-3(2) is a concrete requirement to test, validate, and document changes, and it is more useful as a design constraint than as a box to tick. Ben Link’s episode frames it through CI/CD, risk-based tiering, and documentation kept in Git. Those are sensible places to start, provided you cite Rev. 5 correctly, confirm the control wording against NIST’s text, and treat the episode as one practitioner’s framing rather than as an authoritative implementation guide.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

