The HTMD Blog article “New Microsoft Entra Portal Walkthrough”, published July 25, 2023, is a useful introduction to Microsoft’s post–Azure AD rebrand portal. Its screenshots are historical, however. The current administrative entry point is the Microsoft Entra admin center, and the menus you see depend on your tenant, role, licensing, cloud, feature rollout and personalization.
This updated walkthrough explains the terminology, current navigation model, major workloads and the safest way to use the portal in 2026.
What the Microsoft Entra portal is
Microsoft Entra is Microsoft’s product family for identity, access, governance and identity-aware network access. Microsoft Entra ID is the foundational cloud identity and access-management service formerly called Azure Active Directory (Azure AD). The rename changed the product brand, not the underlying tenant concept. Organizations using Microsoft 365, Azure or Dynamics Online generally already have an associated Entra tenant.
The family now includes Entra ID, Identity Governance, External ID, Verified ID, Workload ID, Domain Services, Internet Access, Private Access and newer agent-identity capabilities. Microsoft describes the family and its management options in its Entra overview.
#1 Best Overall

- Supports FIDO2 biometric authentication services and FIDO U2F services requiring security key functionality. Secure and flexible authentication across multiple platforms.
- Exceptional biometric performance, 360° readability, and advanced anti-spoofing technology.
- Designed for portability, it comes with a cover to protect the security key when not in use.
- Aligns with cybersecurity measures that comply with key privacy laws and regulations, including GDPR, BIPA, and CCPA. Approved for use in U.S. federal government institutions.
- Passkey compatibility with Microsoft, Google, and Apple for a convenient and secure sign-in experience. Certified for Microsoft Entra ID for secure multifactor integration with Microsoft services.
How to open the current admin center
- Go to https://entra.microsoft.com/.
- Sign in with an organizational account.
- If the account can access multiple directories, select the correct tenant.
- Confirm that your account has the Entra role required for the task.
- Use the portal search or the left navigation to open the workload.
The landing page, labels and visible blades can differ between administrators. A guest account, delegated administrator, national-cloud tenant, preview enrollment, missing license or limited role can all produce a different view.
Understanding the navigation
The 2023 HTMD walkthrough showed Home, Favorites, Identity, Protection, Identity Governance, Verifiable Credentials, Permissions Management and Global Secure Access. Treat that list as an orientation to the era, not a guaranteed menu. Microsoft can rename, move, hide or gradually roll out features.
Home, search and Favorites
Home provides shortcuts and recently used resources. Search is often more reliable than browsing when a blade has moved. Where the current portal exposes Favorites, pin frequently used workloads. The HTMD article also documented appearance and startup-view settings accessed from the settings icon; those options may change with portal updates.
Identity
Identity is where most directory administration begins. It commonly leads to users, groups, devices and applications, although exact grouping varies.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Users, groups and devices
Users
Under the users area, administrators may create, disable or delete accounts, edit properties, assign licenses and manage authentication methods when their role and policy permit it. All users, Deleted users and user settings were explicit sections in the HTMD walkthrough. Deleted objects have retention and restoration limits, so verify the current portal status before assuming an account can be recovered.
Groups
Groups can be used for application assignment, Conditional Access targeting, licensing and delegated administration. Depending on tenant configuration and licensing, you may see security groups, Microsoft 365 groups, dynamic membership, group settings and deleted-group recovery. Visibility of a group does not automatically grant permission to change membership or settings.
Rank #2

- POWERFUL SECURITY KEY: The Security Key C NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key C NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key C NFC via USB-C and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
Devices
Entra device objects can be registered, joined or hybrid joined. A device object is not the same thing as an Intune-managed or compliant endpoint. Intune remains the service for endpoint configuration, compliance, application deployment and device-management workflows. The HTMD article also pointed to BitLocker recovery keys; treat those keys as sensitive recovery data, restrict access and audit retrieval.
Applications: registrations versus enterprise applications
App registrations
An app registration defines an application identity, redirect URIs, permissions, credentials and other configuration used by developers or application administrators.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Enterprise applications
Enterprise applications represent service principals and application instances in your tenant. They are used for assignment, single sign-on, provisioning and access policy. The two areas are related but not interchangeable.
Application Proxy
Application Proxy publishes suitable on-premises web applications through Entra. It is not identical to Microsoft Entra Private Access, which is a separate identity-centric private-access product.
Protection and authentication
The protection area in the HTMD guide included Identity Protection, Conditional Access, authentication methods, self-service password reset, custom security attributes and risky activities.
Authentication methods
These settings govern which methods users can register and use, such as passwordless or multifactor options. Changes can affect enrollment and sign-in behavior across the tenant.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Rank #3

- Supports FIDO2 biometric authentication services and FIDO U2F services requiring security key functionality. Secure and flexible authentication across multiple platforms.
- Exceptional biometric performance, 360° readability, and advanced anti-spoofing technology.
- Designed for portability, it comes with a cover to protect the security key when not in use.
- Aligns with cybersecurity measures that comply with key privacy laws and regulations, including GDPR, BIPA, and CCPA. Approved for use in U.S. federal government institutions.
- Passkey compatibility with Microsoft, Google, and Apple for a convenient and secure sign-in experience. Certified for Microsoft Entra ID for secure multifactor integration with Microsoft services.
Conditional Access
Conditional Access evaluates signals such as user, device, application, location and risk, then applies requirements such as multifactor authentication. Use report-only mode, test groups and documented exclusions before enforcement. Maintain emergency-access accounts and exclude them deliberately; an incorrectly scoped policy can lock out administrators.
Identity Protection and risk
Identity Protection detects identity-related risk, while risk-based policies can require remediation or stronger authentication. Review sign-in and audit evidence before changing policy, and distinguish detection from an automatic block.
Password reset
Self-service password reset can let users recover access when configured. Its availability and writeback behavior depend on tenant setup, licensing and directory architecture.
Identity Governance
The governance workload is designed to control who receives access, for how long and with what approval. The HTMD walkthrough highlighted the following areas:
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitches- Entitlement Management: catalogs, access packages, approval workflows and controlled requests.
- Access Reviews: recurring validation that users still need group, application or resource access.
- Privileged Identity Management (PIM): governed, often just-in-time activation of privileged roles.
- Lifecycle Workflows: automation for joiner, mover and leaver processes.
These capabilities are not universal free-tenant features. Microsoft’s pricing and plan information shows that governance is licensed through higher-level plans and standalone offerings, and each operation also requires an appropriate administrative role.
External ID, cross-tenant access and Verified ID
Microsoft Entra External ID
External ID covers partner, guest, customer and consumer-facing identity scenarios. Depending on the scenario, administrators may configure identity providers, user flows, custom authentication extensions, cross-tenant access and external collaboration settings.
Rank #4
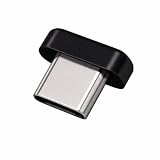
- FIDO2 + FIDO U2F certified security key, supports PIV credential authentication
- Sits with a low-profile when plugged-in
- Works in every browser without installing any drivers
- Supports desktops, laptops, tablets, and Android mobile devices via USB-C
- Helps protect your accounts from phishing and other cyber-attacks. Prevents your devices from unauthorized use.
Cross-tenant access
Cross-tenant settings define trust and collaboration controls with other Entra tenants. They do not replace application-specific authorization or resource-level permissions.
Microsoft Entra Verified ID
Verified ID issues and verifies digital credentials. It is distinct from ordinary user sign-in and should be designed around credential issuance, presentation and verification use cases.
Permissions Management and Global Secure Access
Permissions Management
Permissions Management addresses excessive permissions across cloud environments and least-privilege governance. It should not be confused with ordinary Entra directory-role administration.
Global Secure Access
Global Secure Access is associated with Microsoft Entra Internet Access and Microsoft Entra Private Access. Internet Access applies identity-centric controls to internet, SaaS, Microsoft 365, web and related traffic. Private Access provides identity-aware access to private applications and resources, potentially reducing reliance on traditional VPN designs for suitable workloads.
These capabilities can require separate licenses, client deployment, network configuration and, for some functions, preview enrollment. Application Proxy and Private Access solve different publishing and access problems.
What changed since the July 2023 HTMD walkthrough?
| Area | HTMD-era view | Current interpretation |
|---|---|---|
| Branding | Azure AD had just become Microsoft Entra ID. | Use Entra ID for the foundational service and Entra for the wider family. |
| Navigation | Screenshot-led menu tour. | Menus vary by role, tenant, license, rollout and personalization. |
| Network access | Global Secure Access appeared as preview-era functionality. | Discuss Internet Access and Private Access as distinct current products. |
| AI identities | Not covered. | Microsoft’s family now includes Entra Agent ID and related agent-security work. |
| Recovery | Not covered. | Microsoft release information includes Entra Backup and Recovery developments. |
| Licensing | Broad references. | Map each workload to role, entitlement, cloud and feature status. |
Microsoft’s release information lists features such as agent-focused Conditional Access protections, device soft-delete preview and other changes. Availability must be checked by status—Generally Available, Public Preview, Plan for Change or tenant-dependent—rather than inferred from a screenshot.
Best Value

- FIDO2 + FIDO U2F certified and supported USB security key
- Supports Computers, Laptops, Tablets, and Mobile Devices with a USB-C port and/or NFC
- Works without downloading any drivers. Supported OS: Android, Chrome OS, Windows, MacOS, Linux
- Durable design made to last for a long time with everyday use. Water-resistant (IP67)
- Helps protect your accounts from phishing and other cyber-attacks. Prevents your devices from unauthorized use.
A safe test sequence
- Confirm the tenant name and directory ID.
- Use a test user and test group.
- Register or configure a non-production application.
- Run Conditional Access in report-only mode where possible.
- Check sign-in and audit logs.
- Apply only validated changes to production users or groups.
Do not use a production tenant as the first environment for testing authentication-method changes, PIM activation, application consent or Conditional Access.
Why a menu item may be missing
- The wrong directory is selected.
- Your role lacks permission; a Global Administrator sees more than a User Administrator, Application Administrator or Security Administrator.
- The operation requires Entra ID P1/P2, Governance, Entra Suite, External ID, Workload ID or another entitlement.
- The feature is in Public Preview, unavailable in your cloud or still rolling out.
- Microsoft moved the workload to another Entra experience or service.
- You are signed in as a guest or delegated administrator.
- A stale browser session is hiding a recent change; sign out and back in.
Portal visibility, role authorization, licensing and actual feature usability are separate checks. Some tasks belong in Intune, Defender, Azure or Microsoft Graph rather than Entra. Microsoft supports both the admin center and Graph for management, but Graph does not remove authorization or licensing requirements.
Plans and capability signals
| Offering | Typical use | Commercial note |
|---|---|---|
| Entra ID Free | Basic users, groups, MFA support, reports, password change and synchronization. | Included with qualifying Microsoft cloud subscriptions; see Microsoft’s pricing page. |
| Entra ID P1/P2 | Advanced Conditional Access, identity protection and access controls. | Availability varies by standalone license and Microsoft 365 or EMS bundle. |
| Entra ID Governance | Access Reviews, entitlement, lifecycle and privileged-access governance. | US pricing page lists $7 per user/month paid yearly; verify current regional terms. |
| Internet Access | Identity-centric internet, SaaS and Microsoft 365 access. | US pricing page lists $5 per user/month paid yearly; verify current terms. |
| Private Access | Identity-centric access to private applications. | US pricing page lists $5 per user/month paid yearly; verify current terms. |
| Workload ID | Application and service identity governance. | US pricing page lists $3 per workload identity/month paid yearly. |
| External ID | Partner, customer and consumer identities. | Microsoft states core features are free for the first 50,000 monthly active users; confirm details. |
| Verified ID | Issuing and verifying digital credentials. | Included with an Entra ID subscription; premium Face Check terms differ. |
Prices above are signals from Microsoft’s US page, paid yearly, and can change by geography, agreement and date. Check the official pricing page before purchase. An Azure free account is available at https://azure.microsoft.com/en-us/free/.
When Entra is not the whole answer
Entra does not replace Intune for endpoint management, Defender for security operations, Azure for infrastructure or Graph for automation. Entra Domain Services is a separate option for legacy applications requiring managed LDAP, Kerberos or NTLM capabilities. Organizations without a substantial Microsoft investment, or those needing a narrowly focused MFA product, may compare alternatives such as Okta Workforce Identity, JumpCloud, Ping Identity, Cisco Duo and Cloudflare Zero Trust; feature and price comparisons require current vendor verification.
Recommended Free Tools
Bottom line
The HTMD walkthrough remains a valuable historical map of the Entra portal introduced in 2023, but it is not a precise current navigation reference. Start at entra.microsoft.com, select the correct tenant, search by workload, and validate role, licensing, cloud and release status before changing production settings. Use Microsoft Learn’s current labels and release notes for decisions that depend on today’s portal.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




