Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteIntel SGX and Intel TDX solve different isolation problems. SGX places selected application code and data in hardware-protected enclaves, creating a comparatively small application-level trust boundary. TDX places an entire supported virtual machine in a Trust Domain (TD) designed to remain confidential and intact even when the host virtual-machine monitor (VMM) or hypervisor is not trusted. Choose SGX when you need tightly scoped protection around a function or data set and can engineer an enclave boundary. Choose TDX when your unit of deployment is a VM and you want to protect an existing guest with fewer application changes.
Neither technology makes every component trustworthy or removes side-channel, denial-of-service, physical, firmware, or implementation risks. The practical decision depends on the exact threat model, trusted-computing base (TCB), attestation claims, processor and firmware support, guest software, cloud availability, and measured performance of your workload.
As an Amazon Associate I earn from qualifying purchases.
SGX and TDX at a glance
| Dimension | Intel SGX | Intel TDX |
|---|---|---|
| Protection scope | Selected application code and data inside enclaves | An entire guest VM operating as a Trust Domain |
| Primary trust boundary | Application-level enclave boundary designed by the developer | VM-level boundary intended to exclude non-TD host software, including the VMM |
| Typical software work | Enclave APIs, boundary design, porting, or an SGX-enabled LibOS | TDX-capable host, firmware, VMM, guest kernel and firmware, devices, and attestation integration |
| Application changes | Often required when using the SDK directly; some LibOS approaches can reduce changes | Intel positions TDX for VM deployment without application modification, subject to guest and platform compatibility |
| Best fit | A sensitive component that should be smaller than the whole application | Lift-and-shift or VM-centric workloads that need protection from the host layer |
| Main qualification | The enclave boundary and interfaces become engineering and security responsibilities | Shared memory, virtual devices, attestation, and platform enablement still require careful integration |
What Intel SGX protects
Enclaves define a narrow application boundary
Software Guard Extensions (SGX) lets an application designate code and data for execution in an enclave. Hardware controls access to enclave memory and helps prevent untrusted software outside the enclave from reading or modifying it. The application owner decides what enters the enclave, which calls cross the boundary, and which data remains protected.
This granularity can reduce the TCB. A service might put a key operation, a biometric matching routine, or a confidential algorithm in an enclave while leaving networking, storage, and other ordinary code outside it. The smaller boundary is useful only if the interfaces are designed correctly: data crossing into or out of the enclave must be validated, and bugs in trusted enclave code remain inside the TCB.
#1 Best Overall

- Intel Xeon E5-2699 V4 Docosa-core (22 Core) 2.20 Ghz Processor - Socket Lga 2011-v3 - 5.50 Mb - 55 Mb Cache - 64-bit Processing - 14 Nm - 145 W
SGX threat model and attestation
SGX is intended to let a relying party verify an enclave before sending it secrets. Remote attestation supplies evidence about the enclave measurement and platform state; the relying party then applies its own policy before provisioning keys or data. Intel describes SGX as protecting enclave code and data from modification and supporting attestation before information is shared.
That model does not mean the entire machine is hidden. The operating system, hypervisor, drivers, application code outside the enclave, and external services may remain untrusted. Availability is also outside the confidentiality guarantee: a hostile host can stop an enclave, delay it, or refuse service. Side channels, incorrect enclave interfaces, compromised dependencies, and physical attacks require separate analysis.
SDK and LibOS choices
Using Intel’s SGX SDK generally means defining enclave entry points, managing trusted and untrusted calls, and adapting memory, threading, file, and network behavior to enclave constraints. This work can be worthwhile when only a small portion of an application needs protection, but it is not a transparent packaging step.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
A library operating system (LibOS) can provide a different path. Intel identifies Gramine as an open-source example and also lists commercial offerings. A LibOS can run some existing applications with little or no source modification by supplying expected operating-system services inside the enclave model. Compatibility, system-call coverage, debugging, performance, and the resulting TCB still have to be tested for the specific application.
What Intel TDX protects
A Trust Domain is a VM-level boundary
Intel Trust Domain Extensions (TDX) creates a hardware-isolated guest VM called a Trust Domain. The TD runs with protected memory and CPU state, while the host VMM manages ordinary virtualization functions without receiving the TD’s private contents. Intel’s security objective includes confidentiality and integrity against software modification, relocation, and cross-domain corruption.
Intel’s documentation describes the model this way: A TD runs in a CPU mode that is designed to protect the confidentiality of its memory contents and its CPU state from any other software, including the host VMM or hypervisor, unless the memory contents are explicitly shared by the TD itself.
The qualification about explicitly shared memory matters. A TD must communicate through defined shared regions and virtual devices, so those paths need validation and appropriate trust assumptions.
Rank #2

TDX adversaries and residual exposure
The stated primary adversaries include a malicious host VMM, potentially colluding malicious TDs, and other software such as legacy VMs or firmware for some side-channel attacks. TDX is therefore aimed at a stronger host-disclosure scenario than an ordinary VM, but its guarantees are not a promise that every physical attack, side channel, denial-of-service condition, firmware defect, or implementation flaw has been eliminated.
Recommended Free Tools
TDX also creates a broader system boundary than an individual enclave. The protected guest, TDX module, CPU microcode, firmware, VMM behavior, guest kernel, virtual-device model, and attestation service all influence the security result. The host may be unable to read private TD memory while still controlling scheduling, interrupt delivery, resource availability, and other aspects of execution.
VM deployment model
TDX is managed through virtualization infrastructure. Intel presents it as suitable for lift-and-shift VM workflows and says application modification is not required. That statement describes the application interface, not a zero-work deployment. Operators still need a supported processor and firmware, a TDX-enabled VMM, a compatible guest kernel and firmware, correct private-versus-shared memory handling, virtual-device support, and an attestation workflow that the relying service accepts.
Threat model and isolation differences
| Question | SGX answer | TDX answer |
|---|---|---|
| What is isolated? | A selected enclave and its protected pages | A guest VM and its private TD memory and CPU state |
| Who defines the boundary? | The application and enclave developer | The VM image and TDX platform define the guest boundary; the operator defines shared interfaces and policy |
| Is the host VMM trusted? | It is outside the enclave trust boundary and should not learn enclave secrets | TDX explicitly aims to protect the TD from a malicious host VMM or hypervisor |
| What is the dominant engineering risk? | Incorrect enclave partitioning, entry points, data flows, and trusted code | Platform readiness, guest compatibility, shared-memory and device paths, attestation, and VM lifecycle operations |
| What happens if the boundary is wrong? | Secrets or security-critical logic may remain outside the enclave or be exposed through an interface | Unprotected shared data, unsupported devices, or an unverified guest stack can defeat the intended deployment policy |
The key distinction is not that one technology is secure and the other is insecure. SGX minimizes the amount of application code that must be trusted. TDX minimizes the need to trust the host virtualization layer for the confidentiality and integrity of a whole guest. A design that needs both properties may use different confidential-computing layers, but that combination must be evaluated as a new system rather than assumed to inherit the strongest property of each.
Workload support and required changes
When SGX is the better software fit
- The sensitive operation is a clearly separable component with a manageable API.
- You can audit the enclave’s code, dependencies, memory ownership, and data-flow boundary.
- You need an application-level attestation decision rather than attestation of an entire guest image.
- The application can tolerate enclave constraints or can run successfully under a tested SGX LibOS.
Direct SDK integration gives precise control but usually requires source changes and specialized testing. A LibOS can reduce porting work, yet it does not erase enclave-specific limits or remove the need to measure what code and libraries are trusted.
When TDX is the better operational fit
- The application already runs reliably in a VM and changing its source would be expensive or risky.
- The threat model requires the host VMM to be outside the confidentiality boundary.
- The deployment team can standardize a supported TDX host, guest image, VMM, and attestation service.
- Most of the workload, rather than one function, needs protection from the host.
“No application modification” should be read narrowly. A TDX deployment can preserve an application’s VM-facing interface, but unsupported kernel features, drivers, virtual devices, boot firmware, memory-sharing behavior, or attestation assumptions can still require engineering work. Application compatibility is not the same as platform readiness, and it does not guarantee equal performance.
Rank #3
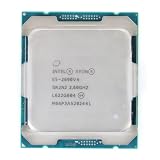
- Total Cores 14
- Total Threads 28
- Processor Base Frequency 2.60 GHz
- Max Turbo Frequency 3.50 GHz
- Sockets Supported LGA2011-3
Attestation: what the relying service must verify
SGX attestation flow
- Build and measure the enclave and record the identity and configuration values your policy expects.
- Obtain an attestation report from the running enclave and its platform.
- Send the report, along with any required collateral, to the relying service.
- Verify the report, platform status, enclave identity, freshness, and policy conditions.
- Only after successful verification provision keys or confidential input to the enclave.
The verifier must decide which enclave measurements, signer identities, security versions, and update states are acceptable. Updating a library or rebuilding the enclave can change measurements, so the policy needs a controlled rollover process.
TDX attestation flow
- Create a TD from a known guest image and record the expected TD measurements and configuration.
- Collect the TDX attestation evidence for that TD through the platform’s supported interface.
- Validate the evidence, its collateral, freshness, TDX version, platform status, and guest identity claims.
- Check that the host, firmware, VMM, guest kernel, and device configuration meet the relying service’s policy.
- Provision secrets only to the verified TD, and monitor updates, migration events, and policy changes.
TDX attestation does not make an arbitrary VM trustworthy by itself. The relying service must define which guest image, kernel, firmware, TDX version, and platform states it accepts. Migration, snapshots, re-provisioning, and cloud-provider changes can alter those assumptions and should trigger explicit policy decisions.
Hardware, firmware, and cloud availability
Processor generations
Intel introduced TDX with 4th Generation Xeon Scalable processors, also known as Sapphire Rapids. Intel’s support material lists 5th Generation Xeon Scalable as supported and says 3rd Generation Xeon Scalable and earlier do not support TDX. The same material discusses Xeon 6 families, but its table treats TDX support there as implied by the broader confidential-computing lineage rather than as a SKU-by-SKU guarantee. Verify the exact processor, server platform, BIOS or firmware level, and cloud instance before committing to a design.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →SGX availability likewise depends on the exact processor and platform configuration. Do not infer support from a product family name alone; confirm the SGX capability, firmware settings, operating-system support, and attestation service for the target environment.
Cloud and hosted environments
Intel lists Alibaba Cloud, Microsoft Azure, Google Cloud, and Intel Developer Cloud as TDX environments. Availability varies by region, instance type, host generation, guest image, and service lifecycle. A provider listing is not proof that the exact instance you need exposes every TDX function, supports your guest kernel, or offers the attestation interface your verifier expects. Obtain the provider’s current instance and documentation details before migration.
Performance: why one percentage cannot answer the question
Intel’s 2025 performance analysis identifies TDX transitions, memory encryption, and handling of shared versus private memory for I/O as possible overhead sources. In the study configurations summarized by Intel, CPU- and memory-intensive workloads showed about a 5% performance effect. Intel reports that I/O-intensive results vary and are generally higher. Those figures are vendor-published observations tied to the tested configurations and 4th Generation Xeon platform, not an independent benchmark or a guarantee for another processor, cloud instance, kernel, or application.
Rank #4

- Manufacturer: Intel CPU Frequency: 2.20 GHz CPU Max Turbo Frequency: 3.60 GHz Number of Cores: 22 Threads: 44 Cache: 55 MB Intel Smart Cache Number of UPI Links: 0 Lithography: 14 nm Thermal Design Power: 145 W Memory Types: DDR4 1600/1866/2133/2400 Max Memory Size: 1.5 TB Max # Memory Channels: 4 Sockets Supported: FCLGA2011-3 E5-2699v4
Measure the workload you actually intend to protect. Record baseline and TDX results for:
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →- CPU utilization and throughput for steady-state compute.
- Memory bandwidth, latency, page-fault behavior, and working-set size.
- Frequency of transitions between guest and host services.
- Network and storage I/O, especially operations that cross shared/private memory boundaries.
- Startup, attestation, reboot, migration, and recovery times.
- Tail latency and service-level objectives, not only average throughput.
SGX performance depends on how often data crosses the enclave boundary, the size of enclave memory, paging behavior, cryptographic operations, and whether a LibOS is used. A small SGX enclave can be efficient for a narrowly scoped function but costly if the application repeatedly moves large data sets in and out.
Security assurance and what the published reviews mean
Intel describes a 2024 Intel-and-Google security review that evaluated 81 attack scenarios and identified nine confirmed security vulnerabilities. Intel says those issues were mitigated in 4th Generation Xeon Scalable processors. This is a report of a review and its findings, not a certification or proof that later vulnerabilities cannot exist.
Intel separately reports a 2023 review of TDX 1.5 with Microsoft that examined 29 attack vectors, found six confirmed vulnerabilities, and produced 15 improvement recommendations or defense-in-depth issues. Intel says the issues were mitigated by the production release it names. Treat these figures as Intel’s account of its assurance work, not as an independent guarantee of security.
For either technology, a credible assessment should also cover side channels, speculative execution behavior, firmware and microcode updates, denial of service, rollback and replay, supply-chain integrity, key management, logging, and the security of the verifier. Confidential computing narrows what a hostile host can read; it does not remove the need for normal application and operational security.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchPC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11How to decide between SGX and TDX
Choose SGX when the sensitive boundary is small
SGX is usually the stronger fit when a single function, key store, or data-processing component needs isolation and the team can maintain a small, auditable TCB. It is also appropriate when the relying party needs attestation tied to that component rather than to a full guest image. Budget for enclave engineering, interface review, dependency management, and specialized testing.
Best Value

- Part Number Identification: CD8069504194501 for easy reference and compatibility verification
- CPU Series Specification: 2nd Generation Intel Xeon Scalable processor from the Gold 6000 series
- Processor Frequency: 3.10GHz base clock speed with 18 cores for high-performance computing tasks
- Package Type: OEM tray processor without retail packaging
- Cooling Device Notice: Processor only, cooling device not included and must be purchased separately
Choose TDX when the VM is the natural unit of trust
TDX is usually the stronger fit when an entire VM must be protected from the host VMM and the application already follows a conventional VM deployment model. It can reduce source-level porting, but the platform team must own hardware validation, firmware and VMM enablement, guest compatibility, shared-device design, attestation, and lifecycle operations.
Use a written decision record
- Describe the adversary: host VMM, co-resident tenant, firmware, operator, physical attacker, or another party.
- List the data and code that must remain confidential and identify what may be shared.
- Draw the TCB for each option, including libraries, guest components, TDX or SGX components, firmware, and attestation services.
- Define the exact attestation claims and update policy that a relying service will enforce.
- Confirm processor SKU, firmware, OS, VMM, cloud region, instance type, and feature version.
- Benchmark representative CPU, memory, storage, network, startup, and failure scenarios.
- Compare migration effort and lifecycle risk against the value of the smaller SGX boundary or the VM-level TDX boundary.
SGX-to-TDX migration playbook
- Inventory the current enclave. Record whether the application uses direct SGX SDK APIs, an SGX LibOS, or a combination. List enclave measurements, signer identities, security-version requirements, and every external interface.
- Map the existing TCB. Separate code and data that are inside the enclave from services that remain outside. Identify which secrets are released only after SGX attestation and what claims the relying service checks.
- Test VM behavior without TDX. Confirm that the application, dependencies, kernel, drivers, storage, networking, and operational tooling work as a conventional VM. This exposes assumptions hidden by enclave-specific code.
- Choose a supported TDX target. Verify the exact Xeon SKU, server or cloud instance, firmware, VMM, guest kernel, guest firmware, TDX version, and attestation interface.
- Redesign trust policy, not just packaging. Replace enclave-specific measurements and release rules with TD measurements and the guest, platform, and version claims the verifier will require. Preserve least-privilege key release.
- Audit shared interfaces. Classify network, storage, management, debugging, and device paths as private or shared. Validate data crossing those paths and remove secrets from shared buffers.
- Benchmark and fault-test. Measure performance, startup, attestation failures, host interference, reboots, updates, migration behavior, and loss of service. Compare against the SGX deployment under equivalent workload and policy.
- Run a staged cutover. Keep the SGX release and its attestation policy available while the TDX verifier policy is tested. Rotate keys deliberately, monitor evidence, and document rollback conditions.
Intel’s transition material describes multiple migration paths and is not an exhaustive design guide. A migration that preserves application binaries can still change the security assumptions, attestation policy, operational controls, and performance profile.
Deployment checklists
SGX checklist
- Define the enclave boundary and minimize trusted code and dependencies.
- Review every enclave entry point and untrusted call for validation and data ownership.
- Choose direct SDK integration or a tested LibOS approach.
- Verify processor, firmware, operating-system, SDK, and attestation support.
- Implement verifier policy for measurements, signer identity, security versions, freshness, and updates.
- Benchmark transitions, paging, cryptographic work, and data movement.
- Plan for denial of service, side channels, rollback, key rotation, and recovery.
TDX checklist
- Verify the exact processor SKU, BIOS or firmware, VMM, guest kernel, guest firmware, and TDX version.
- Confirm that the cloud region or server actually offers TDX and the required attestation interface.
- Measure the TD image and define acceptable guest, platform, and version claims.
- Classify private and shared memory and audit every virtual device.
- Test snapshots, reboot, migration, updates, host interference, and recovery behavior.
- Benchmark CPU, memory, storage, networking, startup, and tail latency on the intended platform.
- Document which host-controlled properties remain outside confidentiality and integrity guarantees.
Roadmap and lifecycle planning
Intel’s October 2026 transition guide says future confidential-computing investment will focus exclusively on TDX and that Diamond Rapids will be the last platform to support SGX. The same guide says SGX support will continue well into the 2030s. These are Intel’s stated roadmap positions, not an independently confirmed lifecycle guarantee for every processor, server, cloud service, SDK, or attestation endpoint.
For a long-lived system, record the exact hardware and software versions you depend on, the attestation collateral and verifier policy, and the cloud or server provider’s support commitment. Recheck those details before each procurement or migration decision, because feature availability, firmware requirements, TDX versions, cloud regions, and roadmap information can change.
Bottom line
SGX is the choice for a deliberately small application enclave when you can afford enclave-aware engineering and need a narrowly scoped TCB. TDX is the choice for protecting a supported VM from the host virtualization layer when VM compatibility and platform integration matter more than function-level isolation. TDX does not simply replace SGX: it changes the trust boundary, attestation object, operational work, and performance questions. Select the technology only after documenting the threat model and validating the complete workload on the exact target platform.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

