Free tools Windows power users keep installed
One-click scans. No signup required.
Google rolling back its decision to kill third-party cookies in Chrome is a real operational change—not just a policy tweak. For teams running ad tech, analytics, and personalization, the safest response is to treat it as extra time while you fix the underlying dependencies.
Third-party cookies have been under pressure for years due to privacy concerns and regulatory expectations. A rollback can delay breakage, but it doesn’t remove the need for privacy-safe measurement and storage strategies.
As an Amazon Associate I earn from qualifying purchases.
What Google actually rolled back, and why it matters
When a browser vendor rolls back a deprecation plan, the visible result is usually that third-party cookies remain available for longer (or that blocking rules are softened). The details can vary by Chrome version, environment, and user settings, but the practical meaning is consistent: some cross-site tracking workflows that were going to break are less likely to break immediately.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Even so, you should avoid treating this as a permanent reversal. Chrome’s broader direction—replacing third-party cookie dependence with privacy-focused mechanisms—still matters for deliverability, compliance, and long-term system stability.
#1 Best Overall

- [Compatible with Google Pixel 10/Pixel 10 Pro 6.3 inch] Only compatible with Google Pixel 10/Pixel 10 Pro phone 6.3 inch (Not for Pixel 10 Pro XL 6.8 inch). Precise cutouts for easy access to all ports, buttons, sensors and cameras. Sensitive buttons with good response, are easy to press.
- [Magnetic Designed for Google Pixel 10/Pixel 10 Pro 6.3 inch ] Built-in magnet ring aligns perfectly and locks into place making wireless charging faster and easier than ever. This Google Pixel 10/Pixel 10 Pro case will not fall off no matter how it rotates with super adsorption capacity.
- [Thorough Camera & Screen Protection for Google Pixel 10/Pixel 10 Pro 6.3 inch] 1.5mm raised lips over screen and 1.5mm raised lips over camera relieves over this Google Pixel 10/Pixel 10 Pro case, impacts and protects the phone screen and camera against drop damage, cracks and scratches. Reinforced corner effectively absorb bumps from any angle drop.
- [Zero Fingerprints] SPIDERCASE translucent matte Google Pixel 10/Pixel 10 Pro case with a smart Nano Oleophobic Coating design that prevents fingerprints, watermarks, oil, and dust, comfortable and clean.
- [Shock Protection] Passing military drop tests up, your device is effectively protected from violent impacts and drops
Third-party cookies in plain English
A first-party cookie is set by the domain a user is currently visiting. A third-party cookie is set by a different domain embedded in that page—commonly ad networks, analytics providers, pixels, and other cross-site tags.
Because third-party cookies flow across sites, they’ve historically powered audience recognition, retargeting, frequency capping, and cross-site attribution.
What a rollback changes for websites and advertisers
- Less immediate breakage: Some vendors’ tracking setups may continue to function as before.
- More variability: You can still see different outcomes depending on Chrome version, consent state, and user privacy controls.
- More time to migrate: Teams get breathing room to implement Privacy Sandbox alternatives and harden consent + measurement logic.
Timeline and how Chrome behavior can vary
Chrome’s cookie roadmap has included staged rollouts, trials, and exceptions. When Google changes course, it often modifies the effective timeline rather than reverting all related privacy features to “no restrictions ever.”
Practically, this means you should test on the exact Chrome versions and configurations your audience uses—not only on your primary dev environment.
Why you may see different results in different environments
Several factors can affect whether third-party cookies work:
- Chrome version: Chrome updates frequently, and storage behavior can change between milestones.
- User privacy settings: Chrome and platform settings can override defaults.
- Consent mode / consent gating: If tags are blocked until consent, you may misinterpret results.
- Third-party context: iFrames, redirects, pop-ups, and embedded content can change how storage is accessed.
Who should care most
Publishers and ad tech
If you monetize with display ads, you likely rely on vendor cookies for frequency, uniqueness, and reporting. A rollback reduces urgency, but it doesn’t remove the need to improve measurement accuracy and reduce fragile cross-site dependencies.
Advertisers and measurement teams
Retargeting and conversion attribution are the first places where cookie changes show up. Even if third-party cookies persist longer, you still need a measurement plan that can survive more restrictive scenarios.
Developers and analytics engineers
For engineering teams, the work is less about “tracking vs not tracking” and more about correct storage behavior across browsers, domains, and consent states. Your goal is consistency: predictable analytics, fewer silent failures, and clear debugging signals.
Immediate actions to take (before you rewrite everything)
A rollback often tempts teams to pause migration projects. The better approach: keep the migration work, but re-prioritize based on risk and effort. The fastest wins usually come from auditing and controlled testing.
Rank #2
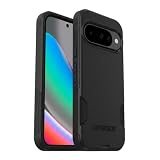
- Perfect Fit for Google Pixel 10 & Pixel 10 Pro (Only - Not Compatible with Pixel 10 Pro XL): Precision-engineered for the Google Pixel 10 & 10 Pro, this OtterBox case offers a flawless fit. It not only preserves your phone's sleek design but also ensures unparalleled protection against everyday hazards.
- Rugged Multi-Layer Defense: Featuring dual-layer construction with a rigid shell and internal rubber layer, our case exceeds 3X military drop standards (MIL-STD-810G 516.6), crafted from over 35% recycled plastic for eco-conscious resilience.
- Secure Grip, Streamlined Protection: Rely on the OtterBox legacy with Commuter Series—total protection with rubber-gripped edges for a secure hold. It's a slim, easy-to-install case providing durable quality and a precise fit for hassle-free defense
- Wireless Charging Compatible: Its slim profile is pocket-friendly, offering protection and ease for your on-the-go lifestyle
- Trusted OtterBox Quality: With OtterBox, you're not just buying a case; you're investing in peace of mind.
Audit your cookie usage and consent flows
Document where third-party cookies are used and under what conditions they’re set or read:
- Which domains set cookies (analytics, ad networks, SSPs, CMPs)?
- Which tags run only after consent?
- Which journeys rely on cross-site continuity (e.g., ad click → site visit → conversion)?
Make it concrete: list each vendor script/pixel and the cookie names or storage keys they rely on.
Segment test cases by browser and user state
Don’t test only “Chrome default.” Create scenarios that reflect real user states:
- Consent granted: All marketing/ad tags allowed.
- Consent denied: Only essential/vendor-required tags.
- Incognito: No long-lived storage.
- Cross-site journey: Land via ad/affiliate, then navigate to conversion.
- Iframe-heavy pages: Embedded players, galleries, or widgets.
Re-check ad/measurement vendors and tags
Vendor setups can be brittle even when third-party cookies are still available. Confirm each vendor’s current configuration matches your consent and attribution strategy.
- Verify tag firing order (especially CMP → analytics → ad tags).
- Confirm your conversion events are deduped and correctly scoped.
- Ensure your reporting pipeline doesn’t assume a cookie always exists.
Prepare anyway: the safer long-term path
A rollback gives you time, but browser privacy strategies move toward reducing universal cross-site identifiers. The long-term work is to reduce your dependency on third-party cookies for core measurement and audience use cases.
Chrome’s Privacy Sandbox initiative provides replacement primitives. You don’t have to adopt everything at once; you do need to understand what each mechanism is for and where it fits.
Privacy Sandbox options you should understand
Below are the main families of APIs and concepts that commonly come up when teams migrate away from third-party cookie reliance.
CHIPS (partitioned cookies)
CHIPS enables partitioned third-party cookies: the cookie is scoped to the top-level site that embeds it, reducing cross-site tracking while preserving functionality for embedded experiences.
It’s commonly relevant when you need third-party functionality in an iframe without sharing identifiers across all sites.
Rank #3

- Strong Magnetic Attraction: Powerful built-in magnets, easier place-and-go wireless charging and compatible with Pixelsnap
- Compatibility: Compatible with Google Pixel 10/10 Pro 6.3 inch; precise cutouts for easy access to all ports, buttons, sensors and cameras, soft and sensitive buttons with good response, are easy to press
- Matte Translucent Back: Features a flexible TPU frame and a matte coating on the hard PC back to provide you with a premium touch and excellent grip, while the entire matte back coating perfectly blocks smudges, fingerprints and even scratches
- Shock Protection: Passing military drop tests up to 10 feet, your device is effectively protected from violent impacts and drops
- HD Tempered Glass Screen Protector: 0.33mm thin with 99% clarity and oleophobic coating.Features edge-to-edge coverage,bubble-free installation kit and 9H hardness against scratches
Storage Access API
The Storage Access API allows a third-party context to request access to cookies under user gesture or permission conditions. It’s designed to avoid automatic cross-site storage access while supporting legitimate embedded use cases.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Topics
Topics is an interest-based mechanism that categorizes browsing signals into broad topics. Advertisers can then target based on these categories rather than per-user cross-site identifiers.
FLEDGE (interest-based ads)
FLEDGE supports on-device interest signaling and ad selection using cohorts and privacy-preserving flows. It’s aimed at retargeting and dynamic ad selection without direct third-party cookie identifiers.
Attribution Reporting
Attribution Reporting focuses on conversion measurement using privacy-preserving attribution models. Instead of reading third-party cookie IDs directly, it uses reporting events with limits designed to reduce re-identification.
FedCM (sign-in continuity)
FedCM helps maintain federated sign-in continuity while reducing the need for cross-site tracking cookies. If you run SSO and login flows across domains, this is worth understanding.
How to test third-party cookie behavior in Chrome
Testing is where teams usually lose days. The goal is to verify whether cookies are blocked, whether storage is partitioned, and whether your tags degrade gracefully.
Use DevTools to see blocked storage
In Chrome:
- Open DevTools (right-click → Inspect).
- Go to the Application tab.
- In the left panel, check Cookies and Storage for the relevant domains.
- Use the network and console logs to identify failed requests tied to tracking or attribution.
Also watch for network endpoints that rely on identifiers. If those requests return empty payloads or missing IDs, your analytics may look “working” while attribution silently fails.
Validate with controlled test profiles
Repeat your journey tests on:
- A fresh profile (no cookies).
- A returning profile (with first-party cookies).
- An environment where third-party cookies are restricted (for comparison).
This lets you tell whether your system is resilient or merely “currently lucky.”
Watch for edge cases: iframes, cross-site redirects, and first-party proxies
Common failure points include:
- Iframe embedding: Third-party scripts inside iFrames may behave differently than top-level pages.
- Cross-site redirects: Redirect chains can change the top-level site context that storage is scoped to.
- First-party proxy patterns: If you proxy third-party calls through your domain, confirm you aren’t masking a broken consent condition.
Fallback strategies when third-party cookies are blocked (or half-working)
Even with a rollback, you should design for “partial failure.” That means your conversion and analytics pipelines should tolerate missing third-party identifiers.
Recommended Free Tools
Rank #4
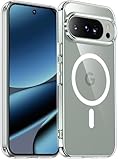
- [Compatible] Only compatible with Google Pixel 10/Pixel 10 Pro phone. Precise cutouts for easy access to all ports, buttons, sensors and cameras. Sensitive buttons with good response, are easy to press.
- [Magnetic Designed] Built-in magnet ring aligns perfectly and locks into place making wireless charging faster and easier than ever. This Google Pixel 10/Pixel 10 Pro case will not fall off no matter how it rotates with super adsorption capacity.
- [Thorough Camera & Screen Protection] 1.5mm raised lips over screen and 1.5mm raised lips over camera relieves over this Google Pixel 10/Pixel 10 Pro case, impacts and protects the phone screen and camera against drop damage, cracks and scratches. Reinforced corner effectively absorb bumps from any angle drop.
- [Zero Fingerprints] SPIDERCASE translucent matte Google Pixel 10/Pixel 10 Pro case with a smart Nano Oleophobic Coating design that prevents fingerprints, watermarks, oil, and dust, comfortable and clean.
- [Shock Protection] Passing military drop tests up, your device is effectively protected from violent impacts and drops
Consent-gated tagging
Ensure your CMP behavior is deterministic:
- If consent is denied, tags that require marketing storage shouldn’t fire.
- If consent is granted later, your system should support late initialization without double-counting conversions.
In practice, this is where teams reduce compliance risk and improve analytics correctness.
Server-side tagging and first-party endpoints
Server-side approaches can reduce reliance on client-side third-party storage. Instead of assuming the browser has a third-party cookie, your backend can manage sessions using first-party identifiers or privacy-preserving mechanisms.
Be careful: server-side doesn’t make privacy constraints disappear. You still need a consent-aware data strategy and correct event deduplication.
First-party storage partitioning where appropriate
If your use case is tied to a specific publisher and embedded partner, partitioned storage (or Storage Access patterns) may preserve functionality without cross-site tracking.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsThe key is to map each requirement to a storage model and then test it under restricted conditions—not just under defaults.
Common mistakes that cost weeks
Assuming the rollback applies instantly everywhere
Chrome versions roll out in phases across platforms. Also, some systems behave differently in iOS or on managed devices. Test on realistic environments, not a single desktop profile.
Not updating QA scenarios for new Chrome versions
If you keep a stale QA matrix, you’ll miss regressions and misattribute them to the cookie change. Build a minimal regression suite you can rerun after each Chrome milestone.
Skipping vendor configuration checks
Most cookie-dependent breakage comes from vendor scripts expecting cookies that your consent gating (or browser privacy settings) prevents from being set. Treat vendor reconfiguration as part of rollout readiness.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Troubleshooting checklist
If things break, don’t guess. Use a structured checklist to isolate whether the issue is storage availability, event firing, deduplication, or reporting pipeline logic.
Best Value

- Perfect Fit for Google Pixel 9 & 9 Pro: Precision-engineered for the Google Pixel 9 & 9 Pro, this OtterBox case offers a flawless fit. It not only preserves your phone's sleek design but also ensures unparalleled protection against everyday hazards.
- Rugged Multi-Layer Defense: Featuring dual-layer construction with a rigid shell and internal rubber layer, our case exceeds 3X military drop standards (MIL-STD-810G 516.6), crafted from over 35% recycled plastic for eco-conscious resilience.
- Secure Grip, Streamlined Protection: Rely on the OtterBox legacy with Commuter Series—total protection with rubber-gripped edges for a secure hold. It's a slim, easy-to-install case providing durable quality and a precise fit for hassle-free defense
- Wireless Charging Compatible: Its slim profile is pocket-friendly, offering protection and ease for your on-the-go lifestyle
- Trusted OtterBox Quality: With OtterBox, you're not just buying a case; you're investing in peace of mind. Our limited warranty covers material and workmanship defects.
If attribution breaks after a Chrome update
- Confirm event firing: Does the conversion event reach your endpoint?
- Check identifier dependencies: Are you reading cookie-based IDs at event time?
- Verify dedupe logic: Missing IDs can cause “new” users and duplicate counts.
- Compare top-level vs iframe behavior: Some attribution setups differ across contexts.
If login or SSO loops show up
- Inspect whether third-party storage or federated sign-in tokens are blocked.
- Test the flow with and without cross-site embedding.
- Validate any FedCM-related integration if your stack supports it.
If “no cookies” reports contradict DevTools
- Ensure you’re looking at the same domain scope and the same frame context.
- Verify consent state: a CMP can disable tags even if cookies are technically allowed.
- Check network calls for missing identifiers in payloads.
Alternatives to third-party cookies: what to choose and when
Different business goals map to different mechanisms. The table below is a pragmatic way to align use cases with privacy-safe alternatives.
| Use case | Common third-party cookie reliance | Privacy-safe alternative(s) to evaluate |
|---|---|---|
| Cross-site conversion measurement | Click/user IDs stored in third-party context | Attribution Reporting, server-side measurement with consent controls |
| Retargeting / interest-based ads | Audience membership via third-party identifiers | FLEDGE, Topics |
| Embedded functionality in iFrames | Third-party cookies shared across sites | CHIPS, Storage Access API |
| Federated sign-in continuity | Cross-site cookies for session continuity | FedCM |
| Frequency capping | Persistent cross-site user identifier | Partitioned approaches and privacy-preserving reporting (vendor dependent) |
Vendor support is uneven by feature and platform. Build a compatibility matrix that matches your traffic sources and your top conversion paths.
FAQs
Does this rollback mean third-party cookies will never be removed?
No. A rollback typically delays or alters enforcement details. Chrome’s privacy direction still points toward replacing cross-site tracking with privacy-preserving mechanisms.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchPC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Will my site stop breaking if I do nothing?
Not necessarily. Even if third-party cookies remain available longer, consent gating, iframe contexts, and vendor configurations can still break attribution or personalization logic.
What should I prioritize if I’m a small site?
Start with a cookie + tag audit and a minimal test suite that covers consent granted/denied and cross-site journeys. Then check whether your analytics and ad stack can operate without third-party identifiers.
Which is safer: patching now or migrating now?
Best practice is “migrate while stabilizing.” Use the rollback time to implement privacy-safe alternatives where they map to your core use cases, while keeping current tracking functional for the majority of users.
Bottom Line
Google’s rollback buys time, but it doesn’t remove the need to modernize measurement and reduce brittle third-party cookie dependencies. Treat this as an opportunity to harden consent flows, audit storage usage, and test your critical journeys under multiple Chrome conditions.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchIf you align your tracking plan to Privacy Sandbox primitives and build resilient fallback behavior, you’ll be ready regardless of whether enforcement tightens again later.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

