What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
To deploy GlobalProtect Connect Before Logon (CBL) with Configuration Manager, install the organization’s GlobalProtect MSI, register its Windows sign-in provider with PanGPS.exe -registerplap, apply the portal and connection settings required by your GlobalProtect design, and detect both the installed client and its configuration. Run the deployment as SYSTEM through a Configuration Manager Application and test it on representative devices before broad rollout.
CBL, PLAP registration, and GlobalProtect pre-logon are related but not interchangeable. The forum example’s CBLPortal1 registry key is community-provided and may be specific to that environment. Palo Alto’s pre-logon quick-configuration guide documents a different bootstrap path, PanSetup, with Portal and Prelogon values. Confirm which settings your GlobalProtect release and portal configuration require before deploying them.
What the deployment needs to accomplish
A working deployment has more parts than the MSI command and PLAP registration. Configuration Manager can install the client, but the portal, gateway, authentication, certificate, and agent policy must also support the connection method you intend to use.
- Install the correct GlobalProtect MSI for the Windows architecture and release managed by your organization.
- Set the approved portal and the connection method supported by that MSI and your portal configuration.
- Register the GlobalProtect PLAP provider so Windows can offer it at sign-in.
- Apply only the registry configuration appropriate to your chosen implementation.
- Use detection that verifies the intended installed state, not just the presence of a leftover registry key.
Palo Alto describes pre-logon as a GlobalProtect connection method that establishes a tunnel before a user signs in. An endpoint that has not yet obtained its portal configuration may need a pre-deployed portal and registry bootstrap settings. See Palo Alto Networks’ pre-logon configuration guide.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minute#1 Best Overall
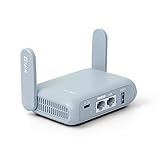
- 【DUAL BAND AX TRAVEL ROUTER】Products with US, UK, EU Plug; Dual band network with wireless speed 574Mbps (2.4G)+2402Mbps (5G); 2.5G Multi-gigabit WAN port and a 1G gigabit LAN port; USB 3.0 port; Wi-Fi 6 offers more than double the total Wi-Fi speed with the MT3000 VPN Router.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Beryl AX automatically encrypts all network traffic within the connected network. Max. VPN speed of 150 Mbps (OpenVPN); 300 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl AX is a portable wifi box and mini router that runs on OpenWrt 21.02 firmware. It supports more than 5,000 ready-made plug-ins for customization. Simply browse, install, and manage packages with our no-code interface within Beryl AX's Admin Panel.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
- 【VPN CASCADING AT EASE】Surpassing the mediocre performance of most VPN routers for home usage, the Beryl AX is capable of hosting a VPN server and VPN client at the same time within the same device, enabling users to remote access local network resources like Wi-Fi printers or local web servers, and accessing the public internet as a VPN client simultaneously.
Understand CBL, PLAP, and pre-logon
Connect Before Logon and PLAP
Connect Before Logon commonly describes the Windows sign-in experience made available through a credential provider known as a PLAP provider. Running PanGPS.exe -registerplap registers the provider; it does not, by itself, establish a working VPN or configure the portal, gateway, authentication, or policy.
Pre-logon
Pre-logon describes the GlobalProtect connection method used to establish a tunnel before a user signs in. Its operation depends on the GlobalProtect portal and gateway configuration as well as the endpoint’s authentication and network prerequisites. For example, a machine certificate may be required by the organization’s authentication design.
Ordinary user-logon or on-demand VPN
If users only need to connect after signing in, a pre-logon design may be unnecessary. Do not copy an MSI property or registry configuration from another organization and assume it enables your preferred mode. The forum example uses CONNECTMETHOD="on-demand" alongside PLAP registration and CBL registry settings; that is evidence of one environment’s approach, not a universal pre-logon recipe. Check the administrator guide for the exact GlobalProtect release and align the MSI settings with the portal’s agent configuration. The original example is at the GlobalProtect SCCM forum thread.
Prepare the source content and prerequisites
Use a versioned source directory so the MSI, scripts, and deployment configuration stay associated with the same release:
Rank #2

- 【DUAL BAND WIFI 7 TRAVEL ROUTER】Products with US, UK, EU, AU Plug; Dual band network with wireless speed 688Mbps (2.4G)+2882Mbps (5G); Dual 2.5G Ethernet Ports (1x WAN and 1x LAN Port); USB 3.0 port.
- 【NETWORK CONTROL WITH TOUCHSCREEN SIMPLICITY】Slate 7’s touchscreen interface lets you scan QR codes for quick Wi-Fi, monitor speed in real time, toggle VPN on/off, and switch providers directly on the display. Color-coded indicators provide instant network status updates for Ethernet, Tethering, Repeater, and Cellular modes, offering a seamless, user-friendly experience.
- 【OpenWrt 23.05 FIRMWARE】The Slate 7 (GL-BE3600) is a high-performance Wi-Fi 7 travel router, built with OpenWrt 23.05 (Kernel 5.4.213) for maximum customization and advanced networking capabilities. With 512MB storage, total customization with open-source freedom and flexible installation of OpenWrt plugins.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Slate 7 automatically encrypts all network traffic within the connected network. Max. VPN speed of 100 Mbps (OpenVPN); 540 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【PERFECT PORTABLE WIFI ROUTER FOR TRAVEL】The Slate 7 is an ideal portable internet device perfect for international travel. With its mini size and travel-friendly features, the pocket Wi-Fi router is the perfect companion for travelers in need of a secure internet connectivity on the go in which includes hotels or cruise ships.
GlobalProtect
├── GlobalProtect64.msi
├── Install-GlobalProtect.ps1
└── Detect-GlobalProtect.ps1
For example, store release content under a versioned path such as \SCCMSourceApplicationsGlobalProtect6.x.x. Replace the example version with the actual release; obtain the MSI through your organization’s Palo Alto Networks software and support channel.
- Confirm the GlobalProtect version, MSI architecture, and supported MSI public properties.
- Obtain the approved portal hostname and confirm the intended connect method with the firewall or Panorama administrator.
- Verify that portal and gateway policy, authentication, certificates, DNS, and pre-logon network reachability are ready.
- Use a Configuration Manager test collection and define the reboot behavior for the exact MSI and device population.
- Decide whether the official pre-logon bootstrap path, a version-specific CBL configuration, or both are required. Do not import an unreviewed registry export.
Install the MSI and configure the endpoint with PowerShell
The following wrapper provides a baseline for a Configuration Manager Application. It logs the MSI and script activity, checks for the installed executable, registers PLAP, and writes Palo Alto’s documented pre-logon bootstrap values when the selected method is pre-logon. Verify PORTAL, CONNECTMETHOD, and accepted property values against the administrator guide for your MSI release before production use. The registry and portal policy must also match your organization’s design.
[CmdletBinding()]
param(
    [Parameter(Mandatory = $true)]
    [string]$Portal,

    [ValidateSet('on-demand', 'pre-logon', 'user-logon')]
    [string]$ConnectMethod = 'pre-logon',

    [switch]$ConfigureForumStyleCbl
)

$ErrorActionPreference = 'Stop'

$LogDirectory = Join-Path $env:ProgramData 'CompanyLogs'
$LogFile = Join-Path $LogDirectory 'GlobalProtect-Install.log'
New-Item -Path $LogDirectory -ItemType Directory -Force | Out-Null
Start-Transcript -Path $LogFile -Append | Out-Null

try {
    $MsiPath = Join-Path $PSScriptRoot 'GlobalProtect64.msi'
    if (-not (Test-Path -LiteralPath $MsiPath)) {
        throw "GlobalProtect MSI was not found: $MsiPath"
    }

    $MsiLog = Join-Path $LogDirectory 'GlobalProtect-MSI.log'
    $MsiArguments = @(
        '/i'
        "`"$MsiPath`""
        '/qn'
        '/norestart'
        "PORTAL=`"$Portal`""
        "CONNECTMETHOD=`"$ConnectMethod`""
        '/L*v'
        "`"$MsiLog`""
    ) -join ' '

    $MsiProcess = Start-Process `
        -FilePath "$env:SystemRootSystem32msiexec.exe" `
        -ArgumentList $MsiArguments `
        -Wait -PassThru -WindowStyle Hidden

    if ($MsiProcess.ExitCode -notin @(0, 3010)) {
        throw "GlobalProtect MSI installation failed with exit code $($MsiProcess.ExitCode)"
    }

    $PanGpsPaths = @(
        (Join-Path $env:ProgramFiles 'Palo Alto NetworksGlobalProtectPanGPS.exe'),
        (Join-Path ${env:ProgramFiles(x86)} 'Palo Alto NetworksGlobalProtectPanGPS.exe')
    ) | Where-Object { $_ -and (Test-Path -LiteralPath $_) }

    $PanGpsPath = $PanGpsPaths | Select-Object -First 1
    if (-not $PanGpsPath) {
        throw 'PanGPS.exe was not found after installation.'
    }

    $PlapProcess = Start-Process `
        -FilePath $PanGpsPath `
        -ArgumentList '-registerplap' `
        -Wait -PassThru -WindowStyle Hidden

    if ($PlapProcess.ExitCode -ne 0) {
        throw "PLAP registration failed with exit code $($PlapProcess.ExitCode)"
    }

    if ($ConnectMethod -eq 'pre-logon') {
        $PanSetupPath = 'HKLM:SOFTWAREPalo Alto NetworksGlobalProtectPanSetup'
        New-Item -Path $PanSetupPath -Force | Out-Null
        New-ItemProperty -Path $PanSetupPath -Name 'Portal' `
            -Value $Portal -PropertyType String -Force | Out-Null
        New-ItemProperty -Path $PanSetupPath -Name 'Prelogon' `
            -Value '1' -PropertyType String -Force | Out-Null
    }

    # Use only if this CBL path is required by the tested release and design.
    if ($ConfigureForumStyleCbl) {
        $CblPath = 'HKLM:SOFTWAREPalo Alto NetworksGlobalProtectCBL'
        New-Item -Path $CblPath -Force | Out-Null
        New-ItemProperty -Path $CblPath -Name 'Portal1' `
            -Value $Portal -PropertyType String -Force | Out-Null
    }

    if ($MsiProcess.ExitCode -eq 3010) {
        exit 3010
    }
    exit 0
}
catch {
    Write-Error $_
    exit 1
}
finally {
    Stop-Transcript | Out-Null
}
The PanSetupPortal and PanSetupPrelogon values reflect the bootstrap settings in Palo Alto’s cited pre-logon guide. The optional CBLPortal1 value comes from the forum example and should not be treated as interchangeable with PanSetup or as universally required. Confirm the exact registry view and values for the GlobalProtect version you deploy.
What the MSI switches and result codes mean
/qnrequests a quiet installation with no user interface./norestartprevents the MSI from initiating a restart./L*vcreates a verbose Windows Installer log at the supplied path.PORTALandCONNECTMETHODare shown as example MSI properties; their availability and accepted values must be checked for the exact release.3010is commonly used to signal successful installation with a reboot required. Configure Configuration Manager’s return-code behavior and reboot handling based on the tested MSI, rather than assuming every release behaves identically.
The sample paths and log directory assume Windows and an organization-created CompanyLogs directory name. Change that name to your standard. Do not put credentials, secrets, or certificates in a command line.
Rank #3

- 【Five Gigabit Ports】1 Gigabit WAN Port plus 2 Gigabit WAN/LAN Ports plus 2 Gigabit LAN Port. Up to 3 WAN ports optimize bandwidth usage through one device.
- 【One USB WAN Port】Mobile broadband via 4G/3G modem is supported for WAN backup by connecting to the USB port. For complete list of compatible 4G/3G modems, please visit TP-Link website.
- 【Abundant Security Features】Advanced firewall policies, DoS defense, IP/MAC/URL filtering, speed test and more security functions protect your network and data.
- 【Highly Secure VPN】Supports up to 20× LAN-to-LAN IPsec, 16× OpenVPN, 16× L2TP, and 16× PPTP VPN connections.
- Security - SPI Firewall, VPN Pass through, FTP/H.323/PPTP/SIP/IPsec ALG, DoS Defence, Ping of Death and Local Management. Standards and Protocols IEEE 802.3, 802.3u, 802.3ab, IEEE 802.3x, IEEE 802.1q
Choose the registry configuration deliberately
Palo Alto pre-logon bootstrap settings
Palo Alto’s pre-logon guide identifies HKLMSOFTWAREPalo Alto NetworksGlobalProtectPanSetup and the Portal and Prelogon values for endpoints that need a pre-deployed portal configuration. These settings are a bootstrap element, not a substitute for configuring the portal, gateway, and authentication design.
Forum-style CBL value
The community thread shows HKLMSOFTWAREPalo Alto NetworksGlobalProtectCBL with a Portal1 value. Use it only when your organization has verified that this is required for its installed release and implementation. Do not infer additional value names for multiple portals without version-specific documentation.
Create the Configuration Manager Application
A Configuration Manager Application is generally a better fit than a legacy Package/Program when you need detection and an installed-state result. Microsoft documents script installer deployment types, MSI deployment types, and detection methods in its script installer deployment type, MSI deployment type, and detection method references.
Deployment type and install command
- Create an Application and add a Script Installer deployment type, with content pointing to the folder containing the MSI and scripts.
- Use an install command such as
powershell.exe -NoLogo -NoProfile -ExecutionPolicy Bypass -File .Install-GlobalProtect.ps1 -Portal "vpn.example.com" -ConnectMethod pre-logon. Replace the example portal with your approved hostname. - If the optional forum-style path has been validated for your environment, append
-ConfigureForumStyleCbl. - Set installation behavior to Install for system, logon requirement to Whether or not a user is logged on, and administrative rights as required. The SYSTEM context is appropriate for machine-wide MSI and HKLM configuration; it is not the same as an interactive administrator session.
- Set a maximum runtime long enough for MSI installation and service operations. Configure return codes, including the tested handling of
3010, and select a reboot behavior consistent with your change process. - Distribute the content, deploy first to a test collection, and confirm client evaluation, enforcement, detection, and user sign-in behavior before expanding deployment.
Uninstall command
Use the product code from the exact MSI or installed product registration; do not borrow a GUID from another release:
Recommended Free Tools
Rank #4

- 【AC1200 Dual-band Wireless Router】Simultaneous dual-band with wireless speed up to 300 Mbps (2.4GHz) + 867 Mbps (5GHz). 2.4GHz band can handles some simple tasks like emails or web browsing while bandwidth intensive tasks such as gaming or 4K video streaming can be handled by the 5GHz band.*Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【Easy Setup】Please refer to the User Manual and the Unboxing & Setup video guide on Amazon for detailed setup instructions and methods for connecting to the Internet.
- 【Pocket-friendly】Lightweight design(145g) which designed for your next trip or adventure. Alongside its portable, compact design makes it easy to take with you on the go.
- 【Full Gigabit Ports】Gigabit Wireless Internet Router with 2 Gigabit LAN ports and 1 Gigabit WAN ports, ideal for lots of internet plan and allow you to connect your wired devices directly.
- 【Keep your Internet Safe】IPv6 supported. OpenVPN & WireGuard pre-installed, compatible with 30+ VPN service providers. Cloudflare encryption supported to protect the privacy.
msiexec.exe /x {PRODUCT-CODE-GUID} /qn /norestart /L*v "%ProgramData%CompanyLogsGlobalProtect-Uninstall.log"If your removal process also unregisters PLAP, verify the vendor-supported procedure for that GlobalProtect release in a test environment before adding it. The cited Palo Alto administrator guide is for GlobalProtect 10.0 and is version-specific; it is not proof that one uninstall procedure applies to every current release. See the GlobalProtect 10.0 administrator guide.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Set detection to match the required state
If the goal is only to install the MSI, use MSI product-code detection for the exact package. If the goal is a pre-logon-ready endpoint, stronger detection should also check the executable and the intended configuration. Configuration Manager supports MSI, registry, file, and custom script detection methods; a script can represent a combined desired state.
$ErrorActionPreference = 'SilentlyContinue'

$PanGpsPaths = @(
    (Join-Path $env:ProgramFiles 'Palo Alto NetworksGlobalProtectPanGPS.exe'),
    (Join-Path ${env:ProgramFiles(x86)} 'Palo Alto NetworksGlobalProtectPanGPS.exe')
) | Where-Object { $_ -and (Test-Path -LiteralPath $_) }

$PanGpsExists = $null -ne ($PanGpsPaths | Select-Object -First 1)
$PanSetup = Get-ItemProperty `
    -Path 'HKLM:SOFTWAREPalo Alto NetworksGlobalProtectPanSetup' `
    -ErrorAction SilentlyContinue

$ExpectedPortal = 'vpn.example.com'
$ConfigurationMatches = $null -ne $PanSetup `
    -and $PanSetup.Portal -eq $ExpectedPortal `
    -and $PanSetup.Prelogon -eq '1'

if ($PanGpsExists -and $ConfigurationMatches) {
    Write-Output 'GlobalProtect pre-logon configuration detected'
    exit 0
}
exit 1
Replace the portal placeholder and tailor the script if your approved design uses a different registry path. If the deployment intentionally uses the forum-style CBL configuration, detection should check that required value as well as the installed client. Do not report installed solely because a registry key exists: stale values can survive an incomplete uninstall. Test detection under the same architecture and SYSTEM context used by Configuration Manager.
Test in stages before broad deployment
- Test installation on a clean supported Windows device and confirm the MSI and PowerShell logs are created.
- Test upgrade behavior on a device with the previous GlobalProtect release, including whether old registry or PLAP state needs cleanup.
- Confirm
PanGPS.exeexists and the PLAP registration process returns success. - Check that the intended registry values and portal are present in the expected registry view.
- Test the Windows sign-in experience and verify that the provider appears as expected.
- Test a device with no prior user sign-in, and one that is off the corporate network, to confirm portal and gateway reachability and authentication behavior.
- Test relevant certificate conditions, including a missing or expired certificate if machine-certificate authentication is part of the design.
- Restart when required by the MSI, then verify the pre-logon tunnel and SCCM’s final installed status.
Troubleshoot deployment and connection failures
PanGPS.exe is missing
Check the verbose MSI log first. The MSI may have failed, the package architecture may be wrong, the installation path may differ, or the wrapper may not have waited for installation to finish. The sample checks both Program Files locations; confirm the actual path on the affected release and do not continue configuration when the executable is absent.
Best Value

- 【Rapid OpenVPN & Wireguard Speed】Wireguard VPN and OpenVPN both deliver speeds of up to 1100 Mbps, giving you complete control over your gaming, streaming and working bandwidth. Actual speed may differ depending on internet service provider, network environment, VPN server location, VPN service provider, etc.
- 【Extensive Coverage】Experience seamless Wi-Fi connection throughout your home and workplace with performance designed for extra long range WiFi, modern connectivity. This advanced router system delivers strong, reliable signal strength for up to 2,500 square feet of coverage.
- 【Mass device connectivity】Experience enhanced online connectivity with our higher storage capacity, catering to over a hundred devices and fulfilling the requirements of DIY users seeking to install additional plugins. Enjoy stable and reliable connections, ensuring seamless performance and accommodating a wide range of digital needs.
- 【MLO + 4K-QAM Breakthrough】Flint 3e represents the future of wireless router, delivering ultra-fast speeds, significantly reduced latency, and improved connectivity in high-density environments through cutting-edge innovations like Multi-Link Operation (MLO), enhanced OFDMA, 4K-QAM, preamble puncturing and Multi-RUs.
- 【AdGuard Home Supported】Enables the use of a DNS server for blocking unwanted tracking and offers a convenient web interface for filtering selected digital advertisements. Users can take full control of their online experience and enjoy a clutter-free browsing environment with ease.
PLAP registration fails or is absent at sign-in
Confirm the script ran with administrative rights, capture the process exit code, and test the registration command manually on a lab device using the installed version. Check for incomplete prior installations and any required restart. PLAP registration is only one part of the sign-in workflow; also validate portal policy, gateway configuration, authentication, certificates, and pre-sign-in connectivity.
Configuration Manager retries or reports the app as not installed
Compare detection logic with the values the installer actually writes. Common mismatches include checking CBLPortal1 when deployment writes PanSetupPortal, a different portal string, registry-view differences, or an MSI product code from another release. Review AppDiscovery.log for application evaluation and AppEnforce.log for install enforcement. Microsoft’s references cover application installation logs and deployment evaluation logs.
The package installs but the VPN does not connect before logon
Separate endpoint deployment from network and policy troubleshooting. Verify the portal hostname, portal agent configuration and ordering, gateway support, machine authentication, required certificate or other credentials, DNS resolution, and reachability before user sign-in. Palo Alto’s pre-logon guide discusses portal and gateway configuration and the pre-deployed portal case for endpoints that have not previously connected.
The deployment works interactively but not through SCCM
Configuration Manager runs in a different context from a signed-in administrator: it may use SYSTEM, a different PowerShell bitness, no user profile, and different network access. Test the script and detection in the actual deployment context, confirm registry-view behavior, and use logs rather than relying on an interactive run.
When a wrapper is worth maintaining
A native MSI deployment is simpler when the MSI properties and detection requirements are sufficient. A PowerShell wrapper is useful when the deployment must sequence MSI installation, PLAP registration, explicit registry writes, error handling, and custom detection. A deployment framework such as PSAppDeployToolkit may suit organizations that already standardize on it, but it is not required for this task; the forum mentions it as one approach in a particular environment. See the PSAppDeployToolkit project.
Use the endpoint-management platform already in production. Microsoft Configuration Manager is appropriate where it is deployed and managing Windows devices. Intune Win32 app deployment is an alternative for cloud-managed or co-managed endpoints, but it uses a different packaging and detection workflow. Licensing and suitability depend on the organization’s agreements and management model.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




