What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Versions 2.1 and earlier of mySCADA myPRO Manager are affected by two separate access-control failures. CVE-2026-73807 lets an unauthenticated attacker with network access reach privileged management functions through the command API. CVE-2026-82567 lets an unauthenticated caller send SMS messages through a GSM modem connected to the software. mySCADA Technologies fixed both in version 2.2, and the advisory recommends updating to the latest release.
Which installations are affected
The affected product is mySCADA myPRO Manager, versions 2.1 and earlier. Version 2.2 addresses both issues. Any installation running 2.1 or an older build should be treated as exposed until it is updated. The advisory does not break the range down by operating system, deployment type or hardware, so the version number is the only reliable test.
As an Amazon Associate I earn from qualifying purchases.
To check your version, open the application’s information or about screen in your installation, or read the version from the installed package. If you cannot find it, check the update status inside the application, since a connected instance will show whether an update is available.
The two flaws
Both vulnerabilities are missing-control problems, but they sit in different parts of the software and produce different outcomes. They should be assessed separately.
#1 Best Overall

- DEVICE INTERFACE: 5 x 10/100Mbps Ports; 4-Pin Removable Terminal Block; LED Indicators
- TRENDnet LIFETIME PROTECTION: We stand by our products. The TI-E50 5-Port Industrial Switch is secured with Lifetime Manufacturer Protection from TRENDnet.
- NDAA + TAA COMPLIANT: With our NDAA and TAA compliant Industrial switches, you can plan and install networking solutions that Government customers demand today (U.S. and Canada Only)
- RELIABLE TECH SUPPORT: Our team of advisors, support and tech experts are English speaking, and available for all your needs during normal business hours. We take pride in being there for our customers.
- FAST ETHERNET PORTS: This industrial hardened switch features five 10/100Mbps ports for high-speed device connections up to 200Mbps full-duplex per port with 1Gbps total switching capacity.
CVE-2026-73807: privileged command API without authorization
The myPRO Manager command API does not properly enforce authentication for privileged functions. An unauthenticated attacker with network access to the affected API could reach privileged management functions. The advisory classifies the weakness as CWE-862 (Missing Authorization). It scores the flaw CVSS 3.1 9.8 (Critical), with the vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, and CVSS 4.0 9.3 (Critical).
This is the more serious of the two. The vector means no privileges and no user interaction are needed, and the impact is rated high for confidentiality, integrity and availability. Because the problem is in management functions rather than a single feature, the practical risk depends on what those functions can change in your deployment.
CVE-2026-82567: unauthenticated SMS through the notification gateway
The second flaw is a separate missing-authentication issue in the software’s HTTP notification gateway. The exposed endpoint accepts a destination phone number and a message body without authentication. When this happens, a GSM modem connected to the software can be made to send the SMS. The advisory rates it CVSS 3.1 6.3 (Medium). No CVSS 4.0 score or CWE classification is stated for this entry in the material reviewed.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #2
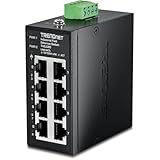
- DEVICE INTERFACE: 8 x 10/100Mbps Ports; 4-Pin Removable Terminal Block; LED Indicators
- ULTRA MINI HOUSING: Industry leading compact mini housing design. One of the smallest switches in the industry with dimensions of 3.34” x 3.14” x 1.53” allow for space saving installation nearly anywhere.
- NDAA + TAA COMPLIANT: With our NDAA and TAA compliant Industrial switches, you can plan and install networking solutions that Government customers demand today (U.S. and Canada Only)
- RELIABLE TECH SUPPORT: Our team of advisors, support and tech experts are English speaking, and available for all your needs during normal business hours. We take pride in being there for our customers.
- FAST ETHERNET PORTS: This industrial hardened switch features eight 10/100Mbps ports for high-speed device connections up to 200Mbps full-duplex per port with 1Gbps total switching capacity.
The advisory describes this flaw as arbitrary SMS transmission. It does not describe control of the industrial process through this endpoint. That distinction matters for triage: the immediate impact is unauthorized messages sent from your modem, which can still be harmful, for example through spam, fraud, or misleading alerts sent to operators, but it is a different class of consequence from the command API flaw.
Side-by-side comparison
| Item | CVE-2026-73807 | CVE-2026-82567 |
|---|---|---|
| Affected component | myPRO Manager command API | HTTP notification gateway |
| Missing control | Authentication enforcement for privileged functions (authorization) | Authentication on the endpoint that accepts a phone number and message |
| Attacker outcome | Access to privileged management functions | Arbitrary SMS sent through the connected GSM modem |
| CWE | CWE-862 (Missing Authorization) | Not stated in the advisory material reviewed |
| CVSS 3.1 | 9.8 (Critical) | 6.3 (Medium) |
| CVSS 4.0 | 9.3 (Critical) | Not stated in the advisory material reviewed |
| Fixed in | Version 2.2 | Version 2.2 |
What can happen if these vulnerabilities are exploited
The CISA advisory summarizes the outcome in one sentence: successful exploitation “could allow an attacker to access privileged management functions or send arbitrary SMS messages through the connected GSM modem.”
In operational terms, the first outcome means an attacker who reaches the command API may be able to use management functions that an authorized operator would normally control. The second means an attacker can use the modem as an outbound messaging channel. If your installation has the modem connected and the gateway reachable from a network the attacker can access, both outcomes are possible on the same host. Patching one does not remove the other, so both must be closed by the same version update.
Rank #3
- 10/100/1000Mbps Ethernet – The Industrial 5 ports Ethernet Switch have 5 RJ45 ports 10/100/1000Mbps half/full duplex.
- Small Size – The 5 ports Ethernet Switch size is 3.74x2.76x1.18in, it only need small space to install.
- ELECTRO MAGNETIC COMPLIANT & Surge Protection – Industrial DIN-rail switch complies with CE EN 55022 Class A standards, with surge protection design.
- Industrial Grade Quality – The Hardened Mini Gigabit Switch use industrial grade components and aluminum housing, it can work at wide range temperature -40°C to 75°C (-40°F to 167°F). You can use it in outdoor harsh environment.
- Din-Rail & Wall Mount –The media converter come with 35mm Din-rail Clip and Wall mount accessories.
How to fix it
The vendor’s remedy is to update to version 2.2 or later. The advisory names the update path for each type of installation:
- Identify every myPRO Manager instance and record its version. Anything at 2.1 or earlier is in scope.
- For instances that are online and connected, watch for the in-app update notification and apply the update it offers.
- For instances that are disconnected from the internet, obtain the software from the vendor download page on the mySCADA website and install version 2.2 or later.
- After updating, confirm the version again. A notification that was dismissed or deferred does not mean the update was applied.
Until an instance is updated, the advisory’s guidance does not cover interim controls, so the following is general hardening rather than vendor instruction. Remove the command API and notification gateway from any network that does not need them, and do not expose either to the internet. Disconnect the GSM modem if SMS notifications are not needed while the system is unpatched. Review logs for unexpected SMS activity or unexpected management actions where your logging allows it.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Where these products are used
The advisory lists critical manufacturing, energy, food and agriculture, transportation systems, and water and wastewater as sectors where the software is deployed, with deployments described as worldwide. These are the sectors the advisory cites. They are not a count of vulnerable organizations or systems, and the material reviewed does not provide one.
Rank #4

- DEVICE INTERFACE: 8 x Gigabit Ports; 3-Pin Removable Terminal Block; LED Indicators
- ULTRA MINI HOUSING: Industry leading compact mini housing design. One of the smallest switches in the industry with dimensions of 3.93” x 3.16” x 1.53” allow for space saving installation nearly anywhere.
- NDAA + TAA COMPLIANT: With our NDAA and TAA compliant Industrial switches, you can plan and install networking solutions that Government customers demand today (U.S. and Canada Only)
- RELIABLE TECH SUPPORT: Our team of advisors, support and tech experts are English speaking, and available for all your needs during normal business hours. We take pride in being there for our customers.
- GIGABIT PORTS: This industrial network Ethernet switch features eight copper gigabit ports for high-speed device connections
What is not established
The sources reviewed for this article do not establish whether either vulnerability is being exploited in the wild, whether public proof-of-concept code exists, or how many internet-reachable or otherwise exposed installations are running a vulnerable version. Treat the severity scores as a measure of the flaw’s potential, not as evidence of an active attack. The CISA advisory is the primary reference for the affected range and remediation, and readers should check it directly for any update, because mirrored copies can lag the official page.
Sources: CISA advisory ICSA-26-258-03 (indexed copy) and the CSIRTS advisory record for mySCADA myPRO Manager.
Free tools Windows power users keep installed
One-click scans. No signup required.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

