Freedom251 › Public Key Infrastructure Software
XiPKI
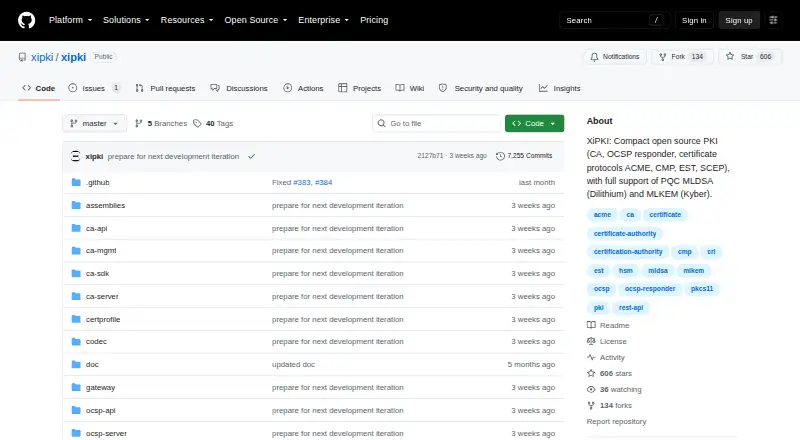
What XiPKI is
XiPKI is a free, open-source public key infrastructure system for certification authority, registration authority and OCSP responder functions, intended for critical infrastructure. It can manage multiple CAs in one instance, database clusters and active instances for the same CA. Its CA gateway supports EST, SCEP, CMP, ACME and its own RESTful API. The OCSP responder handles signed and unsigned requests, health checks and several certificate status sources.
HSM connections use PKCS#11, with devices including AWS CloudHSM, Nitrokey, nCipher, Sansec, SoftHSM, TASS, Thales and Utimaco listed. The project describes native support for ML-DSA, ML-KEM and composite post-quantum algorithms. Supported platforms are Linux and macOS, with Java 11 or later and Tomcat 10 or 11 required. Listed databases include DB2, MariaDB, MySQL, Oracle, PostgreSQL, H2 and HSQLDB. XiPKI is available under Apache License 2.0; setup archives can be obtained from GitHub Releases or Maven Central, or built from source.
Who it suits
XiPKI suits organisations needing CA, registration authority or OCSP functions, including critical infrastructure operators. It is aimed at teams able to run it on Linux or macOS with Java 11 or later and Tomcat 10 or 11.
What it does well
- Supports EST, SCEP, CMP and ACME protocols.
- Manages multiple CAs in one instance.
- PKCS#11 HSM integration covers a range of listed devices.
- Free and licensed under Apache License 2.0.
What to know first
- Requires Java 11 or later.
- Requires Tomcat 10 or 11.
- Supported operating systems are Linux and macOS.
Limits
The listed operating requirements are Linux or macOS, Java 11 or later, and Tomcat 10 or 11; supported databases are DB2, MariaDB, MySQL, Oracle, PostgreSQL, H2, and HSQLDB.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Apache License 2.0 | Open-source software under Apache Software License, Version 2.0 | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Download the setup archive from GitHub Releases or Maven Central, or build XiPKI from source.
- Prepare a Linux or macOS environment with Java 11 or later and Tomcat 10 or 11.
- Choose a supported database for the deployment.
- Configure CA management through embedded OSGi commands or an API.
XiPKI is open-source infrastructure software for operating certificate authorities, registration authorities, and OCSP responders. It is best suited to teams that need control over a broad, self-hosted PKI stack; its protocol and HSM breadth stand out, but deployment and upkeep call for Java and database expertise.
Overview
XiPKI brings CA, RA, and OCSP services together, with multiple CAs in one instance, clustered databases, and active instances for a CA. That combination suits organizations consolidating certificate operations or planning for availability. Administration through embedded OSGi commands and an API adds flexibility, though this remains infrastructure to operate rather than a managed certificate service.
The CA gateway handles EST, SCEP, CMP, ACME, and XiPKI’s RESTful API. This range accommodates different enrollment environments without limiting the system to one protocol. Native support for ML-DSA, ML-KEM, and composite post-quantum algorithms is a further reason to consider it for teams planning cryptographic transitions.
Key features
CA operations and enrollment
Multiple authorities and active instances support more involved deployments than a single-CA setup. Database clustering can support a resilient architecture, while API and OSGi-based administration give operators more than one management path. These options reward teams with PKI operations experience; they also bring configuration and maintenance responsibility.
Support for EST, SCEP, CMP, ACME, and the project’s REST API makes XiPKI adaptable to varied enrollment clients. Its post-quantum algorithms broaden its cryptographic choices, but teams still need to determine which algorithms and deployment configuration fit their own requirements.
OCSP, HSM, and compliance
The OCSP responder supports RFC 2560 and RFC 6960, the high-volume profile in RFC 5019, signed and unsigned requests, health checks, and several certificate status sources, including EJBCA databases. That breadth is useful for organizations integrating status checking into existing certificate operations.
PKCS#11 connects XiPKI with HSMs from AWS CloudHSM, Nitrokey, nCipher, Sansec, SoftHSM, TASS, Thales, and Utimaco. Bouncy Castle can be switched between LTS and FIPS variants, and the project lists support for eIDAS standards EN 319 411 and EN 319 412. These options help address different security and compliance needs, but do not remove the work of selecting and operating an appropriate environment.
Pricing
XiPKI is free open-source software under the Apache License 2.0: free. There are no paid tiers or plan-based feature reductions described. The trade-off is operational rather than a subscription fee: adopters run and maintain the software and its dependencies themselves.
Platforms
XiPKI is self-hosted and supports Linux and macOS, with Java 11 or later and Tomcat 10 or 11 required. Supported databases are DB2, MariaDB, MySQL, Oracle, PostgreSQL, H2, and HSQLDB. This selection gives organizations options to fit an existing database environment, but the runtime stack makes it a poor fit for teams seeking a turnkey or managed deployment.
The setup archive can be obtained from GitHub Releases or Maven Central, or built from source. For support, the project directs users to GitHub issues and asks bug reports to include test data, logs, version, operating system, JRE or JDK, and reproduction steps; teams should be prepared to provide a useful technical report when seeking help.
Who it's for
XiPKI is a strong candidate for infrastructure and security teams that need a full CA, RA, and OCSP system, several enrollment protocols, HSM options, or post-quantum algorithms, and have the skills to run Java-based on-premises services. Teams that need a managed certificate product, or cannot take responsibility for the runtime and database stack, should look elsewhere.
Pros and cons
- Pros: CA, RA, and OCSP functions in one system, with multiple CAs, clustered databases, and active instances for a CA.
- Pros: Broad protocol support, including EST, SCEP, CMP, and ACME, plus native post-quantum algorithm support.
- Pros: PKCS#11 HSM integration and support for a broad range of named devices.
- Cons: Linux or macOS, Java, Tomcat, and a supported database are required, adding deployment and maintenance work.
- Cons: Self-hosted operation and issue-based support suit technical teams better than buyers seeking a managed service.
Alternatives
For a wider comparison, see Public Key Infrastructure Software.
- OpenCA PKI is another free open-source PKI option for Linux, macOS, self-hosted, or web use.
- step-ca is a free option if a single configured intermediate CA, an offline root CA, and authority-wide issuance policies better match the deployment.
- EJBCA offers a free Community Edition for basic PKI learning, testing, and prototyping, rather than production use.
- OpenXPKI may suit teams looking for a free community edition with Debian packages, example configuration, documentation, and mailing-list support.
- Boulder is a free option when its MPL-2.0 license fits, provided the adopter can handle the separate implementation and security work required for production.
- cert-manager is the more focused choice for X.509 certificate management for Kubernetes and OpenShift workloads.
- Dogtag Certificate System is another free certificate authority option, with a requirement for access to 389 Directory Server.
- SecureW2 Cloud NAC is a paid alternative for buyers who prefer to request a quote for a solution priced around their needs.
Verdict
Choose XiPKI if your team needs a versatile self-hosted PKI with broad enrollment protocols, CA and OCSP coverage, HSM integration, and post-quantum options. Its strongest case is the breadth of capabilities in a free package; its chief drawback is the technical ownership required to deploy and maintain the stack. Teams seeking managed operations or a narrower workload-specific tool should compare alternatives.
Verdict
XiPKI covers CA, registration and OCSP functions, with protocol, database and HSM options. Its listed runtime requirements and operating systems are important considerations before deployment.
Questions
How much does XiPKI cost?
XiPKI is available for free under Apache License 2.0.
Which platforms does XiPKI support?
The project lists Linux and macOS, with Java 11 or later and Tomcat 10 or 11 as requirements.
Which certificate protocols does XiPKI support?
Its CA protocol gateway supports EST, SCEP, CMP, ACME, and XiPKI's own RESTful API.
Can XiPKI integrate with HSMs?
Yes. It supports HSM integration through PKCS#11 and lists devices including AWS CloudHSM, Nitrokey, nCipher, Sansec, SoftHSM, TASS, Thales, and Utimaco.
Which databases can XiPKI use?
The supported databases listed by the project are DB2, MariaDB, MySQL, Oracle, PostgreSQL, H2, and HSQLDB.
Where can I get XiPKI?
The setup archive is available from GitHub Releases or Maven Central, and the project can also be built from source.
Facts from XiPKI's own pages
- CA management
- XiPKI supports multiple CAs in one software instance, database clusters, active instances for the same CA, and CA management through embedded OSGi commands and an API. · github.com, 4 Oct 2026
- Certificate protocols
- Its CA protocol gateway supports EST, SCEP, CMP, ACME, and XiPKI's own RESTful API. · github.com, 4 Oct 2026
- Database support
- Supported databases listed are DB2, MariaDB, MySQL, Oracle, PostgreSQL, H2, and HSQLDB. · github.com, 4 Oct 2026
- Downloads
- The setup archive can be downloaded from GitHub Releases or Maven Central, or built from source. · github.com, 4 Oct 2026
- HSM integrations
- It supports HSM integration through PKCS#11 and lists AWS CloudHSM, Nitrokey, nCipher, Sansec, SoftHSM, TASS, Thales, and Utimaco devices. · github.com, 4 Oct 2026
- Latest release
- The releases page lists v6.7.1 as the latest release, dated 2026/09/07. · github.com, 4 Oct 2026
- Maker
- The GitHub account identifies the project author as Lijun Liao, PhD, and lists Germany as the location. · github.com, 4 Oct 2026
- OCSP
- The OCSP responder supports RFC 2560 and RFC 6960, the lightweight high-volume profile in RFC 5019, signed and unsigned requests, health checks, and several certificate status sources including EJBCA databases. · github.com, 4 Oct 2026
- Operating requirements
- The project lists Linux and macOS, Java 11 or later, and Tomcat 10 or 11 as supported platform requirements. · github.com, 4 Oct 2026
- Post-quantum cryptography
- The project describes native support for ML-DSA, ML-KEM, and composite post-quantum algorithms. · github.com, 4 Oct 2026
- Purpose
- XiPKI is an open-source public key infrastructure system covering certification authority, registration authority, and OCSP responder functions, intended for critical infrastructure. · github.com, 4 Oct 2026
- Security and compliance
- The project says Bouncy Castle can be switched between LTS and FIPS variants to meet different compliance requirements, and lists eIDAS standards EN 319 411 and EN 319 412 support. · github.com, 4 Oct 2026
- Support
- The project directs users to open a GitHub issue and asks bug reports to include test data, logs, version, OS, JRE or JDK, and reproduction steps. · github.com, 4 Oct 2026