Freedom251 › Public Key Infrastructure Software
OpenCA PKI
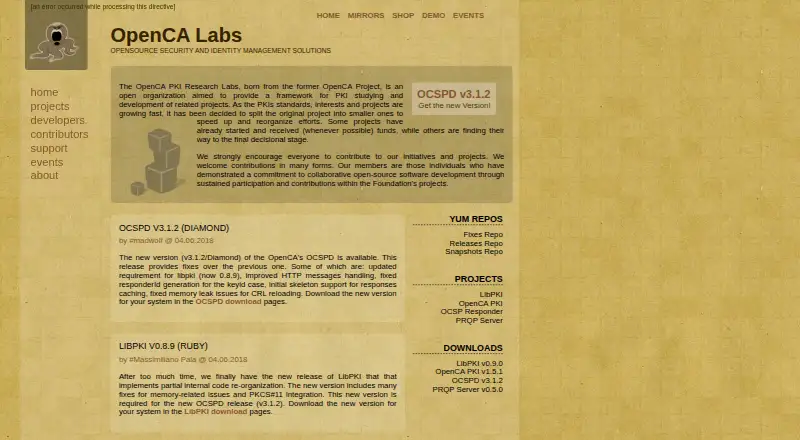
What OpenCA PKI is
OpenCA PKI is open-source software for establishing and managing a public key infrastructure, with a Certification Authority intended to be ready to set up. It is designed for on-premises deployment and listed for Linux, macOS, self-hosted, and web environments. The project says it implements commonly used protocols with full-strength cryptography; listed capabilities include SCEP support, HSM integration, and certificate profiles. The download page lists OpenCA PKI (SpecialK) version 1.5.1. Setup has prerequisites: OpenLDAP, OpenSSL, Apache, and Apache mod_ssl are among the required software, and OpenCA Tools version 1.3.0 should be installed first. The project dates to 1998 and is volunteer-driven, with collaborative, consensus-based management. Community support is available through mailing lists, forums, and online chat; independent third parties offer paid support. Security issues can be reported privately by email or publicly through the project issue trackers. Downloadable documentation is unavailable, and the project describes its OpenCA Guide for version 0.9.2 as outdated in some parts. The plan is free.
Who it suits
It suits teams setting up an on-premises PKI that can meet its software prerequisites. It may also suit users who want SCEP, HSM integration, and certificate profiles.
What it does well
- Free plan listed as free
- Supports SCEP and HSM integration
- Community support via mailing lists, forums, and chat
- Accepts private and public vulnerability reports
What to know first
- Requires several software dependencies
- OpenCA Tools 1.3.0 should be installed first
- Downloadable documentation is unavailable
- The version 0.9.2 guide is outdated in parts
Limits
The listed plan is free. The documentation page says downloads are unavailable and parts of the OpenCA Guide for version 0.9.2 are outdated.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| OpenCA PKI | Open source PKI management software · Version 1.5.1 listed | Free |
As openca.org lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Install OpenCA Tools version 1.3.0 first.
- Prepare OpenLDAP, OpenSSL, Apache, and Apache mod_ssl.
- Download OpenCA PKI (SpecialK) version 1.5.1 from the project website.
- Deploy it on premises in a listed Linux, macOS, self-hosted, or web environment.
- Use mailing lists, forums, or online chat for community support.
OpenCA PKI is open-source software for running a certificate authority and managing a public key infrastructure on premises. It best suits technically capable teams that need control over their own PKI; the free price is attractive, but setup prerequisites and thin, partly outdated documentation raise the cost of operating it.
Overview
Developed since 1998, OpenCA PKI is intended as an out-of-the-box foundation for establishing and managing a certification authority. The project says it implements commonly used protocols with full-strength cryptography. Its current listed release is OpenCA PKI (SpecialK) 1.5.1.
On-premises deployment gives an organization responsibility for its own environment rather than placing the authority in a hosted service. That control requires a supporting stack: OpenCA names OpenLDAP, OpenSSL, Apache and Apache mod_ssl as prerequisites, and OpenCA Tools 1.3.0 should be installed before OpenCA PKI. Teams without the capacity to install and maintain these components should look elsewhere.
Key features
OpenCA combines certification-authority operation with PKI management. SCEP support, HSM integration and certificate profiles make it relevant to deployments that need those capabilities under local control. These are useful building blocks, but they do not remove the work of managing the underlying software.
The project accepts private vulnerability reports by email and public reports through the OpenCA and OpenCA-Tools issue trackers. Community support runs through mailing lists, forums and online chat; independent third parties also offer paid support. That gives users ways to seek help, though teams needing a defined vendor support relationship may prefer a commercial option.
Documentation is a material drawback. Downloadable documentation is unavailable, and the OpenCA Guide for version 0.9.2 is described as outdated in some parts. An older 2008 release announcement mentions elliptic-curve support, automatic certificate and CRL issuance through online engines, and a graphical installer for binary distributions; those historical notes should not be treated as confirmation of current-release behavior.
Pricing
OpenCA PKI is free: the OpenCA PKI plan is free and covers open-source PKI management software, with version 1.5.1 listed. There are no paid tiers or free-plan caps given. The zero price makes evaluation accessible, but does not eliminate the effort of installing and maintaining the required components. Paid support from independent third parties may be an option for organizations that need additional help.
Platforms
OpenCA PKI is listed for Linux, macOS, web and self-hosted use. Its on-premises deployment model makes it a fit for teams operating their own infrastructure, rather than those looking for a managed certificate authority.
Who it's for
Choose OpenCA PKI if your organization wants a free, self-managed certification authority with SCEP, HSM integration and certificate profiles, and can take responsibility for its prerequisites and upkeep. It is a weaker fit for teams that need current, downloadable guidance or a polished, low-maintenance setup path.
Pros and cons
- Pro: Free, open-source PKI management keeps software licensing cost at zero.
- Pro: On-premises deployment, SCEP support, HSM integration and certificate profiles suit organizations seeking local control and these specific capabilities.
- Con: OpenLDAP, OpenSSL, Apache, Apache mod_ssl and OpenCA Tools must be accounted for, increasing setup and maintenance demands.
- Con: Downloadable documentation is unavailable, while the guide for version 0.9.2 is outdated in parts.
- Con: Support is community-based, with paid help coming from independent third parties rather than a stated project-run support plan.
Alternatives
Public Key Infrastructure Software is the broader category to browse if you want to compare more PKI tools.
Choose step-ca instead if you want free, self-hosted software available across Linux, macOS, Windows and API platforms, with a single configured intermediate CA, an offline root CA and authority-wide issuance policies; its open-source plan has no Certificate Transparency integration.
XiPKI is another free, open-source option for Linux, macOS, self-hosted and API environments.
Consider Boulder if you want free, open-source software for API, Linux or self-hosted environments and can take on the separate implementation and security work required for production deployment.
SecureW2 Cloud NAC is a paid alternative with Android, iOS, Linux, macOS, Windows, web and API platform listings; pricing is by quote.
If you need S/MIME on-premises service with a free trial, KeyTalk CKMS offers a plan at €5 a month, billed per user, for up to 250 participants.
Cloudflare Serverless Registry is a free alternative whose registry has no separate price listed, with R2 usage-based charges for storage and operations.
Entrust Certificate Manager is a paid option with pricing obtained by talking with Entrust experts.
HashiCorp Nomad is a freemium alternative with a free plan and self-managed enterprise plans at custom pricing.
Verdict
OpenCA PKI is a sound candidate for technically equipped organizations that want a free certification authority under their own operational control. Its strongest case is the combination of on-premises deployment and PKI capabilities without a software price; its main reason to look elsewhere is the installation burden compounded by limited, partly outdated documentation.
Verdict
OpenCA PKI provides a free, on-premises certificate authority with listed PKI capabilities and community support. Plan for its dependencies and limited documentation when evaluating setup.
Questions
How much does OpenCA PKI cost?
The listed OpenCA PKI plan is free.
What does OpenCA PKI do?
It provides an out-of-the-box Certification Authority for setting up and managing a PKI.
Which platforms are listed?
Linux, macOS, self-hosted, and web environments are listed. Its deployment model is on premises.
Is OpenCA PKI open source?
Yes. The project describes OpenCA PKI as open source software.
What software is needed before installation?
OpenLDAP, OpenSSL, Apache, and Apache mod_ssl are among the named requirements. OpenCA Tools version 1.3.0 should be installed before OpenCA PKI.
What support is available?
Community support is available through mailing lists, forums, and online chat. Independent third parties offer paid support.
Facts from OpenCA PKI's own pages
- Access control
- The system documents channel verification, login, session management and ACL configuration. · openca.org, 15 Oct 2026
- Automatic revocation
- The 1.5.0 changelog records an auto-revocation daemon and automatic CRL processing. · openca.org, 15 Oct 2026
- CA management
- The software provides a complete certification-authority management solution. · openca.org, 15 Oct 2026
- Certificate requests
- Users can submit PKCS#10 certificate-signing requests through the web interface or SCEP. · openca.org, 15 Oct 2026
- Certificate revocation
- The user and administrator workflows include certificate revocation and CRL handling. · openca.org, 15 Oct 2026
- Current listed release
- The download page lists OpenCA PKI (SpecialK) version 1.5.1. · openca.org, 4 Oct 2026
- Database support
- The guide documents PostgreSQL, MySQL, Oracle and DBM database back ends. · openca.org, 15 Oct 2026
- Dependencies
- The project names OpenLDAP, OpenSSL, Apache, and Apache mod_ssl among the required software. · openca.org, 4 Oct 2026
- Developer API
- The related LibPKI project offers a high-level cryptographic API for applications handling keys, certificates and other PKI data. · github.com, 15 Oct 2026
- Distributed design
- The architecture separates CA, RA, LDAP and public interfaces into nodes suitable for hierarchical deployments. · openca.org, 15 Oct 2026
- Documentation depth
- The guide spans design, installation, configuration, user workflows and a technology guide, but the documentation page warns that much of it is outdated. · openca.org, 15 Oct 2026
- Documentation limitation
- The project says no current downloadable documentation is available and directs users to package contents and mailing lists. · openca.org, 15 Oct 2026
- Documentation limits
- The documentation page says downloadable documentation is unavailable and that the OpenCA Guide for version 0.9.2 is outdated in some parts. · openca.org, 4 Oct 2026
- Download versions
- The official download page lists OpenCA PKI 1.5.1 and separate packages for OpenCA Tools, LibPKI, OCSPD and PRQP Server. · openca.org, 15 Oct 2026
- Founded
- 1998 · openca.org, 28 Sept 2026
- Hardware tokens
- Configuration documentation covers OpenSSL, Luna, nCipher and OpenSC cryptographic tokens. · openca.org, 15 Oct 2026
- Independent platform description
- Wikipedia describes OpenCA as cross-platform free CA software with web-based certificate enrollment and management using OpenLDAP, OpenSSL and Apache. · de.wikipedia.org, 15 Oct 2026
- Independent version record
- The German Wikipedia entry records OpenCA PKI version 1.5.2 dated May 2014 and lists Linux, Unix and Mac OS X. · de.wikipedia.org, 15 Oct 2026
- Integrations
- Official dependencies and integrations include OpenLDAP, OpenSSL, Apache HTTP Server and Apache mod_ssl. · openca.org, 15 Oct 2026
- LDAP integration
- OpenCA uses OpenLDAP and documents publishing certificates and CRLs into LDAP directories. · openca.org, 15 Oct 2026
- License
- The OpenCA source license is an Apache-style permissive license with attribution and trademark conditions. · github.com, 15 Oct 2026
- Limit: complexity
- LinuxFr discussion participants characterized OpenCA and comparable full PKI suites as excessive for simple personal certificate use. · linuxfr.org, 15 Oct 2026
- Limit: perceived maintenance
- A LinuxFr commenter in 2013 described OpenCA as seemingly unmaintained and possibly nonfunctional in the tested version. · linuxfr.org, 15 Oct 2026
- Maker history
- The project guide traces OpenCA's start to 1998, when the founders sought a complete PKI solution without per-certificate licensing costs. · openca.org, 15 Oct 2026