Freedom251 › Infrastructure Policy as Code Tools
Tirith
What Tirith is
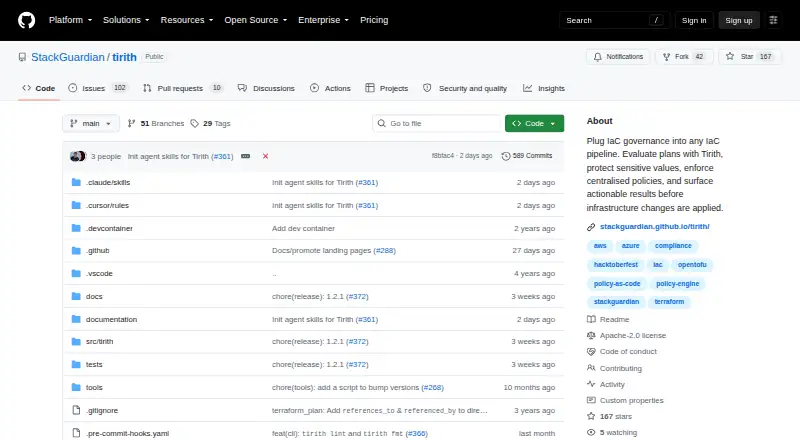
Tirith is a free, open-source command-line tool for evaluating infrastructure documents against declarative JSON policies. It reports passed and failed rules together with the affected resource and value. A pipeline gate checks Terraform plan output and can return a nonzero exit code when a policy violation appears, allowing a CI job to stop before changes are applied. Documented inputs include Terraform plans and state, Kubernetes manifests, Infracost breakdowns, and other JSON documents. Policies can use providers and evaluators such as ContainedIn, Equals, and RegexMatch, while the provider design supports extensions for other formats. Local evaluation runs on the user’s runner, with the project stating that policies and documents are not sent elsewhere. Optional StackGuardian organization mode evaluates against organization policies and uploads a masked document. Tirith can run through GitHub Actions, GitLab, Bitbucket Pipelines, other CI, or locally. OpenTofu plans work like Terraform plans for the documented gate.
Who it suits
Tirith is aimed at DevSecOps engineers, infrastructure architects, cloud administrators, and others enforcing infrastructure guardrails.
What it does well
- Checks Terraform plans before infrastructure changes
- Supports Kubernetes, Infracost, and JSON inputs
- Runs locally without sending policies or documents
- Integrates with several CI environments
- Includes policy lint and format commands
What to know first
- GitLab has no native action equivalent
- Organization mode uploads a masked document
- Interactive interface is optional beta
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Tirith (Apache-2.0) | Open-source CLI; no account required; optional StackGuardian organization mode | Free |
As github.com lists them, read 7 Oct 2026. The maker's own page has the final word.
Getting started
- Open the project website on GitHub.
- Use the CLI locally or in a container-based CI job.
- For GitHub Actions, follow the documented integration.
- For GitLab, invoke the CLI directly in a CI job.
- Optionally use StackGuardian organization mode for organization-enforced policies.
Verdict
Tirith provides policy evaluation and pipeline gating for infrastructure documents, with local execution and multiple CI routes. Teams using GitLab must invoke the CLI directly, and organization mode has different data handling from local mode.
Questions
How much does Tirith cost?
The listed plan is free. The CLI is open-source and does not require an account.
Which inputs does it support?
Documented inputs include Terraform plans and state, Kubernetes manifests, Infracost breakdowns, and other JSON documents. The maker also lists CloudFormation.
Can Tirith block a pipeline?
For Terraform plan output, it can return a nonzero exit code for a policy violation before infrastructure changes are applied.
Does it work with OpenTofu?
The maker says OpenTofu plans work like Terraform plans for the documented gate.
How does local evaluation handle sensitive documents?
In local mode, evaluation runs on the user's runner; the project says policies and documents are not sent elsewhere.
Does it have GitLab integration?
The CLI can be invoked directly in GitLab CI jobs. The maker says there is no GitLab-native action equivalent.
Facts from Tirith's own pages
- CI integrations
- The README documents a GitHub Actions integration and direct CLI use in GitLab or other container-based CI jobs. · github.com, 7 Oct 2026
- Headquarters
- Germany · github.com, 28 Sept 2026
- Intended users
- The project names DevSecOps engineers, infrastructure architects, cloud administrators, and others who manage or enforce infrastructure guardrails. · github.com, 7 Oct 2026
- Interactive interface
- The optional beta terminal interface provides an Explorer for results, a Builder for policies, and a Playground for examples; it can also be served in a browser. · github.com, 7 Oct 2026
- Maker and founding
- StackGuardian says it was founded in 2022. · stackguardian.io, 7 Oct 2026
- Notable limitation
- The maker says there is no GitLab-native action equivalent, so GitLab users invoke the CLI directly. · github.com, 7 Oct 2026
- OpenTofu
- The maker's site says OpenTofu plans work identically to Terraform plans for the documented gate. · stackguardian.github.io, 7 Oct 2026
- Organization mode
- The optional platform check evaluates plans against policies enforced by a StackGuardian organization and uploads a masked document to StackGuardian for evaluation. · github.com, 7 Oct 2026
- Other CI platforms
- The maker's site lists GitHub Actions, GitLab CI, Bitbucket Pipelines, any CI, and local CLI as ways to run Tirith. · stackguardian.github.io, 7 Oct 2026
- Pipeline gate
- It checks Terraform plan output and can return a nonzero exit code for a policy violation before infrastructure changes are applied. · github.com, 7 Oct 2026
- Policy features
- Policies can use providers and evaluators such as ContainedIn, Equals, and RegexMatch, and the provider architecture can be extended for other input formats. · github.com, 7 Oct 2026
- Policy maintenance
- The CLI includes lint and format commands, and both are published as pre-commit hooks. · github.com, 7 Oct 2026
- Purpose
- Tirith evaluates infrastructure documents against declarative JSON policies and reports which rules passed or failed, including the affected resource and value. · github.com, 7 Oct 2026
- Sensitive values
- In local mode, evaluation runs on the user's runner and the project says that policies and documents are not sent anywhere. · github.com, 7 Oct 2026
- Supported inputs
- The project documents support for Terraform plans and state, Kubernetes manifests, Infracost breakdowns, and other JSON documents. · github.com, 7 Oct 2026
Where Tirith stands on Freedom251
- Infrastructure Policy as Code Tools#17 of 25