Freedom251 › AI Security Testing Tools
RedForge
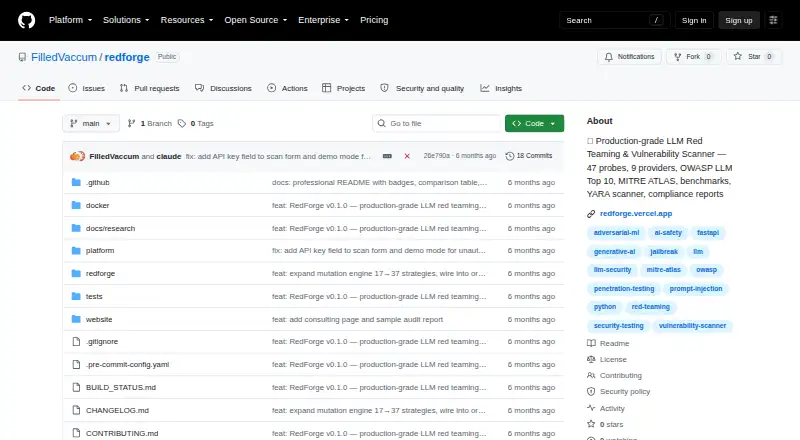
What RedForge is
RedForge is an open-source platform for red teaming and vulnerability scanning of large language models. It runs self-hosted on Linux and is also available through an API. The project lists more than 49 probes, full coverage of the OWASP LLM Top 10, and YAML-based probe additions that do not require Python. Its attack modules include PAIR, Crescendo multi-turn escalation, Skeleton Key, many-shot jailbreaking, and GCG adversarial suffixes. A mutation engine develops two payloads into 37 variants using encoding, Unicode, cognitive reframing, and structural injection strategies.
Adapters cover OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints. Ollama can run locally without an API key. Scan outputs include JSON, JSONL audit, and failures reports, with HTML, Markdown, SARIF, and other formats also supported. Compliance reports address NIST AI RMF, EU AI Act, ISO/IEC 42001, GDPR, and OWASP LLM Top 10; custom YAML frameworks can be added. The project is Apache 2.0 licensed, and probe payloads use CC0. The free RedForge plan costs nothing.
Who it suits
RedForge suits teams that need to scan LLMs they own or are authorized to assess, including teams connecting supported hosted or local model providers. Its SARIF export and CI failure status make it relevant to teams using GitHub Code Scanning or CI gates.
What it does well
- Lists 49+ probes and full OWASP LLM Top 10 coverage.
- Adds YAML probes without requiring Python.
- Supports local Ollama use without an API key.
- Produces SARIF and can gate CI on critical or high findings.
- Includes compliance reporting and custom YAML frameworks.
What to know first
- The CLI requires an authorization value for owned, authorized, or research use.
- The documented REST API rate limit is 10 scan requests per minute per client.
Limits
The free RedForge plan costs nothing. Its REST API allows 10 scan requests per minute per client.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| RedForge | Apache 2.0 open-source software · install with pip | Free |
As github.com lists them, read 9 Oct 2026. The maker's own page has the final word.
Getting started
- Open the RedForge GitHub repository.
- Install the software with pip or use the documented Docker deployment.
- Run it on Linux or configure a self-hosted deployment.
- Connect a supported model provider, or use Ollama locally without an API key.
- Provide the CLI authorization value for owned, authorized, or research use.
- Use SARIF output with GitHub Code Scanning or its documented GitHub Actions workflow.
Verdict
Choose RedForge if you need a self-hosted, open-source LLM security scanner with broad provider support, compliance reporting, and CI-oriented SARIF output. Its CLI is restricted to authorized or research use, and REST API clients are limited to 10 scan requests per minute.
Questions
Is RedForge free?
Yes. The RedForge plan is listed as free, and the project is open source under Apache 2.0.
Where can I run RedForge?
The listed platforms are API, Linux, and self-hosted. Docker instructions describe a non-root container with a read-only filesystem.
Which model providers does it support?
Adapters are listed for OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints.
Can RedForge test models locally?
Its Ollama adapter runs locally without an API key; the README describes this use as zero cost.
Does it integrate with GitHub Code Scanning?
Yes. RedForge can export SARIF for GitHub Code Scanning, and a GitHub Actions workflow uploads the SARIF file.
What authorization is required?
The CLI requires an authorization value indicating owned, authorized, or research use. The project says the tool is for authorized use only.
Facts from RedForge's own pages
- Attack methods
- Attack modules include PAIR, Crescendo multi-turn escalation, Skeleton Key, many-shot jailbreaking, and GCG adversarial suffixes. · github.com, 9 Oct 2026
- Attack modules
- Its attack modules include PAIR, Crescendo multi-turn escalation, Skeleton Key, many-shot jailbreaking, and GCG adversarial suffixes. · github.com, 9 Oct 2026
- CI integration
- RedForge can emit SARIF for GitHub Code Scanning and exits with status 1 on critical or high findings for use as a CI gate. · github.com, 9 Oct 2026
- Compliance
- Compliance reporting covers NIST AI RMF, EU AI Act, ISO/IEC 42001, GDPR, and OWASP LLM Top 10, and users can add custom YAML frameworks. · github.com, 9 Oct 2026
- Deployment
- The Docker instructions say the container runs as non-root user redforge (UID 1001) with a read-only filesystem. · github.com, 9 Oct 2026
- Detectors
- The README lists seven detector types, including YARA-style, similarity, refusal, regex, keyword, code, and unsafe-content detectors. · github.com, 9 Oct 2026
- Guardrails
- A bidirectional guardrail pipeline scans inputs and outputs for prompt injection, PII, toxicity, and secrets. · github.com, 9 Oct 2026
- Integrations
- It can export SARIF for GitHub Code Scanning and documents a GitHub Actions workflow that uploads the SARIF file. · github.com, 9 Oct 2026
- License
- The project is released under the Apache 2.0 license, and the README says probe payloads are released under CC0. · github.com, 9 Oct 2026
- License and use
- The repository identifies the license as Apache 2.0 and says the tool is for authorized use only. · github.com, 9 Oct 2026
- Local use
- The Ollama adapter runs locally without an API key, and the README describes it as zero cost. · github.com, 9 Oct 2026
- Model providers
- It lists adapters for OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints. · github.com, 9 Oct 2026
- Mutation engine
- The mutation engine expands two payloads to 37 variants across encoding, Unicode, cognitive reframing, and structural injection strategies. · github.com, 9 Oct 2026
- Probe coverage
- It lists 49+ probes and full OWASP LLM Top 10 coverage, with YAML probes that can be added without Python. · github.com, 9 Oct 2026
- Providers
- The README lists provider adapters for OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints. · github.com, 9 Oct 2026
- Purpose
- RedForge is an LLM security testing platform for red teaming and vulnerability scanning. · github.com, 9 Oct 2026
- Reports
- Scans automatically produce JSON, JSONL audit, and failures reports, with additional HTML, Markdown, SARIF, JSON, audit, and failures formats. · github.com, 9 Oct 2026
- Security controls
- Documented controls include masking API keys in logs, setting result files to mode 0600, bearer-token REST API authentication, disabled-by-default CORS, and a rate limit of 10 scan requests per minute per client. · github.com, 9 Oct 2026
- Usage requirement
- The CLI requires an authorization value indicating owned, authorized, or research use. · github.com, 9 Oct 2026
Where RedForge stands on Freedom251
- AI Security Testing Tools#19 of 29