Freedom251 › Penetration Testing Software
Pentesterra
What Pentesterra is
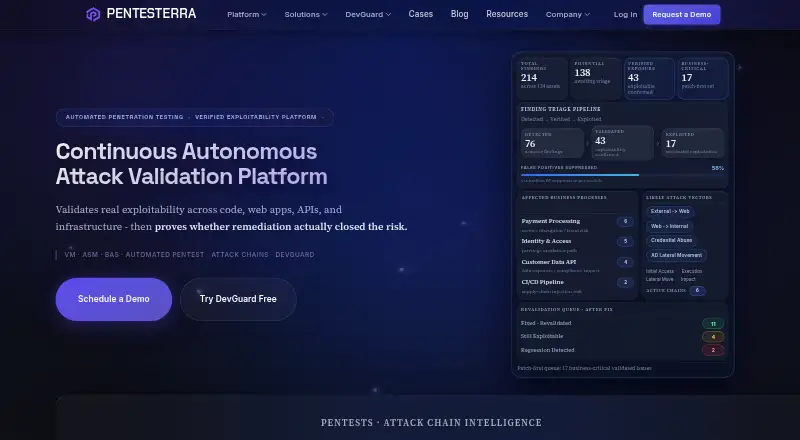
Pentesterra is a security orchestration platform that brings vulnerability management, automated network and web pentesting, breach and attack simulation, and AI-assisted exploit verification into a continuous workflow. It combines attack-surface mapping with breach simulation and controlled exploitation, prioritizing findings around evidence. Web testing covers modern web applications, single-page applications, and APIs through public or private proxies and Tor, including authentication flows, CSRF, JWT, and WAF evasion. Safe exploit validation uses real-world tools in non-malicious modes and is described as having no malware or ransomware. Attack Chain Analysis connects web, network, and DevGuard findings into directed kill-chain graphs, with up to 20 paths at depth five or less. Deployment options include SaaS, dedicated PaaS, and fully air-gapped on-premises installations. Verified findings can generate Jira tickets, and a REST API supports scan triggers, results retrieval, and reporting automation. The free DevGuard Free plan costs nothing and includes one project and three scans per month. Paid plans start at €23 a month.
Who it suits
Pentesterra is designed for internal security teams, MSSPs, and regulated environments. Its combination of vulnerability management, testing, and deployment choices may suit organizations that need to coordinate several security workflows.
What it does well
- Combines vulnerability management and security testing
- Supports web, SPA, API, and network testing
- Offers SaaS, dedicated PaaS, and air-gapped deployment
- Free DevGuard plan includes three scans monthly
- Enterprise plans include compliance evidence packages
What to know first
- Free plan is limited to one project
- Free plan allows three scans per month
- Enterprise pricing is custom
Limits
DevGuard Free includes one project and three scans per month. Vibe Coding at €23.00 per month includes three projects, 20 scans monthly, 300 dependencies per scan, 14-day raw data retention and limited network scanning.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| DevGuard Free | 1 project · 3 scans/mo · CLI, IDE plugin and web console · community support | Free |
| Team (SMB) | €1,299/ month · 100 network hosts · 20 web-pentest launches/week · 20 DevGuard projects · 140 scans/mo · 900 dependencies · 2 scanner nodes · internal scanning · gray/white-box, proxy and TOR support | €1,299 a month |
| Vibe Coding | €23/ month · 3 projects · 20 scans/mo · 300 dependencies/scan · 14-day raw-data retention · limited network scanning | €23 a month |
| Small Team | €299/ month · Full web pentest · 10 network hosts · 10 network launches/week · 12 DevGuard projects · 60 scans/mo · 4 reports/day and 10/week · limited CI/CD integration · SOC 2, ISO 27001, PCI DSS and NIST packs | €299 a month |
| Vibe Coding Pro | €75/ month · 5 projects · 40 scans/mo · 500 dependencies · 90-day retention · limited web pentest · 1 report/day and 4/week · performance scanner node | €75 a month |
| Enterprise | Custom · Unlimited modules, targets, nodes and seats · single-tenant or on-prem deployment · custom SLA · dedicated CSM · white-label and multi-tenant orchestration · SIEM hooks · API webhooks · SSO | On request |
As pentesterra.com lists them, read 15 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the Pentesterra website.
- Choose SaaS, dedicated PaaS or fully air-gapped on-premises deployment.
- Start with DevGuard Free for one project and three scans per month, or select a paid tier.
- For DevGuard, use the CLI, IDE plugin and web console included with the free plan.
- Use DevGuard's pre-built binary CLI for Linux, macOS Intel, macOS Apple Silicon or Windows, or its extensions for VS Code, Cursor or Windsurf.
Overview
Pentesterra is a security testing and vulnerability-management platform that connects assessment findings to attack paths and evidence. It is best suited to security teams managing several testing workflows or deployment environments; smaller users should weigh its firm scan and project caps against that breadth.
Key features
Its workflow combines vulnerability management and attack-surface mapping with breach simulation and controlled exploitation, using evidence-first prioritization. That joined-up approach is useful for teams that need to judge findings in context rather than work through disconnected scan queues.
Web testing covers modern applications, single-page apps and APIs, with public or private proxies and Tor, plus authentication flows, CSRF, JWT and WAF evasion. Safe exploit validation uses real-world tools in non-malicious modes and is described as avoiding malware and ransomware. These capabilities suit authorized testing that needs more than an unverified finding, but require clear scope and controls.
Attack Chain Analysis links web, network and DevGuard findings in directed kill-chain graphs, with up to 20 paths at depth five or less. Jira ticket creation for verified findings and a REST API for scans, results and reporting help connect assessment to follow-up work. Enterprise integrations add SIEM export in CEF or JSON, ServiceNow and Jira auto-ticketing, and SAML 2.0 or OIDC SSO. Enterprise evidence packages support SOC 2, ISO 27001, PCI-DSS and NIST CSF, with per-finding proofs of concept and delta reports.
Pentesterra states that it uses end-to-end encryption, isolated credential vaults, per-scope processing isolation and distributed scanner isolation. DevGuard does not send source code or raw secrets to the cloud; it sends metadata and redacted findings for analysis. Its CLI supports Linux, macOS Intel and Apple Silicon, and Windows, with extensions for VS Code, Cursor and Windsurf.
Pricing
The free DevGuard plan costs nothing and includes one project, three scans per month, CLI, IDE plugin and web console, with community support. It is a useful starting point, but the one-project and three-scan caps make it a limited fit for regular or multi-project work.
Vibe Coding costs €23/ month and allows three projects, 20 scans per month and 300 dependencies per scan, with 14-day raw data retention and limited network scanning. It suits light use where those quotas are enough. Vibe Coding Pro costs €75/ month: five projects, 40 scans monthly, 500 dependencies, 90-day retention, one report a day and four reports a week. Its higher quotas and retention suit more sustained work, though reporting remains capped.
Small Team costs €299/ month and includes full web app pentesting, 10 network hosts, 10 launches a week, 12 projects, 60 scans monthly and SOC 2, ISO 27001 and PCI DSS packs. It is the first listed tier with full web app pentesting, but its host and launch limits constrain broader testing. Team (SMB) costs €1,299/ month, with 100 network hosts, 20 web pentest launches a week, 20 projects, 140 scans monthly, 900 dependencies, two scanner nodes and internal network scanning. Those expanded limits fit larger operations, at a substantial step up in monthly cost.
Enterprise has custom pricing and offers all modules without limits, single-tenant or on-premises deployment, unlimited nodes, targets and seats, custom SLA, a dedicated customer success manager, white-label and multi-tenant orchestration, SIEM hooks, API webhooks and SSO. The licensing matrix lists 24x7 support for VM, ANPT, BAS, Web pentesting, MSSP and GOV tiers.
Platforms
Pentesterra supports API, browser extension, Linux, macOS, self-hosted, web and Windows deployments. SaaS, dedicated PaaS and fully air-gapped on-premises options make it relevant to organizations with different infrastructure and isolation needs.
Who it's for
Internal security teams, MSSPs and regulated environments are the stated audience. Teams that need connected vulnerability management, web and network testing, breach simulation and evidence packages can make use of its breadth. Individuals or small teams with low scan volumes may find the free or entry paid caps workable; those needing frequent scans, extensive network coverage or unlimited seats and targets should consider higher tiers. It is less compelling if only a single, narrow testing function is needed.
Pros and cons
Pros
- Brings vulnerability management, attack mapping, simulation and controlled exploitation into one workflow, helping teams prioritize connected risks.
- Offers SaaS through air-gapped on-premises deployment, including dedicated PaaS for organizations needing a deployment between those options.
- Enterprise integrations and compliance evidence can connect verified findings to ticketing, SIEM and audit work.
- DevGuard keeps source code and raw secrets out of cloud analysis, sending metadata and redacted findings instead.
Cons
- Free DevGuard is limited to one project and three scans monthly, so it is not a broad ongoing assessment tier.
- Paid plans impose project, scan, dependency, host, launch, retention or reporting caps; teams with heavier usage may need the much more expensive Team tier or custom Enterprise pricing.
- Full web app pentesting appears in Small Team and above, while Vibe Coding has only limited network scanning.
Alternatives
Compare penetration testing software if you want to weigh a broader set of tools before choosing a platform.
- Caido is a reasonable alternative for users seeking a freemium option with a free Basic plan capped at two projects, seven workflows, three plugins, five filter presets and one pipeline session at a time.
- Dradis is worth considering if an open-source Community Edition for one project at a time is a better fit, or if a free trial matters.
- Kali Linux is a free, open-source distribution to consider instead of a paid platform.
- OWASP Amass is a free, Apache-licensed framework for readers seeking an open-source option.
- RedAmon offers a free MIT-licensed Docker stack for self-hosted use.
- Aircrack-ng is a free software suite with no license fee.
- OWASP ZAP is a free, open-source option for users who want software they can also contribute to.
- Reconmap is free and open source, with no usage limits stated.
Verdict
Pentesterra is a strong fit for internal teams, MSSPs and regulated organizations that need vulnerability management, testing, attack-chain analysis and evidence in a connected workflow, with deployment choices that reach air-gapped environments. Its main reason to choose it is that breadth; its main reason to look elsewhere is the tiered quotas and steep cost of the larger paid plans, especially if your needs are narrow or your usage is high.
Verdict
Pentesterra brings multiple security workflows together and offers deployment options from SaaS to air-gapped on-premises. The free DevGuard plan has stated project and scan limits, while enterprise pricing is custom.
Questions
Does Pentesterra have a free plan?
Yes. DevGuard Free is listed as free and includes one project, three scans per month, the CLI, IDE plugin and web console, and community support.
What is the lowest priced paid plan?
Vibe Coding costs €23 a month, billed at €23 per month. It includes three projects, 20 scans per month, 300 dependencies per scan, 14-day raw data retention and limited network scanning.
Which deployment options are available?
Pentesterra can be deployed as SaaS, dedicated PaaS or fully air-gapped on-premises.
Which platforms does DevGuard support?
Its pre-built CLI binary is available for Linux, macOS Intel, macOS Apple Silicon and Windows. Extensions are available for VS Code, Cursor and Windsurf.
What integrations does Pentesterra offer?
It provides Jira ticket creation from verified findings and a REST API for scans, results and reporting. Enterprise integrations include SIEM export in CEF or JSON, Jira and ServiceNow ticketing, SAML 2.0 or OIDC SSO, and a REST API.
Which compliance frameworks are covered by enterprise evidence packages?
Enterprise plans provide per-cycle evidence packages for SOC 2, ISO 27001, PCI-DSS and NIST CSF, including per-finding proofs of concept and delta reports.
Facts from Pentesterra's own pages
- Active Directory testing
- The platform automates AD enumeration, ACL analysis, credential-abuse simulation and safe lateral-movement validation. · pentesterra.com, 15 Oct 2026
- Attack-chain analysis
- Pentesterra correlates code, web and network findings into directed attack paths mapped to kill-chain phases. · pentesterra.com, 15 Oct 2026
- Automated network pentesting
- Its network pentest module performs controlled exploit validation for internal and external exposure with operational guardrails. · pentesterra.com, 15 Oct 2026
- Breach and attack simulation
- BAS scenarios test whether defensive controls work and expose realistic attack paths. · pentesterra.com, 15 Oct 2026
- Build extensibility
- The extension is described as TypeScript orchestrating a Python CLI and Pentesterra API, and it can be built into a VSIX from source. · marketplace.visualstudio.com, 15 Oct 2026
- CLI requirement
- The DevGuard CLI requires Python 3.9 or newer and installs with pip as pentesterra-devguard. · pentesterra.com, 15 Oct 2026
- Company facts
- LinkedIn lists Pentesterra as a computer and network security company founded in 2021 with 2–10 employees and public-company status. · linkedin.com, 15 Oct 2026
- Compliance evidence
- Enterprise plans provide per-cycle evidence packages for SOC 2, ISO 27001, PCI-DSS and NIST CSF, including per-finding proofs of concept and delta reports. · pentesterra.com, 1 Oct 2026
- Core workflow
- Pentesterra combines vulnerability management, attack-surface mapping, breach simulation and controlled exploitation into a continuous workflow with evidence-first prioritization. · pentesterra.com, 1 Oct 2026
- Data protection
- Pentesterra states that it uses end-to-end encryption, credential-vault isolation, per-scope processing isolation and distributed scanner isolation. · pentesterra.com, 1 Oct 2026
- Deployment
- The platform is deployable as SaaS, dedicated PaaS, or fully air-gapped on-premises. · pentesterra.com, 1 Oct 2026
- Deployment options
- Deployments include managed SaaS, dedicated PaaS, hybrid scanner nodes, full on-premises operation and an air-gapped GOV edition. · pentesterra.com, 15 Oct 2026
- Developer extension
- The VS Code Marketplace extension supports VS Code, Cursor and Windsurf and can install the CLI automatically. · marketplace.visualstudio.com, 15 Oct 2026
- DevGuard platforms
- DevGuard offers a pre-built binary CLI for Linux, macOS Intel, macOS Apple Silicon and Windows, plus extensions for VS Code, Cursor and Windsurf. · pentesterra.com, 1 Oct 2026
- DevGuard privacy
- DevGuard does not upload source code or transmit raw secrets; it sends metadata and redacted findings for cloud analysis. · pentesterra.com, 1 Oct 2026
- Documentation
- The public DevGuard guide covers API-key creation, CLI installation, project initialization, scans, JSON output, IDE use, privacy, ecosystems and troubleshooting. · pentesterra.com, 15 Oct 2026
- Dynamic Rule Security Engine
- DRSE is a programmable rule layer that can trigger rescans, alerts or enrichment workflows from scan events. · pentesterra.com, 15 Oct 2026
- Enterprise integrations
- Enterprise integrations include SIEM export in CEF or JSON, Jira and ServiceNow auto-ticketing, SAML 2.0 or OIDC SSO, and a REST API. · pentesterra.com, 1 Oct 2026
- Exploit validation
- Safe exploit validation uses real-world tools in non-malicious modes and is described as having no malware or ransomware. · pentesterra.com, 1 Oct 2026
- Exploit verification
- Findings can be validated with non-destructive verify-only or exploit-mode scripts and evidence is attached to reports. · pentesterra.com, 15 Oct 2026
- Founded
- 2021 · pentesterra.com, 23 Sept 2026
- Founder
- Pentesterra identifies Olesia Shelestova as founder and CEO and places headquarters in Italy. · pentesterra.com, 15 Oct 2026
- Headquarters
- Italy · pentesterra.com, 23 Sept 2026
- Independent package record
- The piwheels mirror lists pentesterra-devguard version 1.4.24 released 2026-07-06, with 13 files and 16 all-time downloads recorded on that page. · piwheels.org, 15 Oct 2026
Where Pentesterra stands on Freedom251
- Penetration Testing Software#9 of 34