Freedom251 › Vulnerability Scanning Software
NSAuditor AI
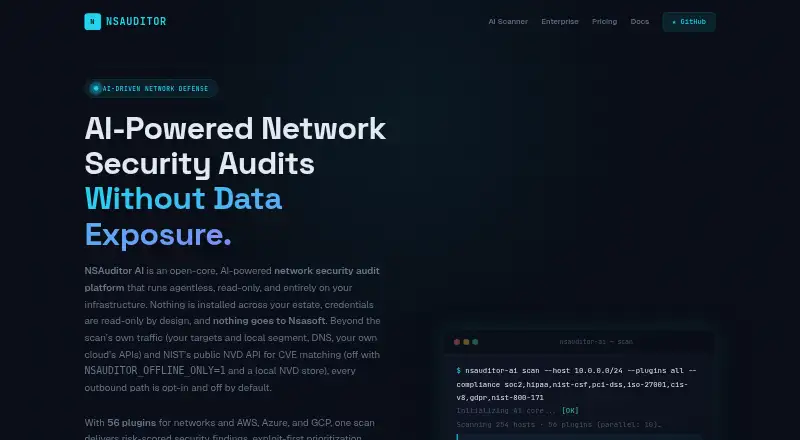
What NSAuditor AI is
NSAuditor AI is an on-premises network security audit platform for Windows, macOS, and Linux. It scans without agents and reads configuration and metadata, so its auditing does not need permissions to create, change, or delete data. All tiers support AI analysis through OpenAI, Claude, or Ollama, using API keys supplied by the customer. Reports can be exported in formats such as JSON, HTML, SARIF, CSV, and Markdown, depending on edition. Pro adds offline CVE matching and prioritization using threat data populated by the customer. Enterprise adds 28 auditors for AWS, GCP, and Azure, and can map one scan to eight compliance frameworks. The platform also supports air-gapped environments, offline licensing, and operation designed to prevent data leaving the customer’s environment. Community is free, Pro is listed at $470 per year or $49 per month, and Enterprise plans are $2,000, $5,000, or $10,000 per year.
Who it suits
It suits organizations that need to audit network security on their own infrastructure, including in air-gapped environments. Pro and Enterprise add options for threat matching, cloud audits, compliance mapping, and expanded support.
What it does well
- Agentless scans read configuration and metadata only.
- Runs on customer infrastructure and supports air-gapped use.
- All tiers support AI analysis with customer-provided API keys.
- Enterprise maps scans to eight compliance frameworks.
- Reports support multiple export formats, depending on edition.
What to know first
- Pro is listed at $470 per year or $49 per month.
- Enterprise plans start at $2,000 per year.
- Community support is self-serve documentation and GitHub discussions.
Limits
Community includes 27 scanner plugins. Enterprise Base supports up to 5 seats or scanning nodes, Growth up to 25, and Scale has unlimited seats; Pro and Enterprise are paid plans.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Community | forever · 27 scanner plugins · AI analysis · JSON/HTML/SARIF/CSV · MCP server (3 of 7 tools) · 7-day CTEM history · webhook alerts | Free |
| Enterprise Scale | annual invoicing · Unlimited seats · custom SLA · custom plugins · 56 plugins · eight compliance frameworks | $10,000 a year |
| Enterprise Base | annual invoicing · Up to 5 seats/scanning nodes · 56 plugins · eight compliance frameworks · air-gapped operation | $2,000 a year |
| Pro (annual) | Billed as $470/yr · saves $118 vs monthly · CVE matching · 4 parallel analysis agents · risk scoring · 48hr email-support SLA | $470 a year |
| Pro annual | annual payment; $39.17/month effective · Same Pro features as monthly · annual savings stated as $118 | $470 a year |
| Pro monthly | billed each month · CVE matching · MITRE annotations · risk scoring · exploit intelligence · executive HTML/Jira CSV reports · unlimited CTEM history · 5 MCP tools · 48-hour email SLA | $49 a month |
| Pro (monthly) | Billed each month · Same features as annual Pro · CVE matching · risk scoring · parallel analysis agents | $49 a month |
| Enterprise Growth | annual invoicing · Up to 25 seats/scanning nodes · 56 plugins · eight compliance frameworks · air-gapped operation | $5,000 a year |
As nsauditor.com lists them, read 15 Oct 2026. The maker's own page has the final word.
Getting started
- Visit https://www.nsauditor.com/.
- Choose the Community plan for a free, forever-billed option with no signup, or review Pro and Enterprise plans.
- Run it on Windows, macOS, or Linux in the on-premises deployment model.
- Configure read-only credentials for scanning.
- For AI analysis, use OpenAI, Claude, or Ollama with customer-provided API keys.
NSAuditor AI is an on-premises platform for network security audits, with agentless scanning and optional AI analysis. It will suit teams that need tight control over scan data and permissions; its strongest cloud and compliance capabilities are reserved for Enterprise.
Overview
NSAuditor AI audits network configuration and metadata using read-only credentials. It does not require permission to create, write, modify, or delete resources, a useful safeguard for teams reluctant to grant an auditing tool broader access. The trade-off is deployment: it runs on the customer’s infrastructure rather than as a hosted service.
Zero-data-exfiltration operation, air-gapped environments, and offline licensing make it a practical candidate for restricted networks. AI analysis is available across all tiers through OpenAI, Claude, or Ollama, using customer-provided API keys. Its MCP server works with Claude Desktop, Claude Code, Cursor, and other MCP-compatible assistants. These options support AI-assisted workflows, but require customers to choose and supply their own provider credentials.
Key features
Community includes 27 scanner plugins and is MIT licensed. Pro adds offline NVD CVE matching and exploit-first prioritization using CISA KEV and FIRST EPSS data from customer-populated stores. That gives teams threat-context signals for prioritizing findings without relying on an online intelligence feed; they must maintain the underlying stores themselves.
Enterprise adds 28 auditors for AWS, GCP, and Azure, plus a zero-trust posture check scored from a network-host scan. It also maps one scan to eight frameworks: SOC 2, HIPAA, NIST CSF 2.0, PCI DSS v4.0.1, ISO/IEC 27001:2022, CIS Controls v8, GDPR Article 32, and NIST SP 800-171 Rev 2. This breadth can reduce repeated mapping work for organizations with multiple compliance obligations, but it is a costly step up from Pro.
Reports can be exported as JSON, HTML, SARIF, CSV, Markdown, executive HTML, or Jira-importer CSV, depending on edition. Compliance artifacts include SHA-256 chain-of-custody sidecars, with RFC 3161 trusted timestamps available as an opt-in feature. Enterprise also has opt-in scan-time connectors for Vanta, Drata, and Secureframe; production live-tenant validation is still in progress, so teams should not treat those connectors as validated production integrations.
Pricing
Community costs nothing, billed Forever. It includes 27 scanner plugins, is MIT licensed, has no restrictions, and requires no signup. This is a strong starting point for individual users or teams assessing the core audit workflow, but it does not include Pro’s CVE matching, risk scoring, parallel analysis agents, or 48hr email-support SLA.
Pro (annual) is $39 a year, billed as $470/yr, and saves $118 vs monthly. It adds CVE matching, four parallel analysis agents, risk scoring, and a 48hr email-support SLA. Pro (monthly) is $49 a month, billed each month, with the same core Pro features: CVE matching, risk scoring, and parallel analysis agents. Monthly billing offers flexibility, while annual billing lowers the stated cost for a full-year commitment.
Enterprise Base costs $2,000 a year with annual invoicing and supports up to five seats or scanning nodes. Enterprise Growth costs $5,000 a year, also with annual invoicing, and raises that cap to 25 seats or scanning nodes. Enterprise Scale costs $10,000 a year with annual invoicing and offers unlimited seats, a custom SLA, and custom plugins. These tiers are for organizations that need the cloud auditors and eight-framework mapping; the seat and node caps matter when sizing Base or Growth. Enterprise support adds onboarding, dedicated channels, or a dedicated support engineer, depending on tier.
Platforms
NSAuditor AI supports Linux, macOS, and Windows. It is on-premises software with credentialed, agentless scanning and network discovery, so it fits teams able to operate audits from their own infrastructure rather than those seeking a managed cloud scanner.
Who it's for
The best fit is an infrastructure or security team that needs read-only audits, offline or air-gapped operation, and control over where scan activity runs. Pro makes more sense when threat-informed prioritization and support response matter. Enterprise is the relevant choice for multi-cloud auditing and compliance mapping across the named frameworks. Teams wanting a hosted service, or only a narrow scanning function, may find the deployment model or Enterprise price harder to justify.
Pros and cons
- Pros: Read-only, agentless scanning avoids write permissions and agent deployment, simplifying audits where access and change control are strict.
- Pros: Offline operation, air-gap support, and offline licensing suit environments that cannot rely on routine external connectivity.
- Pros: All tiers can use OpenAI, Claude, or Ollama for AI analysis, with an MCP server for compatible assistants.
- Pros: Enterprise maps one scan to eight frameworks and adds AWS, GCP, and Azure auditors, covering several needs in one tier.
- Cons: Pro’s threat-intelligence matching depends on customer-populated data stores, adding upkeep to the offline approach.
- Cons: Cloud auditors and framework mapping require Enterprise, starting at $2,000 a year.
- Cons: The opt-in Vanta, Drata, and Secureframe connectors are still undergoing production live-tenant validation.
Alternatives
Consider Intruder if you want a freemium scanner with a free tier that includes five infrastructure targets, weekly external scans, and one connected cloud account; its free plan excludes web apps.
ManageEngine Vulnerability Manager Plus is another freemium option, with a free edition and a Professional on-premises plan, for readers comparing a separate vulnerability-management product. OpenVAS offers a free virtual appliance with a community feed and limited enterprise features, making it an alternative for those who prefer that model and can work without default support.
For a free, standalone CLI, Nuclei is an option; OWASP Amass is a free open-source framework. Qualys External Attack Surface Management offers a 30-day no-cost period for CSAM with EASM, while Pentest-Tools Port Scanner includes open ports and services discovery in its free tier.
Browse more options in Network Vulnerability Scanners and Vulnerability Scanning Software.
Verdict
NSAuditor AI is a good fit for teams that need locally run, read-only network audits and value offline operation. Its core case is disciplined access and data control, with optional AI analysis across every tier. Look elsewhere if you need hosted scanning, or if cloud coverage and compliance mapping are essential but Enterprise pricing is beyond reach.
Verdict
NSAuditor AI combines read-only, agentless auditing with optional AI analysis and edition-dependent reporting. Community is free; cloud auditors and eight-framework mapping are Enterprise features.
Questions
Is NSAuditor AI free?
Yes. Community costs nothing, is billed forever, and requires no signup. The pricing note lists paid plans from $470/yr.
What does Pro cost?
Pro monthly is listed at $49 a month. Pro annual is listed at $39 a year, with billing described as $470/yr.
What platforms does it support?
Windows, macOS, and Linux are listed.
Can it run without internet access?
It supports air-gapped environments and offline licensing.
Which AI providers can it use?
All tiers support OpenAI, Claude, or Ollama using customer-provided API keys.
Who makes NSAuditor AI?
Nsasoft US LLC is the maker. It says it has provided network security and recovery software since 2004.
Facts from NSAuditor AI's own pages
- AI integrations
- The MCP server works with Claude Desktop, Claude Code, Cursor, and other MCP-compatible AI assistants. · nsauditor.com, 30 Sept 2026
- AI providers
- OpenAI, Claude and Ollama are supported in every tier using customer-supplied keys. · nsauditor.com, 15 Oct 2026
- Cloud coverage
- Enterprise provides 28 cloud auditors across AWS, GCP, and Azure, plus a zero-trust posture check scored from a network-host scan. · nsauditor.com, 30 Sept 2026
- Cloud integrations
- Enterprise provides read-only auditors for AWS, Azure and GCP and optional Vanta, Drata and Secureframe connectors. · nsauditor.com, 15 Oct 2026
- Company founded
- LinkedIn lists the company as founded in 2011. · linkedin.com, 15 Oct 2026
- Company headquarters
- LinkedIn lists headquarters in Las Vegas, Nevada, with a primary address of 732 S 6th St. · linkedin.com, 15 Oct 2026
- Company type
- LinkedIn lists NSAuditor.ai as privately held in computer and network security with 11–50 employees. · linkedin.com, 15 Oct 2026
- Compliance
- Enterprise maps one scan to eight frameworks: SOC 2, HIPAA, NIST CSF 2.0, PCI DSS v4.0.1, ISO/IEC 27001:2022, CIS Controls v8, GDPR Article 32, and NIST SP 800-171 Rev 2. · nsauditor.com, 30 Sept 2026
- Compliance frameworks
- Enterprise maps one scan to SOC 2, HIPAA, NIST CSF 2.0, PCI DSS v4.0.1, ISO 27001:2022, CIS Controls v8, GDPR Article 32 and NIST SP 800-171 Rev 2. · nsauditor.com, 15 Oct 2026
- Continuous monitoring
- CTEM watch mode rescans on a schedule, compares history and can send webhook alerts; Enterprise retains unlimited JSONL history. · nsauditor.com, 15 Oct 2026
- Data handling
- The vendor states that scans, findings and reports stay on the customer machine and that license validation is offline. · nsauditor.com, 15 Oct 2026
- Documentation depth
- The documentation covers installation, architecture, typed plugin SDK, compliance evidence, MCP workflows and air-gapped deployment. · nsauditor.com, 15 Oct 2026
- Evidence integrity
- Enterprise evidence packs use SHA-256 chain-of-custody manifests, optional RFC 3161 timestamps and operator-held Ed25519 signatures verifiable offline. · nsauditor.com, 15 Oct 2026
- Exports
- Community exports JSON, HTML, SARIF and CSV, while Pro adds executive HTML and Jira-importer CSV reports. · nsauditor.com, 15 Oct 2026
- Founded
- 2004 · nsauditor.com, 28 Sept 2026
- GRC integrations
- Enterprise includes opt-in scan-time connectors for Vanta, Drata, and Secureframe; production live-tenant validation is still in progress. · nsauditor.com, 30 Sept 2026
- Headquarters
- Las Vegas, Nevada, USA · nsauditor.com, 28 Sept 2026
- Independent review: product scope
- SC Media described the earlier Nsauditor as a Windows multipurpose scanner covering ports, SQL, web servers, NetBIOS, SNMP, RPC and reporting. · scworld.com, 15 Oct 2026
- Installation
- The documented installation command is npm install -g nsauditor-ai, with deployment also described for isolated hosts and container/orchestrator environments. · nsauditor.com, 15 Oct 2026
- Licence
- The Community Edition repository is MIT licensed; Pro and Enterprise features use a separate proprietary licence. · github.com, 15 Oct 2026
- Limit: comparison with open-source tools
- SC Media said users experienced with nmap and Nessus might find some Nsauditor options restrictive. · scworld.com, 15 Oct 2026
- Limit: interface organization
- SC Media said the large number of utilities could make the interface feel cluttered and disorganized. · scworld.com, 15 Oct 2026
- Limit: reporting depth
- SC Media characterized the reporting output as fairly basic, although it was XML and could be restyled. · scworld.com, 15 Oct 2026
- Maker
- Nsasoft US LLC says it has provided network security and recovery software for businesses and individuals since 2004. · nsauditor.com, 30 Sept 2026
Where NSAuditor AI stands on Freedom251
- Vulnerability Scanning Software#1 of 35
- Network Vulnerability Scanners#1 of 23