Freedom251 › Vulnerability Scanning Software
Nikto
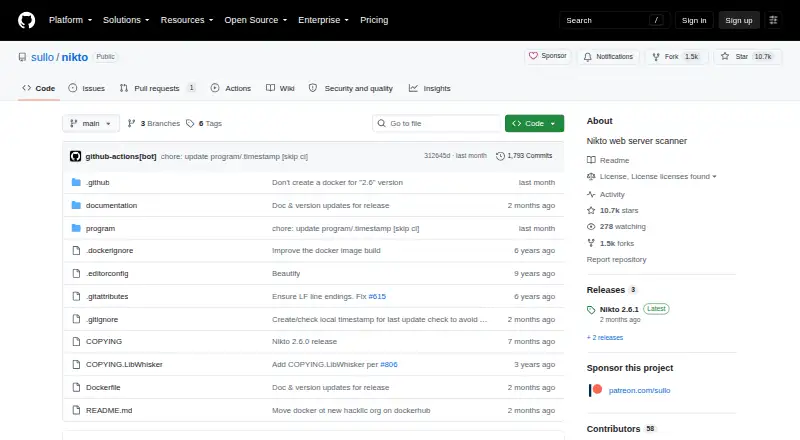
What Nikto is
Nikto is an on-premises web server scanner for security professionals, penetration testers, and system administrators. It checks web servers and host URLs for more than 8,000 potentially dangerous or notable files and programs, and flags outdated server versions and common misconfigurations. It identifies installed servers and software from headers, page content, and file analysis; scan items and plugins can update automatically. Users can include or exclude classes of checks, scan multiple ports or servers, and use server lists from Nmap output. Custom checks can be added through CSV files. Reports are available as plain text, JSON, SQL, XML, HTML, or CSV, including direct reporting to MySQL and PostgreSQL. Nikto supports IPv4, IPv6, HTTP proxies, Basic and NTLM host authentication, and credential attempts for Basic, NTLM, and Digest realms. It detects TLS configuration and fingerprints, handles cookies automatically, and can disable cookie use. It is free software under GPLv3; database files are restricted to use with Nikto, and commercial use requires a license.
Who it suits
Nikto suits security professionals, penetration testers, and system administrators who need to scan web servers and host URLs. It is available for Linux, Windows, and self-hosted deployment.
What it does well
- Checks more than 8,000 potentially dangerous or notable items.
- Supports multiple report formats and database reporting.
- Scans can cover multiple ports and servers.
- Supports IPv4, IPv6, and HTTP proxies.
- Custom checks can be added through CSV files.
What to know first
- Database files are restricted to use with Nikto.
- Commercial use of database files requires a license.
Limits
Nikto is free under GPLv3. Its database files may only be distributed with and used in Nikto; commercial use requires a license from the author.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Nikto | Free software under GPLv3 · Database files are restricted to use with Nikto; commercial use requires a license | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Nikto project website on GitHub.
- Choose a documented installation route: Perl, Docker, or Windows.
- Set the web server or host URL to scan.
- Adjust the check classes, ports, servers, authentication, or cookie settings as needed.
- Choose a report format or direct reporting to MySQL or PostgreSQL.
Verdict
Nikto combines broad server checks with configurable scans, authentication support, and several reporting options. Note the separate restrictions on its database files when considering commercial use.
Questions
How much does Nikto cost?
The listed plan is free. Nikto is open source.
What is Nikto licensed under?
Nikto 2.6 code is GPLv3. Its database files have separate restrictions and commercial use requires a license from the author.
Which platforms does Nikto support?
Its listed platforms are Linux, Windows, and self-hosted deployment. Installation documentation covers Perl, Docker, and Windows.
What can Nikto scan?
It scans web servers and host URLs, including multiple ports or servers in a scan.
Can Nikto scan authenticated targets?
Yes. It supports Basic and NTLM host authentication and can attempt credentials for Basic, NTLM, and Digest authorization realms.
What reports can Nikto produce?
Reports can be plain text, JSON, SQL, XML, HTML, or CSV. Direct reporting to MySQL and PostgreSQL is supported.
Facts from Nikto's own pages
- Authentication
- It supports Basic and NTLM host authentication and can guess credentials for Basic, NTLM, and Digest authorization realms. · cirt.net, 4 Oct 2026
- Custom checks
- Users can add custom checks through CSV files. · cirt.net, 4 Oct 2026
- Detection
- It identifies installed web servers and software using headers, content, and file analysis, and its scan items and plugins can update automatically. · cirt.net, 4 Oct 2026
- False positives
- The scanner uses headers, page content, hashing, and other methods to reduce false positives. · cirt.net, 4 Oct 2026
- Install options
- The project documents Perl installation, Docker images, and Windows installation. · github.com, 4 Oct 2026
- License terms
- Nikto 2.6 code is GPLv3, while its database files may only be distributed with and used in Nikto unless a commercial license is obtained from the author. · cirt.net, 4 Oct 2026
- Protocols and proxies
- Nikto supports IPv4, IPv6, and HTTP proxies. · cirt.net, 4 Oct 2026
- Purpose
- Nikto is an open-source web server scanner for security professionals, penetration testers, and system administrators. · cirt.net, 4 Oct 2026
- Reporting
- Scans can produce plain text, JSON, SQL, XML, HTML, or CSV reports, including direct reporting to MySQL and PostgreSQL. · cirt.net, 4 Oct 2026
- Scan controls
- Users can tune scans to include or exclude vulnerability check classes and scan multiple ports or servers, including servers listed in Nmap output. · cirt.net, 4 Oct 2026
- Scan coverage
- It checks for over 8,000 potentially dangerous or interesting files and programs and identifies outdated server versions and common misconfigurations. · cirt.net, 4 Oct 2026
- Support
- The project directs users to GitHub or Docker and its documentation for support, and asks users to open GitHub issues for bugs, feature requests, or questions. · cirt.net, 4 Oct 2026
- TLS and cookies
- Nikto detects TLS configuration and fingerprints, handles cookies automatically, and offers an option to disable cookie use. · cirt.net, 4 Oct 2026
Where Nikto stands on Freedom251
- Vulnerability Scanning Software#7 of 35