Freedom251 › Database Vulnerability Scanners
DBX
What DBX is
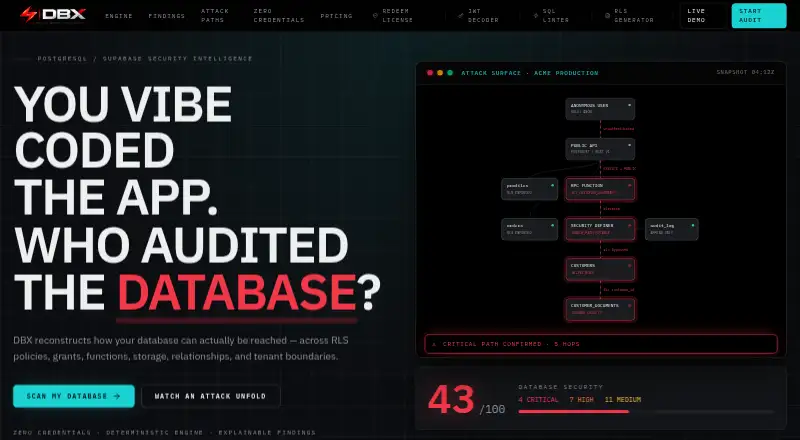
DBX is a web-based security analysis tool for PostgreSQL and Supabase databases. It maps how identities can reach database objects through policies, grants, functions, storage, relationships, and tenant boundaries. The scanner inspects live security objects and evaluates practical access with a deterministic rule engine and permission graph. It groups weaknesses into attack paths and reports severity, confidence, and supporting evidence. Each deterministic finding includes a proposed migration tied to the relevant object, with an expected security effect and compatibility risk. A snapshot contains catalog metadata such as schemas, policies, grants, routines, and relationships, rather than database rows. DBX says the snapshot workflow does not need a database password, persistent connection, agent, or production write access; scanning is designed for a dedicated least-privilege role with catalog access. A language model explains verified findings and drafts remediation for human review. DBX does not assess application code, network controls, or client authorization logic, and does not claim compliance certification. The free Database Scan plan offers unlimited introspection; Full Remediation is listed at $195, paid once and includes five unique scans.
Who it suits
DBX is positioned for developers and teams building PostgreSQL or Supabase applications, including multi-tenant systems and AI-generated SQL workflows. It suits teams looking for database access-path analysis and migration guidance.
What it does well
- Maps practical access across database objects and tenant boundaries
- Connects weaknesses into evidenced attack paths
- Proposed migrations include effect and compatibility risk
- Snapshot contains catalog metadata, not database rows
- Free plan offers unlimited introspection
What to know first
- Does not test application code or network controls
- Does not assess client authorization logic
- Makes no compliance certification claims
- Full Remediation costs $195, paid once
Limits
The free Database Scan plan provides introspection, topology and score views, finding counts and severity, and local analysis. Exact vulnerability details, complete attack path graphs, copy-paste SQL remediation, and fix verification are included in Full Remediation at $195, paid once, with five unique scans.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Database Scan | Unlimited schemas · topology and score · finding counts and severity · local browser analysis | Free |
| Full Remediation | Introductory Launch Price · 5 unique scans · exact vulnerability details · attack-path graphs · copy-paste SQL remediation · fix verification | $19, paid once |
As dbxray.co lists them, read 15 Oct 2026. The maker's own page has the final word.
Getting started
- Open https://www.dbxray.co/ in a web browser.
- Choose the free Database Scan plan for unlimited introspection or Full Remediation for five unique scans.
- Prepare a dedicated least-privilege database role with CONNECT, schema USAGE, and SELECT on catalog views.
- Submit database credentials through the snapshot workflow; DBX says they are sent to server-side functions over TLS and are not returned to the browser or written to logs or analytics events.
DBX is a web-based analyzer for effective access in PostgreSQL and Supabase databases. It suits developers and security teams working on permission-heavy or multi-tenant systems, including projects that generate SQL with AI. Its main value is turning database reachability problems into evidenced attack paths and migration-ready fixes, while its scope stops at the database layer.
Overview
DBX reconstructs how identities can actually reach database objects rather than reviewing grants or policies in isolation. It follows interactions among row-level security, grants, functions, storage, relationships, and tenant boundaries. That makes it a focused choice for teams that need to understand authorization behavior inside PostgreSQL-family databases, especially when several controls combine to produce an unexpected path.
The scanner is agentless and works with cloud databases. Its snapshot workflow requires no database password, persistent connection, agent, or production write access. A dedicated least-privilege role is designed to need CONNECT, schema USAGE, and SELECT on catalog views. Snapshots contain catalog metadata, including schemas, policies, grants, routines, and relationships, but not database rows. Credentials submitted for the workflow are sent to server-side functions over TLS, are not returned to the browser, and are not written to logs or analytics events.
Key features
DBX resolves what each identity can reach in practice by introspecting live security objects. It then joins individual weaknesses into attack paths and reports severity and confidence with evidence. This connected view is more useful than a flat permission inventory when a risk depends on several policies, routines, or relationships interacting.
Every deterministic finding includes a proposed migration tied to the object that created the issue. The proposal states the expected security effect and compatibility risk, and the paid remediation plan adds copy-paste SQL and post-change verification. That gives database owners a concrete repair workflow, although the team must still review, run, and validate migrations.
A deterministic rule engine evaluates introspected facts and a permission graph. A language model is limited to explaining verified findings and drafting remediation for human review, rather than deciding whether an unverified issue exists. DBX supports privilege analysis and lists Supabase, PostgreSQL, Neon, AWS, GCP, Azure, Render, and DigitalOcean among its platform links.
DBX does not assess application code, network controls, or client authorization logic, and it makes no compliance-certification claims. Organizations seeking broad application, infrastructure, or regulatory coverage need additional tools and reviews.
Pricing
Database Scan
The free plan costs free, billed as “Free Unlimited Introspection.” It includes unlimited schema introspection, database topology and score views, finding counts and severity, and local analysis so data never leaves the browser. This is the sensible choice for developers who want recurring visibility into database permissions without remediation deliverables or a paid commitment.
Full Remediation
The paid plan costs $195, paid once at an introductory launch price. It includes five unique scans, exact vulnerability details, complete attack-path graphs, copy-paste SQL remediation, and verification of fixes after remediation. It fits teams preparing to repair a defined set of databases; the five-scan allowance is a meaningful limit for organizations with many environments or frequent reassessments, and the stated price is one-time rather than a subscription.
Platforms
DBX is delivered on the web and is intended for cloud databases as well as PostgreSQL and Supabase deployments. Its listed ecosystem includes Supabase, PostgreSQL, Neon, AWS, GCP, Azure, Render, and DigitalOcean.
Who it's for
Choose DBX if you build PostgreSQL or Supabase applications and need an identity-by-identity view of effective reach, particularly in multi-tenant architectures or AI-generated SQL workflows. The free plan suits exploratory and ongoing introspection; Full Remediation suits teams that need evidence, attack-path diagrams, executable migration guidance, and fix verification.
It is not the right primary tool for application-code review, network segmentation, client-side authorization, or compliance certification. Those concerns require separate assessment.
Pros and cons
- Pro: Connects RLS, grants, functions, storage, relationships, and tenant boundaries into practical attack paths, exposing interaction risks that isolated checks can miss.
- Pro: Free Unlimited Introspection includes topology, scores, severity counts, and browser-local analysis at no cost.
- Pro: Proposed migrations are tied to the responsible object and include security effect and compatibility risk; the paid tier adds SQL and verification.
- Pro: Agentless, read-oriented snapshot design limits operational footprint, with catalog metadata rather than row data.
- Con: Coverage ends at database security; application, network, and client authorization weaknesses remain outside its analysis.
- Con: Full Remediation is limited to five unique scans, so larger estates may outgrow the one-time package.
- Con: No compliance certification claims are made, so regulated programs cannot treat DBX as their certification evidence.
Alternatives
For a broader directory of products, see Database Vulnerability Scanners.
- Defensia Database Security is a better fit when you need Linux, self-hosted, or web deployment and a free monitoring tier capped at one server, 2,000 events per month, and three days of retention.
- Onam Database Security suits cloud-security-posture work across one cloud account and up to 500 resources, with CIS benchmarks and core critical/high rules.
- Oracle Cloud Infrastructure Secret Management is for managing secrets and versions in OCI rather than tracing PostgreSQL authorization paths.
- Qualys External Attack Surface Management is preferable for external asset discovery and attack-surface management, with a 30-day no-cost CSAM/EASM period.
- SQLTriage is a free Windows or self-hosted option with all features and no per-server fees or subscription.
- Free SQL Server Compliance Benchmark Tool fits SQL Server benchmark checking with more than 80 checks and PDF output.
- Omega DB Scanner Standalone is for Windows-based Oracle security scanning on listed 10g through 12c versions.
- Trellix Data Loss Prevention is the alternative when enterprise DLP across endpoints, email, web, networks, and storage is the priority.
Verdict
DBX is a strong choice for PostgreSQL and Supabase teams that need a defensible picture of effective database reach and practical, object-linked remediation. Its free introspection removes a cost barrier, while the one-time Full Remediation plan adds unusually concrete repair output. Look elsewhere when your priority is application or network security, compliance certification, secret management, or broad data-loss prevention rather than database permission analysis.
Verdict
DBX focuses on database permissions and object reachability, with findings linked to proposed migrations. It is not a substitute for assessment of application code, network controls, or client authorization.
Questions
Is DBX free?
Yes. Database Scan is listed as free and includes unlimited introspection. Full Remediation is listed at $195, paid once.
Which databases and platforms does DBX support?
DBX analyzes PostgreSQL and Supabase databases through its web app. Its platform links include Supabase, PostgreSQL, Neon, AWS, GCP, Azure, Render, and DigitalOcean.
Does DBX need a database password or production write access?
DBX says the snapshot workflow requires no database password, persistent connection, agent, or production write access. The scanner is designed for a least-privilege role with CONNECT, schema USAGE, and SELECT on catalog views.
What data does the snapshot contain?
It contains catalog metadata such as schemas, policies, grants, routines, and relationships, but not database rows.
What does DBX include in Full Remediation?
The $195, paid once plan includes five unique scans, exact vulnerability details, attack-path graphs, copy-paste SQL remediation, and verification after remediation.
What does DBX not assess?
It does not test application code, network controls, or client authorization logic, and it makes no compliance certification claims.
Facts from DBX's own pages
- Access model
- DBX states that it requires no database password, persistent connection, agent, or production write access for its snapshot workflow. · dbxray.co, 30 Sept 2026
- Analysis method
- DBX introspects live security objects and resolves what each identity can reach in practice. · dbxray.co, 30 Sept 2026
- Attack paths
- DBX links separate weaknesses into multi-hop attack paths with severity and confidence indicators. · dbxray.co, 15 Oct 2026
- Credential handling
- Submitted database credentials are sent to server-side functions over TLS, are not rendered back to the browser, and are not written to logs or analytics events. · dbxray.co, 30 Sept 2026
- Credential model
- The advertised scan workflow uses a read-only catalog snapshot rather than a persistent database connection or production write access. · dbxray.co, 15 Oct 2026
- Credential protection
- Credentials are sent to server-side functions over TLS, encrypted, and excluded from browser rendering, logs, analytics and AI prompts. · dbxray.co, 15 Oct 2026
- Data handling
- The security snapshot contains catalog metadata such as schemas, policies, grants, routines, and relationships, but never database rows. · dbxray.co, 30 Sept 2026
- Data scope
- Snapshots contain catalog metadata and exclude application rows. · dbxray.co, 15 Oct 2026
- Detection method
- A deterministic rule engine and permission graph determine findings; the language model only explains verified results and drafts remediation. · dbxray.co, 15 Oct 2026
- Findings
- DBX connects individual weaknesses into attack paths and reports severity and confidence with evidence. · dbxray.co, 30 Sept 2026
- Founder motivation
- The interview says DBXray originated from the question of who audited the database behind an otherwise finished application. · signal-tech-news.vercel.app, 15 Oct 2026
- Independent developer profile
- Theodore Ochsen’s profile says he developed DBXray as a PostgreSQL and Supabase database-security analysis platform. · meritpages.com, 15 Oct 2026
- Independent technical description
- The same profile says DBXray examines database structure, RLS, policies, roles, grants, foreign keys and access patterns. · meritpages.com, 15 Oct 2026
- Independent workflow description
- Ochsen’s profile describes a read-only process in which users run an introspection query and provide the resulting snapshot for analysis. · meritpages.com, 15 Oct 2026
- Intended users
- DBX is positioned for developers and teams building PostgreSQL or Supabase applications, including multi-tenant systems and AI-generated SQL workflows. · dbxray.co, 30 Sept 2026
- Limitations
- DBX does not test application code, network controls, or client authorization logic and makes no compliance certification claims. · dbxray.co, 30 Sept 2026
- Limit: compliance
- The company says DBX does not certify databases as secure and makes no compliance-certification claims. · dbxray.co, 15 Oct 2026
- Limit: coverage
- DBX does not test application code, network controls or client-side authorization logic. · dbxray.co, 15 Oct 2026
- Linter claims
- The SQL-linter page labels the engine version 4.2.0-stable and claims 99.9% audit accuracy. · dbxray.co, 15 Oct 2026
- Local processing
- The homepage says snapshots, findings and remediation data are analyzed locally in the browser and are not retained. · dbxray.co, 15 Oct 2026
- Maker attribution
- Signal//Tech identifies Theodore Ochsen as founder of DaemonCore Enterprises and lists DBXray among its projects. · signal-tech-news.vercel.app, 15 Oct 2026
- Maker role
- Ochsen’s independent profile lists him as founder and lead software engineer of DaemonCore Enterprises. · meritpages.com, 15 Oct 2026
- Methodology
- A deterministic rule engine evaluates introspected facts and a permission graph, while a language model only explains verified findings and drafts remediation for human review. · dbxray.co, 30 Sept 2026
- Notable news
- A Signal//Tech founder interview published August 20, 2026 discusses DBXray as a response to database-access risks in rapidly built applications. · signal-tech-news.vercel.app, 15 Oct 2026
Where DBX stands on Freedom251
- Database Vulnerability Scanners#3 of 27