Freedom251 › Database Vulnerability Scanners
CyanoRisk Data Security Posture Management
Visit CyanoRisk Data Security Posture Management Alternatives Pricing
What CyanoRisk Data Security Posture Management is
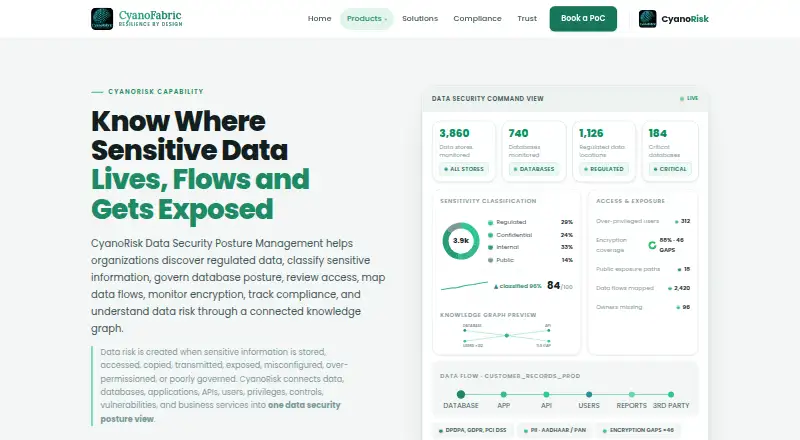
CyanoRisk Data Security Posture Management is an enterprise product from CyanoFabric Private Limited for finding and managing data security risks. It discovers regulated data, classifies sensitive information, reviews database posture and access, maps data flows, monitors encryption, and tracks compliance. Its posture view connects data and databases with applications, APIs, users, privileges, controls, vulnerabilities, and business services. A knowledge graph shows relationships between data objects, exposure paths, and graph coverage. The product highlights India-first detection of personally identifiable information, including Aadhaar and PAN. Its risk engine draws on discovery, database inventory, access reviews, encryption and configuration status, vulnerability findings, data flow signals, compliance requirements, and consent records. The maker says the platform maps risks to DPDPA, GDPR, and PCI DSS, and produces owner actions, remediation tickets, and an executive risk view. Scanner ingest is listed for Tenable, Qualys, Rapid7, and CrowdStrike. CyanoRisk runs on customer-provisioned infrastructure and network, with analysis inside the deployment and no telemetry or phone-home. Its described controls include role-based access, tamper-evident audit records, rate limits for sensitive operations, revocable short-lived sessions, and independently approved bulk changes. A six-week PoC and commissioning process covers kickoff through acceptance.
Who it suits
CyanoRisk is aimed at organizations that need to locate sensitive data and connect it to access, infrastructure, and compliance risks. Its named users include CISOs, CIOs, security engineers, DBAs, application owners, DPOs, executives, and auditors, particularly where on-premises deployment is required.
What it does well
- Connects data risks with applications, users, privileges, and services.
- Knowledge graph shows exposure paths and graph coverage.
- Detects Aadhaar and PAN alongside other PII.
- Maps risks to DPDPA, GDPR, and PCI DSS.
- Supports scanner ingest from Tenable, Qualys, Rapid7, and CrowdStrike.
- Analysis runs within customer infrastructure without telemetry or phone-home.
What to know first
- Paid enterprise product with pricing available on request.
- On-premises deployment uses customer-provisioned infrastructure.
- PoC and commissioning process spans six weeks.
Limits
The enterprise plan has no listed price and is offered through a demo or PoC request. Commissioning is described as a six-week process on customer-provisioned infrastructure.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| CyanoRisk Data Security Posture Management | Enterprise product · request a demo/PoC | On request |
As cyanofabric.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the CyanoRisk Data Security product website.
- Request a demo or PoC for the enterprise product.
- Provision the infrastructure and network for the deployment.
- Work through kickoff, installation, data ingest, UAT, and acceptance.
Verdict
Choose CyanoRisk if your organization needs an on-premises view linking sensitive data to access, vulnerabilities, and compliance, with remediation outputs. Its six-week commissioning process and pricing-on-request enterprise model may be a poor fit for teams seeking a quick start or a listed price.
Questions
How much does CyanoRisk cost?
Pricing is available on request; the enterprise product page invites buyers to request a demo or PoC.
Where does CyanoRisk run?
It is self-hosted and deployed on premises, on the customer's infrastructure and network.
What regulations does it map to?
The maker says it maps data risk to DPDPA, GDPR, and PCI DSS.
Which scanners can it ingest from?
The maker lists Tenable, Qualys, Rapid7, and CrowdStrike.
How long is onboarding?
The described PoC and commissioning process takes six weeks and covers kickoff, installation, data ingest, UAT, and acceptance.
Who makes CyanoRisk?
CyanoFabric Private Limited identifies itself as the maker and lists its registered office in Jakkur, Bengaluru, Karnataka, India.
Facts from CyanoRisk Data Security Posture Management's own pages
- Company
- The maker identifies itself as CyanoFabric Private Limited and lists its registered office in Jakkur, Bengaluru, Karnataka, India. · cyanofabric.com, 4 Oct 2026
- Compliance mapping
- The maker says DSPM maps data risk to DPDPA, GDPR, and PCI DSS. · cyanofabric.com, 4 Oct 2026
- Connected data risk
- It connects data, databases, applications, APIs, users, privileges, controls, vulnerabilities, and business services in a data security posture view. · cyanofabric.com, 4 Oct 2026
- Headquarters
- Bengaluru, Karnataka, India · cyanofabric.com, 28 Sept 2026
- Hosting and data handling
- The maker says CyanoRisk runs on the customer's infrastructure and network, with no telemetry or phone-home, and that analysis runs inside the deployment. · cyanofabric.com, 4 Oct 2026
- Integrations
- The maker lists scanner ingest for Tenable, Qualys, Rapid7, and CrowdStrike on its platform page. · cyanofabric.com, 4 Oct 2026
- Intended users
- The platform page names CISO, CIO, security engineer, DBA, application owner, DPO, and executive or auditor personas. · cyanofabric.com, 4 Oct 2026
- Knowledge graph
- The data risk knowledge graph links data objects with their relationships and shows exposure paths and graph coverage. · cyanofabric.com, 4 Oct 2026
- PII detection
- The product highlights India-first PII detection, including Aadhaar and PAN. · cyanofabric.com, 4 Oct 2026
- Purpose
- CyanoRisk DSPM discovers regulated data, classifies sensitive information, governs database posture, reviews access, maps data flows, monitors encryption, and tracks compliance. · cyanofabric.com, 4 Oct 2026
- Remediation
- The product page describes owner actions, remediation tickets, and an executive data risk view as outputs of its risk engine. · cyanofabric.com, 4 Oct 2026
- Risk signals
- The data risk engine lists discovery, database inventory, PII detection, access review, encryption status, configuration posture, vulnerability findings, data flow signals, compliance requirements, and consent records as inputs. · cyanofabric.com, 4 Oct 2026
- Security controls
- The maker describes role-based access control, a tamper-evident audit trail, rate-limited sensitive operations, short-lived revocable sessions, and independently approved bulk data changes. · cyanofabric.com, 4 Oct 2026
- Support and onboarding
- The maker describes a six-week PoC/commissioning process covering kickoff, installation, data ingest, UAT, and acceptance on customer-provisioned infrastructure. · cyanofabric.com, 4 Oct 2026
Where CyanoRisk Data Security Posture Management stands on Freedom251
- Database Vulnerability Scanners#14 of 27