Freedom251 › Software Composition Analysis Software
Bomly CLI
What Bomly CLI is
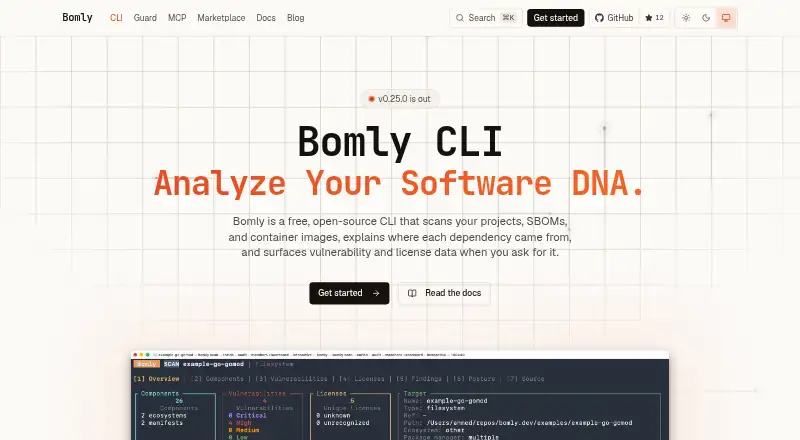
Bomly CLI is a free, open-source command-line tool for inspecting software dependencies. It scans source trees, SBOMs, Git refs, and container images, then builds dependency graphs that explain why packages appear in a project. Its scan, explain, and diff commands cover dependency analysis and comparisons between changes.
It has native detectors for major ecosystems and Syft-based detectors for the long tail, including the listed C++, Dart, .NET/NuGet, Elixir, Go, JavaScript package managers, PHP/Composer, Python tools, Ruby/Bundler, Rust/Cargo, Scala/SBT, and Swift package managers. Bomly reads and generates SPDX and CycloneDX SBOMs. Optional enrichment requests vulnerability and license data from OSV, CISA KEV, deps.dev, ClearlyDefined, and endoflife.date. Those requests go from the user’s machine directly to public APIs; telemetry and default outbound traffic are absent.
For automated workflows, Bomly can produce SARIF and documents CI recipes for GitHub Actions, GitLab, Jenkins, Azure DevOps, and CircleCI. Its stdio MCP server exposes the core commands to compatible agents such as Claude Code and Cursor. Go binaries can extend detection, matching, auditing, and analysis through its gRPC contract. Reachability analysis is available as a beta feature, with documented tiers varying by ecosystem. Bomly runs locally or in CI on Linux, macOS, and Windows; it requires no account or subscription.
Who it suits
Bomly suits developers who need local or CI dependency analysis, SBOM generation, or pull request scanning across its supported ecosystems. It also fits teams using MCP-aware coding agents or extending analysis through the gRPC contract.
What it does well
- Free and open source, with no account or subscription required.
- Scans source trees, SBOMs, Git refs, and container images.
- Reads and generates SPDX and CycloneDX SBOMs.
- SARIF output and documented recipes for five CI systems.
- No telemetry or default outbound traffic.
- MCP tools expose scan, explain, and diff to compatible agents.
What to know first
- Reachability analysis is marked beta.
- Optional vulnerability and license enrichment sends requests to public APIs.
Limits
The free plan has no listed quota or seat limit. Reachability analysis is beta, with different documented analysis tiers for Go and for npm, Python, and JVM.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Bomly CLI | Free; no account or subscription required · Free and open source · runs locally or in CI | Free |
As bomly.dev lists them, read 8 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Bomly website or its project repository.
- Choose Linux, macOS, or Windows for local use, or run it in CI.
- Use the scan command to analyze source trees, SBOMs, Git refs, or container images.
- Use explain to inspect why packages are present, or diff to compare changes.
- Optionally enable enrichment or connect its MCP server to a compatible agent.
Verdict
Choose Bomly CLI if you want a free local or CI tool for dependency graphs, SBOM work, or pull request scanning. Teams needing reachability analysis should account for its beta status and ecosystem-specific analysis tiers.
Questions
How much does Bomly CLI cost?
Bomly CLI is free: free plan. No account or subscription is required.
Which operating systems does it support?
It supports Linux, macOS, and Windows, and can also run in CI.
Can it create SBOMs?
Yes. It reads and generates SPDX and CycloneDX SBOMs.
Does Bomly provide vulnerability data?
Opt-in enrichment queries OSV, CISA KEV, deps.dev, ClearlyDefined, and endoflife.date for vulnerability and license data.
Can it scan in CI or pull requests?
It supports pull request scanning, SARIF output, and documented CI recipes for GitHub Actions, GitLab, Jenkins, Azure DevOps, and CircleCI.
Is it open source?
Yes. Bomly is described as free and open source.
Facts from Bomly CLI's own pages
- AI agents
- Its stdio MCP server exposes scan, explain, and diff tools for MCP-aware agents including Claude Code and Cursor. · bomly.dev, 8 Oct 2026
- Checksums
- Release archives and packages include SHA256SUMS for checksum verification. · bomly.dev, 8 Oct 2026
- CI integration
- Bomly supports SARIF output for code scanning and documents CI recipes for GitHub Actions, GitLab, Jenkins, Azure DevOps, and CircleCI. · bomly.dev, 8 Oct 2026
- Core commands
- Its core commands are scan, explain, and diff for analyzing dependencies and comparing changes. · bomly.dev, 8 Oct 2026
- Ecosystems
- It has native detectors for major ecosystems and uses Syft-based detectors for the long tail. · bomly.dev, 8 Oct 2026
- Experimental feature
- Reachability analysis is marked beta, with different analysis tiers documented for Go versus npm, Python, and JVM. · bomly.dev, 8 Oct 2026
- Extensibility
- Separate Go binaries can extend detection, matching, auditing, and analysis through Bomly's gRPC contract. · bomly.dev, 8 Oct 2026
- Intended users
- Bomly describes itself as built for developers and the AI agents they work with. · bomly.dev, 8 Oct 2026
- Privacy
- The CLI has no telemetry or default outbound traffic; enrichment calls are opt-in and go directly from the user's machine to public APIs. · bomly.dev, 8 Oct 2026
- Purpose
- Bomly scans source trees, SBOMs, Git refs, and container images to build dependency graphs and explain why packages are present. · bomly.dev, 8 Oct 2026
- SBOM formats
- It reads SPDX and CycloneDX SBOMs and can generate SPDX and CycloneDX output. · bomly.dev, 8 Oct 2026
- Support
- The project directs users to GitHub issues for bugs, discussions for questions and feedback, and its repository security policy for security reports. · bomly.dev, 8 Oct 2026
- Vulnerability enrichment
- Opt-in enrichment queries OSV, CISA KEV, deps.dev, ClearlyDefined, and endoflife.date for vulnerability and license data. · bomly.dev, 8 Oct 2026