A password that looks complicated cannot compensate for an unpatched vulnerability. In a story published by The Register on October 1, 2026, security leader Joe Brinkley described a penetration test in which a tester reportedly used the BlueKeep flaw to access a law firm’s Windows systems, then found plaintext passwords—including one the firm’s CISO recognized as his own.
What the reported penetration test found
The Register’s Avram Piltch reported Brinkley’s account of a test at a large national law firm, apparently conducted as due diligence on a smaller company the firm planned to acquire. Brinkley said he had assessed the same firm the previous year. According to his account, the firm spent “probably a half a million dollars” on security work while preparing for a merger and acquisition.
In the later test, Windows systems were still vulnerable to BlueKeep. Brinkley said the tester exploited the flaw, found passwords stored in plaintext and reached 2,500 of the organization’s computers. One password was a number-and-symbol substitution for “realgoodpassword”; the tester displayed it in an executive presentation, and the CISO reportedly identified it as his own.
These are details attributed to Brinkley in The Register’s report, not an independently verified breach record or official incident notice. The article does not name the law firm, give the exact test date, or establish the systems’ current status. The computer count and approximate spending figure are Brinkley’s reported figures, not independently audited totals.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
BlueKeep was a vulnerability, not a password attack
CVE-2019-0708, commonly called BlueKeep, is a Remote Desktop Protocol (RDP) vulnerability. In its June 17, 2019 advisory, CISA said the affected legacy Windows versions included Windows 2000, Vista, XP, Windows 7, Windows Server 2003, Server 2003 R2, Server 2008 and Server 2008 R2. That is the advisory’s affected-version list, not a statement that those products are currently supported.
CISA warned that an attacker could execute code remotely on a vulnerable system before authentication and described the flaw as wormable. In other words, an attacker did not first need to guess or steal a user’s password to exploit BlueKeep. CISA’s advisory states: “An attacker can exploit this vulnerability to perform remote code execution on an unprotected system.”
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
That distinction matters in this account. The reportedly exposed password was a serious, separate weakness, but it did not cause BlueKeep or make the vulnerability work. An unpatched RDP service created an entry point; plaintext credential storage and a weak, reused-looking password could compound the damage after access.
Why the password’s substitutions did not make it safe
Replacing letters with familiar numbers and symbols can make a password look more intricate without making it meaningfully hard to guess. A transformed phrase such as “realgoodpassword” still follows a predictable pattern. The account does not establish whether the CISO reused that password elsewhere, but reuse would allow a password exposed on one system to put other accounts at risk.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsRank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
Plaintext storage is another failure mode: if an attacker can read the system or a file containing credentials, the passwords are exposed in usable form rather than protected by secure storage. CISA’s ransomware guidance recommends unique, longer passwords, avoiding reuse, using a password manager, applying updates promptly and enabling multifactor authentication (MFA). For accounts accessing critical systems, it recommends phishing-resistant MFA where possible.
What organizations should do about exposed RDP systems
CISA’s BlueKeep advisory recommended applying available patches and testing them before installation. If an affected system cannot be patched immediately, the advisory’s mitigations reduce particular risks but do not remove the vulnerable condition.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
- Patch, or upgrade an end-of-life system. Installing the available security update addresses the vulnerability; upgrading is the appropriate path where the operating system is no longer supported.
- Disable unused services. If RDP is not needed, disabling it removes that service from the attack surface.
- Enable Network Level Authentication where applicable. CISA specifically advised enabling it on Windows 7 and Windows Server 2008 or 2008 R2. It is a mitigation for applicable systems, not a substitute for patching.
- Restrict RDP at the network perimeter where appropriate. CISA advised blocking TCP port 3389 at the enterprise perimeter when suitable. This can disrupt legitimate RDP access and does not necessarily prevent an unauthenticated attacker who can reach the service from inside the network.
For credentials, require unique passwords and use a password manager rather than relying on predictable substitutions. Add MFA, prioritizing phishing-resistant methods for accounts with access to critical systems. These controls address credential theft or reuse; they do not patch BlueKeep.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Why spending on security did not guarantee protection
Brinkley’s account illustrates the difference between paying for security work and consistently closing specific control gaps. The reported half-million-dollar figure is an approximation he gave to The Register, not an audited spend total, and the account does not specify what the work covered. It therefore cannot show that any particular product or service failed. It does show why an organization needs to verify that systems are patched, exposed services are controlled and credentials are protected—not assume those conditions from a budget or a prior assessment.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Best Value
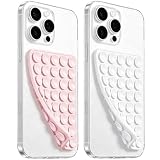
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
A useful response to a finding is operational: identify affected hosts, assign an owner and deadline, apply or document a mitigation, and verify remediation. Treat credential exposure as a separate incident: determine which accounts and systems were accessible, rotate affected credentials, check for reuse where possible, and strengthen storage and authentication controls.
The practical takeaway
BlueKeep could enable remote code execution without a password; a weak password and plaintext storage could then make an intrusion more damaging. The reported test is a reminder to manage vulnerabilities and credentials as distinct controls: patch or upgrade vulnerable systems, limit RDP exposure, store credentials securely, use unique passwords and require strong MFA for sensitive access.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




