Freedom251 › Software Composition Analysis Software
Twira Dependency Vulnerabilities
What Twira Dependency Vulnerabilities is
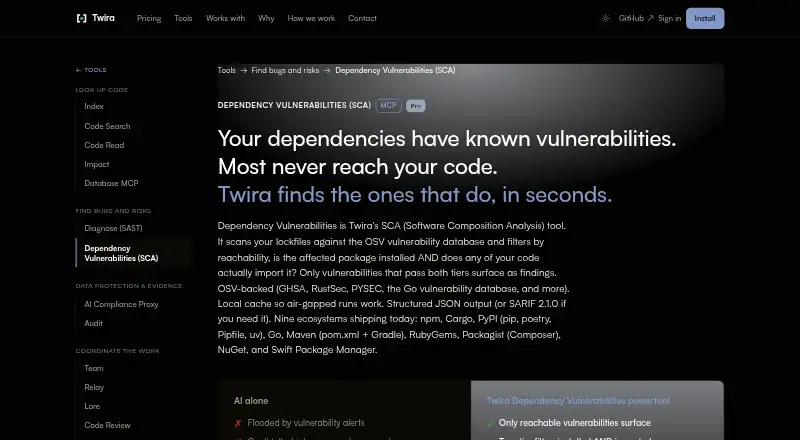
Twira Dependency Vulnerabilities is a software composition analysis tool for scanning dependency lockfiles against OSV. It reports vulnerabilities that pass installed-package and code-import reachability filters, covering npm, Cargo, PyPI, Go, Maven, RubyGems, Packagist, NuGet, and Swift Package Manager. Findings are provided as structured JSON by default or SARIF 2.1.0. After an initial synchronization, a local vulnerability-data cache with a 24-hour time-to-live supports offline and air-gapped scans. Accepted-risk suppressions remain through lockfile changes, while detections are recorded in an append-only Merkle audit chain. The same binary can run on a laptop, CI runner, or air-gapped environment, with self-hosted deployment available. Twira says indexing stays local, indexed content is not telemetered, and LLM calls use the customer’s provider and key. The tool is intended for developers and their AI agents, including security and compliance workflows. It has a free plan, while Pro is $29.99 a month with a 14-day trial.
Who it suits
It suits developers, AI agents, and security or compliance teams checking supported dependency ecosystems. Self-hosted, offline, and air-gapped options may fit organizations keeping indexing local.
What it does well
- Reachability filtering for findings
- Supports nine lockfile ecosystems
- JSON and SARIF output
- Offline and air-gapped scanning
- Self-hosted deployment
What to know first
- No SBOM generation
- No runtime or container scanning
- Several ecosystems remain unsupported
- Free plan does not list SCA
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | Personal use · Index, Code Search, and Code Read · 26 languages · SCA not listed | Free |
| Pro | Billed in USD; receipt localises to your country. · Full toolbelt · SCA with reachability filter · Free 14-day trial · Students with a valid .edu email get Pro free | $29.99 a month |
As twira.com lists them, read 9 Oct 2026. The maker's own page has the final word.
Verdict
Twira focuses on known dependency vulnerabilities with reachability analysis and deployment flexibility. Check its unsupported ecosystems and excluded scanning categories before relying on it for broader software supply-chain coverage.
Facts from Twira Dependency Vulnerabilities's own pages
- Company
- The maker identifies itself as Twira Ltd, registered in England and Wales, with a registered office in London. · twira.com, 9 Oct 2026
- Coverage limits
- The scanner covers application dependencies and known vulnerabilities; Twira says it does not detect novel malware, typosquatting, dependency confusion, or malicious-maintainer attacks. · twira.com, 9 Oct 2026
- Headquarters
- London, United Kingdom · twira.com, 28 Sept 2026
- Integration
- An agent can call dependency scanning through the Diagnose MCP tool with the security profile. · twira.com, 9 Oct 2026
- Intended users
- Twira describes the product as a tool for developers and their AI agents, including security and compliance workflows. · twira.com, 9 Oct 2026
- Not supported
- Dart Pub, Hex, Conan, and CocoaPods are not yet supported; the page also excludes SBOM export, licence analysis, runtime monitoring, and container, OS, or firmware scanning. · twira.com, 9 Oct 2026
- Offline use
- The local vulnerability-data cache has a 24-hour TTL and supports offline or air-gapped scans after an initial sync. · twira.com, 9 Oct 2026
- Output formats
- Findings are available as structured JSON by default or SARIF 2.1.0. · twira.com, 9 Oct 2026
- Privacy
- Twira says indexing runs locally, indexed content is not telemetered, and LLM calls go through the customer's chosen provider and key. · twira.com, 9 Oct 2026
- Purpose
- Twira Dependency Vulnerabilities is a software composition analysis tool that scans lockfiles against OSV and reports vulnerabilities that pass installed-package and code-import reachability filters. · twira.com, 9 Oct 2026
- Run locations
- Twira says the same binary can run on a laptop, CI runner, or in an air-gapped environment. · twira.com, 9 Oct 2026
- Supported ecosystems
- It supports lockfiles for npm, Cargo, PyPI, Go, Maven, RubyGems, Packagist, NuGet, and Swift Package Manager. · twira.com, 9 Oct 2026
- Suppression and audit
- Twira says accepted-risk suppressions persist through lockfile changes and each detection is recorded in an append-only Merkle audit chain. · twira.com, 9 Oct 2026
- Vulnerability data
- Twira says its vulnerability data comes from OSV, which aggregates GHSA, RustSec, PYSEC, the Go vulnerability database, and other ecosystem feeds. · twira.com, 9 Oct 2026