Freedom251 › Third-Party Risk Management Software
TERTIQ
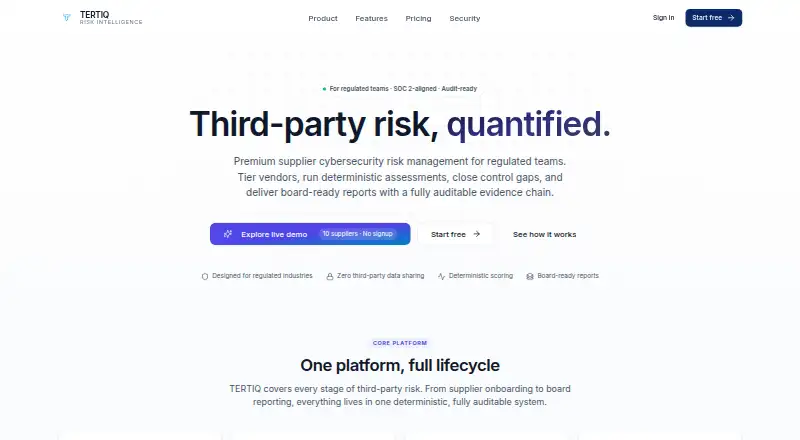
What TERTIQ is
TERTIQ is a web platform for managing cybersecurity risk across suppliers. Security and compliance teams can assess suppliers using tiered questionnaires, attach evidence such as policies and reports, identify control gaps, and assign remediation tasks with owners and deadlines. Its supplier scores use an explainable seven-factor inherent-risk model; the company says AI does not calculate the scores. Assessments cover areas including governance, access, data protection, incident response and business continuity. Reporting includes CSV exports and an executive Board Summary, while timestamped and attributed assessments, findings, attachments and remediation events can be exported for NIS2, ISO 27001, SOC 2 and GDPR workflows. Starter costs €79 a month and supports up to 20 suppliers and five team members. Business costs €199 a month, supports up to 100 suppliers and unlimited team members, and adds full assessments and executive dashboards. There is no free commercial plan, though a public demo is available. TERTIQ says it does not currently hold third-party certifications.
Who it suits
TERTIQ is designed for internal security and compliance teams, vCISOs, MSPs and consultants working with regulated or security-conscious businesses. It may suit teams that need supplier questionnaires, evidence records and tracked remediation.
What it does well
- Explainable supplier scoring uses a seven-factor model
- Questionnaires cover multiple security control areas
- Findings can be assigned owners and deadlines
- Exports and Board Summary support risk reporting
What to know first
- No free commercial plan
- Starter is limited to 20 suppliers and five team members
- The company says it holds no third-party certifications
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Business | €199/month · Up to 100 suppliers · Unlimited team members · Everything in Starter · Board summary reporting · Full assessments and control coverage · Advanced finding categorization · Executive-ready risk dashboards | €199 a month |
| Starter | €79/month · Up to 20 suppliers · Up to 5 team members · Supplier risk scoring · Tiered assessments · Evidence vault and review workflow · Findings and remediation tracking · Periodic reviews · Reports and CSV exports | €79 a month |
| Consultant / Custom | Contact sales · Custom supplier capacity · Custom deployment options · Tailored onboarding and support · Capacity scoped to engagement model | On request |
As tertiq.com lists them, read 9 Oct 2026. The maker's own page has the final word.
Verdict
TERTIQ combines supplier assessments, evidence collection, remediation tracking and reporting in a web platform. Teams should weigh its plan limits and the stated absence of third-party certifications against their requirements.
Facts from TERTIQ's own pages
- Assessments
- Tiered assessments use structured YES, PARTIAL, NO, and N/A responses across areas including governance, identity and access, data protection, vulnerability management, incident response, business continuity, and supply-chain security. · tertiq.com, 9 Oct 2026
- Audit trail
- Assessments, findings, attachments, and remediation events are timestamped, attributed, and exportable for NIS2, ISO 27001, SOC 2, and GDPR workflows. · tertiq.com, 9 Oct 2026
- Certifications
- TERTIQ states that it does not currently hold SOC 2, ISO 27001, NIS2, GDPR, or another third-party certification. · tertiq.com, 9 Oct 2026
- Evidence and remediation
- Teams can attach security reports, policies, certifications, and other documents to supplier assessments, then assign findings remediation actions, owners, deadlines, and progress states. · tertiq.com, 9 Oct 2026
- Free access
- There is no free commercial plan, but a public live demo can be explored without modifying production data. · tertiq.com, 9 Oct 2026
- Infrastructure
- The company says its platform runs on Vercel and stores primary data in Neon PostgreSQL, with database backups, point-in-time recovery, and replication handled by Neon. · tertiq.com, 9 Oct 2026
- Intended users
- It is designed for internal security and compliance teams, vCISOs, MSPs, and consultants working with regulated or security-conscious businesses. · tertiq.com, 9 Oct 2026
- Notable limits
- Starter supports up to 20 suppliers and 5 active team members; Business supports up to 100 suppliers and unlimited team members. · tertiq.com, 9 Oct 2026
- Privacy
- TERTIQ says it does not store full payment card numbers or card security codes in its own database; payment details go directly to Stripe. · tertiq.com, 9 Oct 2026
- Purpose
- TERTIQ is a third-party cybersecurity risk management platform for assessing suppliers, collecting security evidence, identifying control gaps, tracking remediation, and maintaining an auditable supplier-risk program. · tertiq.com, 9 Oct 2026
- Reporting
- TERTIQ includes risk reporting, CSV exports, and an executive Board Summary covering supplier risk, findings, remediation, and overall risk posture. · tertiq.com, 9 Oct 2026
- Risk scoring
- Supplier risk scoring is deterministic and explainable, based on a seven-factor inherent-risk model; the company says it does not use AI to calculate risk. · tertiq.com, 9 Oct 2026
- Security architecture
- The security page describes organization-scoped records, role-based access control with five roles, Auth.js passwordless email sign-in, and HTTPS traffic. · tertiq.com, 9 Oct 2026
- Support
- The pricing page offers tailored onboarding and support for Consultant / Custom plans and directs inquiries to [email protected]. · tertiq.com, 9 Oct 2026
Where TERTIQ stands on Freedom251
- Third-Party Risk Management Software#24 of 31