Freedom251 › Dynamic Application Security Testing Software
Safeguard DAST
What Safeguard DAST is
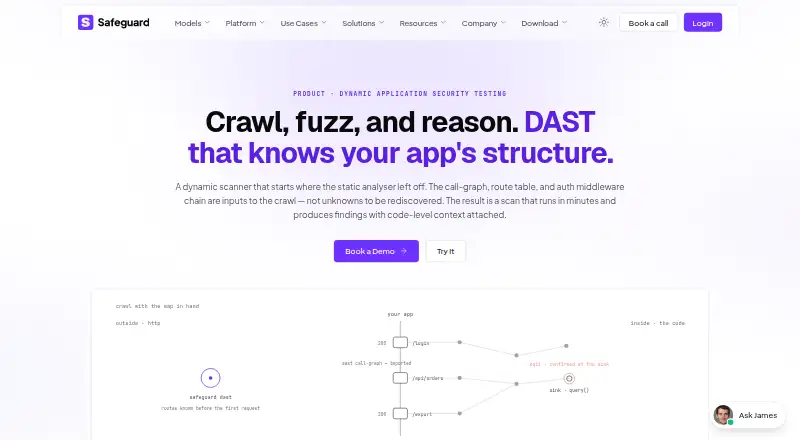
Safeguard DAST tests running applications and reports both security findings and how much of the discovered attack surface a scan reached. It uses Safeguard SAST call graphs, route tables, and authentication middleware to guide crawling, then generates payloads for SQL, OS command, SSRF, XSS, and deserialization risks based on expected parameter shapes. Endpoint discovery can draw on OpenAPI, GraphQL introspection, gRPC reflection, and live traffic samples. Supported authenticated flows include form auth, OAuth 2.0 with refresh, JWT bearer, session cookies, SAML, and mutual TLS. Scan modes include Fast, Deep, Progressive, and Reconnaissance; the last sends no probes. A Coverage Score explains reached attack surface and why scanning stopped. The product states coverage for the OWASP Top 10 and API Top 10. It also analyzes served JavaScript, JSON, and source maps for exposed credentials, routes, endpoints, and other data. A free plan is available; paid plans start at $9/mo. The DAST page itself does not state a product-specific price.
Who it suits
Safeguard DAST suits teams scanning live applications, including teams that need authenticated flows, API discovery, or CI integrations. Its self-hosted scanner option also supports internal-network and on-premises scanning.
What it does well
- Guides crawling with call graphs, route tables, and auth middleware.
- Supports multiple authenticated flows, including SAML and mutual TLS.
- Provides Fast, Deep, Progressive, and Reconnaissance scan modes.
- Lists GitHub Actions, GitLab CI, Buildkite, CircleCI, and Jenkins integrations.
- Redacts reported secret samples at detection time.
What to know first
- The DAST page does not state a product-specific price.
- Ownership verification is required before sending requests.
Getting started
- Open the Safeguard DAST product page and select “Try It” or request a demo.
- Use the web platform or set up the self-hosted scanner for internal or on-prem scanning.
- Verify ownership of the target before sending requests.
- Choose a scan mode and configure supported authentication or API discovery inputs.
- Connect a listed CI system if you want scans in that workflow.
Verdict
Safeguard DAST combines guided dynamic scanning with attack-surface coverage reporting and links findings to a shared SAST and SCA triage queue. Its listed free plan and CI integrations may suit teams seeking to incorporate runtime findings into development workflows.
Questions
Is Safeguard DAST free?
It has a free plan. The listed paid starting price is $9/mo, while the DAST page does not state a DAST-specific price.
Does it offer a free trial?
No free trial is listed; the product has a free plan.
Which platforms and deployment options are supported?
The listed platforms are web and self-hosted, and the deployment model is hybrid. Internal-network and on-prem scanning use a self-hosted scanner pod with mTLS to the control plane.
Which CI systems does it integrate with?
The listed integrations are GitHub Actions, GitLab CI, Buildkite, CircleCI and Jenkins.
What kinds of targets and endpoints can it scan?
It dynamically tests running applications and can discover endpoints from OpenAPI, GraphQL introspection, gRPC reflection and live traffic samples.
Who makes Safeguard DAST?
The product page footer identifies the company as Safeguard.sh Inc, headquartered in Dublin, California, United States.
Facts from Safeguard DAST's own pages
- API discovery
- Endpoint discovery draws on OpenAPI, GraphQL introspection, gRPC reflection, and live traffic samples. · safeguard.sh, 7 Oct 2026
- Authentication
- Supported authenticated flows include form auth, OAuth 2.0 with refresh, JWT bearer, session cookies, SAML, and mutual TLS. · safeguard.sh, 7 Oct 2026
- CI integrations
- The DAST page lists GitHub Actions, GitLab CI, Buildkite, CircleCI, and Jenkins integrations. · safeguard.sh, 7 Oct 2026
- Coverage
- The product page states full OWASP Top 10 and API Top 10 coverage. · safeguard.sh, 7 Oct 2026
- Coverage reporting
- A Coverage Score reports how much discovered attack surface the scan reached and why it stopped. · safeguard.sh, 7 Oct 2026
- Delta scans
- Subsequent scans focus on changes from the last clean run, and the page describes nightly delta scans as taking minutes. · safeguard.sh, 7 Oct 2026
- Deployment
- Internal-network and on-prem scanning is supported through a self-hosted scanner pod with mTLS to the control plane. · safeguard.sh, 7 Oct 2026
- Endpoint discovery
- It builds endpoint inventories from OpenAPI, GraphQL introspection, gRPC reflection and live traffic samples. · safeguard.sh, 7 Oct 2026
- Findings
- Findings can include the function and file reached by a request, the patch that introduced a regression, and a static call-graph annotation. · safeguard.sh, 7 Oct 2026
- Findings workflow
- DAST findings join the same ranked triage queue as Safeguard SAST and SCA results, with code-level context attached. · safeguard.sh, 7 Oct 2026
- Founded
- 2026 · safeguard.sh, 28 Sept 2026
- Graph-aware crawling
- The scanner uses Safeguard SAST call graphs, route tables, and authentication middleware to guide its crawl. · safeguard.sh, 7 Oct 2026
- Headquarters
- Dublin, California, United States · safeguard.sh, 28 Sept 2026
- Integrations
- The listed CI integrations are GitHub Actions, GitLab CI, Buildkite, CircleCI and Jenkins. · safeguard.sh, 7 Oct 2026
- JavaScript analysis
- DAST analyzes served JavaScript, JSON, and source maps for exposed credentials, API endpoints, routes, cloud-storage references, personal data, configuration, and developer comments. · safeguard.sh, 7 Oct 2026
- Maker
- The DAST page footer identifies the company as Safeguard.sh Inc and lists its headquarters at 7779 Topaz Circle, Dublin, California 94568, United States. · safeguard.sh, 7 Oct 2026
- Pricing
- The DAST page offers a demo and a “Try It” button but does not state a DAST-specific price. · safeguard.sh, 7 Oct 2026
- Purpose
- Safeguard DAST dynamically tests running applications and reports attack surface coverage alongside findings. · safeguard.sh, 7 Oct 2026
- Scan modes
- The launch page lists Fast, Deep, Progressive, and Reconnaissance scan modes, with Reconnaissance sending no probes. · safeguard.sh, 7 Oct 2026
- Scanning
- It generates targeted SQL, OS command, SSRF, XSS and deserialization payloads based on expected parameter shapes. · safeguard.sh, 7 Oct 2026
- Secret handling
- Reported secret samples are redacted at detection time, and the launch page says raw credentials are not stored or returned. · safeguard.sh, 7 Oct 2026
- Target authorization
- Ownership verification is required before requests are sent, and requests are gated by scope, rate, and budget limits. · safeguard.sh, 7 Oct 2026
- Targeted fuzzing
- It generates payloads for sink classes including SQL, OS command, SSRF, XSS, and deserialization, informed by expected parameter shapes. · safeguard.sh, 7 Oct 2026
- Triage
- DAST findings join SAST and SCA results in a shared ranked queue, with cross-links between runtime hits and related SAST findings. · safeguard.sh, 7 Oct 2026