Freedom251 › Container Engines
runc
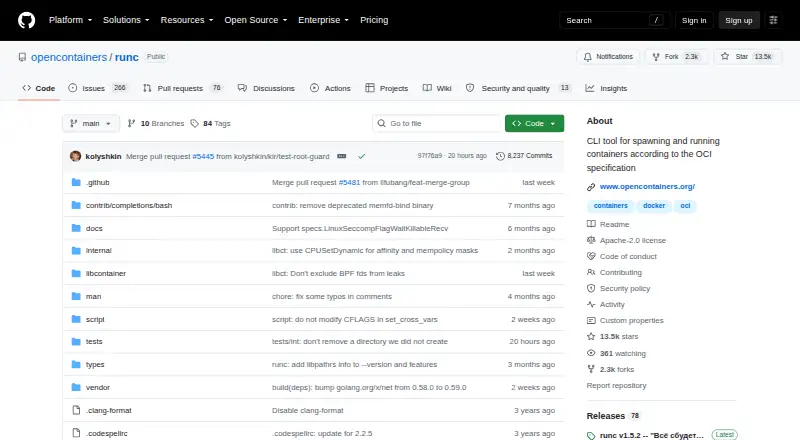
What runc is
runc is a free Linux command-line tool that spawns and runs containers according to the Open Container Initiative specification. It operates at a low level and is generally intended for higher-level container software rather than direct use by most people. Each container must be supplied as an OCI bundle, and the spec command can generate a base configuration. A container can run with one command or through separate create, start, list, and delete operations. Rootless execution is available when Linux kernel user namespaces are enabled. Build features include seccomp system-call filtering and libpathrs path safety, with an option to disable checkpoint and restore. Documentation covers use with Docker for preparing a root filesystem and with systemd or other process supervisors. runc supports Linux only, does not build images or run Windows containers, and uses the Apache 2.0 license. Official releases are signed, and a Cure53 security audit is documented.
Who it suits
runc suits developers and operators building Linux container systems or integrating a low-level runtime into higher-level software. It is less suited to people seeking a standalone container management interface.
What it does well
- Free OCI container runtime
- Supports rootless containers with user namespaces
- Offers separate container lifecycle commands
- Seccomp filtering enabled by default
- Apache 2.0 licensed
What to know first
- Linux hosts only
- Requires containers in OCI bundle format
- Not recommended for most direct users
- Does not build images
Verdict
runc supplies the low-level Linux runtime capabilities behind container software. Its OCI bundle requirement, Linux-only scope, and command-line design make it an infrastructure component rather than a general desktop tool.
Facts from runc's own pages
- Build features
- Build tags include seccomp syscall filtering, libpathrs path safety, and an option to disable checkpoint and restore. · github.com, 8 Oct 2026
- Checkpoint and restore
- runc supports checkpoint and restore unless built with the runc_nocriu tag, which disables that feature. · github.com, 8 Oct 2026
- Container format
- A container must be provided as an OCI bundle, and runc can generate a base configuration with its spec command. · github.com, 8 Oct 2026
- Integrations
- The project documents using runc with Docker to prepare a root filesystem and with systemd or other process supervisors to manage containers. · github.com, 8 Oct 2026
- Intended users
- The project describes runc as a low-level tool mostly used by higher-level container software, and does not recommend using it directly for most users. · github.com, 8 Oct 2026
- License
- The code and documentation are released under the Apache 2.0 license. · github.com, 8 Oct 2026
- Lifecycle
- runc can run a container with one command or manage it through separate create, start, list, and delete operations. · github.com, 8 Oct 2026
- OCI bundles
- To use runc, a container must be provided in OCI bundle format. · github.com, 8 Oct 2026
- Path safety
- The libpathrs build feature provides path safety and is enabled by default in the listed build tags. · github.com, 8 Oct 2026
- Platform limit
- The project states that runc only supports Linux. · github.com, 8 Oct 2026
- Purpose
- runc is a command-line tool for spawning and running containers on Linux according to the OCI specification. · github.com, 8 Oct 2026
- Release integrity
- The project says all official releases are signed by one of the keys listed in the repository's runc.keyring file. · github.com, 8 Oct 2026
- Release signing
- The project says all official runc releases are signed by one of the keys listed in its repository keyring. · github.com, 8 Oct 2026
- Rootless mode
- runc can run containers without root privileges when user namespaces are enabled in the kernel. · github.com, 8 Oct 2026
- Security audit
- The project says a third-party security audit was performed by Cure53 and links to the report. · github.com, 8 Oct 2026
- Security feature
- The project lists seccomp syscall filtering as a build feature enabled by default, using libseccomp. · github.com, 8 Oct 2026
- Security reporting
- The OCI security policy directs vulnerability reports to [email protected] rather than GitHub issues or pull requests. · github.com, 8 Oct 2026
Where runc stands on Freedom251
- Container Engines#26 of 31
- Container Runtime Software#25 of 28