Freedom251 › Software Composition Analysis Software
Retire.js
What Retire.js is
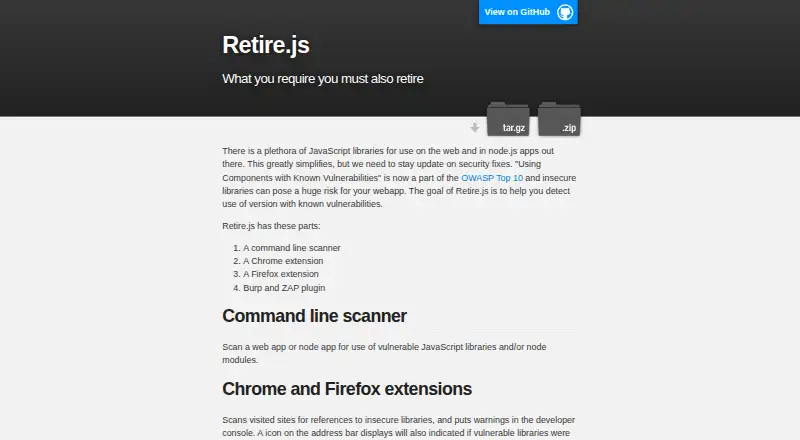
Retire.js is a free, self-hosted scanner for identifying JavaScript libraries and Node.js modules with known vulnerabilities. Its command-line scanner checks web apps and Node.js projects, including libraries stored directly in source control, and requires Node.js and npm to install and run. Chrome and Firefox extensions scan visited sites and report insecure libraries through the developer console and browser toolbar. The Chrome extension is not officially available in the Chrome Web Store, and the Firefox extension is deprecated. Other options include a Burp extension, an OWASP ZAP add-on, and headless website scanning through retire-site-scanner. Retire.js can generate CycloneDX SBOM output in JSON formats, including variants with a vulnerabilities section. By default, the command-line scanner exits with code 13 when it finds vulnerabilities; the documentation says this behavior can be overridden with --exitwith 0. The Grunt plugin and Gulp task are marked deprecated. The project is distributed under Apache License 2.0, which grants a no-charge, royalty-free license subject to its terms.
Who it suits
Retire.js suits developers and security teams checking web applications or Node.js projects for vulnerable JavaScript dependencies. Its integrations and SBOM output may be useful for teams with related scanning or inventory workflows.
What it does well
- Scans web apps and Node.js projects.
- Can scan websites in headless mode.
- Provides Burp and OWASP ZAP integrations.
- Generates CycloneDX SBOM output.
- Free and distributed under Apache License 2.0.
What to know first
- CLI requires Node.js and npm.
- Firefox extension is deprecated.
- Chrome extension is not officially available in its store.
- Grunt plugin and Gulp task are deprecated.
Limits
The Firefox extension is deprecated, the Chrome extension is not officially available in the Chrome Web Store, and the Grunt plugin and Gulp task are deprecated. The command-line scanner requires Node.js and npm.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Retire.js | Open-source scanner and related tools | Free |
As retirejs.github.io lists them, read 12 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Retire.js project website.
- Install Node.js and npm to use the command-line scanner.
- Use the command-line scanner to check a web app or Node.js project.
- Choose a browser extension for visited-site scanning, noting the stated Chrome and Firefox availability.
- Use the Burp extension, OWASP ZAP add-on, or retire-site-scanner project for those workflows.
Verdict
Retire.js offers command-line, browser, and integration-based scanning, along with CycloneDX SBOM generation. Note the deprecated browser and build-tool components, and the CLI’s default exit code when vulnerabilities are found.
Questions
How much does Retire.js cost?
The Retire.js plan is free.
What does Retire.js scan?
Its command-line scanner checks web apps and Node.js projects for vulnerable JavaScript libraries and Node.js modules. Browser extensions scan visited sites.
Which platforms are listed?
The listed platforms are API, extension, Linux, macOS, self-hosted, web, and Windows.
Does Retire.js generate SBOMs?
Yes. It can generate CycloneDX SBOM output, including JSON formats and variants with a vulnerabilities section.
Which integrations are available?
Retire.js has a Burp extension and an OWASP ZAP add-on. The Grunt plugin and Gulp task are deprecated.
Who maintains Retire.js?
The project site identifies Erlend Oftedal as a maintainer.
Facts from Retire.js's own pages
- Browser availability
- The README says the Chrome extension is not officially available in the Chrome Web Store and the Firefox extension is deprecated. · github.com, 11 Oct 2026
- Browser extensions
- Chrome and Firefox extensions scan visited sites and show warnings in the developer console and browser toolbar. · github.com, 11 Oct 2026
- Browser scanning
- The browser extensions scan visited sites and report insecure libraries in the developer console and through an address-bar icon. · github.com, 12 Oct 2026
- Chrome status
- The Chrome extension is not officially available in the Chrome Web Store. · github.com, 12 Oct 2026
- CLI scanning
- The command-line scanner scans web apps and Node.js projects for vulnerable JavaScript libraries and Node.js modules. · github.com, 12 Oct 2026
- Command-line scanner
- The command-line scanner checks web apps and Node.js apps for vulnerable JavaScript libraries and Node.js modules. · github.com, 11 Oct 2026
- Deprecated integrations
- The Grunt plugin and Gulp task are marked deprecated. · github.com, 12 Oct 2026
- Detection limit
- The README says the Firefox extension is deprecated and asks for a maintainer to resume its development. · github.com, 11 Oct 2026
- Firefox status
- The Firefox extension is marked deprecated, and the maintainers invite someone to maintain it. · github.com, 12 Oct 2026
- Funding
- The project says donations fund maintenance of the tool and vulnerability repository. · github.com, 12 Oct 2026
- Headless scanning
- The retire-site-scanner project can scan websites in headless mode. · github.com, 12 Oct 2026
- Integrations
- Retire.js has a Burp plugin and an OWASP ZAP add-on; ZAP officially supports its add-on and includes it in weekly releases. · github.com, 12 Oct 2026
- License
- The project is published under the Apache-2.0 license. · github.com, 12 Oct 2026
- Maintainer
- The project site identifies Erlend Oftedal as a maintainer. · retirejs.github.io, 11 Oct 2026
- Other deprecated integrations
- The README marks the Grunt plugin and Gulp task as deprecated. · github.com, 11 Oct 2026
- Purpose
- Retire.js detects JavaScript library versions with known vulnerabilities, including libraries that are not listed in package manifests. · github.com, 12 Oct 2026
- Runtime requirement
- The command-line scanner requires Node.js and npm to install and run. · github.com, 12 Oct 2026
- SBOM
- Retire.js can generate CycloneDX SBOMs in XML and JSON, including newer JSON formats with vulnerability sections. · github.com, 12 Oct 2026
- Support and contributions
- The project README invites users to contribute to the scanner and vulnerability repository and says donations fund their maintenance. · github.com, 11 Oct 2026
- Vulnerability exit behavior
- By default, the command-line scanner exits with code 13 when it finds vulnerabilities, and its documentation says this can be overridden with --exitwith 0. · github.com, 12 Oct 2026