Freedom251 › Network Protocol Analyzers
PacketSense
What PacketSense is
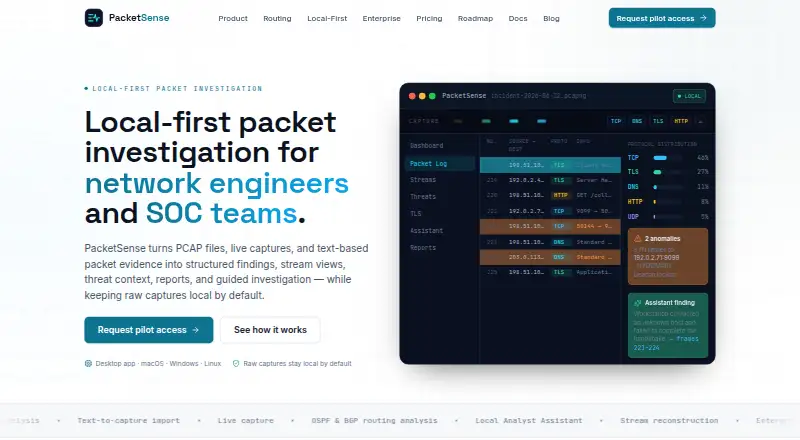
PacketSense is paid desktop software for investigating network evidence from PCAP and PCAPNG files, live local captures, text captures, FortiGate logs, and hex dumps. It organizes evidence into packet details, protocol categories, reconstructed streams, routing observations, threat context, and reports. Users can filter packet logs, inspect bytes, follow streams, and reconstruct HTTP, TCP, or UDP-style conversations when the capture contains enough evidence. It can reconstruct observed OSPF and BGP behavior, including adjacencies, sessions, topology, prefixes, and policy evidence. The on-device Local Analyst Assistant summarizes evidence, suggests next steps, and links conclusions to packet frames. Threat hunting includes anomaly summaries, local rules, and optional intelligence enrichment. Reports and CSV or PCAP slices retain packet-level traceability. Raw captures remain local by default, while cloud AI is off unless enterprise explicitly enables and approves it. PacketSense supports Windows, macOS, and Linux, offers a 14-day trial, and has no free plan.
Who it suits
PacketSense suits network engineers, SOC analysts, and incident responders analyzing local captures and packet evidence on Windows, macOS, or Linux.
What it does well
- Supports PCAP and PCAPNG
- Local Analyst Assistant
- Routing reconstruction for OSPF and BGP
- Evidence-linked reports and exports
- Raw captures local by default
What to know first
- No free plan
- Pricing is set per engagement
- No traffic decryption
- No remote capture
Limits
There is no free plan. The 14-day trial provides evaluation access; pilot pricing is set per engagement during beta, and plan details require contacting QuantamQ.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Trial | Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. · Full local evaluation; PCAP and text import; live capture; Local Analyst Assistant; threat hunting; reports | On request |
| Enterprise | Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. · Enterprise governance; admin seats; seat and device management; cloud AI policy; allowed-provider controls; local-only policy; intelligence-update policy; enterprise support path | On request |
| Individual | Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. · Single analyst workstation; offline analysis; PCAP and text import; live capture | On request |
| Pro | Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. · Everything in Individual; Local Analyst Assistant; guided diagnosis; threat hunting; reports; MITRE-style investigation support | On request |
As packetsense.com lists them, read 8 Oct 2026. The maker's own page has the final word.
Getting started
- Open the PacketSense website
- Request current pilot pricing from QuantamQ
- Start the 14-day trial
- Install the desktop application on Linux, macOS, or Windows
- Import PCAP, text, log, or hex evidence, or begin a live capture
Verdict
PacketSense focuses on evidence-based desktop investigation, combining packet, stream, routing, and threat-hunting views with local-by-default data handling. Its pilot status, engagement-based pricing, and lack of decryption or remote capture define important boundaries.
Questions
What platforms does PacketSense support?
It runs on Linux, macOS, and Windows as desktop software.
Is there a free plan?
No. PacketSense offers a 14-day trial, with pilot pricing set per engagement.
Does PacketSense upload captures?
Raw captures stay local by default, and license checks do not upload capture data. Cloud AI is off by default and requires enterprise approval.
Can it capture traffic remotely?
No. Its capture sources are local, and remote capture is not supported.
Does PacketSense decrypt traffic?
No, traffic decryption is not provided.
Facts from PacketSense's own pages
- Assistant
- The on-device Local Analyst Assistant summarizes capture evidence, suggests next steps, and links conclusions to packet frames. · packetsense.com, 8 Oct 2026
- Data handling
- Raw captures stay local by default, and the site says license checks do not upload capture data. · packetsense.com, 8 Oct 2026
- Enterprise controls
- Enterprise controls include local-only mode, allowed AI providers, audit detail, remote export settings, intelligence-update behavior, and seat and device inventory. · packetsense.com, 8 Oct 2026
- Inputs
- It accepts PCAP and PCAPNG files, live captures from interfaces, text captures, FortiGate logs, and hex dumps. · packetsense.com, 8 Oct 2026
- Not a continuous monitor
- PacketSense works from capture evidence and is not described as a continuous monitoring platform. · packetsense.com, 8 Oct 2026
- Optional cloud AI
- Cloud AI is off by default and the site says enterprise must explicitly enable and approve it. · packetsense.com, 8 Oct 2026
- Packet inspection
- Its packet log includes filtering, protocol categorization, packet details and bytes, context actions, and follow-stream navigation. · packetsense.com, 8 Oct 2026
- Product status and pricing
- PacketSense is in active pilot development, and the maker says pilot pricing is set per engagement with no prices published until finalized. · packetsense.com, 8 Oct 2026
- Purpose
- PacketSense turns PCAP files, live captures, and text-based packet evidence into structured findings, stream views, threat context, reports, and guided investigation. · packetsense.com, 8 Oct 2026
- Reports and exports
- PacketSense provides evidence-backed reports and CSV or PCAP slices with packet-level traceability. · packetsense.com, 8 Oct 2026
- Routing analysis
- It reconstructs observed OSPF and BGP behavior from captures, including adjacencies, sessions, topology, prefixes, and policy evidence. · packetsense.com, 8 Oct 2026
- Stream reconstruction
- PacketSense reconstructs HTTP, TCP, and UDP-style conversations where the capture supports it and identifies when evidence is insufficient. · packetsense.com, 8 Oct 2026
- Threat hunting
- Threat hunting includes anomaly summaries, local rules, and threat-intelligence enrichment where configured. · packetsense.com, 8 Oct 2026
- Users
- The product is presented for network engineers, SOC analysts, and incident responders. · packetsense.com, 8 Oct 2026
Where PacketSense stands on Freedom251
- Network Protocol Analyzers#30 of 30