Freedom251 › OT and ICS Security Monitoring Software
OTDefend
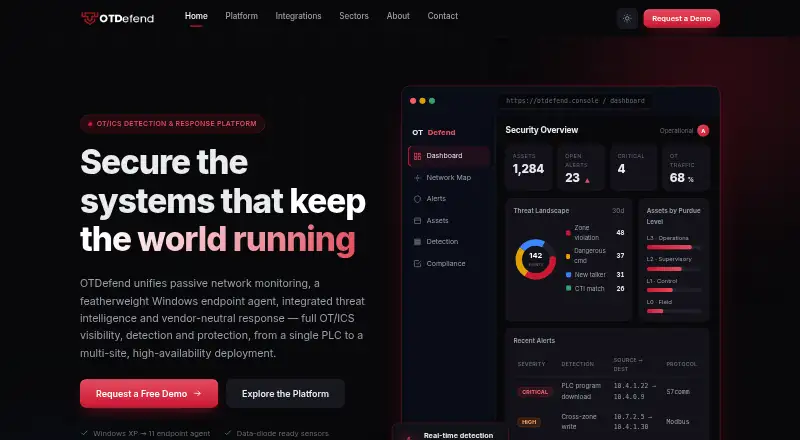
What OTDefend is
OTDefend provides passive monitoring, threat detection, vulnerability management, and response for industrial environments. Its network intrusion detection inspects more than 16 industrial protocols through a mirror or TAP port; the company says this does not inject traffic. A dependency-free Windows agent, compatible with Windows XP through Windows 11, collects host inventory and intrusion-detection events. Detection combines network IDS signatures, Sigma analytics, and YARA signatures, with 688 rules stated on the homepage. The threat-intelligence store accepts TAXII 2.1 and STIX 2.1 feeds and matches indicators against live traffic. Deployment options include an offline Docker bundle, a .deb sensor, and a bootable appliance ISO. Listed integrations include SIEM, endpoint, service-management, and network-security products such as Splunk, IBM QRadar, ServiceNow, Jira, Fortinet FortiGate, and Palo Alto Networks. OTDefend also lists exportable compliance reports for IEC 62443, NERC CIP, and NIS2. It is available for Linux, Windows, web, API, and self-hosted use. Pricing is on request; the company offers a free personalized demo and consultation.
Who it suits
OTDefend is aimed at industrial environments, including critical infrastructure in energy, manufacturing, water, and oil and gas. It may suit teams needing passive network monitoring, OT asset discovery, threat intelligence, and compliance reporting.
What it does well
- Passive inspection covers more than 16 industrial protocols
- Windows agent supports Windows XP through Windows 11
- Deployment options include offline Docker and bootable ISO
- Free personalized demo and consultation offered
What to know first
- Pricing is available on request
- Emergency 24/7 support depends on the support plan
- Technical support hours are listed as Monday–Friday
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Custom solution | Solution proposal and pricing tailored to your needs | On request |
As otdefend.com lists them, read 5 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the OTDefend website and request a solution proposal and pricing.
- Arrange the free personalized demo and consultation; standard demos last about 45–60 minutes.
- Choose a deployment route: offline Docker bundle, .deb sensor, or bootable appliance ISO.
- Use the passive network sensor from a mirror or TAP port and, where needed, the Windows agent for host inventory and intrusion-detection events.
- Connect listed security and service-management integrations as required.
OTDefend is a paid OT/ICS security platform for industrial operators that need passive visibility across network traffic and Windows hosts. It suits critical-infrastructure teams in sectors such as energy, manufacturing, water, and oil and gas. The main attraction is its combination of broad protocol coverage, host events, threat-intelligence matching, and deployable sensors; the main buying constraint is custom pricing.
Overview
OTDefend provides passive OT/ICS monitoring, asset discovery, vulnerability management, threat detection, and response. Its network IDS reads traffic from a mirror or TAP port and does not inject traffic, making it appropriate for sensitive operational environments where active probing is undesirable.
Protocol support covers Modbus TCP and RTU, S7comm, DNP3, EtherNet/IP, IEC-104, IEC 61850, PROFINET, EtherCAT, POWERLINK, CC-Link IE, OPC UA, BACnet, FINS, MELSEC, and HART-IP. That breadth is useful on mixed-vendor sites, although organizations should match the list against their own equipment and traffic.
Key features
Network and host visibility
Passive inspection and OT asset discovery provide inventory and traffic context without sending packets into the control network. A dependency-free Windows agent runs from Windows XP through Windows 11 and collects host inventory and intrusion-detection events. This creates a useful network-plus-host view for Windows-heavy plants, while teams needing equivalent agents on other operating systems should assess their coverage separately.
Detection and intelligence
The detection engine combines network IDS signatures, Sigma analytics, and YARA signatures; OTDefend states that it has 688 rules. Its threat-intelligence store accepts TAXII 2.1 and STIX 2.1 feeds and matches indicators against live traffic, giving teams a way to apply their own intelligence alongside built-in detections.
Deployment, integrations, and governance
Deployment options include an offline Docker bundle, a .deb sensor, and a bootable appliance ISO. This range supports disconnected or tightly controlled environments as well as conventional server deployments. Integrations include Splunk, IBM QRadar, CrowdStrike Falcon, Microsoft Defender, SentinelOne, ServiceNow, Jira, Fortinet FortiGate, Palo Alto Networks, and Check Point, with SIEM integration available.
OTDefend describes per-tenant isolation, role-based access, an active/standby core, and one-way sensors for data-diode segments. Compliance reporting covers IEC 62443, NERC CIP, and NIS2, with exportable PDF reports. These controls and reports are particularly relevant to regulated operators that must separate tenants, protect segmented networks, and document compliance work.
Pricing
Custom solution
Custom solution uses a tailored proposal and custom pricing rather than a published rate. It is the only stated plan, so buyers should expect a sales-led scope and cost discussion rather than a self-serve purchase or transparent per-seat comparison. A free personalized demo and consultation is offered without obligation; standard demonstrations run about 45–60 minutes. Technical support is listed Monday–Friday, 9:00 AM–6:00 PM, while emergency 24/7 support depends on the support plan.
Platforms
OTDefend is offered through API, Linux, self-hosted, web, and Windows environments. The offline Docker bundle, .deb sensor, and appliance ISO give infrastructure teams several ways to place components in industrial networks, including segmented settings. The Windows agent’s XP-to-11 range is a practical advantage for plants with older workstations.
Who it's for
OTDefend is aimed at critical-infrastructure and industrial security teams in energy, manufacturing, water, and oil and gas. It is a strong fit when passive monitoring, broad industrial-protocol coverage, Windows host telemetry, threat-feed matching, and compliance exports must work together. Smaller organizations or buyers seeking a fixed public price may find the custom-sales process less suitable.
Pros and cons
Pros
- Passive architecture: Mirror- or TAP-based inspection avoids injecting traffic into sensitive OT networks.
- Wide protocol coverage: Support for 16 named industrial protocols helps on heterogeneous sites.
- Combined telemetry: Network detections, Windows host events, asset discovery, and vulnerability management provide broader context than network-only monitoring.
- Flexible deployment: Offline Docker, .deb, and bootable ISO options accommodate different operational constraints.
- Operational integrations: SIEM, endpoint, ticketing, firewall, and case-management integrations can connect findings to existing workflows.
- Compliance output: IEC 62443, NERC CIP, and NIS2 reporting with PDF export supports audit preparation.
Cons
- Custom pricing: There is no published cost for the custom solution, making budget comparison difficult.
- Support varies by plan: Emergency 24/7 assistance is tied to the selected support plan rather than assured for every customer.
- Windows-focused host coverage: The stated agent targets Windows, so other endpoint requirements need separate validation.
Alternatives
Choose Nozomi Networks Platform instead if you want a free Nozomi Vantage SaaS option used to license hardware and Guardian nodes, with cloud-hosted security infrastructure and API, Linux, self-hosted, and web platforms.
EmberOT is the better choice when a free OT PCAP Analyzer for protocol and device breakdown is the immediate need; a school or business email is required to download it.
Consider Honeywell Forge when you need Honeywell's product-specific offerings across a wider mobile, desktop, API, and web platform mix, with pricing handled by product and sales contact.
FactoryTalk Analytics is another paid option for teams seeking an analytics platform spanning API, Linux, web, and Windows environments.
Kaspersky Industrial CyberSecurity Platform suits enterprise OT/IoT environments where a demo or sales engagement is acceptable.
Radiflow iSID is an alternative self-hosted and web platform with pricing handled through a demo or direct contact.
Claroty CTD fits buyers seeking on-premises federal OT cybersecurity controls and mobile flyaway kits.
Claroty xDome is the alternative for a modular SaaS platform sold through a pricing inquiry.
For a broader category comparison, browse OT and ICS Security Monitoring Software.
Verdict
Choose OTDefend if your industrial security program needs passive, protocol-aware monitoring combined with Windows telemetry, threat-intelligence feeds, integrations, and compliance reporting. Look elsewhere if transparent pricing or guaranteed emergency support terms are essential before a sales conversation.
Verdict
OTDefend combines passive network inspection with host events, threat-intelligence matching, and compliance reporting for industrial environments. Its deployment choices and integrations span several operating contexts, while pricing and emergency support terms require a direct inquiry.
Questions
How much does OTDefend cost?
Pricing is available on request, with a solution proposal tailored to the buyer's needs.
Is there a free plan or trial?
The listed offer is a free personalized demo and consultation with no obligation. No free software plan or trial is described.
What deployment options are available?
OTDefend lists an offline Docker bundle, a .deb sensor, and a bootable appliance ISO. Its listed platforms are API, Linux, self-hosted, web, and Windows.
Which industrial protocols does it support?
The list includes Modbus TCP and RTU, S7comm, DNP3, EtherNet/IP, IEC-104, IEC 61850, PROFINET, EtherCAT, POWERLINK, CC-Link IE, OPC UA, BACnet, FINS, MELSEC, and HART-IP.
Which integrations are listed?
They include Splunk, IBM QRadar, CrowdStrike Falcon, Microsoft Defender, SentinelOne, ServiceNow, Jira, Fortinet FortiGate, Palo Alto Networks, and Check Point.
Who makes OTDefend?
OTDefend was founded in 2025 and lists its headquarters in Ankara, Turkey.
Facts from OTDefend's own pages
- Audience
- The site describes OTDefend for critical infrastructure sectors including energy, manufacturing, water, and oil and gas. · otdefend.com, 5 Oct 2026
- Compliance
- The platform lists IEC 62443, NERC CIP and NIS2 compliance reporting, including exportable PDF reports. · otdefend.com, 5 Oct 2026
- Deployment
- The site lists an offline Docker bundle, a .deb sensor and a bootable appliance ISO as deployment options. · otdefend.com, 5 Oct 2026
- Detection content
- The detection engine combines network IDS signatures, Sigma analytics and YARA signatures, with 688 rules stated on the homepage. · otdefend.com, 5 Oct 2026
- Founded
- OTDefend says it was founded in 2025. · otdefend.com, 5 Oct 2026
- Free demo
- OTDefend offers a free personalized demo and consultation, with no obligation; the site says standard demos last about 45–60 minutes. · otdefend.com, 5 Oct 2026
- Headquarters
- Ankara, Turkey · otdefend.com, 28 Sept 2026
- Integrations
- Listed integrations include Splunk, IBM QRadar, CrowdStrike Falcon, Microsoft Defender, SentinelOne, ServiceNow, Jira, Fortinet FortiGate, Palo Alto Networks and Check Point. · otdefend.com, 5 Oct 2026
- Network inspection
- Its passive network IDS inspects 16+ industrial protocols from a mirror or TAP port and says it does not inject traffic. · otdefend.com, 5 Oct 2026
- Purpose
- OTDefend provides passive OT/ICS monitoring, threat detection, vulnerability management and response for industrial environments. · otdefend.com, 5 Oct 2026
- Security design
- The platform describes per-tenant isolation, role-based access, an active/standby core and one-way sensors for data-diode segments. · otdefend.com, 5 Oct 2026
- Support
- Technical support is listed for Monday–Friday, 9:00 AM–6:00 PM, with emergency 24/7 support based on the support plan. · otdefend.com, 5 Oct 2026
- Threat intelligence
- The built-in threat-intelligence store accepts TAXII 2.1 and STIX 2.1 feeds and matches indicators against live traffic. · otdefend.com, 5 Oct 2026
- Training
- OTDefend says it offers online and on-site training programs. · otdefend.com, 5 Oct 2026
- Windows agent
- A dependency-free agent runs on Windows XP through Windows 11 and collects host inventory and intrusion-detection events. · otdefend.com, 5 Oct 2026