Freedom251 › Container Registries
Keppel
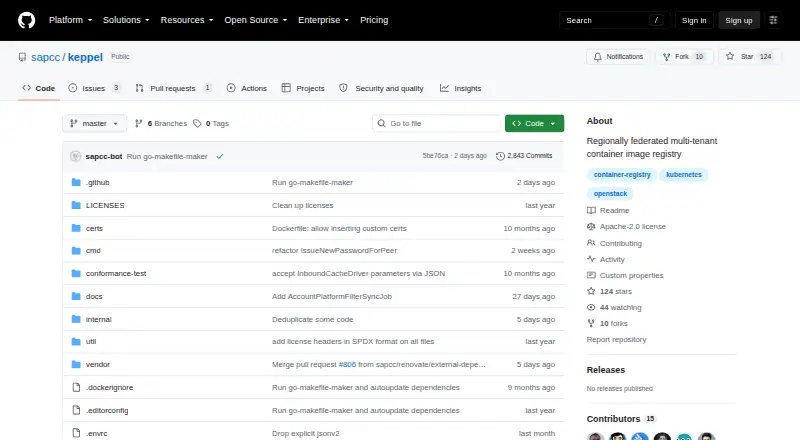
What Keppel is
Keppel is a free, Apache-2.0-licensed container image registry for regionally federated, multi-tenant deployments. Its storage drivers give each customer separate backing storage, allowing quotas and usage tracking by account. Keppel fully implements the OCI Distribution API and adds APIs for tenant, repository, manifest, and tag metadata. Instances in different regions or network segments can share account namespaces and replicate accounts with matching names. It supports Docker images and lists, OCI manifests and indexes, and OCI artifacts. Online garbage collection runs without scheduled downtime or operator intervention, and Trivy can scan registry contents for vulnerabilities. Deployments require one or more API servers and exactly one janitor; liquidapi, healthmonitor, and anycastmonitor are optional. PostgreSQL is listed for the database, while Redis is optional for compatible authentication and rate-limit drivers. Server components expose Prometheus metrics, and audit events can be sent to RabbitMQ when configured. Keppel runs through API, Linux, or self-hosted deployments.
Who it suits
Keppel fits operators managing multi-tenant registries across regions or network segments who can run the required services and external drivers. It is suited to teams wanting open-source deployment and OCI-compatible storage.
What it does well
- Separate storage supports per-account quotas and usage tracking
- OCI Distribution API is fully implemented
- Replication works across regions or network segments
- Online garbage collection avoids scheduled downtime
- Trivy vulnerability scanning is supported
What to know first
- A deployment needs exactly one janitor
- PostgreSQL is required for the database
- Several capabilities depend on external pluggable services
- Redis is optional rather than built in
Verdict
Keppel provides a federated OCI registry with tenant-aware storage, replication, scanning, and online cleanup. Its free license and self-hosted model suit operators comfortable assembling the required components and external integrations.
Facts from Keppel's own pages
- Audit events
- Audit events can be sent to RabbitMQ when audit trail configuration is enabled; otherwise they are written only to the debug log. · github.com, 11 Oct 2026
- Build and deploy
- The project says to build with make, install with make install, or use docker build; its binary contains client and server commands. · github.com, 11 Oct 2026
- Deployment
- The project says to build with make, install with make install, or build a Docker image; server and client commands are in one binary. · github.com, 11 Oct 2026
- Deployment components
- A complete deployment requires one or more API servers and exactly one janitor; liquidapi, healthmonitor, and anycastmonitor are optional components. · github.com, 11 Oct 2026
- External services
- Keppel uses pluggable auth, storage, federation, inbound cache, account management, and optional rate limit drivers that connect to external services. · github.com, 11 Oct 2026
- Federation
- Keppel instances in different regions or network segments can share account namespaces and replicate between accounts with the same name. · github.com, 11 Oct 2026
- Garbage collection
- Online garbage collection runs without scheduled downtime or operator intervention. · github.com, 11 Oct 2026
- Integrations
- The operator guide describes optional integration with Limes through the liquidapi server and vulnerability scanning through a configured Trivy instance. · github.com, 11 Oct 2026
- License
- The repository lists the Apache-2.0 license. · github.com, 11 Oct 2026
- Monitoring
- All server components expose Prometheus metrics at the /metrics endpoint. · github.com, 11 Oct 2026
- Product
- Keppel is a regionally federated, multi-tenant container image registry. · github.com, 11 Oct 2026
- Registry API
- Keppel fully implements the OCI Distribution API and also provides a custom API for multitenancy and repository, manifest, and tag metadata. · github.com, 11 Oct 2026
- Security reporting
- The project directs security reports to its security policy and asks users not to file security issues as GitHub issues. · github.com, 11 Oct 2026
- Storage
- Each customer account gets separate backing storage, allowing storage quota and usage to be tracked by that storage. · github.com, 11 Oct 2026
- Storage and database requirements
- The operator guide lists PostgreSQL for the database and supports optional Redis for compatible authentication and rate-limit drivers. · github.com, 11 Oct 2026
- Storage model
- It uses multi-tenant-aware storage drivers to give each customer separate storage space, allowing quotas and usage to be tracked by the backing storage. · github.com, 11 Oct 2026
- Support and contributions
- The project accepts feature requests and bug reports through GitHub issues and welcomes contributions and feedback. · github.com, 11 Oct 2026
- Support and security reporting
- The project accepts feature requests and bug reports through GitHub issues and directs security reports to its security policy rather than public issues. · github.com, 11 Oct 2026
- Supported manifest formats
- Keppel supports Docker images and image lists, OCI image manifests, and OCI image indexes. · github.com, 11 Oct 2026
- Vulnerability scanning
- Keppel can use Trivy to scan registry contents for vulnerabilities. · github.com, 11 Oct 2026
Where Keppel stands on Freedom251
- Container Registries#22 of 60