Freedom251 › Open Source License Compliance Software
FOSSLight Hub
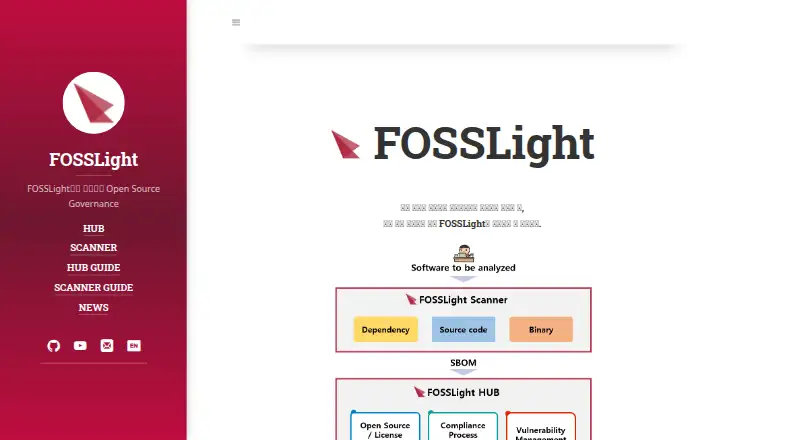
What FOSSLight Hub is
FOSSLight Hub is an open-source tool for managing software components, licenses, vulnerabilities, software bills of materials, and compliance work. Teams can register open-source software and license information in bulk, review license restrictions, generate open-source notices, verify disclosed source, and track issues. Its project BOMs cover both open-source and proprietary software, support SPDX, and let users search projects by software. The listed SBOM import formats are SPDX and CycloneDX. Teams can also track third-party software and agreements as projects.
A project’s Security tab records vulnerability findings from its SBOM, with a configurable score threshold and resolution status. For open-source entries without a version, the tab does not show vulnerability lists by ID because verification depends on having a version. The documented REST API can return project vulnerability information as JSON and accept analyzed open-source reports. Projects can assign a registered Hub user to security-related Jira issues; if no responsible person is designated, the issue creator is assigned by default.
FOSSLight Hub is free and released under AGPL-3.0. The maker documents self-hosted installation through Docker or Docker Compose, or Java with Java 11 or higher, MariaDB 10.0 or higher or MySQL 5.6 or higher, and at least 8 GB memory.
Who it suits
FOSSLight Hub suits teams handling software distribution, internal transfers, B2B delivery, internal-only software, self-checks, or open-source contributions. It is relevant to teams that need project BOMs, license and vulnerability management, and compliance workflows, including Jira issue assignment and REST API access.
What it does well
- Free and released under the AGPL-3.0 license.
- Manages open-source and proprietary software in project BOMs.
- Imports SBOMs in SPDX and CycloneDX formats.
- Tracks vulnerability findings with thresholds and resolution status.
- Documents Docker, Docker Compose, and Java installation routes.
What to know first
- The Java installation requires Java 11 or higher and a supported database.
- Java deployment requires at least 8 GB memory.
- Vulnerability lists by ID are unavailable for OSS entries without a version.
Limits
The free plan costs nothing and is released under AGPL-3.0. Java installation requires Java 11 or higher, MariaDB 10.0 or higher or MySQL 5.6 or higher, and at least 8 GB memory. Vulnerability lists by ID are not shown for open-source entries without a version.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| FOSSLight Hub | Released under AGPL-3.0; self-hosted installation is documented | Free |
As fosslight.org lists them, read 7 Oct 2026. The maker's own page has the final word.
Getting started
- Open https://fosslight.org/.
- Choose a documented self-hosted installation route: Docker, Docker Compose, or Java.
- For Java installation, prepare Java 11 or higher, MariaDB 10.0 or higher or MySQL 5.6 or higher, and at least 8 GB memory.
- Use the LGE-only Hub or FOSSLight Enterprise only if applicable; Enterprise requires a separate account.
- For account inquiries, contact [email protected].
Verdict
Choose FOSSLight Hub if your team needs a free, self-hosted tool for BOMs, licenses, vulnerabilities, and compliance workflows. Consider the Java prerequisites when choosing that installation route, and account for the version requirement when reviewing vulnerability findings by ID.
Questions
How much does FOSSLight Hub cost?
The FOSSLight Hub plan is free.
Is FOSSLight Hub open source?
Yes. It is released under the AGPL-3.0 license.
Which SBOM formats does it support?
The listed import formats are SPDX and CycloneDX. Its SBOM features also support SPDX.
How can it be installed?
The maker documents Docker and Docker Compose installation, or a Java installation. Java installation requires Java 11 or higher, MariaDB 10.0 or higher or MySQL 5.6 or higher, and at least 8 GB memory.
Can it track project vulnerabilities through an API?
The documented REST API can query project vulnerability information as JSON and upload analyzed open-source reports.
What is the vulnerability version caveat?
The Security tab does not show vulnerability lists by ID for open-source entries without a version, because accurate verification depends on the version.
Facts from FOSSLight Hub's own pages
- Access
- The guide lists an LGE-only Hub and FOSSLight Enterprise, which requires a separate account; account inquiries go to [email protected]. · fosslight.org, 7 Oct 2026
- Automation
- The documented REST API can query project vulnerability information as JSON and upload analyzed open source reports. · fosslight.org, 7 Oct 2026
- Compliance
- It supports an all-in-one compliance process, including generating open source notices, verifying disclosed source, and tracking issues. · github.com, 7 Oct 2026
- Deployment
- The maker documents Docker and Docker Compose installation, or a Java installation requiring Java 11 or higher, MariaDB 10.0 or higher or MySQL 5.6 or higher, and at least 8 GB memory. · fosslight.org, 7 Oct 2026
- Intended users
- Project distribution types include general software distribution, internal transfer, B2B, internal-only software, self-check, and open source contribution. · fosslight.org, 7 Oct 2026
- Jira workflow
- A project can designate a registered Hub user as the responsible person assigned to security-related Jira issues; the creator is assigned by default if none is designated. · fosslight.org, 7 Oct 2026
- License
- The Hub is released under the AGPL-3.0 open source license. · fosslight.org, 7 Oct 2026
- License management
- It manages open source information, license restrictions, and vulnerabilities, with bulk registration for open source and licenses. · github.com, 7 Oct 2026
- Purpose
- FOSSLight Hub manages open source, licenses, vulnerabilities, project BOMs, and open source compliance workflows. · fosslight.org, 7 Oct 2026
- SBOM
- It manages open source and proprietary software in SBOMs, supports SPDX, and can search projects by software. · github.com, 7 Oct 2026
- Security
- The project Security tab tracks vulnerability findings from the project SBOM, with a configurable vulnerability score threshold and resolution status. · fosslight.org, 7 Oct 2026
- Supply chain
- It can manage third-party software and agreements as projects. · github.com, 7 Oct 2026
- Vulnerability data caveat
- The Security tab does not show vulnerability lists by ID for OSS entries without a version, because accurate vulnerability verification is difficult without that version. · fosslight.org, 7 Oct 2026