Freedom251 › Dark Web Monitoring Services
DarkThreat
What DarkThreat is
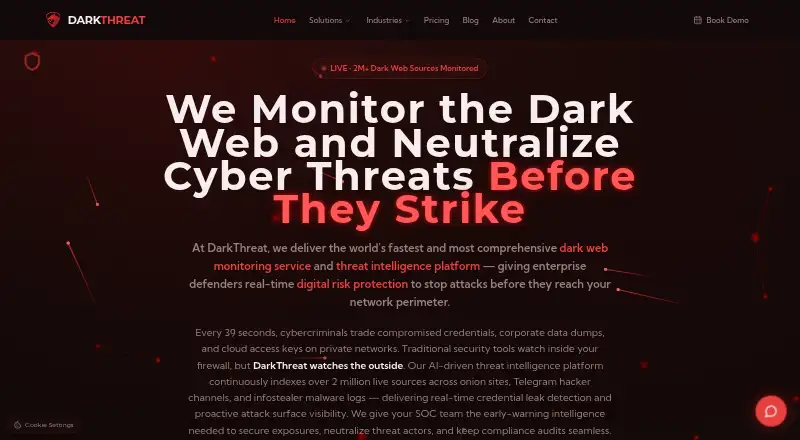
DarkThreat is a web and API platform for monitoring dark web exposure, corporate credentials and attack surfaces. It continuously indexes more than 2 million live sources, including onion sites, Telegram hacker channels and infostealer malware logs. Its Asset Exposure Engine maps domains, IP ranges, cloud buckets, shadow IT and third-party integrations. The Credential Leak Monitor searches combination lists, malware outputs and marketplaces for corporate emails, Active Directory credentials, VPN tokens and cloud API keys. Findings are connected to threat actors, adversary techniques, ransomware programs, CVEs and MITRE ATT&CK techniques. A 24/7 Security Operations Center validates alerts and recommends remediation; email and dashboard alerts typically arrive within minutes of discovery. The service is agentless, requiring no software installation or internal changes. It supports API polling, syslog push and webhooks, with field-mapping templates for Splunk, Microsoft Sentinel, QRadar, LogRhythm and ELK Stack. Standard costs $2,000 a year and covers one domain and one user. Enterprise costs $3,400 a year, with two domain/IP coverages, two users and priority support. MSSP adds a white-label portal, multi-tenant API, bulk onboarding, dedicated support and priority threat intelligence.
Who it suits
DarkThreat suits organizations seeking monitoring for exposed domains, credentials, tokens and other listed data, including businesses in financial services, healthcare, critical infrastructure, legal and technology. Its API and SIEM delivery options fit security teams that route alerts into tools such as Splunk or Microsoft Sentinel.
What it does well
- Indexes over 2 million live sources continuously.
- Maps domains, cloud buckets, shadow IT and third-party integrations.
- SOC validates alerts and recommends remediation.
- Supports API, syslog and webhook SIEM delivery.
- Agentless operation requires no software installation or internal changes.
What to know first
- Standard is $2,000 a year.
- Standard covers one domain and one user.
- No free plan is offered.
Limits
The 7-day trial is the listed trial period. Standard covers one domain and one user; Enterprise covers two domain/IP coverages and two users.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Standard | per year · Basic breach & credential monitoring · 1 x Domain coverage · 1 User · Email notifications · Web UI access | $2,000 a year |
| Enterprise | per year · Full domain & hacker chatter feeds · 2 x Domain/IP coverage · 2 Users · Priority support | $3,400 a year |
| MSSP | White-label portal · Multi-tenant API · Bulk onboarding · Dedicated support · Priority threat intelligence | On request |
As darkthreat.ai lists them, read 1 Oct 2026. The maker's own page has the final word.
Getting started
- Open https://www.darkthreat.ai/.
- Choose Standard or Enterprise; the listed annual prices are 2000.00 USD and 3400.00 USD.
- Use the 7-day trial to evaluate the service.
- Access the service through its web interface or API.
- Connect alerts through email, webhooks, API polling or syslog as needed.
Verdict
Choose DarkThreat if you need agentless dark web and credential monitoring with validated, enriched alerts and remediation guidance. Standard is limited to one domain and one user; organizations needing broader coverage or priority support must consider Enterprise, while MSSP pricing is not included here.
Questions
Is there a free plan?
No. DarkThreat is listed as paid, with a 7-day trial.
What does Standard cost?
Standard costs $2,000 a year, billed yearly.
What does Standard include?
It includes basic breach and credential monitoring, one domain, one user, email notifications and web UI access.
What platforms does DarkThreat support?
The listed platforms are web and API.
Which SIEM tools have field-mapping templates?
Templates are listed for Splunk, Microsoft Sentinel, QRadar, LogRhythm and ELK Stack.
What does Enterprise cost?
Enterprise costs $3,400 a year, billed yearly.
Facts from DarkThreat's own pages
- Agentless setup
- DarkThreat operates as a fully agentless service requiring no software installation or internal changes. · darkthreat.ai, 1 Oct 2026
- Alert delivery
- Its threat-intelligence platform provides email, webhook and SIEM delivery for SOC-ready alerts. · darkthreat.ai, 1 Oct 2026
- Alert timing
- The platform provides real-time alerts by email and dashboard, typically within minutes of discovery. · darkthreat.ai, 1 Oct 2026
- Attack surface mapping
- Its Asset Exposure Engine maps domains, IP ranges, cloud buckets, shadow IT and third-party integrations. · darkthreat.ai, 1 Oct 2026
- Compliance alignment
- The service supports alignment with ISO 27001, the NIST Cybersecurity Framework, GDPR, HIPAA and PCI-DSS. · darkthreat.ai, 1 Oct 2026
- Credential detection
- The Credential Leak Monitor scans combination lists, malware outputs and marketplaces for corporate emails, Active Directory credentials, VPN tokens and cloud API keys. · darkthreat.ai, 1 Oct 2026
- Dark web monitoring
- The AI-driven platform continuously indexes over 2 million live sources across onion sites, Telegram hacker channels and infostealer malware logs. · darkthreat.ai, 1 Oct 2026
- Ease of use
- The company says no technical expertise is required and its dashboard provides threat summaries, risk scores and actionable recommendations. · darkthreat.ai, 1 Oct 2026
- Founded
- 2024 · darkthreat.ai, 28 Sept 2026
- Security controls
- DarkThreat says it uses encryption for transmission and storage, stores only cryptographic hashes rather than actual passwords, and operates SOC 2-compliant infrastructure with regular security audits. · darkthreat.ai, 1 Oct 2026
- SIEM integrations
- DarkThreat supports API polling, syslog push and webhook delivery, with field-mapping templates for Splunk, Microsoft Sentinel, QRadar, LogRhythm and ELK Stack. · darkthreat.ai, 1 Oct 2026
- SOC validation
- A 24/7 Security Operations Center validates alerts and provides recommended remediation. · darkthreat.ai, 1 Oct 2026
- Support tiers
- Enterprise includes priority support, while MSSP includes dedicated support and priority threat intelligence. · darkthreat.ai, 1 Oct 2026
- Target customers
- DarkThreat says more than 500 enterprises use it across financial services, healthcare, critical infrastructure, legal firms and technology companies. · darkthreat.ai, 1 Oct 2026
- Threat enrichment
- Validated alerts are mapped to threat actor groups, adversary TTPs, active ransomware programs, CVE vulnerabilities and MITRE ATT&CK techniques. · darkthreat.ai, 1 Oct 2026
Where DarkThreat stands on Freedom251
- Dark Web Monitoring Services#8 of 25