Freedom251 › Data recovery software
BreadCrumb
What BreadCrumb is
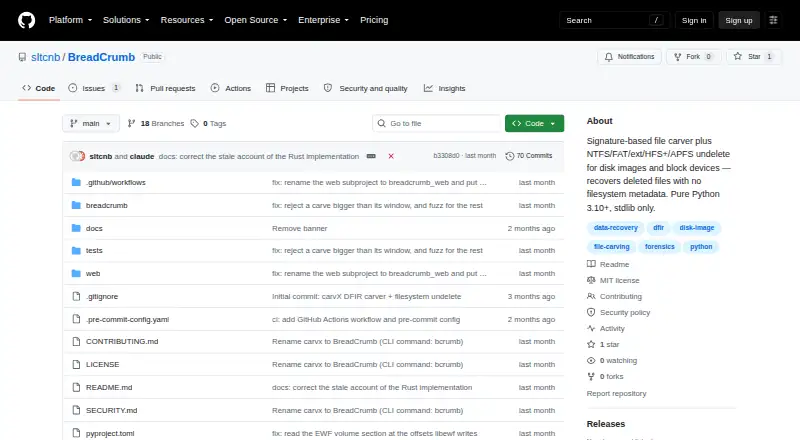
BreadCrumb is a free forensic file-carving and recovery tool for Linux, macOS, and Windows. It scans block devices and disk images for deleted files by signature, including formatted, corrupted, or unknown filesystems. Inputs include raw and split images, EWF/E01, QCOW2, and VMDK, detected automatically. Filesystem-aware modes support NTFS, ext2/3/4, FAT12/16/32, exFAT, HFS+/HFSX, and APFS, including memory-card sources. Listed signatures cover JPEG, PNG, PDF, ZIP, SQLite, MP4, Outlook stores, Windows event logs, and Apple binary plists. Reports can include JSON manifests, optional CSV, Sleuth Kit bodyfiles, HTML reports, and deletion timelines. An optional Flask interface accepts images, shows progress, and supports result downloads. BitLocker volumes can be read with supported credentials in read-only mode. BreadCrumb requires Python 3.10 or later and uses the standard library, with optional extras for specific capabilities. Carving recovers intact contiguous files but does not restore original names or timestamps.
Who it suits
BreadCrumb suits digital forensics, incident response, and data-recovery work across desktop operating systems. It is useful when sources include memory cards, block devices, or supported image formats.
What it does well
- Free and open under the MIT License
- Runs on Linux, macOS, and Windows
- Reads many image formats automatically
- Exports multiple report formats
- Analyzes sources without modifying them
What to know first
- Requires Python 3.10 or later
- Carving needs contiguous intact files
- Original names and timestamps are not restored
- TRIMmed SSD blocks read as zeros
Verdict
BreadCrumb offers broad, read-only recovery and reporting capabilities without a listed price. Its file-contiguity, encryption, and SSD limitations should guide recovery expectations.
Facts from BreadCrumb's own pages
- BitLocker
- It can read supported BitLocker volumes using a recovery key, password, startup key file, or raw FVEK, with decryption described as read-only. · github.com, 12 Oct 2026
- Carving limits
- Signature carving recovers intact files only when they are contiguous and does not restore original filenames or timestamps. · github.com, 12 Oct 2026
- Credential handling
- The security policy warns that BitLocker credentials passed on the command line may appear in shell history and process lists, and says worker processes receive credentials through an environment variable not written to disk. · github.com, 12 Oct 2026
- Filesystem undelete
- Its filesystem-aware modes support NTFS, ext2/3/4, FAT12/16/32, exFAT, HFS+/HFSX, and APFS. · github.com, 12 Oct 2026
- File types
- The README lists signatures for formats including JPEG, PNG, PDF, ZIP, SQLite, MP4, Outlook stores, Windows event logs, and Apple binary plists. · github.com, 12 Oct 2026
- Free plan
- Yes · github.com, 19 Sept 2026
- Image support
- The README says disk images can be raw, split raw, EWF/E01, QCOW2, or VMDK, with formats detected automatically. · github.com, 12 Oct 2026
- Input formats
- It auto-detects raw and split images, EWF/E01, QCOW2, and VMDK disk images. · github.com, 12 Oct 2026
- Installation
- The project can be installed with pip or run as a Python module and requires Python 3.10 or later. · github.com, 12 Oct 2026
- Integrations
- The README documents Sleuth Kit bodyfile output and JSON-lines events for wrapping in a GUI or pipeline. · github.com, 12 Oct 2026
- Intended users
- The repository describes BreadCrumb as a forensic file carver and tags it for data recovery and digital forensics and incident response. · github.com, 12 Oct 2026
- License
- The repository includes an MIT License granting permission to use, copy, modify, distribute, and sell copies of the software subject to its conditions. · github.com, 12 Oct 2026
- Maintenance status
- The security policy describes the project as pre-1.0 and says only the latest main branch receives security fixes. · github.com, 12 Oct 2026
- Memory card recovery
- Yes · github.com, 19 Sept 2026
- Operating systems
- The project says it runs on Linux, macOS, and Windows, including raw device access. · github.com, 12 Oct 2026
- Optional dependencies
- Pillow, libewf-python, and pyahocorasick are optional extras for image validation and JPEG bifragment recovery, broader EWF support, and faster matching with large signature sets. · github.com, 12 Oct 2026
- Operating systems
- Linux,macOS,Windows · github.com, 19 Sept 2026
- Other recovery limits
- The README says TRIMmed SSD blocks read as zeros and that LUKS and FileVault volumes must already be unlocked. · github.com, 12 Oct 2026
- Platform support
- The README says BreadCrumb runs on Linux, macOS, and Windows, including raw device access. · github.com, 12 Oct 2026
- Purpose
- BreadCrumb scans disk images and block devices for deleted files by signature, including on formatted, corrupted, or unknown filesystems. · github.com, 12 Oct 2026
- Recovery limits
- The README says carving reliably recovers only contiguous files and does not restore original filenames or timestamps; TRIMmed SSD blocks read as zeros cannot be recovered. · github.com, 12 Oct 2026
- Reporting
- The tool can write a JSON manifest and optionally export CSV, Sleuth Kit bodyfiles, HTML reports, and MACB timelines. · github.com, 12 Oct 2026
- Reports
- It can produce a JSON manifest, optional CSV and Sleuth Kit bodyfile exports, HTML reports, and deletion timelines. · github.com, 12 Oct 2026
- Runtime
- The command-line tool uses Python 3.10+ and the standard library; Pillow, libewf-python, pyahocorasick, and cryptography are optional extras for specific capabilities. · github.com, 12 Oct 2026
Where BreadCrumb stands on Freedom251
- Data recovery software#30 of 128