Freedom251 › AI Red Teaming Tools
Advent Prompt Pwn
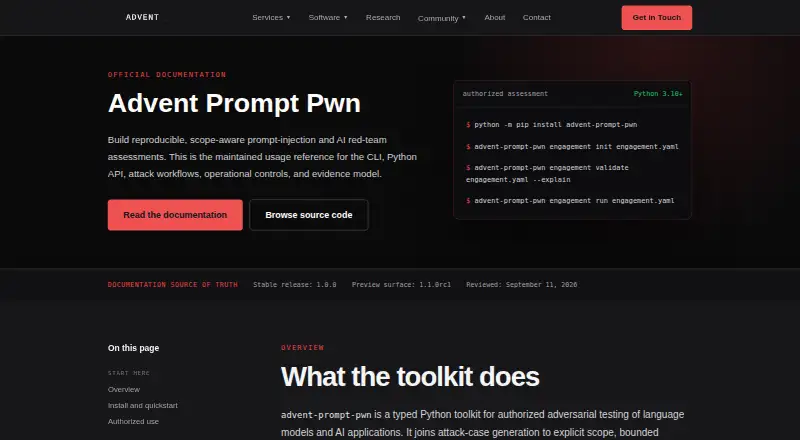
What Advent Prompt Pwn is
Advent Prompt Pwn is an open-source Python toolkit for authorized adversarial testing of language models and AI applications. It connects attack-case generation with defined scope, bounded runs, outcome checks, resumable checkpoints, reports, and regression comparisons. Its documented strategies include direct prompt injection, instruction override, delimiter, encoding, role confusion, indirect injection, and multi-turn testing. Mutation and RAG poisoning are preview features in the 1.1 source line. Built-in checks cover strings, canary leaks, regular expressions, JSON keys and paths, and tool calls, including combinations. Targets include custom HTTP JSON APIs, OpenAI-compatible APIs, Ollama, and Python callbacks, with preview adapters for OpenAI, Azure OpenAI, Anthropic, and Gemini. Remote assessments can use host and port allowlists, DNS checks, authorization windows, and limits on requests and workload. Reports are available in JSON, JSONL, Markdown, HTML, JUnit, and SARIF; evidence bundles include checksums and per-attempt SHA-256 hashes. The toolkit has a Python API, runs on Linux, macOS, and Windows, and requires Python 3.10 or newer. Advent Cybersecurity LLC maintains it; the maker identifies Jashid Sany as its founder. Version 1.0.0 is the stable public release, and the source is Apache-2.0 licensed.
Who it suits
It suits security practitioners assessing language models and AI applications on systems they own, in intentionally vulnerable labs, on public research benchmarks, or with explicit written authorization. Teams that need bounded runs, reviewable evidence, and reports in testing or security formats may find its workflow useful.
What it does well
- Covers direct, indirect, and multi-turn attack strategies.
- Checks strings, canary leaks, JSON paths, and tool calls.
- Supports HTTP JSON APIs, OpenAI-compatible APIs, Ollama, and Python callbacks.
- Scopes remote runs with host, port, DNS, and workload controls.
- Exports six report formats and hashed evidence bundles.
- Open-source under Apache-2.0 with Linux, macOS, and Windows platforms.
What to know first
- Requires Python 3.10 or newer.
- Oracle matches need practitioner review.
- Redaction may miss sensitive values.
- The static tool sandbox is not a production agent runtime.
Limits
Version 1.0.0 is the stable release; the 1.1 source line remains beta pending independent practitioner review and field assessment. Oracle matches require practitioner review, redaction may miss sensitive values, and the static tool sandbox is not a production agent runtime.
Getting started
- Open the Advent Prompt Pwn project page.
- Use a PowerShell, macOS, or Linux shell for the documented installation route.
- Install Python 3.10 or newer.
- Configure cases, targets, scope, runs, and reports through the Python API.
- Limit assessments to owned systems, intentionally vulnerable labs, public research benchmarks, or targets with explicit written authorization.
Verdict
Choose Advent Prompt Pwn if you need an open-source toolkit for authorized adversarial assessments with explicit scope controls and structured reports. Look elsewhere if you need a production agent runtime or expect oracle results and redaction to work without practitioner review.
Questions
Is Advent Prompt Pwn free?
Yes. It is free and open source under the Apache-2.0 license.
Which platforms does it support?
The listed platforms are Linux, macOS, and Windows. Installation requires Python 3.10 or newer.
What systems can it assess?
Targets include custom HTTP JSON APIs, OpenAI-compatible APIs, Ollama, and Python callbacks. Preview adapters are listed for OpenAI, Azure OpenAI, Anthropic, and Gemini.
What reports can it produce?
It supports JSON, JSONL, Markdown, HTML, JUnit, and SARIF reports.
Who maintains the toolkit?
Advent Cybersecurity LLC maintains it; the maker identifies Jashid Sany as its founder.
Where can I contact the maker?
The documentation lists [email protected].
Facts from Advent Prompt Pwn's own pages
- Assessment workflow
- It connects attack case generation to explicit scope, bounded execution, deterministic oracles, resumable checkpoints, reporting, and regression comparison. · adventcybersecurity.com, 5 Oct 2026
- Attack coverage
- Strategies cover direct, instruction override, delimiter, encoding, role confusion, indirect injection, and multi-turn attacks, with mutation and RAG poisoning listed as 1.1 preview features. · adventcybersecurity.com, 5 Oct 2026
- Attack features
- Documented strategies include direct, instruction override, delimiter, encoding, role confusion, indirect injection, and multi-turn testing. · adventcybersecurity.com, 5 Oct 2026
- Availability
- Installation requires Python 3.10 or newer and is documented for PowerShell, macOS, or Linux shells. · adventcybersecurity.com, 5 Oct 2026
- Evidence and reports
- It produces JSON, JSONL, Markdown, HTML, JUnit, and SARIF reports, plus evidence bundles with checksums and per-attempt SHA-256 hashes. · adventcybersecurity.com, 5 Oct 2026
- Evidence handling
- Evidence bundles include a checksum manifest and per-attempt SHA-256 hashes; the documentation says to treat model output as confidential assessment material. · adventcybersecurity.com, 5 Oct 2026
- Integrations
- Targets include custom HTTP JSON APIs, OpenAI-compatible APIs, Ollama, Python callbacks, and preview adapters for OpenAI, Azure OpenAI, Anthropic, and Gemini. · adventcybersecurity.com, 5 Oct 2026
- Known limitations
- Oracle matches require practitioner review, redaction may miss sensitive values, and the static tool sandbox is not a production agent runtime. · adventcybersecurity.com, 5 Oct 2026
- Known limits
- Oracle matches require practitioner review, redaction may miss sensitive values, and the static tool sandbox is not a production agent runtime. · adventcybersecurity.com, 5 Oct 2026
- License
- The project’s GitHub page identifies the source as Apache License 2.0. · github.com, 5 Oct 2026
- Maker
- The product is maintained by Advent Cybersecurity LLC; the maker page identifies Jashid Sany as its founder. · github.com, 5 Oct 2026
- Maturity
- Version 1.0.0 is the stable public release; the 1.1 source line remains beta pending independent practitioner review and field assessment. · adventcybersecurity.com, 5 Oct 2026
- Outcome checks
- Built-in oracles can check strings, canary leaks, regular expressions, JSON keys and paths, and tool calls, including combined conditions. · adventcybersecurity.com, 5 Oct 2026
- Platforms
- Installation instructions specify Python 3.10 or newer and show use from PowerShell, macOS, or Linux shells. · adventcybersecurity.com, 5 Oct 2026
- Purpose
- Advent Prompt Pwn is a typed Python toolkit for authorized adversarial testing of language models and AI applications. · adventcybersecurity.com, 5 Oct 2026
- Python API
- The toolkit provides a Python API for configuring cases, targets, scope, runs, and reports. · adventcybersecurity.com, 5 Oct 2026
- Reports
- Supported report formats are JSON, JSONL, Markdown, HTML, JUnit, and SARIF. · adventcybersecurity.com, 5 Oct 2026
- Scope controls
- Remote assessments support exact host and port allowlists, authorization windows, DNS controls, and request, rate, concurrency, retry, timeout, and evidence limits. · adventcybersecurity.com, 5 Oct 2026
- Security controls
- Remote assessments can be bounded by exact host and port grants, DNS checks, authorization windows, request limits, and workload ceilings. · adventcybersecurity.com, 5 Oct 2026
- Security handling
- Credentials are referenced by environment-variable names, and built-in HTTP clients disable redirects, ignore ambient proxy variables, and bound response bytes. · adventcybersecurity.com, 5 Oct 2026
- Support contact
- The documentation lists [email protected]. · adventcybersecurity.com, 5 Oct 2026
- Targets and integrations
- Targets include custom HTTP JSON, OpenAI-compatible APIs, Ollama, and preview integrations for OpenAI, Azure OpenAI, Anthropic, and Gemini. · adventcybersecurity.com, 5 Oct 2026
- Use restriction
- The maker says to use the toolkit only on owned systems, intentionally vulnerable labs, public research benchmarks, or targets with explicit written authorization. · adventcybersecurity.com, 5 Oct 2026
Where Advent Prompt Pwn stands on Freedom251
- AI Red Teaming Tools#6 of 27