What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Generative AI is a serious new risk factor for open-source software, but current evidence does not show that it has become the ecosystem’s single biggest threat. AI can produce insecure code, obscure provenance and licensing obligations, and accelerate attacks and maintenance work. It also helps find vulnerabilities, write patches, and review changes. The practical response is to treat AI output and AI-system dependencies as untrusted contributions that require the same security discipline as any other code.
What exactly is the threat?
“AI risk” is not one problem. It covers at least three layers that should be assessed separately: code generated for an open-source project, the supply chain of an application that uses AI, and longstanding weaknesses in open-source maintenance. Blurring these layers leads to bad conclusions, such as treating a vulnerable model package as proof that every AI-generated function is unsafe.
| Layer | How harm can occur | What is established | Useful controls |
|---|---|---|---|
| AI-generated project contributions | Insecure logic, copied vulnerability patterns, unclear provenance, or unrecognized third-party license obligations enter a pull request. | The UK Department for Science, Innovation and Technology’s 2026 literature review identifies this as a novel or emerging supply-chain risk. It does not provide a reliable prevalence rate. | Human review, tests, dependency and license checks, provenance records, and project disclosure rules. |
| AI-enabled application supply chains | Outdated packages or models, tampered model files, weak dataset provenance, or undocumented fine-tuning and deployment components compromise an AI application. | OWASP’s LLM03:2025 Supply Chain guidance treats these as concrete risks in building and operating AI systems. | Inventories, signed artifacts, source verification, patching, model and data documentation, and vulnerability response. |
| Traditional open-source conditions | Deep dependency trees, small maintainer teams, and components that lose maintenance allow one flaw to reach many downstream users. | These pressures predate generative AI. DSIT’s March 3, 2025 supply-chain research describes resource constraints and downstream impact. | Maintenance planning, dependency governance, timely disclosure, patching, and investment in critical projects. |
Can AI-generated code introduce vulnerabilities?
Yes. An assistant can produce code that appears plausible while mishandling authentication, input validation, permissions, error paths, cryptography, or concurrency. It may also repeat a vulnerability pattern found in its training material. A reviewer who checks only whether the code compiles can miss a flaw that is obvious when the intended security property is examined.
The evidence supports a risk warning, not a claim that AI-written code is generally less secure. The 2026 UK review says systematic academic research on this specific category remains limited. That uncertainty is a reason to measure and review contributions carefully, not to assume either safety or universal danger.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware match#1 Best Overall

- Durable and High-Quality Material: these CPU radiator fan clips are made of high-quality stainless steel, providing sturdiness and resilience for long-lasting performance. the durable material ensures that your fan stays securely in place, and the clips are designed to withstand high temperatures without losing their shape or effectiveness.
- Easy Installation Process: Installing these fan clips is a breeze, and no complicated operations are required. simply clip them onto the outer fixing holes of your fan and attach the radiator. this straightforward process makes it easy for anyone to secure their fan and improve their system’s heat dissipation.
- Enhanced Heat Dissipation and Performance: our fan clips are specifically designed to fix 12cm fans on radiators, ensuring optimal heat dissipation and reducing chassis noise. by securely holding your fan in place, these clips help maintain proper CPU operation and provide stronger overall system performance.
- Lightweight and Portable Design: Each CPU radiator fan clip weighs only 3 grams and is small in size, making it easy to carry and store. the elegant silver design is not only functional but also ensures that your components remain clean and rust-free, enhancing the overall aesthetics and efficiency of your computer setup.
- Precise Fit and Versatile Application: the dimensions of each clip are 12cm in length, making them suitable for various 12cm fans including models like hyun bing 400 and donghai x4, x5 radiators. the precise fit ensures that the fan is securely attached, providing reliable support and enhancing the overall cooling efficiency of your system.
Provenance is a separate concern. Generated output may resemble material from a third-party project, include a dependency that was not requested, or impose license obligations that are not visible in the surrounding change. Similarity scanners can identify matches to known code, but they cannot establish what data influenced a model, and many tools do not expose training-data similarity.
What risks arise inside AI applications?
An application that calls a language model has more than ordinary source-code dependencies. Its operational chain may include model weights, tokenizer and inference libraries, training or fine-tuning data, evaluation sets, hosted APIs, container images, and deployment services.
OWASP’s LLM03:2025 guidance highlights several failure paths:
Rank #2

- Perfect for computer case fans and radiator fan mounting, these radiator fan screws kit ensure secure and stable, enhancing the efficiency of your cooling fan system
- Made by high-quality stainless steel, these screws are built to last, offering superior corrosion resistance and long-term reliability for pc fan cooling system
- By self-tapping thread design, these pc fan screws allow for fast and hassle-free installation of standard plastic-framed case fans, saving you time and effort
- Thoses computer fan screws was placed inside a compartment and clearly labeled, making it easy for you to use and store at any time.
- Package Contain: 6-32x30mm radiator fan screws*15PCS, M5x10mm case fan mount screws*15PCS
- an outdated or vulnerable package or model remains in production;
- a model file or container is replaced or tampered with;
- dataset ownership, license terms, or provenance are undocumented;
- fine-tuning introduces unsafe behavior or embeds unreviewed material; and
- the organization cannot identify which component must be patched when a problem is disclosed.
These are supply-chain risks in an AI system. They do not, by themselves, prove that an AI coding assistant generated the vulnerable code.
How does AI compare with older open-source risks?
Generative AI changes the speed and scale of activity, but it does not remove familiar causes of compromise. Dependency sprawl, abandoned components, limited maintainer time, weak release integrity, and delayed patching remain central risks. AI can increase pressure on each: it can create more proposed changes to review, help attackers produce convincing malicious packages, and raise the volume of vulnerability reports and fixes.
| Comparison axis | AI-related example | Conventional example |
|---|---|---|
| Evidence maturity | AI-generated contribution risk is emerging; systematic prevalence data is not established. | Unmaintained dependencies and known vulnerabilities are long-observed ecosystem problems. |
| Impact pathway | Generated pull request, model or dataset, deployment platform, or maintainer workload. | Compromised package, exploitable defect, or abandoned project. |
| Detectability | Opaque provenance, hallucinated dependency names, or subtle generated logic can evade ordinary review. | Known vulnerability signatures, package metadata, and license matches are often easier to scan. |
| Primary controls | Human review plus inventories, integrity checks, provenance and license review, and AI-aware development practices. | Code review, dependency scanning, patching, signed releases, and coordinated disclosure. |
OpenSSF and the Cloud Native Computing Foundation put the relationship succinctly in Securing Open Source in the Age of AI, version 1.0 (May 2026): “AI does not change the fundamentals of open source security.” Their point is that least privilege, small attack surfaces, coordinated vulnerability disclosure, and proactive security engineering still apply, even as AI changes the velocity of attacks, reports, fixes, and expectations.
Rank #3

- PC fan mount radiator shockproof rubber screws are widely used for chassis fans, CPU radiator fans, graphics card cooling fans, power supply cooling fans, and hard drive cooling fans, reducing vibration and noise.
- Length: 66mm/2.6 inch; Head Diameter: 8mm/0.31 inch; Slot Width: 24mm/0.94 inch; Color: White; Material: Silicone Rubber; Style: Shock Absorbing Rubber Nails; In the package of: 20PCS x Screws
- Made of silicone rubber, great flexibility, is ultra-soft, aging resistant, and has a long service time to use. It can reduce the vibration transmitted by the fan to the chassis or other components, thereby reducing noise and vibration and improving system stability. The computer fan cooler screws are durable, not easy to deform, and have good flexibility, which can effectively reduce noise.
- Turn off the computer and power-plug. Simply insert the fan rubber nails and shock-absorbing nails into the fixing holes at the bottom of the fan.
- Please allow slight errors due to manual measurement. Avoid excessive pulling on the shock-absorbing pins causing breakage or damage. Do not insert and pull out the shock-absorbing nails repeatedly as this may reduce the shock-absorbing effect.
How should maintainers review AI-assisted contributions?
A project does not need to ban assistants to reduce exposure. It does need an explicit, repeatable workflow.
- Set a contribution policy. State whether AI assistance must be disclosed, who remains responsible for the change, which repositories or data may be sent to a tool, and what evidence a contributor must provide.
- Mark the provenance of the change. Record the tool or service used when policy requires it, the human author, generated files, prompts or design notes that matter to review, and any new dependencies or model assets.
- Review behavior, not just style. Check trust boundaries, authorization, input handling, secrets, failure modes, concurrency, and resource limits. Require tests that exercise security-relevant paths.
- Inspect every dependency and license. Confirm that names resolve to the intended packages, versions are maintained, and transitive additions are justified. Treat an unfamiliar or hallucinated package name as a stop signal until independently verified.
- Run automated checks, then investigate findings. Use static analysis, dependency and vulnerability scanning, secret detection, tests, and license tools. A clean scan does not replace semantic review.
- Verify artifacts used by AI systems. For models, containers, datasets, and plugins, record sources and versions and validate hashes or signatures where available.
- Keep a repair and disclosure path. When a flaw is found, identify affected releases, notify downstream users through the project’s established process, publish a fix, and document the decision.
Which standards and guidance help?
NIST AI-specific secure development
NIST SP 800-218A, finalized July 26, 2024 (with the NIST news page updated June 25, 2025), adds AI-focused practices to the Secure Software Development Framework (SSDF) 1.1. It is intended for model producers, AI-system producers, and acquirers. It is a framework for managing development risk, not a certification that generated output is safe.
OWASP supply-chain controls
OWASP’s LLM03:2025 guidance emphasizes maintaining inventories, scanning components, remediating findings, documenting licenses, verifying sources, protecting model integrity, and keeping records that can be audited. Those practices apply to the model and data chain as well as conventional packages.
Rank #4

- Package Included: 20PCS Reducing Noise Anti-vibration PC Case Fans Computer Cooling Fan Mount Soft Rubber Screws.
- Color: black. Material: rubber. Length: 65mm / 2.56".
- Features: Made of high quality silicone rubber, great flexibility, ultra-soft, aging resistant, and a long service time to use, can be used in high temperature.
- Function: Replace box fan fixing screw, reduce box resonance caused by fan vibration and anti-noise during PC case fan mounting. Reducing noise of fan and shock absorption between the fan and the PC case, eliminating vibration helps to reduce stress.
- Application: Universal-Design fits most open cases fan sizes and PC cases. Extremely convenient and quick for mounting and unmounting.
OpenSSF and CNCF fundamentals
The OpenSSF/CNCF practitioner guide treats AI as both an offensive accelerator and a defensive tool. It discusses vulnerability discovery, patch generation, and code review alongside hallucinations and “slopsquatting,” in which an attacker publishes a package named after a dependency an AI assistant has incorrectly invented. Existing security engineering and disclosure practices remain the foundation.
Project-level contribution rules
The Apache Software Foundation’s generative-tooling guidance says contributor responsibility still applies when code comes from an assistant: “This is as true when using generative AI tooling, as it is when using materials from public websites or code from other open-source projects.” Projects should require contributors to disclose copyrighted or third-party material and confirm that the terms of a tool grant sufficient rights to submit the work.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What are the licensing and legal limits?
There is no universal rule that model training on open-source code is lawful or infringing, and generated output is not automatically free of license obligations. Apache’s guidance notes that copyrightability and the treatment of AI output remain unsettled and can differ by jurisdiction. Its recommendations are project policy and risk-management advice, not a court ruling.
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value
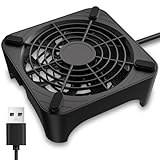
- 【Universal Compatibility】This USB cooling fan works seamlessly with Mini PC, PS5, routers, Apple TV, modems, PlayStation, receivers, Rokus, T-Mobile 5G Home Internet, Xbox Series, and other audio-video electronics. Whether cooling a gaming console, router, or streaming device, it eliminates overheating worries across your digital ecosystem.
- 【Powerful Cooling Performance】Equipped with a 120mm fan boasting 55.8 CFM airflow and 850RPM±10% speed, this USB PC fan delivers rapid cooling—dropping device temperatures by 20% in seconds. The 9-blade design ensures powerful airflow to tackle heat buildup in routers, mini PCs, and gaming consoles, preventing lag and performance drops caused by overheating.
- 【Ultra-Quiet Operation & Scratch-Proof Protection】 Designed for ultra-quiet and scratch-resistant cooling needs, this USB computer fan comes with 4 shock-absorbing pads and operates at just 18dB(A)±10% noise—whisper-quiet, quieter than library silence (30dB) and close to the sound of rustling leaves (20dB). It enables efficient device cooling without noise interference or surface scratches, letting you fully immerse in video, audio, and gaming. It’s perfect for home offices, living rooms, and gaming setups.
- 【USB-Powered & Space-Saving Setup】This USB powered fan features an integrated 530mm (20.87-inch) USB cable, connecting easily to chargers, mobile power banks, or laptops—no extra wires needed. With dimensions of 130mm×130mm×48.6mm (5.12×5.12×1.91 inches), it can be placed flat or upright, making it perfect for narrow spaces while keeping your setup tidy.
- 【Sturdy & Long-Lasting Durability】Made from premium eco-friendly ABS material, this USB fan (with a box fan-like structure) supports heavy-duty use and can withstand weights up to 11LB. With a lifespan of 40000 hours, it offers long-term cooling for your devices, ensuring stable performance and protection against overheating for years to come.
For a real contribution, maintainers should identify included third-party text or code, verify compatibility with the project’s license, preserve required notices, and obtain permission when necessary. If provenance cannot be established, pause the merge rather than treating “the model wrote it” as a rights clearance.
Is AI now the dominant threat to open source?
No reliable published statistic in the reviewed material measures what share of open-source vulnerabilities originates in AI-generated code, so a numerical ranking would be misleading. The strongest defensible conclusion is narrower: generative AI is an emerging supply-chain risk and a risk amplifier. It can make insecure contributions, malicious dependencies, and attacks arrive faster, while also helping defenders find and fix problems.
Maintainers should therefore add AI-specific provenance, model and data integrity, and licensing checks to established secure-development controls. Projects that already inventory dependencies, review changes rigorously, patch promptly, and communicate vulnerabilities are better positioned to absorb AI-driven increases in volume without mistaking novelty for proof that older risks have disappeared.




