Freedom251 › SBOM Management Software
TRUSCA
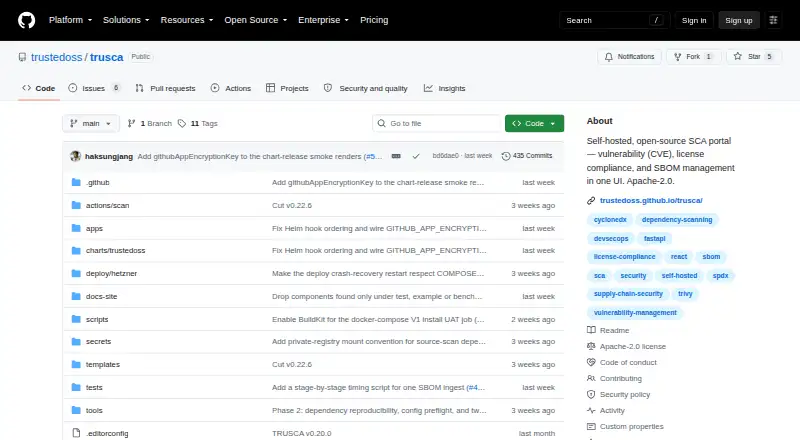
What TRUSCA is
TRUSCA is a free, open-source platform for tracking vulnerabilities in third-party software components, reviewing license compliance, and managing SBOMs. It detects packages across more than 30 language ecosystems and checks components against NVD, OSV, GitHub Advisory, EPSS, and KEV data. Its CVE data refreshes weekly.
The platform can import CycloneDX and SPDX SBOMs and export them in several listed formats. It documents GitHub Actions, a GitLab CI template, a Jenkinsfile example, a REST API, and API keys. Build gates can block a Critical CVE or forbidden license. Teams can classify licenses, generate NOTICE files, approve components, keep an append-only audit log, and receive email, Slack, or Teams notifications. Security triage includes a seven-state CycloneDX VEX workflow and EPSS prioritization. TRUSCA does not scan users’ own source code. Users deploy it themselves with Docker Compose or Helm; a read-only live demo is also available. The UI, error messages, and documentation are in English and Korean. The project has no paid support tier or managed hosting.
Who it suits
TRUSCA is intended for engineering, legal, and security teams managing third-party components. It suits teams able to operate self-hosted software and seeking vulnerability, license, and SBOM workflows.
What it does well
- Free, open-source software under Apache-2.0.
- Detects packages across 30+ language ecosystems.
- Supports CycloneDX and SPDX import and export.
- Build gates can block critical vulnerabilities or forbidden licenses.
- Offers email, Slack, and Teams notifications.
What to know first
- Requires self-hosted deployment.
- Does not analyze users’ own source code.
- No paid support tier or managed hosting.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Apache-2.0 self-hosted | No per-seat licensing · self-hosted deployment | Free |
As github.com lists them, read 3 Oct 2026. The maker's own page has the final word.
Getting started
- Open the project website on GitHub.
- Choose a self-hosted deployment using Docker Compose or a Helm chart.
- Connect a documented GitHub Action, GitLab CI template, or Jenkinsfile example, or use the REST API and API keys.
- Import a CycloneDX or SPDX SBOM, or use cdxgen to detect packages.
- Set license classifications and build gates for Critical CVEs or forbidden licenses.
- Use the read-only live demo to explore the portal.
Verdict
TRUSCA brings component vulnerability tracking, license controls, and SBOM workflows into a self-hosted platform. It focuses on third-party dependencies rather than scanning a team’s own source code, and users should plan to manage deployment themselves.
Questions
How much does TRUSCA cost?
The Apache-2.0 self-hosted plan is listed as free. It has no per-seat licensing.
Is TRUSCA open source?
Yes. The project is open source under Apache-2.0.
Which SBOM formats does it support?
TRUSCA can ingest CycloneDX and SPDX. It exports CycloneDX in JSON or XML and SPDX in JSON or Tag-Value.
Does TRUSCA scan my source code?
No. It focuses on third-party components and does not analyze users’ own source code.
How can teams deploy TRUSCA?
The project provides Docker Compose and Helm chart deployment routes for users to run themselves. A read-only live demo is also available.
What support and languages are available?
The project has no paid support tier or managed hosting and directs users to community support channels. Its UI, error messages, and documentation are available in English and Korean.
Facts from TRUSCA's own pages
- CI integrations
- The project documents a GitHub Action, GitLab CI template, Jenkinsfile example, REST API, and API keys; its build gate can fail on a Critical CVE or forbidden license. · trustedoss.github.io, 3 Oct 2026
- Component detection
- It uses cdxgen to detect packages across 30+ language ecosystems. · trustedoss.github.io, 3 Oct 2026
- Deployment
- TRUSCA is distributed for users to run themselves with Docker Compose or a Helm chart; a read-only live demo is also available. · trustedoss.github.io, 3 Oct 2026
- Intended users
- The project describes the portal as serving engineering, legal, and security teams. · trustedoss.github.io, 3 Oct 2026
- Language support
- The UI, error messages, and documentation are available in English and Korean. · trustedoss.github.io, 3 Oct 2026
- License workflow
- Licenses are classified as allowed, conditional, or forbidden, with NOTICE file generation and build blocking for forbidden licenses. · trustedoss.github.io, 3 Oct 2026
- Not a SAST scanner
- The documentation says TRUSCA does not analyze users’ own source code and focuses on third-party components. · trustedoss.github.io, 3 Oct 2026
- Notifications and audit
- Workflow features include component approval, an append-only audit log, and notifications via email, Slack, and Teams. · trustedoss.github.io, 3 Oct 2026
- Purpose
- TRUSCA is a self-hosted software composition analysis platform for CVE tracking, license compliance, and SBOM management. · trustedoss.github.io, 3 Oct 2026
- SBOM
- TRUSCA exports CycloneDX in JSON or XML and SPDX in JSON or Tag-Value, and can ingest CycloneDX or SPDX SBOMs. · trustedoss.github.io, 3 Oct 2026
- Security triage
- TRUSCA provides a seven-state CycloneDX VEX triage workflow and EPSS prioritization. · trustedoss.github.io, 3 Oct 2026
- Support
- The project says it has no paid support tier or managed hosting and directs users to its community support channels. · github.com, 3 Oct 2026
- Vulnerability feeds
- Trivy matches components against NVD, OSV, GitHub Advisory, EPSS, and KEV data, with new CVEs picked up on weekly database refreshes. · trustedoss.github.io, 3 Oct 2026
Where TRUSCA stands on Freedom251
- SBOM Management Software#10 of 22