Freedom251 › Exposure Management Software
TrollEye CTEM Platform
What TrollEye CTEM Platform is
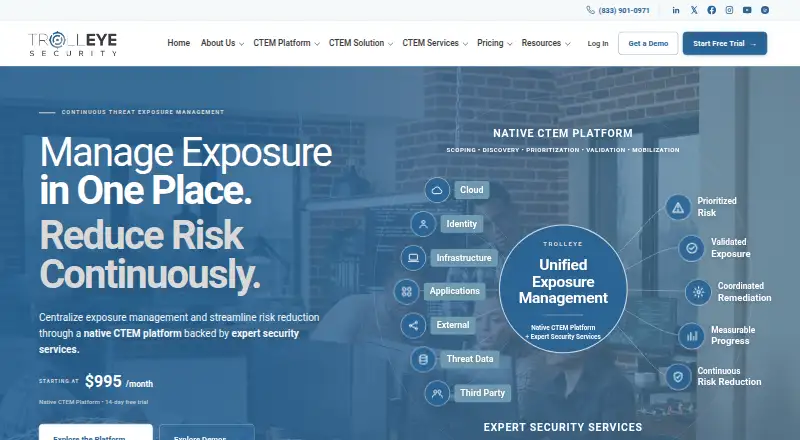
TrollEye CTEM Platform is web software for managing security exposures, from discovering assets to organizing remediation. It assesses applications, cloud, infrastructure, identities, endpoints, networks, code repositories, and third parties. Its contextual risk scoring draws on attack-path analysis, threat intelligence, asset criticality, and compensating-control context to help teams prioritize findings. Validation options include automated checks, manual penetration testing, control-effectiveness testing, and proof of exploitability. Role-based workflows, Jira and ticket synchronization, root-cause analysis, and remediation initiatives support follow-through. Listed integrations include GitHub, Jira, Azure DevOps, Slack, Microsoft Teams, AWS, and Microsoft Azure. TrollEye says its AI agents correlate exposure data, identify exploitable paths, and suggest remediation. For SOC 2 technical security operations, it can retain findings, tests, ownership, remediation, retesting, and verification history as evidence; it does not replace a CPA firm, formal examination, or broader GRC process. Packages include regular cadence calls. Pricing starts at $995/mo, and an eligible 14-day free trial is advertised. The platform is web-based.
Who it suits
It suits security teams that need to assess exposures across multiple asset types and coordinate validation and remediation. The listed package tiers address focused teams through enterprise environments.
What it does well
- Assesses applications, cloud, identities, and third parties
- Contextual prioritization includes attack-path analysis
- Offers automated and manual validation options
- Integrates with Jira, GitHub, AWS, and others
- Packages include regular cadence calls
What to know first
- No free plan
- Starts at $995/mo
Limits
CTEM Essentials costs $995 a month and includes 200 AI vulnerability analyses, four Apex autonomous engagements, one business unit, one cloud account, 1,000 workloads, 200 monitored assets, and five users. Higher plans raise these allowances; Enterprise uses custom analysis and engagement capacity.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| CTEM Growth | 1,500 AI vulnerability analyses/month · 12 Apex autonomous engagements/month · 2 business units · 6 cloud accounts · 6,000 workloads · 1,500 monitored assets · 30 users | $2,995 a month |
| CTEM Professional | 5,000 AI vulnerability analyses/month · 32 Apex autonomous engagements/month · 6 business units · 20 cloud accounts · 20,000 workloads · 5,000 monitored assets · 12 service credits/month · Unlimited users | $8,995 a month |
| CTEM Essentials | 200 AI vulnerability analyses/month · 4 Apex autonomous engagements/month · 1 business unit · 1 cloud account · 1,000 workloads · 200 monitored assets · 5 users | $995 a month |
| CTEM Enterprise | Custom analysis and engagement capacity · 6+ business units · 20+ cloud accounts · 20,000+ workloads · 5,000+ monitored assets · 12+ service credits/month · Unlimited users | On request |
As trolleyesecurity.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the TrollEye website
- Start the eligible 14-day free trial
- Choose a CTEM package for your team
- Connect listed systems such as GitHub, Jira, AWS, or Microsoft Azure
- Scope assets and review prioritized exposures
- Use validation and remediation workflows
Verdict
TrollEye combines broad exposure coverage with prioritization, validation, and remediation workflows. Consider its listed package limits and pricing when deciding whether it fits your team.
Questions
Does TrollEye offer a free plan?
No. TrollEye is a paid platform with an eligible 14-day free trial.
What is the starting price?
CTEM Essentials is $995 a month.
Which platforms does TrollEye support?
TrollEye is available on the web.
Which integrations are listed?
Integrations include GitHub, Jira, Azure DevOps, Slack, Microsoft Teams, AWS, and Microsoft Azure.
Can TrollEye replace a CPA firm or full GRC process?
No. TrollEye says it supports technical security operations and SOC 2 evidence but does not replace a CPA firm, formal examination, or broader GRC process.
What does CTEM Essentials include?
It includes 200 AI vulnerability analyses per month, four Apex autonomous engagements per month, one business unit, one cloud account, 1,000 workloads, 200 monitored assets, and five users.
Facts from TrollEye CTEM Platform's own pages
- AI agents
- TrollEye says its AI agents correlate exposure data, surface exploitable attack paths, and recommend remediation actions. · trolleyesecurity.com, 4 Oct 2026
- Asset coverage
- It assesses applications, cloud, infrastructure, identities, endpoints, networks, code repositories, and third parties. · trolleyesecurity.com, 4 Oct 2026
- Compliance scope
- TrollEye says it supports technical security operations and evidence for SOC 2 but does not replace the CPA firm, formal examination, or broader GRC process. · trolleyesecurity.com, 4 Oct 2026
- Founded
- 2019 · trolleyesecurity.com, 28 Sept 2026
- Headquarters
- Cumming, Georgia, United States · trolleyesecurity.com, 28 Sept 2026
- Integrations
- The platform page lists GitHub, Jira, Azure DevOps, Slack, Microsoft Teams, AWS, and Microsoft Azure as integrations. · trolleyesecurity.com, 4 Oct 2026
- Intended teams
- The pricing page describes Essentials for focused teams, Growth for growing security programs, Professional for mature programs, and Enterprise for enterprise environments. · trolleyesecurity.com, 4 Oct 2026
- Prioritization
- Native prioritization capabilities include context-based risk scoring, attack-path analysis, threat intelligence, and compensating-control context. · trolleyesecurity.com, 4 Oct 2026
- Purpose
- The platform scopes, discovers, prioritizes, validates, and mobilizes remediation for security exposures. · trolleyesecurity.com, 4 Oct 2026
- Remediation workflows
- It offers role-based workflows, Jira and ticket synchronization, root-cause analysis, and remediation initiatives. · trolleyesecurity.com, 4 Oct 2026
- Security evidence
- The SOC 2 solution page says TrollEye preserves findings, testing results, ownership, remediation, retesting, and verification history to support SOC 2 evidence. · trolleyesecurity.com, 4 Oct 2026
- Support
- Every CTEM package includes regular cadence calls with the TrollEye team. · trolleyesecurity.com, 4 Oct 2026
- Trial
- The site advertises an eligible 14-day free trial of the CTEM platform. · trolleyesecurity.com, 4 Oct 2026
- Validation
- The platform lists automated validation, manual penetration testing, control-effectiveness testing, and proof of exploitability. · trolleyesecurity.com, 4 Oct 2026
Where TrollEye CTEM Platform stands on Freedom251
- Exposure Management Software#13 of 20