Freedom251 › Ransomware Protection Software
ShadowStrike Phantom
What ShadowStrike Phantom is
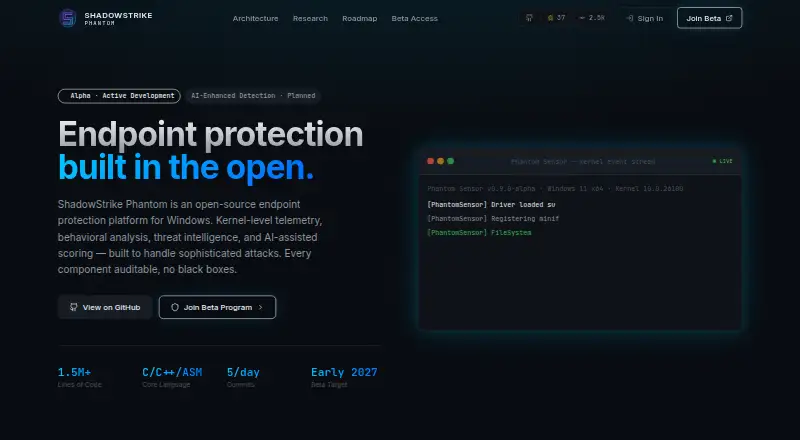
ShadowStrike Phantom is a free, open-source endpoint protection platform for Windows, currently in pre-alpha and active development. Its minifilter driver is designed to intercept file reads, writes, creates, and deletes. An attack-chain tracker correlates kernel events across process trees and maps activity to MITRE ATT&CK. Detection features include memory inspection, syscall tracing, network detection, anti-evasion, and ransomware detection. The platform also lists IOC lookups, STIX/TAXII feed support, and a URL reputation engine. It defines more than 550 MITRE ATT&CK technique IDs, with 14 rules active and 18 pending. AI-enhanced detection is planned, while ML inference is described as part of the scan pipeline. The code, kernel callbacks, detection rules, and heuristics are publicly auditable on GitHub under an AGPL-3.0 license. Phase 2 user-space detection engines are 76% complete; core scan engines, the Windows service layer, and end-to-end integration remain on the roadmap. Later plans include public betas for consumer-focused Phantom Home and enterprise-focused Phantom EDR. A future Phantom XDR phase lists SIEM connectors and MISP and OpenCTI integrations. The product is explicitly labeled not for production use.
Who it suits
Phantom may suit Windows security developers and evaluators interested in an open-source endpoint protection project and its detection architecture. Its pre-alpha status means it is not intended for production use.
What it does well
- Open-source code and detection logic are publicly auditable.
- Intercepts file operations through a Windows minifilter driver.
- Includes memory, syscall, network, and ransomware detection features.
- Lists IOC lookups, STIX/TAXII feeds, and URL reputation.
- Maps correlated attack activity to MITRE ATT&CK.
What to know first
- Labeled pre-alpha and not for production use.
- Only 14 detection rules are active; 18 are pending.
- Core scan engines and integration work remain on the roadmap.
Limits
The product is pre-alpha and not for production use. Core scan engines, the Windows service layer, and end-to-end integration remain among the work ahead.
Verdict
Choose ShadowStrike Phantom if you want to examine an open-source Windows endpoint protection project and its planned detection capabilities. Look elsewhere for a production-ready product, since Phantom is labeled pre-alpha and core components remain under development.
Questions
Does ShadowStrike Phantom cost anything?
It is listed as free and open source.
Which operating system does it support?
It is for Windows.
Is it ready for production use?
No. It is labeled pre-alpha and not for production use.
What detection capabilities does it list?
They include memory inspection, syscall tracing, network detection, anti-evasion, and ransomware detection.
Is the project open source?
Yes. Its source code and detection logic are publicly auditable on GitHub, and the site links to an AGPL-3.0 license.
What is planned for later development?
The roadmap includes consumer-focused Phantom Home, enterprise-focused Phantom EDR, and a Phantom XDR phase with SIEM and threat intelligence integrations.
Facts from ShadowStrike Phantom's own pages
- AI status
- AI-enhanced detection is marked planned on the homepage, which also describes ML inference in the scan pipeline as a capability. · shadowstrike.dev, 4 Oct 2026
- Behavioral detection
- Its attack-chain tracker correlates kernel events across process trees and maps activity to MITRE ATT&CK with real-time threat scoring. · shadowstrike.dev, 9 Oct 2026
- Behavior analysis
- The site says its attack-chain tracker correlates kernel events across process trees and maps them to MITRE ATT&CK. · shadowstrike.dev, 4 Oct 2026
- Detection coverage
- The site says 550+ MITRE ATT&CK technique IDs are defined, with 14 rules active and 18 pending. · shadowstrike.dev, 4 Oct 2026
- Development status
- The site describes Phantom as pre-alpha and says it is not for production use. · shadowstrike.dev, 9 Oct 2026
- Future integrations
- The planned Phantom XDR phase lists SIEM connectors for Elastic SIEM, Splunk, Microsoft Sentinel, and OpenSearch, plus MISP and OpenCTI integrations. · shadowstrike.dev, 4 Oct 2026
- Integrations
- The roadmap lists planned SIEM connectors for Elastic SIEM, Splunk, Microsoft Sentinel, and OpenSearch, plus MISP and OpenCTI threat-intelligence integrations. · shadowstrike.dev, 9 Oct 2026
- Intended users
- The roadmap describes Phantom Home as targeting consumers and Phantom EDR as targeting enterprise endpoints; both are planned products. · shadowstrike.dev, 9 Oct 2026
- Kernel monitoring
- Phantom Sensor uses a Windows minifilter driver to intercept file-system reads, writes, creates, and deletes. · shadowstrike.dev, 9 Oct 2026
- License
- The site links to an AGPL-3.0 license. · shadowstrike.dev, 4 Oct 2026
- Memory and syscall analysis
- Listed capabilities include detecting process injection and hollowing, shellcode, ROP chains, direct syscalls, and NTDLL integrity issues. · shadowstrike.dev, 9 Oct 2026
- Not for production
- The maker labels the product pre-alpha and not for production use. · shadowstrike.dev, 4 Oct 2026
- Product
- ShadowStrike Phantom is an open-source endpoint protection platform for Windows. · shadowstrike.dev, 9 Oct 2026
- Ransomware protection
- Listed ransomware features include honeypot file monitoring, shadow-copy protection, backup integrity checks, and entropy analysis. · shadowstrike.dev, 9 Oct 2026
- Roadmap
- The roadmap describes Phantom Home as consumer-focused and Phantom EDR as enterprise-focused, with both public betas planned in Phase 3. · shadowstrike.dev, 4 Oct 2026
- Roadmap status
- The roadmap says the kernel-driver phase is 97% complete, with driver signing pending, and user-space engines are 76% complete. · shadowstrike.dev, 9 Oct 2026
- Security infrastructure
- The architecture page describes AES-GCM and RSA-OAEP for IPC channel encryption and Authenticode validation for loaded modules. · shadowstrike.dev, 4 Oct 2026
- Support
- The site provides [email protected] and directs users to GitHub Discussions for community discussions. · shadowstrike.dev, 9 Oct 2026
- Threat detection
- Listed detection features include memory inspection, syscall tracing, network detection, anti-evasion, and ransomware detection. · shadowstrike.dev, 4 Oct 2026
- Threat intelligence
- The site lists IOC lookups, STIX/TAXII feed support, and a URL reputation engine. · shadowstrike.dev, 9 Oct 2026
- Transparency
- The maker says source code is publicly auditable on GitHub and describes the project as licensed under AGPL-3.0. · shadowstrike.dev, 9 Oct 2026
Where ShadowStrike Phantom stands on Freedom251
- Ransomware Protection Software#20 of 22