Freedom251 › Software Composition Analysis Software

SBOM Observer
What SBOM Observer is
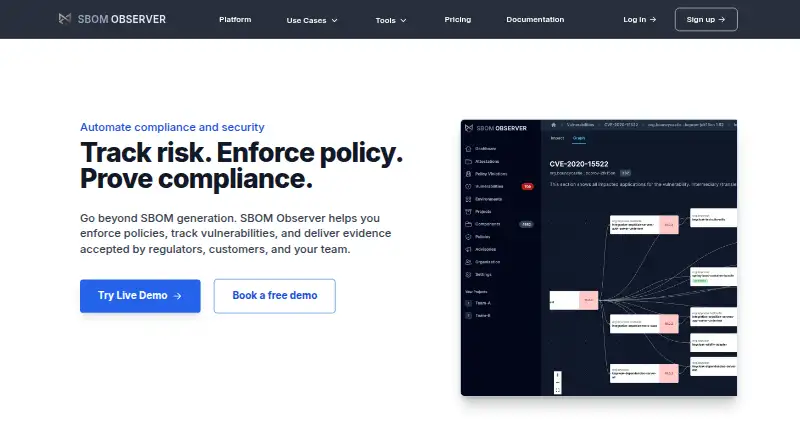
SBOM Observer is a software supply-chain security service that analyzes bills of materials from builds and suppliers. It monitors vulnerabilities and license issues, then enforces policies in CI/CD. Supported formats include CycloneDX 1.3 or later and SPDX 2.2 or later in JSON, XML, YAML, and tag-value forms. Findings use OSV, GitHub Advisories, and NVD, with CVSS and EPSS information. Teams can record VEX decisions, import supplier VEX, and export CISA VEX with a release. Policies can be built visually or written in Rego or JavaScript and can fail builds for vulnerability, license, or SBOM-quality violations. The Observer CLI works with GitHub Actions, GitLab CI, Jenkins, Azure DevOps, CircleCI, or other shell-based CI systems. Analysis traces vulnerable dependencies to applications and releases and breaks container SBOMs into layers and packages. Business is EU-hosted SaaS; Enterprise adds on-premises and air-gapped deployment. Business costs €69 a month per user; Enterprise pricing is custom.
Who it suits
SBOM Observer is aimed at security, compliance, and product teams monitoring software supply chains. Enterprise is presented for 25 or more users, larger rollouts, and regulated industries.
What it does well
- Supports CycloneDX and SPDX formats
- Uses OSV, GitHub Advisories, and NVD
- Policies can block failing CI builds
- VEX import, decisions, and CISA export
- Enterprise supports air-gapped deployment
What to know first
- No free plan
- No separate trial plan
- Business covers one namespace and 10 projects
- Enterprise pricing is custom
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Business | €69/ user / month · 1 namespace · 10 projects · Support within 1 business day | €69 a month |
| Enterprise | Custom · 25+ users · Unlimited namespaces and projects · SSO with SAML · Role-based access control · Audit logs · SLA and dedicated support channel · SaaS or on-premises, including air-gapped | On request |
As sbom.observer lists them, read 11 Oct 2026. The maker's own page has the final word.
Verdict
SBOM Observer combines SBOM analysis, vulnerability monitoring, VEX handling, and CI/CD policy enforcement. Review its deployment model, project allowances, and pricing structure against your rollout.
Facts from SBOM Observer's own pages
- Analysis
- It traces vulnerable dependencies to affected applications and releases and breaks container SBOMs down by base layer, system package and application dependency. · bytesafe.dev, 11 Oct 2026
- Deployment
- Business is managed SaaS hosted in the EU; Enterprise supports SaaS or on-premises deployment, including air-gapped environments. · bytesafe.dev, 11 Oct 2026
- Free access
- A free SBOM Analyzer accepts one SBOM without signup, and a shared live demo is also available without signup. · bytesafe.dev, 11 Oct 2026
- Headquarters
- Sweden · sbom.observer, 28 Sept 2026
- Integrations
- The Observer CLI is described as usable in GitHub Actions, GitLab CI, Jenkins, Azure DevOps, CircleCI or any CI that runs a shell step. · bytesafe.dev, 11 Oct 2026
- Intended users
- Business is presented for small teams in security, compliance and product, while Enterprise is for 25 or more users, larger rollouts and regulated industries. · bytesafe.dev, 11 Oct 2026
- Maker
- SBOM Observer is made by Bitfront AB, a Swedish company that says it has built software supply chain security tools since 2018. · bytesafe.dev, 11 Oct 2026
- Policy engine
- Policies can be built visually or written in Rego or JavaScript, and can fail CI builds for vulnerability, license or SBOM quality violations. · bytesafe.dev, 11 Oct 2026
- Provenance and project health
- Component records can include SLSA provenance and OpenSSF Scorecard checks for the source repository. · bytesafe.dev, 11 Oct 2026
- Purpose
- SBOM Observer analyzes SBOMs from builds and suppliers, monitors vulnerabilities and license issues, and enforces policies in CI/CD. · bytesafe.dev, 11 Oct 2026
- SBOM formats
- It supports CycloneDX 1.3 and later and SPDX 2.2 and later in JSON, XML, YAML and tag-value formats. · bytesafe.dev, 11 Oct 2026
- Security
- The maker says managed SaaS data is stored and processed in the EU, encrypted in transit with TLS and at rest, and protected by role-based access controls. · bytesafe.dev, 11 Oct 2026
- Trial limitation
- The maker says there is no separate trial plan; evaluation with a customer's own SBOMs is available by booking a demo. · bytesafe.dev, 11 Oct 2026
- VEX
- Users can record VEX decisions for findings, import supplier VEX and export CISA VEX with a release. · bytesafe.dev, 11 Oct 2026
- Vulnerability feeds
- It monitors components against OSV, GitHub Advisories and NVD, with CVSS and EPSS on findings. · bytesafe.dev, 11 Oct 2026