Freedom251 › Fuzz Testing Software
Metalware
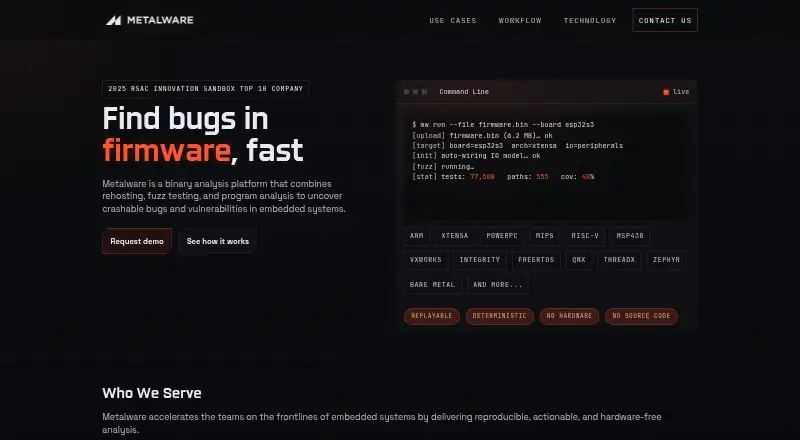
What Metalware is
Metalware analyzes embedded firmware binaries to identify crashes and vulnerabilities through rehosting, fuzz testing, and program analysis. It accepts ELF and raw .bin files for ARM Cortex-M firmware, including ROMs, update blobs, and extracted components; users provide a device or board profile, while symbols are optional. The platform emulates an ARM Cortex-M processor, models peripheral I/O, detects DMA buffers, and uses coverage-guided fuzzing. Analysis does not require physical hardware, source code, or a test harness. Results include a stack trace, root cause analysis, and a reproducible proof-of-concept input, with time-travel debugging for reproduction. Users can launch work through a web interface, CLI, or CI/CD API, and documented workflows cover GitHub Actions and GitLab CI. Defects can be filed as repository issues. Ghidra and Binary Ninja plugins and remote GDB support investigation, and PDF reports are available for audits. Deployment is offered as cloud or on-premise; on-premise setup requires a modern Linux computer with Docker. The default run lasts 24 hours and can be adjusted from the dashboard. Pricing is available on request.
Who it suits
Metalware is aimed at product security and DevSecOps teams, firmware engineers, reverse engineers, and vulnerability researchers working with ARM Cortex-M firmware.
What it does well
- Analysis does not require physical hardware or source code.
- Symbols are not required for supported binaries.
- Results include root cause analysis and a proof-of-concept input.
- Offers cloud and on-premise deployment.
- Documents GitHub Actions and GitLab CI workflows.
What to know first
- Documented firmware support is for ARM Cortex-M.
- On-premise fuzzing is CPU intensive.
- Pricing is available on request.
Limits
Metalware's documented support is for ELF and raw .bin ARM Cortex-M firmware. On-premise fuzzing performance scales with core count, and the default analysis duration is 24 hours unless changed in the dashboard.
Getting started
- Open the Metalware website and request pricing or access
- Choose the cloud service or an on-premise deployment
- For on-premise use, prepare a modern Linux computer with Docker
- Provide an ELF or raw .bin firmware file and a device or board profile
- Run analysis through the web interface, CLI or CI/CD API
- Review defects and export PDF reports
Verdict
Metalware pairs emulated firmware execution with fuzzing and defect analysis, then provides debugging integrations and CI workflows. Its documented target scope and on-premise compute demands are key constraints to weigh.
Questions
What firmware formats and targets does Metalware support?
It supports ELF and raw .bin firmware for ARM Cortex-M processors, including embedded-peripheral, RTOS and bare-metal targets. Debug symbols are not required.
Does analysis require hardware or source code?
No. The maker says analysis runs without physical hardware, source code or a test harness.
How can I run Metalware?
Jobs can be run through a web interface, CLI or CI/CD API. Deployment is available as a cloud service or on premises.
Does Metalware integrate with CI systems?
Documented workflows cover GitHub Actions and GitLab CI. The CLI can file discovered defects as GitHub or GitLab issues and deduplicate previously filed issues.
What debugging integrations are available?
Metalware provides Ghidra and Binary Ninja plugins and remote GDB for investigating defects. Results also support time-travel debugging.
How is Metalware priced?
Pricing is available on request.
Facts from Metalware's own pages
- Analysis duration
- The default analysis duration is 24 hours and can be configured from the dashboard. · metalware.com, 7 Oct 2026
- Analysis output
- Defect details include root cause analysis, a stack trace, and a reproducible proof-of-concept input. · metalware.com, 7 Oct 2026
- Analysis results
- Defects include a stack trace, root cause analysis, and proof-of-concept input, and can be reproduced with time-travel debugging. · metalware.com, 7 Oct 2026
- CI/CD integrations
- The maker documents GitHub Actions and GitLab CI workflows, with options to file discovered defects as GitHub or GitLab issues. · metalware.com, 7 Oct 2026
- Company
- The company site identifies the maker as Metalware Inc.; LinkedIn lists its headquarters as San Francisco, California, and its founding year as 2023. · linkedin.com, 7 Oct 2026
- Debugger integrations
- Metalware provides Ghidra and Binary Ninja plugins and remote GDB for investigating defects. · metalware.com, 7 Oct 2026
- Debugging integrations
- Metalware provides debugging through Ghidra and Binary Ninja plugins and remote GDB. · metalware.com, 7 Oct 2026
- Deployment
- Metalware is available as a cloud service or on-premise deployment; the on-premise instructions require a modern Linux computer with Docker. · metalware.com, 7 Oct 2026
- Emulation
- It runs firmware on an emulated ARM Cortex-M processor and models peripheral I/O without physical hardware. · metalware.com, 7 Oct 2026
- Emulation and fuzzing
- Metalware emulates an ARM Cortex-M processor, models memory-mapped peripheral I/O, automatically detects DMA buffers, and uses coverage-guided fuzzing. · metalware.com, 7 Oct 2026
- Fuzzing
- Its coverage-guided fuzzer tracks basic blocks, keeps inputs that reach new code, and mutates them to explore further. · metalware.com, 7 Oct 2026
- Input requirements
- Metalware supports ELF and raw .bin binaries for ARM Cortex-M firmware, and debug symbols are not required. · metalware.com, 7 Oct 2026
- Inputs
- It accepts firmware ELF files, ROMs, binary images, update blobs, and extracted components, with a device or board profile and optional symbols or metadata. · product.metalware.com, 7 Oct 2026
- Intended users
- The maker describes use by product security teams, DevSecOps, reverse engineers and vulnerability researchers, and firmware engineers. · product.metalware.com, 7 Oct 2026
- Issue tracking
- The CLI can automatically file newly discovered defects as GitHub or GitLab issues and deduplicates previously filed issues. · metalware.com, 7 Oct 2026
- No hardware or source
- The maker says analysis runs without physical hardware or source code, and requires no test harness. · metalware.com, 7 Oct 2026
- Notable limits
- The docs specify support for ARM Cortex-M firmware and say on-premise fuzzing is CPU intensive, with performance scaling linearly with core count. · metalware.com, 7 Oct 2026
- On-premise requirements
- The on-premise documentation says a modern Linux computer with Docker should work and that fuzzing is CPU intensive, with performance scaling linearly with core count. · metalware.com, 7 Oct 2026
- Product
- Metalware is a binary analysis platform that combines rehosting, fuzz testing, and program analysis to find crashable bugs and vulnerabilities in embedded systems. · product.metalware.com, 7 Oct 2026
- Purpose
- Metalware analyzes firmware binaries to find crashes and vulnerabilities using rehosting, fuzz testing, and program analysis. · product.metalware.com, 7 Oct 2026
- Reports
- Metalware generates a downloadable PDF report for every defect, with summary, root cause analysis, stack trace, and proof-of-concept data. · metalware.com, 7 Oct 2026
- Support
- The contact page lists [email protected] and says the team typically responds within 24 hours. · metalware.com, 7 Oct 2026
- Supported firmware
- The documentation says Metalware supports ELF and raw .bin binaries for ARM Cortex-M firmware, and debug symbols are not required. · metalware.com, 7 Oct 2026
- Workflow access
- Users can run analysis through a web interface, CLI, or CI/CD API. · product.metalware.com, 7 Oct 2026
Where Metalware stands on Freedom251
- Fuzz Testing Software#21 of 26