Freedom251 › Static Application Security Testing Sast
Mend SAST
What Mend SAST is
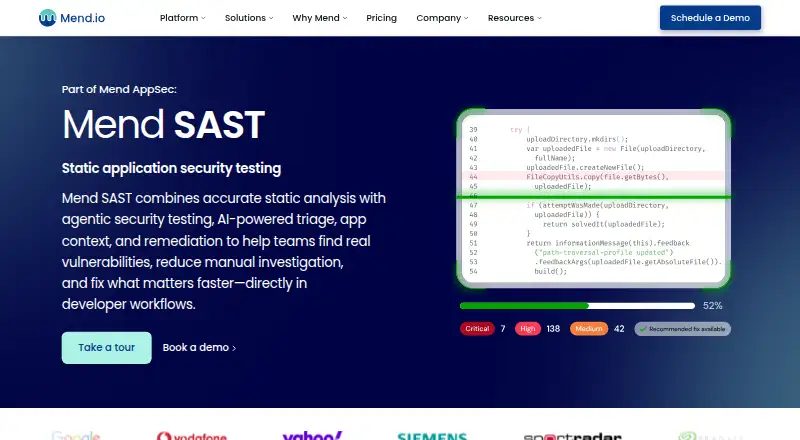
Mend SAST is a static application security testing tool that analyzes source code written by people or AI assistants. It helps development teams identify vulnerabilities, sort findings by context, and address issues within developer workflows. Mend supports more than 30 programming languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++.
Scanning runs on-premises or inside the customer’s environment, keeping proprietary source code within that perimeter. Findings, dashboards, and policy management run in Mend’s cloud. The product integrates with development environments, code hosts, and CI/CD tools including JetBrains, VS Code, Visual Studio, GitHub, GitLab, Jenkins, CircleCI, and GitHub Actions. It can also provide vulnerability information to Cursor, Windsurf, and Copilot.
Mend says incremental scans can run up to 10x faster than traditional SAST tools by analyzing changed code. Its detection claims start with 38% better precision and 48% better recall than benchmark competitors; its AI remediation is claimed to be 46% more accurate. Developers can review and apply proposed fixes. It also detects hardcoded credentials, API keys, tokens, and certificates, which can trigger policy violations and fail a build. The Mend AppSec plan is listed at $1,000 a year and includes SAST, SCA, AI-generated code security, AI-powered fix suggestions, and automated dependency updates.
Who it suits
Mend SAST suits development and security teams that need to scan source code across a range of languages while keeping scans inside their own environment. It may also fit teams that want vulnerability findings and proposed fixes in developer workflows, including workflows with AI code assistants.
What it does well
- Supports more than 30 programming languages.
- Scans on-premises or within the customer’s environment.
- Integrates with IDEs, code hosts, and CI/CD tools.
- Detects credentials, API keys, tokens, and certificates.
- Developers can review and apply proposed AI fixes.
What to know first
- The listed Mend AppSec plan costs $1,000 a year.
- Findings, dashboards, and policy management run in Mend’s cloud.
Limits
The listed Mend AppSec plan costs $1,000 a year. Findings, dashboards, and policy management run in Mend’s cloud, even when scanning runs on-premises or in the customer’s environment.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Mend AppSec | Up to $1000 per dev/per year · Includes Mend SAST, Mend SCA, AI-generated code security, AI-powered fix suggestions, automated dependency updates | $1,000 a year |
As mend.io lists them, read 2 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the Mend SAST website.
- Choose the Mend AppSec plan, listed at $1,000 a year.
- Set up scanning on-premises or within your environment.
- Connect the IDE, code host, or CI/CD tools your team uses.
- Review findings and proposed fixes in the developer workflow.
Verdict
Choose Mend SAST if your team needs source code scanning across many languages, contextual prioritization, and remediation within development workflows. Its hybrid approach keeps scanning inside your environment, while findings and management run in Mend’s cloud. The listed Mend AppSec plan costs $1,000 a year.
Questions
How much does Mend SAST cost?
The Mend AppSec plan is listed at $1,000 a year. It includes Mend SAST, Mend SCA, AI-generated code security, AI-powered fix suggestions, and automated dependency updates.
Which programming languages does Mend SAST support?
It supports more than 30 languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++.
Where does scanning run?
Scanning runs on-premises or inside the customer’s environment. Findings, dashboards, and policy management run in Mend’s cloud.
Which developer tools does it integrate with?
Listed integrations include JetBrains, VS Code, Visual Studio, Cursor, Windsurf, GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI, and GitHub Actions. Mend also says vulnerability information can feed to Cursor, Windsurf, and Copilot.
Can developers apply suggested fixes?
Yes. Developers can review and apply proposed fixes.
Who makes Mend SAST?
Mend identifies itself as Mend.io (White Source Ltd.) and says it is headquartered in Israel.
Facts from Mend SAST's own pages
- AI code assistants
- It feeds vulnerability information to Cursor, Windsurf, and Copilot to help remediate custom code flaws in the AI workflow. · mend.io, 2 Oct 2026
- AI remediation
- Mend says its AI-powered remediation is 46% more accurate than benchmark competitors, and developers can review and apply proposed fixes. · mend.io, 2 Oct 2026
- Company and headquarters
- Mend identifies itself as Mend.io (White Source Ltd.) and says it is headquartered in Israel. · mend.io, 2 Oct 2026
- Compliance
- Mend says its security management system incorporates ISO 27001, ISO 27017, and ISO 27701 controls, which are reviewed externally each year, and says its controls are evaluated for SOC 2 Type II. · mend.io, 2 Oct 2026
- Detection claims
- Mend says its detection starts with 38% better precision and 48% better recall than benchmark competitors. · mend.io, 2 Oct 2026
- Integrations
- The product page lists JetBrains, VS Code, Visual Studio, Cursor, Windsurf, GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI, and GitHub Actions integrations. · mend.io, 2 Oct 2026
- Language coverage
- Mend SAST supports 30+ programming languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++. · mend.io, 2 Oct 2026
- Plan inclusion
- Mend lists SAST as part of Mend AppSec, which also includes SCA, AI-generated code security, AI-powered fix suggestions, and automated dependency updates. · mend.io, 2 Oct 2026
- Purpose
- Mend SAST is a static application security testing tool for human- and AI-generated code, with vulnerability triage, contextual prioritization, and remediation in developer workflows. · mend.io, 2 Oct 2026
- Risk prioritization
- Contextual Project Classification analyzes factors such as sensitive data and critical functionality to help teams prioritize projects and findings. · mend.io, 2 Oct 2026
- Scanning speed
- Mend says incremental scans can run up to 10x faster than traditional SAST tools by analyzing changed code. · mend.io, 2 Oct 2026
- Secrets detection
- It detects hardcoded credentials, API keys, tokens, and certificates; detected secrets can trigger policy violations and fail a build. · mend.io, 2 Oct 2026
- Source code handling
- Scanning runs on-premises or inside the customer’s environment so proprietary source code stays inside its perimeter, while findings, dashboards, and policy management run in Mend’s cloud. · mend.io, 2 Oct 2026
- Support
- Mend’s site provides a support portal for opening and tracking support tickets. · mend.io, 2 Oct 2026